Working Through Security Operations: What You Actually Need
The Microsoft Security Operations Analyst credential (SC-200) covers Sentinel, Defender, and various security tooling. It tests whether you can take logs from different sources and actually build something that works in a real SOC environment. The exam doesn't just ask what a tool does — it asks you to pick the right tool for a specific incident response scenario under time pressure. I sat through this exam twice. The first time I bombed it because I was overthinking the questions instead of reading them carefully. The second time I passed after switching my study approach entirely. Here's what actually matters.
Where to Find a Reliable Sc 200 Practice Test
Forrest Learning and ExamTopics both have solid question pools, but Forrest Learning is closer to the actual difficulty level. ExamTopics has a wider range of quality issues. I'd also recommend the official Microsoft Learn sandbox environments — they give you hands-on access to Sentinel workspaces, which is something most third-party practice tests skip completely. The closest thing to the real exam is building query logic in a live workspace, not clicking through multiple-choice questions in isolation. When I took my first attempt, I had no hands-on experience with Kusto Query Language. I knew the theory. I could describe what Sentinel does. But when a question asked me to write a query that detected a brute force attack across 500 sign-in events in ten minutes, I froze. That's because I never actually typed KQL. I only read about it. The practical component of studying here is non-negotiable.
What the Exam Actually Tests
The exam weightings from Microsoft break down into roughly three buckets: threat detection and response, investigation and automation, and security operations workflows. The hardest section by far is the threat detection part. You need to know how to write detection rules, configure analytics rules, and understand the difference between a behavioral rule and a threshold rule in Sentinel. Most people underestimate how much KQL matters. It's not a huge percentage of the exam, but when it shows up, you need to be accurate quickly. I spent about two weeks building queries in the Microsoft Learn sandbox. I wrote queries for brute force detection, data exfiltration patterns, suspicious PowerShell execution, and lateral movement. After that, the KQL questions stopped feeling like foreign languages. Another thing nobody talks about: understanding Microsoft Defender for Endpoint's attack surface reduction rules. The exam loves asking which rule to apply for a specific attack scenario. The list of ADRules is long. I made a spreadsheet mapping each rule ID to its description and the type of attack it mitigates. That took an afternoon but saved me five hours of confused reading later.
Get the Full Details
My Biggest Mistake on the First Attempt
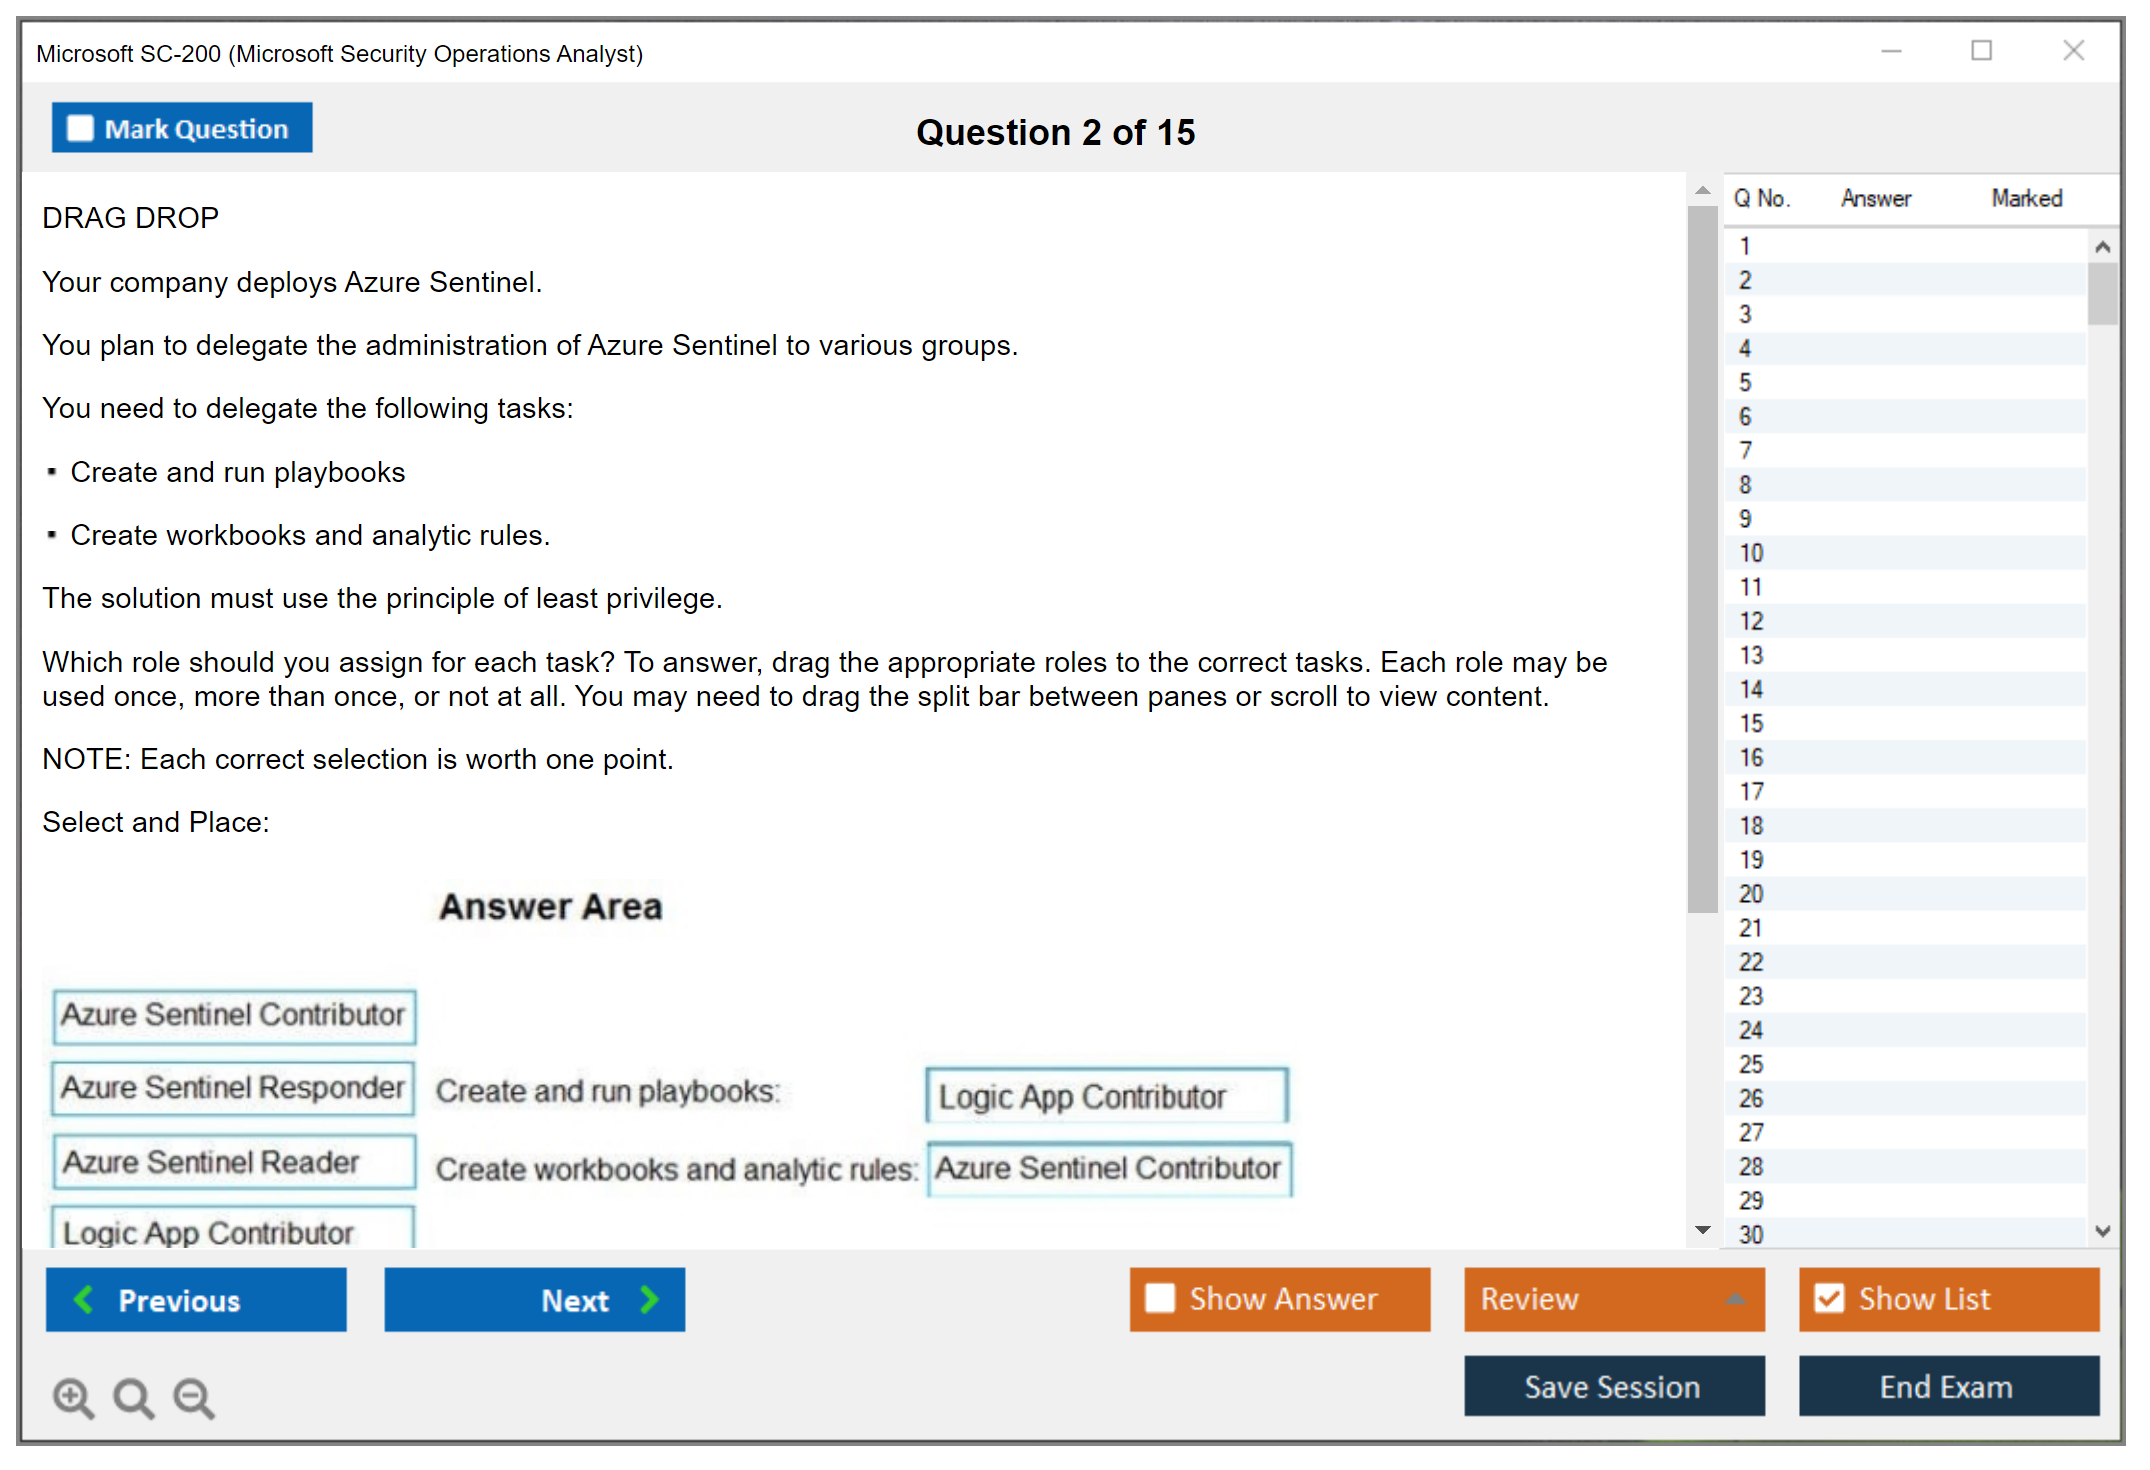
I spent way too much time on Defender for Cloud's cloud posture management features. Microsoft Defender for Cloud has a huge documentation surface area, and the exam asks about recommendations, policies, and regulatory compliance frameworks, but the depth they expect is moderate. I was going deep into ARM template integrations and custom policy creation when I should have been focusing on threat alerts, Sentinel playbooks, and incident management workflows. That was about a third of my study time wasted. I also skipped practice with SOAR playbooks. Sentinel's automation rules are straightforward in concept but annoying to build because of all the dropdown menus and conditional branches. When I finally worked through five or six playbook scenarios manually, I realized the exam pattern for these questions was predictable. They always ask which trigger condition to use, what the first action block should be, and whether you need to pass input variables between actions.
How to Structure Your Study
Don't just read documentation. Build things. Open a free Sentinel workspace in Azure, ingest some sample logs, and write detection rules against them. The Microsoft Learn platform has a free sandbox for this, and it costs nothing. Try breaking something intentionally — generate false positives, misconfigure a connector, see what happens when an alert fires and a playbook runs. This is the kind of experience that separates people who memorize from people who pass. For the practice test phase, do at least one full timed mock before booking the exam. Forrest Learning's version takes about ninety minutes, which is close to the real exam's pace. I scored around 65% on my first full practice run. After two more weeks of targeted study on my weak areas, I jumped to about 82% on the final practice test. The real exam had questions I'd already seen in similar form, which gave me the confidence to move faster. The one area where practice tests fall short is the newer content — Sentinel's integration with Copilot for security operations, and the expanded threat intelligence connector options. Microsoft adds features faster than any third-party test provider updates their question banks. Read the latest Microsoft documentation directly for anything published after mid-2024, especially around Sentinel dashboard customization and Sentinel notebooks for incident investigation.
Book the exam when your practice scores consistently stay above 75%. Going in early and failing costs money and time. The retake fee is the same as the first attempt, and scheduling can take a while depending on your region. There's no shame in pushing the date a few weeks if you need the preparation time.