Writing Security Bid Response Proposals Without Losing Your Mind
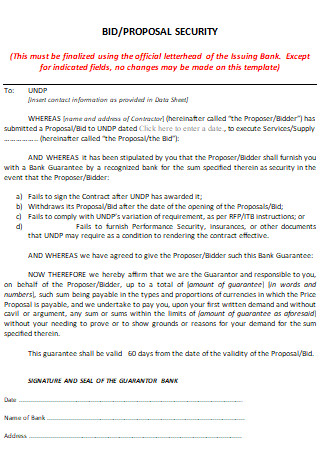
Most people treat a security bid response like it is a creative writing exercise. It is not. It is a compliance document with a narrative attached. You are proving you can secure someone else's systems, follow their rules, and not lose data. The actual writing takes about thirty percent of the effort. The rest is gathering evidence, mapping controls, and making sure you do not contradict something you wrote in section four while answering the question in section eleven. A Sec Security Bid Response Proposal Assignment is simply the work of responding to a formal request for information or proposal in the security domain. That usually means a RFP from a government agency, a large enterprise, or a regulated industry vertical. The assignment covers technical security controls, incident response procedures, compliance mappings, staffing plans, and pricing. I have worked on dozens of these across DoD, healthcare, and financial services, and the structure always feels different until you realize it is the same document wearing different clothing. The trick is not writing well. It is reading the RFP thoroughly before you draft a single sentence. I spent a full day once on a state government contract just highlight-reading the compliance matrix. The client wanted FIPS 140-2 validation for specific encryption modules, and that requirement was buried in annex C under a subsection titled data handling. If I had skimmed it, my proposal would have been non-responsive on page two and the evaluators would have flagged it immediately. You do not want that kind of mistake.
How to actually build a competitive security proposal
Start with the evaluation criteria. Those are the lenses the reviewers will use. Everything you write should point back to those lenses. When I map responses, I build a traceability matrix first. It is a simple spreadsheet with columns for the RFP clause number, the requirement description, the section where I answer it, the compliance level, and any deviation notes. This thing usually saves me three hours of panic during review. Without it, you will inevitably miss a clause or give contradictory answers across sections. Next, pull your existing evidence inventory. This includes past performance write-ups, SOC 2 Type II reports, ISO certificates, vulnerability management screenshots, change management logs, and sample incident response runbooks. Keep these in a organized repository with metadata tags. I use a simple folder system labeled by control family and year. If you are scrambling for a penetration test report two days before submission, you are already behind. Building the evidence library takes real time upfront, but it pays for itself the moment the next RFP drops.
Control mapping and compliance matrices
Security proposals live or die on compliance matrices. You need to translate each RFP requirement into your controls and show evidence. NIST 800-171, CMMC, HIPAA, PCI-DSS, SOX, and FISMA all have different control structures. A common mistake is copying and pasting control text without addressing the specific wording in the RFP. Evaluators read literally. If the RFP asks for dual-factor authentication for remote access and you respond with MFA for VPN only, you have technically missed part of the requirement. I once dealt with a proposal where the RFP specified continuous vulnerability scanning at least weekly. My initial draft referenced monthly scans because that was our standard engagement model for smaller clients. That gap would have cost us the evaluation score. We adjusted the proposal to describe our premium scanning tier and added a schedule table showing weekly cadence with remediation SLAs. The fix took about twenty minutes once I caught it. The risk is real because most people assume their standard offering matches the requirement without checking.
Get the Full Details

Writing the narrative sections
The technical sections need to be clear and specific. Avoid vague language like we follow best practices or our team is highly experienced. Tell me exactly what you do. State the tool, the frequency, the escalation path, and the responsible role. For incident response, include your detection timeline, containment steps, communication plan, and post-incident review process. Concrete details build trust more than confident language. Past performance sections require references and contract numbers. Write them in a way that proves relevance. If the RFP is about cloud security, do not highlight a legacy on-premise migration project unless you explicitly connect the dots. Evaluators spend maybe six minutes per proposal during the initial pass. Make it easy for them to find what they need.
Common pitfalls that sink proposals
One pitfall is ignoring the pricing structure. Some RFPs have complex fee schedules, labor category requirements, and indirect rate restrictions. If you ignore those, your pricing can look fine on the surface and still be technically non-compliant. Always cross-check every line item against the pricing instructions. Another issue is inconsistent terminology. Using both SIEM and log management platform in the same document confuses evaluators. Pick a term and stick with it. I learned this after a reviewer flagged my proposal for ambiguity because I switched between zero-trust and least-privilege frameworks mid-section without explaining the relationship. One paragraph clarified it and fixed the confusion.
Limitations and when this approach fails
Standard proposal frameworks break down when the RFP is unusually vague or contradictory. I have seen requests that asked for both full encryption at rest and zero data retention, which is physically impossible for most logging systems. In those cases, you need to submit questions during the Q&A period. If you stay silent and guess, you risk proposing something non-viable or non-compliant. Also, small firms often struggle with past performance requirements because they lack long government contracts. The workaround is to leverage subcontractor performance and joint venture arrangements if the RFP allows it. Proposal management software helps, but it is not required. I prefer a combination of a traceability spreadsheet, a controlled evidence repository, and a version-controlled document editor. The key is discipline in naming conventions and checklists. A simple submission checklist with items like compliance matrix verified, pricing cross-checked, references confirmed, and formatting validated can prevent most last-minute disasters. If you want a structured template to start with, search for Sec Security Bid Response Proposal Assignment templates from reputable proposal resource sites. Many vendors offer sample matrices and narrative frameworks. The templates are starting points, not finished products. Customize everything to the specific RFP. Copying a template wholesale is the fastest way to get disqualified.

Sec Security Bid Response Proposal Assignment practical workflow
Here is the sequence I use when a new security RFP lands on my desk. I read the full document and mark all requirements. I build the traceability matrix. I extract evidence from my repository. I draft responses section by section, referring back to the matrix constantly. I have a second person review for compliance gaps. I run a final formatting and pricing check. Then I submit. This workflow typically takes a focused team three to five business days for a mid-complexity proposal, depending on how complete the evidence library is. Speed comes from preparation, not rushing. The proposals that fail are rarely the ones with weak writing. They fail because someone missed a requirement, skipped a cross-check, or assumed a detail without verifying it. Pay attention to the details, keep your evidence organized, and write like a professional who expects to be scrutinized line by line.