The Reality of Running Security Assessments
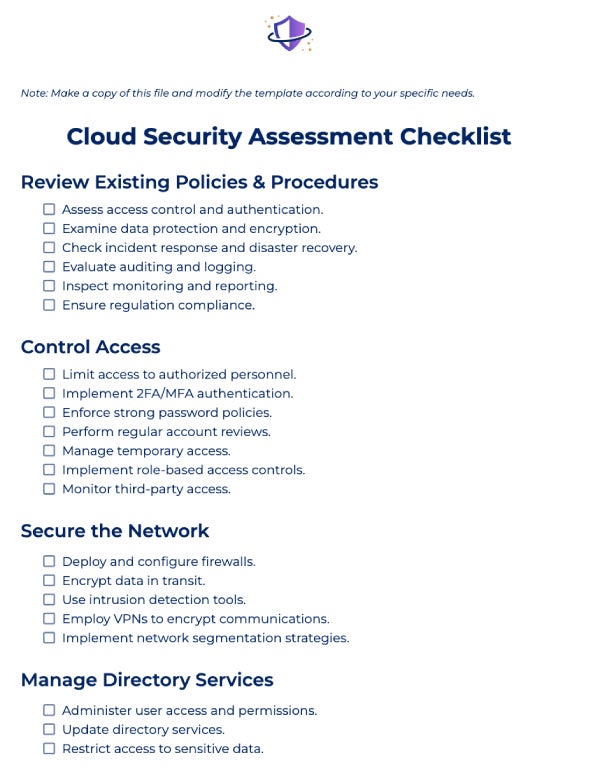
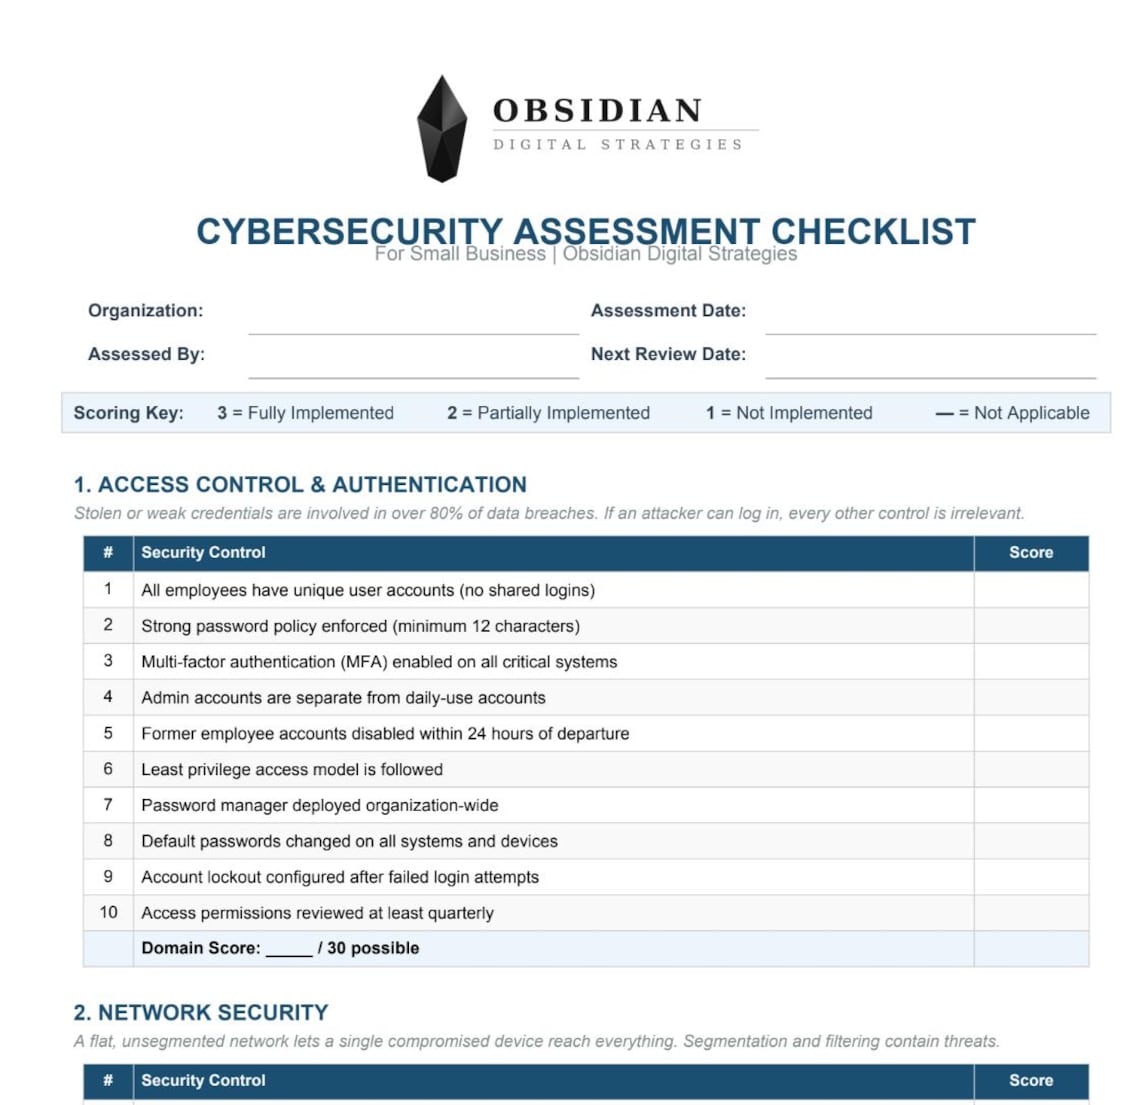
Most people approach security assessments the wrong way. They download a tool, run it against their infrastructure, and hand the resulting PDF to management like it's a pass. It's not. I've watched teams burn weeks on checklist-driven assessments that produced zero actionable findings because nobody stopped to think about what they were actually looking for.The honest truth is that a checklist without context is just paperwork. The value comes from knowing which boxes matter and which are checkbox theater. Here's how I structure mine and what I've learned after doing this kind of work for years. Your checklist needs to cover identity and access management first. Misconfigured IAM policies are the single most common entry point I see. Not brute force, not zero-days. Someone gave a Lambda function a Role with AdministratorAccess because they were in a hurry and forgot to scope it down. Check least privilege enforcement, credential rotation schedules, multi-factor authentication coverage across all privileged accounts, and service account permissions separately from human accounts. Service accounts almost never get rotated because nobody owns them. Network segmentation is the second category that matters. I've assessed environments where the security team had a perfect firewall rule set on paper, but the actual traffic flowed through a misconfigured NAT instance that bypassed every control between the web tier and the database tier. Your checklist should include network flow log review, security group and ACL drift detection, egress filtering validation, and lateral movement path analysis. The last one is the one most checklists skip entirely. Map out every route an attacker could take from a compromised web server to your data store and verify each hop has controls.
Vulnerability management processes need their own section. This isn't about running a scanner and closing tickets. It's about whether your patch pipeline actually works. I once found a critical RCE vulnerability that had been open for eleven months across three separate scanners. The vulnerability was known. The patch existed. Nobody applied it because the change management process required a four-week windows and the team had stopped tracking which patches belonged to which vulnerabilities. Your checklist must include mean time to remediate by severity, patch deployment failure rates, scanner coverage gaps, and exception tracking for unpatched systems.
What Nobody Puts on the Checklist
There are categories that don't appear on any standard template but will save you from embarrassments. Supply chain risk is one. A client of mine had a flawless internal security posture until we discovered their primary authentication library pulled unsigned packages from an unverified npm mirror. The package had been compromised two weeks prior. Their checklist covered everything inside the perimeter and nothing outside it.Logging and observability is another blind spot. You can have every control in place, but if you can't detect when they're bypassed, the controls are theoretical. I once spent a week trying to correlate a breach timeline and couldn't because the WAF logs were being rotated every six hours with no central aggregation. The attacker was in and out in twelve minutes. Your checklist needs log retention periods, centralized log integrity, alert coverage for critical events, and log source inventory that matches your asset inventory. Incident response readiness is usually the weakest category on any assessment. Teams treat it as a document exercise. Write a plan, file it, move on. Real incident response is about decision speed under pressure. Run a table-top exercise where you actually force people to make calls. I've seen security leads freeze for forty-five minutes during a simulated ransomware event because their runbook told them to "contact appropriate stakeholders" without naming a single person or phone number. That's not a plan, that's a wish list.
Get the Full Details

Common Failures That Waste Time
The biggest waste I see is using automated scanners as a substitute for manual review. A scanner will tell you that port 443 is open. It won't tell you that the TLS configuration allows renegotiation, or that the certificate chain includes a cross-signed intermediate from a CA you don't recognize, or that the application behind that port is running a debug endpoint that shouldn't exist. Manual review catches what scanners miss. Budget for it.Another failure is assessing compliance instead of security. The two overlap but they're not the same. PCI DSS has very specific requirements that make sense for cardholder data environments and absolutely nothing to do with your internal HR system. If your checklist treats every system the same way, you'll waste effort on low-risk areas and miss high-risk ones. Risk-tier your assessment scope based on data sensitivity and blast radius, not departmental convenience. Assessment fatigue is real. When you send the same questionnaire to fifty teams every quarter, everyone fills it out mechanically. Responses become copy-paste exercises. I switched to targeted, interview-based assessments for high-risk systems and questionnaire-based checks for everything else. The high-risk reviews take longer per session but surface actual issues instead of documented optimism. The questionnaires still have value for tracking trends over time. Just don't pretend they're equivalent to a real assessment.
How I Validate My Own Work
Before I finalize any assessment, I do a walk-through where I assume I'm an attacker with initial access. Not a skillful attacker, just someone who found a publicly exposed S3 bucket and knows how to read. This red-team mindset catches gaps that checklists miss. I also reverse-check every finding against the asset inventory to make sure I haven't assessed a system that no longer exists or missed one that was added last month. Configuration drift happens constantly.Finally, I document assumptions explicitly. "Assessed as of 2024-03-15 based on live configuration and ten days of log samples." That line matters more than anything else in the report. It tells the reader exactly what the assessment covers and what it doesn't. Anything beyond that is speculation and should be labeled as such.