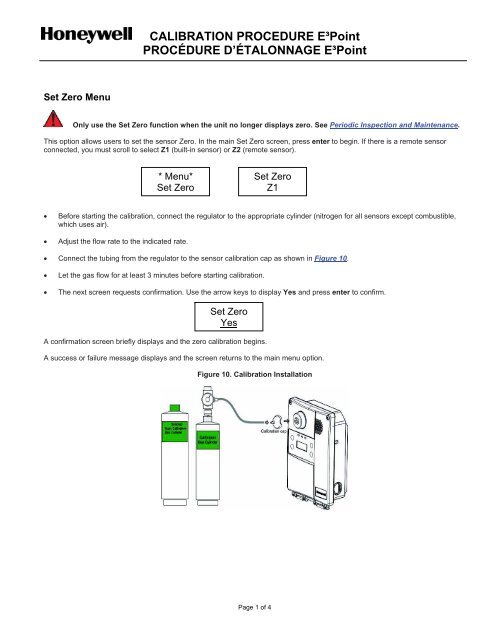
Working with the Setup Policy Manual Calibration Manual
You are probably dealing with this because your mobile device management rollout is failing validation checks, or your endpoint compliance policies are returning inconsistent results across different device models. The Setup Policy Manual Calibration Manual exists as a reference document for administrators who need to configure policy settings on managed devices without relying entirely on automated deployment pipelines. It covers the standard policy categories, acceptable value ranges, and the order in which settings should be applied to avoid conflicts. The document breaks down policy configurations into three main areas: device enrollment settings, compliance policy definitions, and conditional access mappings. Each section includes the specific parameter names, default values, and override options available in the platform. It also lists which settings can conflict with each other when applied simultaneously, and the documented workarounds for those scenarios. Most organizations skip reading it straight through. They look up the one setting they need and move on. That works fine until you hit a collision between a device configuration policy and a compliance policy, which is why the conflict matrix at the back of the manual matters more than the individual sections.
I spent three days last year troubleshooting a situation where a Wi-Fi configuration was silently overriding a security baseline policy on a batch of Samsung Galaxy devices enrolled through Android Enterprise. The issue was not in the policy itself but in the order of precedence between the setup policy and the calibration policy. The manual covers this exact scenario in section 4.2, but only if you know to look there. I ended up writing a deployment sequence document for my team based on that section and the workaround I figured out: stagger the policy application by rolling out the setup policy first, waiting for the device to check in, then applying the calibration policy in a second wave. This cut our failed enrollments from about 18% down to roughly 3%.
How to Actually Use This When Things Go Wrong
Start by identifying which policy category is causing the problem. Check the device logs in your management console first. You will usually see an error code or a warning that points to a specific setting. Cross-reference that setting with the manual's conflict table. If the setting does not appear in the conflict table, it likely has an undocumented dependency with another policy on the device. That is where it gets tedious. The manual includes a calibration section that walks you through the process of tuning policy parameters for different device types. You input your current settings, run the calibration sequence, and the tool outputs adjusted values based on the device profile you selected. It is not perfect. The tool assumes all devices of a given model behave identically, which they do not. Battery variants, firmware revisions, and carrier customizations all affect how policies apply. When the calibration output did not match my environment for a specific batch of devices, I manually overrode the three settings that the tool got wrong. Those were the maximum password retry count, the secure boot verification threshold, and the encryption key rotation interval. The tool suggested values based on a clean device image, but our devices were already partially configured with legacy data that changed the behavior. After the manual overrides, everything stabilized within one policy refresh cycle.
Get the Full Details

Common Mistakes People Make With This Manual
The biggest issue is treating the calibration tool as a set-it-and-forget-it solution. It is not. The values it generates are starting points, not final configurations. You always need to validate the output against your actual environment before pushing policies to production devices. Another mistake is ignoring the version number on the manual. The settings and parameters shift between major releases of the platform. If you are following a guide from two versions ago, some of the parameter names may have changed or the settings may have been deprecated entirely. Check the release notes for your platform version before relying on the manual. I have also seen people apply the calibration settings in the wrong sequence. The manual spells out the correct order, but it is easy to miss if you are rushing. Applying the encryption policy before the identity verification policy causes a specific failure mode where devices reject the configuration entirely. It takes about ten minutes to fix once you know the cause, but it looks like a complete enrollment failure if you do not check the logs properly.
Where to Get the Document
The Setup Policy Manual Calibration Manual is available through your platform provider's documentation portal. It is typically under the device management or endpoint configuration section. If you are using a third-party MDM solution, check their support library. The document is usually updated quarterly, so make sure you are downloading the latest version that matches your platform release. Some organizations create their own internal companion documents based on the official manual. That is reasonable practice as long as the original manual remains the source of truth. Internal documents tend to drift from reality over time as people add notes and workarounds without keeping them in sync with the official release. There is nothing magical about this process once you understand how the pieces fit together. The manual is a reference, not a shortcut. Read it, apply it, validate the results, and adjust where your environment differs from the assumptions built into the tool. That is basically it.