What a Soc 1 Audit Guide Actually Covers
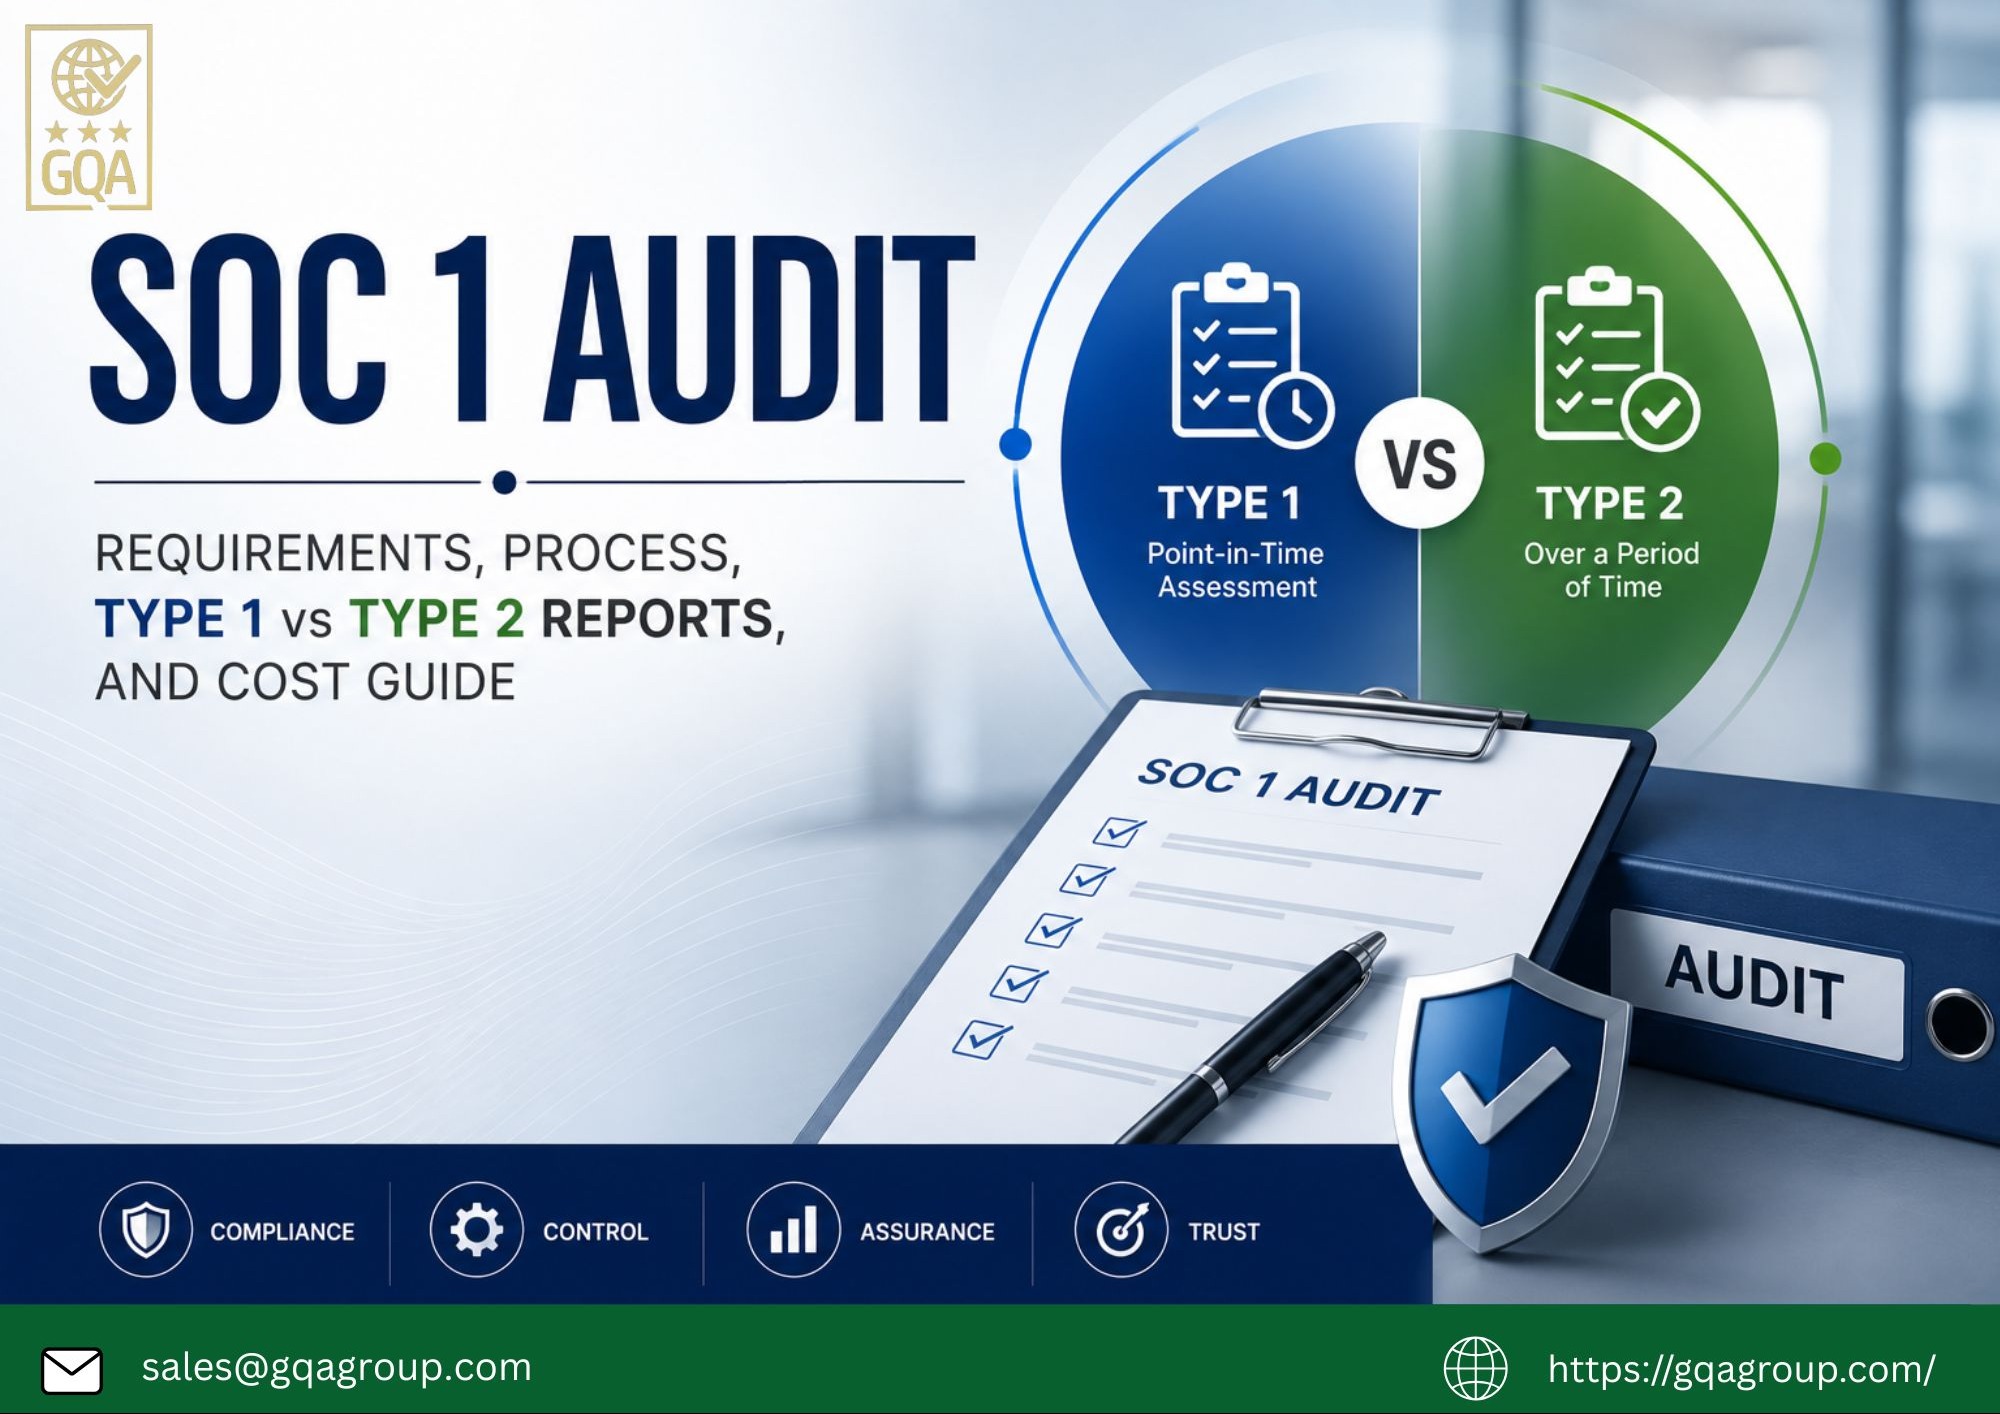
A Soc 1 Audit Guide is a roadmap for how auditors evaluate the controls at a service organization that could matter to your users' financial reporting. The AICPA's AT-C section 350 is the governing standard now, replacing the old SSAE 16 language. Most people I talk to are still looking for a downloadable PDF that lays out every test step, and those exist, but they tend to be dry compliance documents rather than useful working guides. The guide typically breaks into two report types. Type 1 covers the design of controls at a point in time. Type 2 covers design and operating effectiveness over a period, usually twelve months. The difference matters because a Type 1 report won't tell you whether your control actually worked consistently throughout the year. I spent three years managing SOC 1 engagements for a payments processing company, and the first thing I learned was that the scope definition gets everyone in trouble. Service organizations routinely define their scope too narrowly. They'll exclude a system that touches the same data pipeline but call it a separate application. Auditors will push back hard on that during scoping meetings if you're not careful.
How to Approach a SOC 1 Engagement
Start by mapping your sub-service organizations before anything else. This is where most engagement letters go sideways. A sub-service organization is any vendor your service org relies on to deliver part of the service. If you process payroll and your vendor handles the tax filing component through another platform, that's a sub-service org and it needs to be explicitly listed in your description section. Skipping this step means the auditor has to request their own evidence, which slows everything down and adds cost. The description section of the report is everything. It's the foundation the auditor builds on. If it's vague, the audit becomes a negotiation rather than a verification exercise. I once had a client whose description said "cloud infrastructure hosted on AWS." The auditor required them to expand that to include the specific regions, the control environment around AWS shared responsibility, and how the client's own access controls interacted with the provider's infrastructure controls. This alone added two weeks to the timeline.
Common Pitfalls That Waste Time and Money
One issue that comes up repeatedly involves the carryforward of prior period information. If you're a going-in organization with no prior SOC 1 history, you need a full Type 2 period. Some companies try to use a Type 1 report as a placeholder while they build Type 2 coverage. That doesn't work the way people expect. Users and auditors can rely on Type 2 reports, but Type 1 alone provides limited comfort for ongoing oversight purposes. Another frequent problem is the treatment of general IT controls. Service organizations often assume that because their cloud provider has strong IT controls, they don't need their own. The auditor will test your dependency on those provider controls and may conclude that your own GCAs around access provisioning, change management, and monitoring are insufficient to support reliance. I've seen this add roughly sixty to eighty hours of audit work to engagements that didn't account for it.
Get the Full Details

What to Expect During the Fieldwork Phase
Fieldwork usually runs four to eight weeks depending on the size and complexity of the operation. The auditor will request evidence packages - typically policy documents, screenshots of control executions, and sample-based testing documentation. You should prepare evidence before the auditor arrives rather than reactively. A well-organized evidence library cut my last engagement's fieldwork from seven weeks to five. The auditor will also interview your staff. These interviews are not casual conversations. Each response becomes part of the audit trail. I recommend having your control owners prepare talking points beforehand so they don't volunteer unnecessary information or contradict written policies on the record.
Working with the Report Once It's Complete
When the report lands in your inbox, most people skip straight to the opinion section. They should read the qualification narrative first. Any qualified or adverse opinion is usually preceded by a detailed description of the exception and its potential impact on user entities. The exception text is more useful than the opinion letter itself for understanding what actually went wrong. If you receive a report with a qualification, don't treat it as a failure. Qualifications are common and often relate to minor control gaps that can be remediated within a reasonable timeframe. The real risk comes from unqualified opinions that hide material weaknesses in the accompanying management commentary. Always read the entire document, including any supplementary information attached by the service organization.
Practical Advice from Experience
Here's something I wish more people understood about SOC 1 engagements. The audit firm you select matters almost as much as your own preparedness. Larger firms bring more resources but less flexibility on timelines. Boutique firms often work faster and are more willing to accommodate tight deadlines, but you need to verify their competency with your specific industry vertical. I worked with a boutique firm that had never audited a fintech company before. The resulting report contained several control observations that were technically correct but industry-inappropriate, which required additional work to restate. For companies that need a practical reference document, the AICPA publishes a SOC 1 Audit Guide as part of their Auditing Guide series. It's available through the AICPA bookstore and costs approximately ninety-five dollars for the digital version. Third-party publishers like Wiley and CCH also offer annotated versions that include practice aids and sample workpapers at higher price points ranging from two hundred to four hundred dollars. These are helpful if you're new to the process, but the AICPA original remains the authoritative source. The biggest bottleneck in any SOC 1 engagement is evidence collection speed. Companies that centralize their evidence repository before the auditor begins typically finish fifteen to twenty percent faster than those that assemble documents on demand. A simple folder structure organized by control category with dated filenames eliminates most of the back-and-forth communication that drags out these projects.