How to Actually Map SOC 2 to NIST 800-53 Without Losing Your Mind
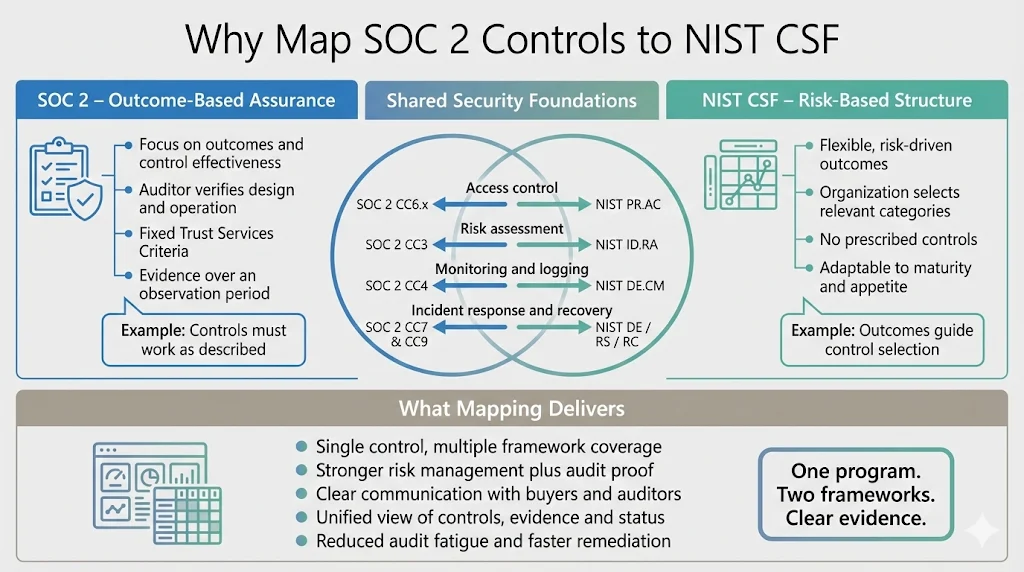
SOC 2 and NIST 800-53 controls overlap significantly but they were built by different organizations for different purposes. SOC 2 comes from AICPA and focuses on trust service criteria. NIST 800-53 comes from the National Institute of Standards and Technology and covers a much broader set of security and privacy controls for federal systems. The mapping process is essentially translation work between two frameworks that share common language but organize it differently. I spend most of my time helping compliance teams figure out which NIST control corresponds to each SOC 2 criterion, and the first thing people get wrong is assuming a one-to-one relationship exists for every control. It doesn't. Some SOC 2 controls map cleanly to a single NIST 800-53 control. Others require mapping across three or four NIST controls, and a few SOC 2 requirements simply have no direct equivalent in NIST 800-53 because they address commercial trust concepts rather than technical security requirements. The practical way to start is by taking your SOC 2 report and listing each applicable Trust Service Criterion category. For a typical SOC 2 Type II covering the security criterion, you'll be working with the CCM-aligned or SIG-aligned controls depending on which questionnaire your auditor used. Map each control to its NIST counterpart using the control family as your anchor point. Access controls in SOC 2 generally map to the AC family in NIST. Audit and monitoring controls map to the AU family. Configuration management maps to CM. incident response maps to IR. And so on through the families.
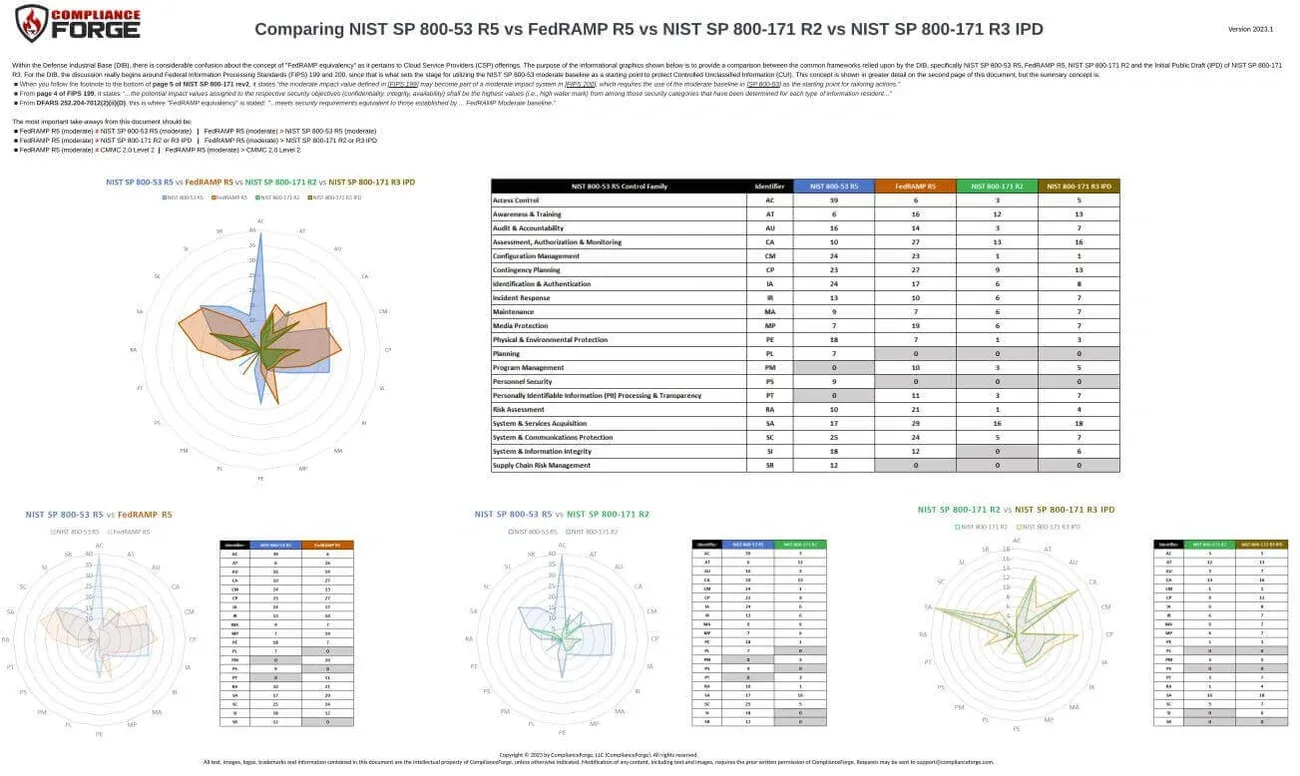
Here is where the real friction shows up. I recently worked with a team that had a SOC 2 report covering availability and processing integrity alongside security, and they needed to demonstrate NIST 800-53 compliance for an FedRAMP authorization. The SOC 2 availability criterion included requirements around system monitoring and capacity planning that didn't map to a single NIST control. Instead, those requirements spread across SC-5 for availability, SI-4 for system monitoring, and RA-5 for system assessments. The auditor's report didn't document the specific monitoring tools or capacity thresholds in enough detail to satisfy NIST's more granular baselines. We had to go back and pull evidence from infrastructure logs, runbooks, and change management records that existed but were never collected with compliance documentation in mind. That took about three weeks of extra work to rebuild the evidence trail. The workaround was straightforward but annoying. We created a cross-reference spreadsheet with columns for the SOC 2 control ID, the NIST 800-53 control ID, the control family, a description of the gap between the two frameworks, the evidence source, and the control owner. This became our living document throughout the engagement. Every time we pulled a new piece of evidence, we updated the relevant row instead of starting a fresh search. One thing most people don't realize is that NIST 800-53 controls are hierarchical in a way SOC 2 controls are not. A single NIST control like AC-2 includes sub-controls for account management, automated account creation, automated account disabling, and so on. Your SOC 2 report might reference access management broadly without breaking it down into those sub-requirements. When you're mapping, you need to identify which NIST sub-controls are satisfied by your existing SOC 2 evidence and which ones require additional implementation. This is where gaps tend to hide. The big ones you'll find most often are in the PE physical protections family, CA assessment controls, and CP contingency planning controls, because SOC 2 reports typically focus heavily on logical security and monitoring while leaving physical and operational resilience controls under-documented.
Another counter-intuitive point is that having a SOC 2 report actually makes NIST 800-53 mapping easier in some areas but harder in others. Easier because the foundation of your security program is already validated and documented. Harder because NIST baselines differ depending on whether you're implementing Low, Moderate, or High impact levels, and SOC 2 doesn't specify an impact level at all. A SOC 2 report that satisfies a Moderate baseline will likely fall short of a High baseline without additional controls around media protection, system backup, and insider threat programs. If you're doing this mapping for FedRAMP, note that the authorization process requires a System Security Plan, a Plan of Action and Milestones for any gaps, and evidence that each selected NIST control is implemented according to the prescribed enhancements. SOC 2 provides the evidence of implementation for the overlapping controls but does not replace the SSP requirement. You will still need to write the SSP separately even if every NIST control has a corresponding SOC 2 evidence link. The automation question comes up constantly. Tools like OneTrust, Drata, and Vanta can handle a significant portion of the initial mapping by maintaining pre-built control correlation libraries. They can auto-associate SOC 2 controls to NIST 800-53 equivalents based on the framework version you select. This usually cuts the initial mapping effort from roughly two weeks of manual work down to about two or three days, provided your control descriptions are detailed enough for the tool to match accurately. The limitation is that these tools struggle with the edge cases I mentioned above, particularly multi-framework coverage and sub-control granularity. You still need a human to review every mapped pair, verify the evidence alignment, and flag the controls that require supplemental implementation.
Get the Full Details
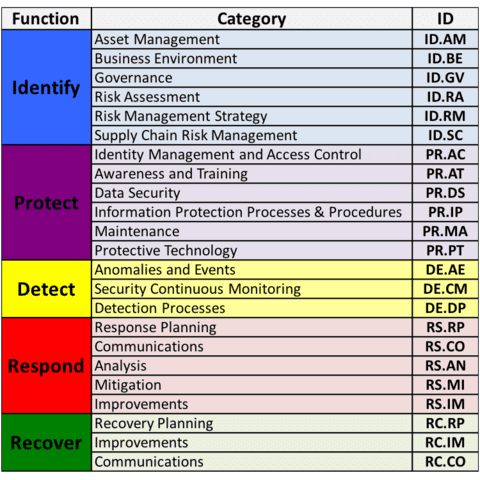
I also recommend maintaining an inverse mapping from NIST back to SOC 2, not just the forward direction. This serves two purposes. It helps you quickly identify which SOC 2 criteria are covered by each NIST control for audit responses, and it prevents the common mistake of assuming a SOC 2 control is satisfied when only a subset of the corresponding NIST control is implemented. The partial implementation trap costs people more failed audits than any other mapping error. The bottom line is that this mapping is repeatable work once you have the first version done. Building the initial cross-reference table takes focused effort over a couple of weeks for a typical mid-size organization. After that, updates are mostly incremental as new controls get added or existing ones change between framework revisions. If your SOC 2 report already uses the CCM as its control framework rather than the raw Trust Service Criteria, the mapping task becomes considerably simpler since the CCM was explicitly designed with NIST overlap in mind.