Understanding How Manipulation Actually Works
Most people treat social engineering as if it's just phishing emails and tech support scams. It's not. The actual scope covers anything where human psychology is the primary attack vector. Trust, urgency, authority, reciprocity—those are the levers. Once you understand which lever gets pulled in a given situation, you can spot the pattern before anything harmful happens. I spent years in security, and the thing that always surprises newcomers is how little technical skill some of the most effective operators have. They spend hundreds of hours researching a target instead of writing a single line of code. There was one instance where someone impersonated a vendor at a Fortune 500 company. They called the IT helpdesk, referenced real invoice numbers, claimed their remote access tool had broken, and asked the helpdesk to push out a patch. No malware, no exploit, no password guessing. Just a phone call and enough domain knowledge to sound credible. The helpdesk employee verified the caller's identity against a phone number that was listed publicly on the company's own vendor page. That is the entire game. The effects of social engineering fall into three buckets. First, you have direct data loss—credentials, PII, financial info. Second, you have access granted—someone talks a user into opening a port, whitelisting an IP, or enabling admin privileges. Third, and the one people underestimate, is trust erosion. After a successful social engineering breach, even legitimate internal requests start getting second-guessed. Productivity drops. Morale drops. You end up with policies that make employees less efficient because nobody trusts the communication channels anymore.
Recognizing Social Engineering Effects in Practice
Here is what most organizations miss. They train people to recognize phishing. They do not train them to recognize the subtle escalation patterns that happen over days or weeks. A classic advanced attack starts with a small, harmless favor. Someone asks for a document format, or a vendor name, or a meeting time. Nothing sensitive. Then, three days later, they follow up with a slightly bigger request that seems related. By the fourth interaction, the target has already established a pattern of compliance. Refusing now feels inconsistent with their own past behavior. I encountered an edge case where a recruiter reached out through LinkedIn to a senior engineer. The recruiter was legitimate—real company, real position, real reference. But the engineer noticed the recruiter asked about the company's internal network topology before discussing the role. When the engineer flagged this as inappropriate, the recruiter replied with what I can only describe as an automated-sounding message about standard pre-screening questions. A real recruiter would have either apologized or deflected gracefully. This one had a script. That mismatch between tone and content is something I check for now before engaging with anyone on professional platforms. You learn these patterns the hard way. Another counter-intuitive point: familiarity increases vulnerability, not decreases it. People who think they are savvy about security are often the most susceptible because they assume they have already identified the threat. A study I saw referenced showed that security-aware employees were phished at higher rates than non-security-aware employees. The reason is simple. Confidence reduces vigilance. When someone feels competent, they stop double-checking.
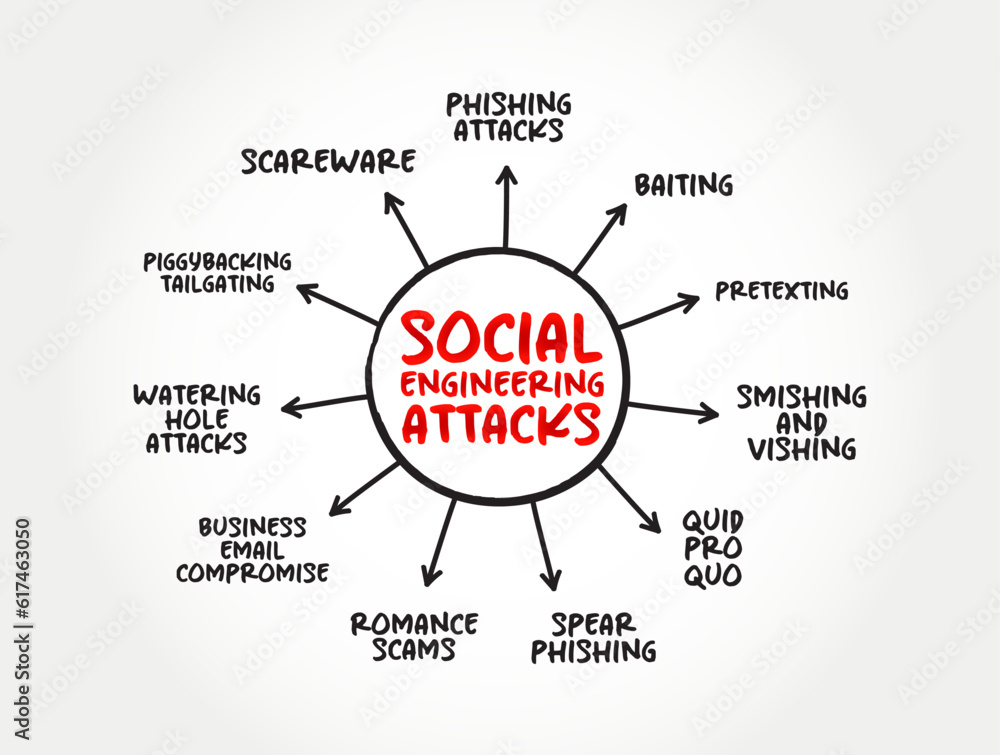
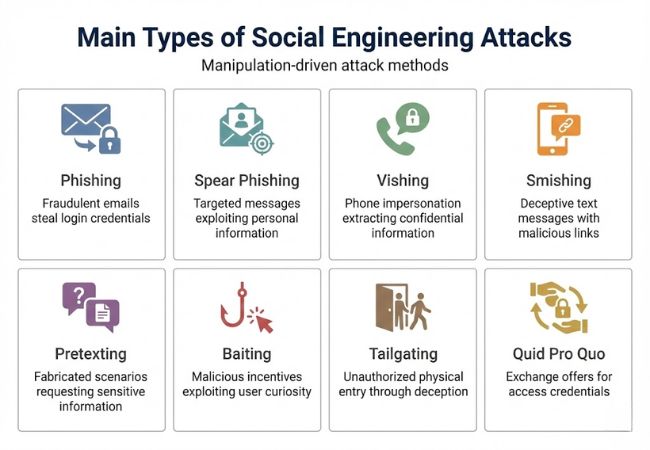
Let me walk through a realistic detection and response workflow. If you suspect someone has been socially engineered, the first step is containment, not investigation. Isolate the affected system or revoke the compromised credentials immediately. Do not try to understand the full scope before stopping the bleed. I once worked a case where a helpdesk analyst spent forty minutes documenting the call transcript before escalating. During those forty minutes, the attacker had already initiated a funds transfer. The documentation was thorough but irrelevant by that point. After containment, you need to determine the method. Was it phishing? Vishing? Tailgating? Pretexting? The method matters for the response. A phishing breach requires credential rotation and email filtering updates. A vishing breach requires voice authentication policy changes. A physical breach like tailgating requires different countermeasures entirely. The Social Engineering Effects are the same in outcome but very different in the remediation path. For prevention, the most effective single control is mandatory second-factor authentication everywhere. Not optional MFA. Mandatory. Every service, every system, every remote access tool. This eliminates the single biggest threat vector—credential theft through phishing and pretexting. An attacker can have your password. They cannot easily have your YubiKey or your authenticator app push notification approval.
Get the Full Details
Employee training needs to shift from annual compliance videos to continuous micro-training. Five-minute modules once a month, delivered at random intervals, with randomized simulation attacks. The simulations should include realistic scenarios—a CEO asking for a gift card purchase, a panicked "IT" calling about a suspected breach, a delivery driver at the front desk. Repetition without variation leads to desensitization. Randomized realistic scenarios maintain engagement. One thing I want to be honest about. There is no perfect defense against social engineering. The human element will always be the weakest link. Organizations that spend $200,000 on security awareness training will still have employees click through phishing links. The goal is not elimination. The goal is reduction to an acceptable risk level. If you are looking for a magic solution, you will waste money on tools that create a false sense of security. The most underrated practical step is establishing clear escalation channels. Employees need to know exactly who to call or message when they are unsure about a request. Make it frictionless. A Slack channel, a dedicated phone line, an instant-response form. If reporting uncertainty requires filling out a form and waiting twenty-four hours, nobody will use it. They will just comply with the suspicious request to avoid looking difficult.
External threat intelligence feeds also help. Services like PhishTank, OpenPhish, and commercial equivalents track known phishing infrastructure. You can automate blocks based on these feeds. This cuts your exposure window from days to minutes for known threats. For new zero-day social engineering campaigns, that automation is the difference between a breached employee count of five and a breached employee count of five hundred.
Advanced Vectors and Unconventional Approaches
Watering hole attacks remain highly effective despite being discussed for nearly two decades. The concept is straightforward—compromise a website that your target audience visits regularly, then inject malicious content or exploits when targets load the page. The trust factor here is enormous because the target associates the website with legitimate daily work activity. Security tools often have a harder time flagging these because the domain itself appears reputable. Supply chain social engineering is another vector worth understanding. Attackers identify a trusted software vendor or service provider and compromise their communication channels. Then they send updates that appear legitimate to all downstream customers. The 2020 SolarWinds incident is the textbook example, though that was more technical compromise than pure social engineering. Still, the principle applies—when the trust chain is long enough, verification becomes statistically impossible for any individual organization. I recently worked with a team that implemented a "break glass" protocol for emergency credential requests. The process requires two authorized individuals to physically sign off on any after-hours privilege escalation. It adds about fifteen minutes to the request process. It also eliminated a significant class of vishing attacks where attackers pressured a single on-call employee into granting elevated access during off hours. The fifteen-minute delay forces the attacker to either wait or abandon the attempt. Most choose the latter.

Language analysis is another underutilized detection technique. Social engineering scripts tend to have specific linguistic patterns—excessive urgency markers, unusual formality shifts, grammatical inconsistencies that suggest translation or template use. Natural human communication does not follow these patterns. Setting up automated analysis on incoming communications that flag these markers can catch a lot of attempts before they reach a human decision point. There is also the problem of reverse social engineering, where the attacker creates a problem and then offers themselves as the solution. I have seen this in the wild—a fake server outage announced through a spoofed internal alert, followed by a call from someone claiming to be emergency IT support offering to fix it. The target is already stressed from the perceived outage and is more likely to comply with the unsolicited "helpful" person. The fix is simple policy: no external party initiates emergency IT support. All incidents are reported through established channels, not responded to by callers. Physical security assessments often reveal gaps that digital controls cannot address. An attacker wearing a generic uniform, carrying a backpack, and walking confidently toward a secure entrance will get through about thirty percent of the time without anyone stopping them. This is called "sucker punching" in the professional security community, and it is not about physical force. It is about exploiting the social norm that people should not publicly challenge someone who appears to belong in a professional setting. The workaround is simple badge verification at every entry point, regardless of appearance or confidence level.
One final practical note. Measure your security posture using realistic metrics, not vanity metrics. The number of phishing simulations passed is not a meaningful security indicator. The rate of genuine phishing clicks over a rolling ninety-day period, the average time between a simulated attack and employee reporting, the percentage of employees who correctly escalate suspicious requests—that is what matters. Track the right things and report them honestly. Bad news told late is worse than bad news told early.