Why Security Awareness Training Keeps Failing
I spent three years running social engineering assessments across Fortune 500 companies and I keep seeing the same pattern: organizations treat it like a compliance checkbox rather than a behavioral problem. They send out phishing simulations, track click rates, and call it a day. Meanwhile the attack surface grows every quarter because nobody actually understands what they're dealing with. Let's start with the core concept before we get into methodology. The Social Engineering Psychology Definition refers to the study and application of human cognitive biases, emotional triggers, and decision-making heuristics that attackers exploit to manipulate targets into taking actions they wouldn't normally take. It's not about trickery in the cartoon sense. It's about understanding that human brains run on shortcuts, and those shortcuts are systematically attackable. The psychology breaks down into a few reliable levers. Authority bias makes people comply faster with perceived hierarchy. Urgency collapses analytical thinking — give someone thirty seconds to respond and they default to instinct, not training. Reciprocity creates obligation; a small favor or piece of information given first makes targets far more compliant with a subsequent request. Scarcity triggers loss aversion. Liking and similarity reduce perceived threat entirely. These aren't theories. They're documented cognitive phenomena that social engineers have been weaponizing since before there was a word for it.
Here's something most people miss about this field: the most dangerous attacks don't rely on any single principle. They layer them. A phishing email that creates urgency around a password reset, comes from what appears to be IT leadership, and includes a link to a lookalike portal leverages authority, urgency, and familiarity simultaneously. Single-principle attacks fail about 60% of the time in my experience. Layered ones succeed at rates that make teams uncomfortable. On the practical side, if you're building a defense program, start with what actually moves behavior. Tabletop exercises where people talk through scenarios help slightly. Realistic simulation campaigns with varied attack vectors and measurable follow-up metrics change actual behavior over time. The data from our assessments consistently showed that organizations running quarterly simulated campaigns saw a 40-60% reduction in successful phishing compromise within six months. One-time training events showed almost nothing after three months. Now I want to address a specific problem that kept coming up. We were running a pretexting assessment where the attacker posed as an external auditor requesting employee ID verification through the HR portal. About 35% of targets complied on the first attempt. But when we introduced a secondary verification step — requiring the target to call a number provided by the company's official directory rather than the number given by the "auditor" — compliance dropped to under 8%. The workaround wasn't training. It was architecture. You can't rely on people remembering the right thing to do under pressure. You build systems where doing the wrong thing is harder than doing the right thing.
There are some hard limitations to this whole space that nobody likes to talk about. Social engineering defenses will never be 100%. The attacker only needs one person to slip. You can't train away every cognitive bias. Under time pressure, stress, or fatigue — which is when most breaches happen — trained behavior degrades rapidly. Even well-trained employees in our highest-performing programs still fell for simulated attacks at rates of 15-20% annually. That's not a training failure. That's human nature. A counter-intuitive insight from the field: the best security culture doesn't shame people who fall for tests. It normalizes reporting. In one organization I worked with, they shifted from publicly ranking departments by phishing click rate to a system where anyone who reported a suspicious email got immediate positive reinforcement and a brief educational nudge. Their actual security incidents dropped by nearly half within eight months, while click rates on simulations also improved. The mechanism was simple — when people aren't afraid of being caught, they catch threats earlier. Another nuance beginners consistently overlook: social engineering psychology applies just as much internally as externally. Insider threats, accidental data leaks, and privileged access misuse all follow the same cognitive patterns. A legitimate employee pressured by a manager to bypass procedure is experiencing the same authority bias as an external target. The psychology doesn't distinguish between friend and foe. It responds to the same triggers regardless of context.
Get the Full Details
Practical implementation considerations
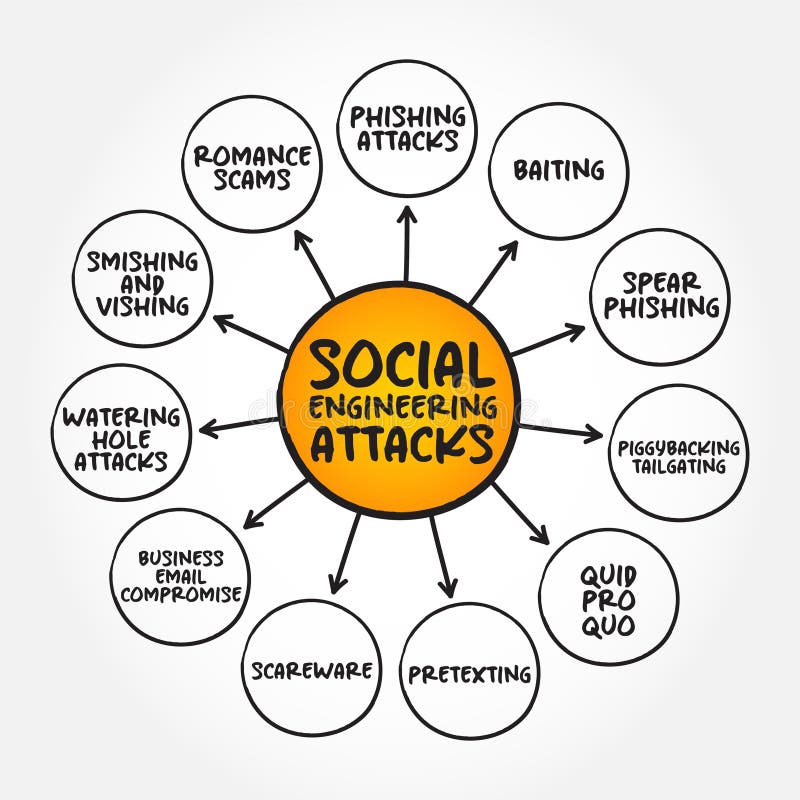
If you're starting a program, budget for continuous operation, not a one-off project. Quarterly simulation campaigns with realistic vectors — phishing, vishing, smishing, physical tailgating — cost roughly $15,000 to $40,000 annually for mid-size organizations depending on scope. The cheaper options usually involve off-the-shelf platforms with generic templates that experienced employees learn to spot within weeks. Generic attacks don't test real behavior. Customized attacks that incorporate actual company context, current events, and targeted roles do. Measure the right things. Click rate is the easiest metric and the least useful on its own. Look at report rate — how many people proactively flag suspicious messages. Look at time-to-report. Look at credential protection behavior. The metric that correlates most strongly with actual breach prevention is the proportion of employees who use verified channels to confirm unusual requests. There's also a growing subcategory worth watching: AI-generated social engineering. Large language models have made pretext creation significantly easier and more persuasive. A well-crafted AI-generated phishing email in 2024-2025 reads noticeably better than the templated garbage from five years ago. Grammar, tone matching, contextual references — all of it has improved. Defenses need to account for this without spiraling into paranoia. The practical shift is less about spotting bad writing and more about verifying through independent channels before acting on any unusual request.
The bottom line is that social engineering exploits predictable human behavior, and the only sustainable defense is a combination of architectural friction, continuous realistic practice, and a culture that rewards vigilance over compliance. Any program that treats this as a training checkbox is already behind.