What Actually Goes Into a Risk Assessment Template
A Software Validation Risk Assessment is a structured document that identifies what could go wrong with a computerized system and assigns risk levels based on potential impact on patient safety, data integrity, and product quality. It is required under GAMP 5 and expected by FDA inspectors during 21 CFR Part 11 reviews. The template itself is just a framework. How you fill it out is where most teams fail. I worked on a validation project for a clinical laboratory information system last year. The risk assessment was supposed to cover LIMS, interface modules, and backup/restore functionality. We built a standard 15-column spreadsheet-based Software Validation Risk Assessment Template covering hazard identification, risk analysis, risk evaluation, and risk control measures. It looked fine on paper. It took us six weeks to redo it because the initial version didn't properly separate user access risk from data integrity risk at the interface level. The FDA auditor flagged it on day two. We had to rework the entire matrix.
How to Build Your Own Software Validation Risk Assessment Template
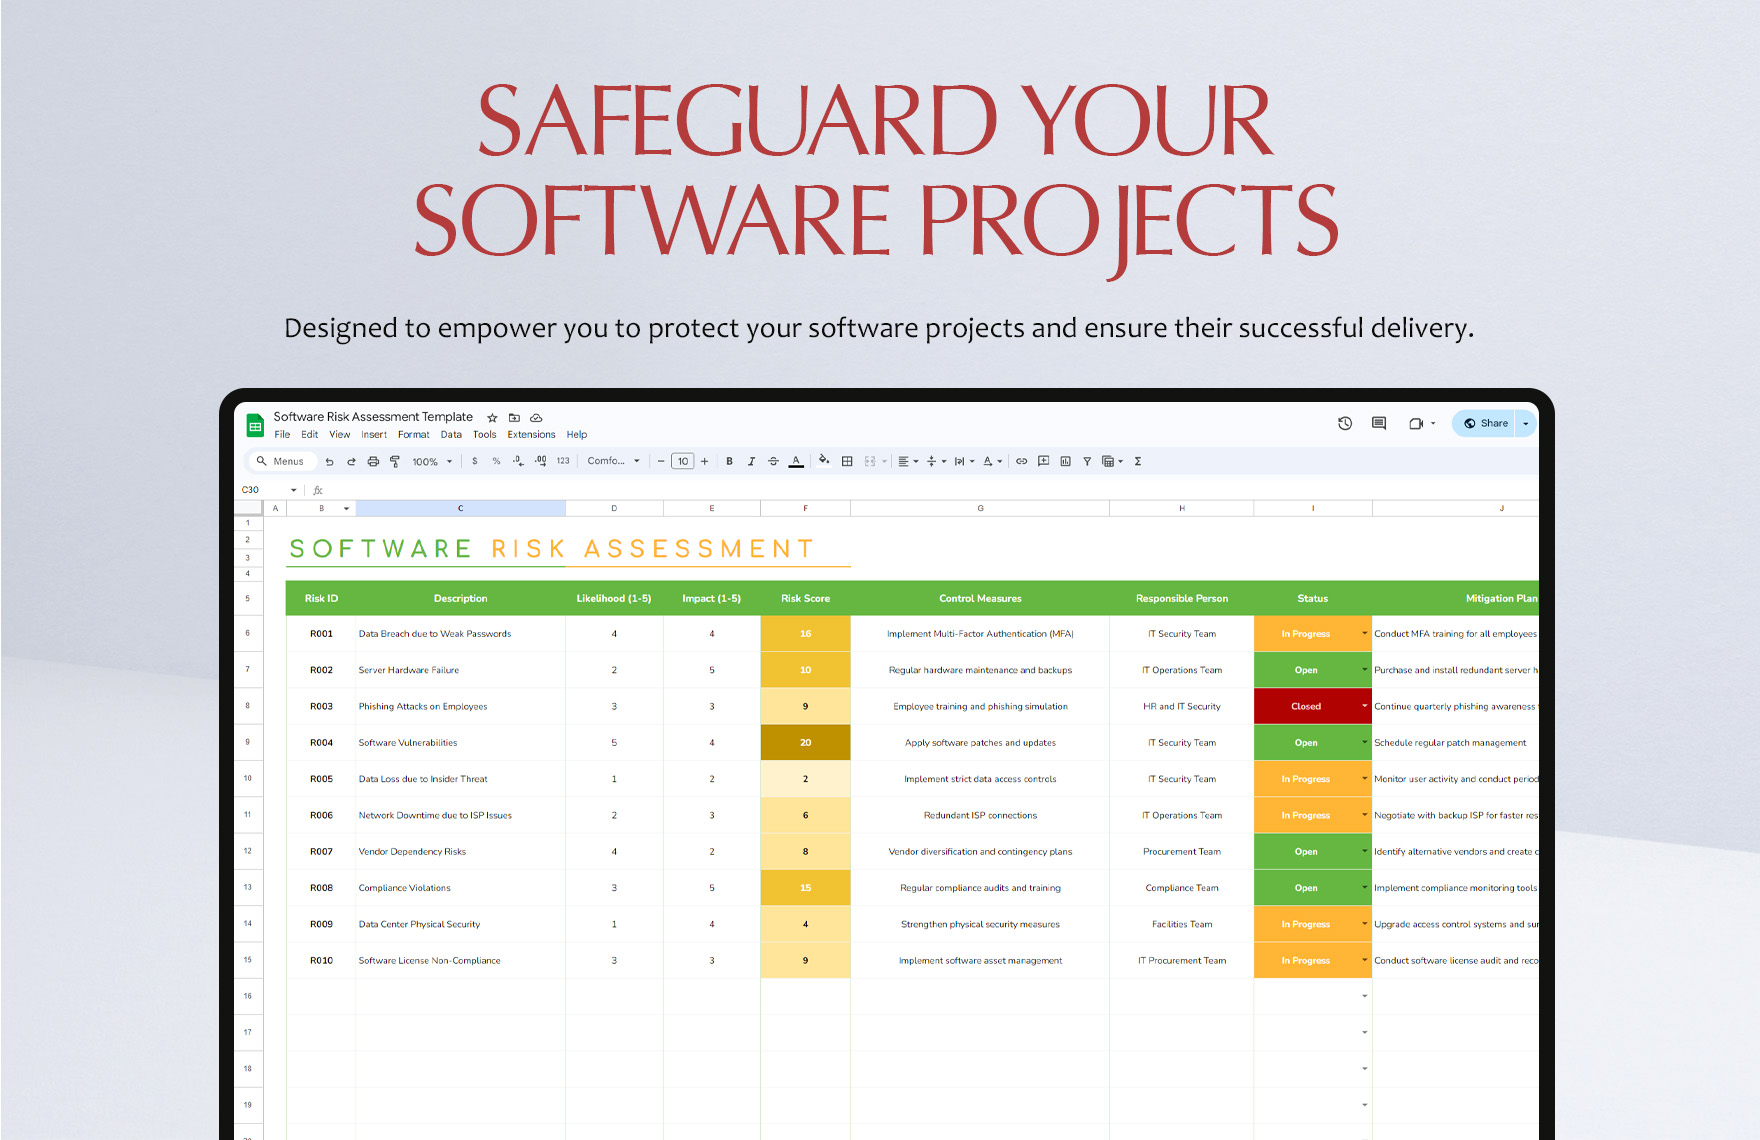
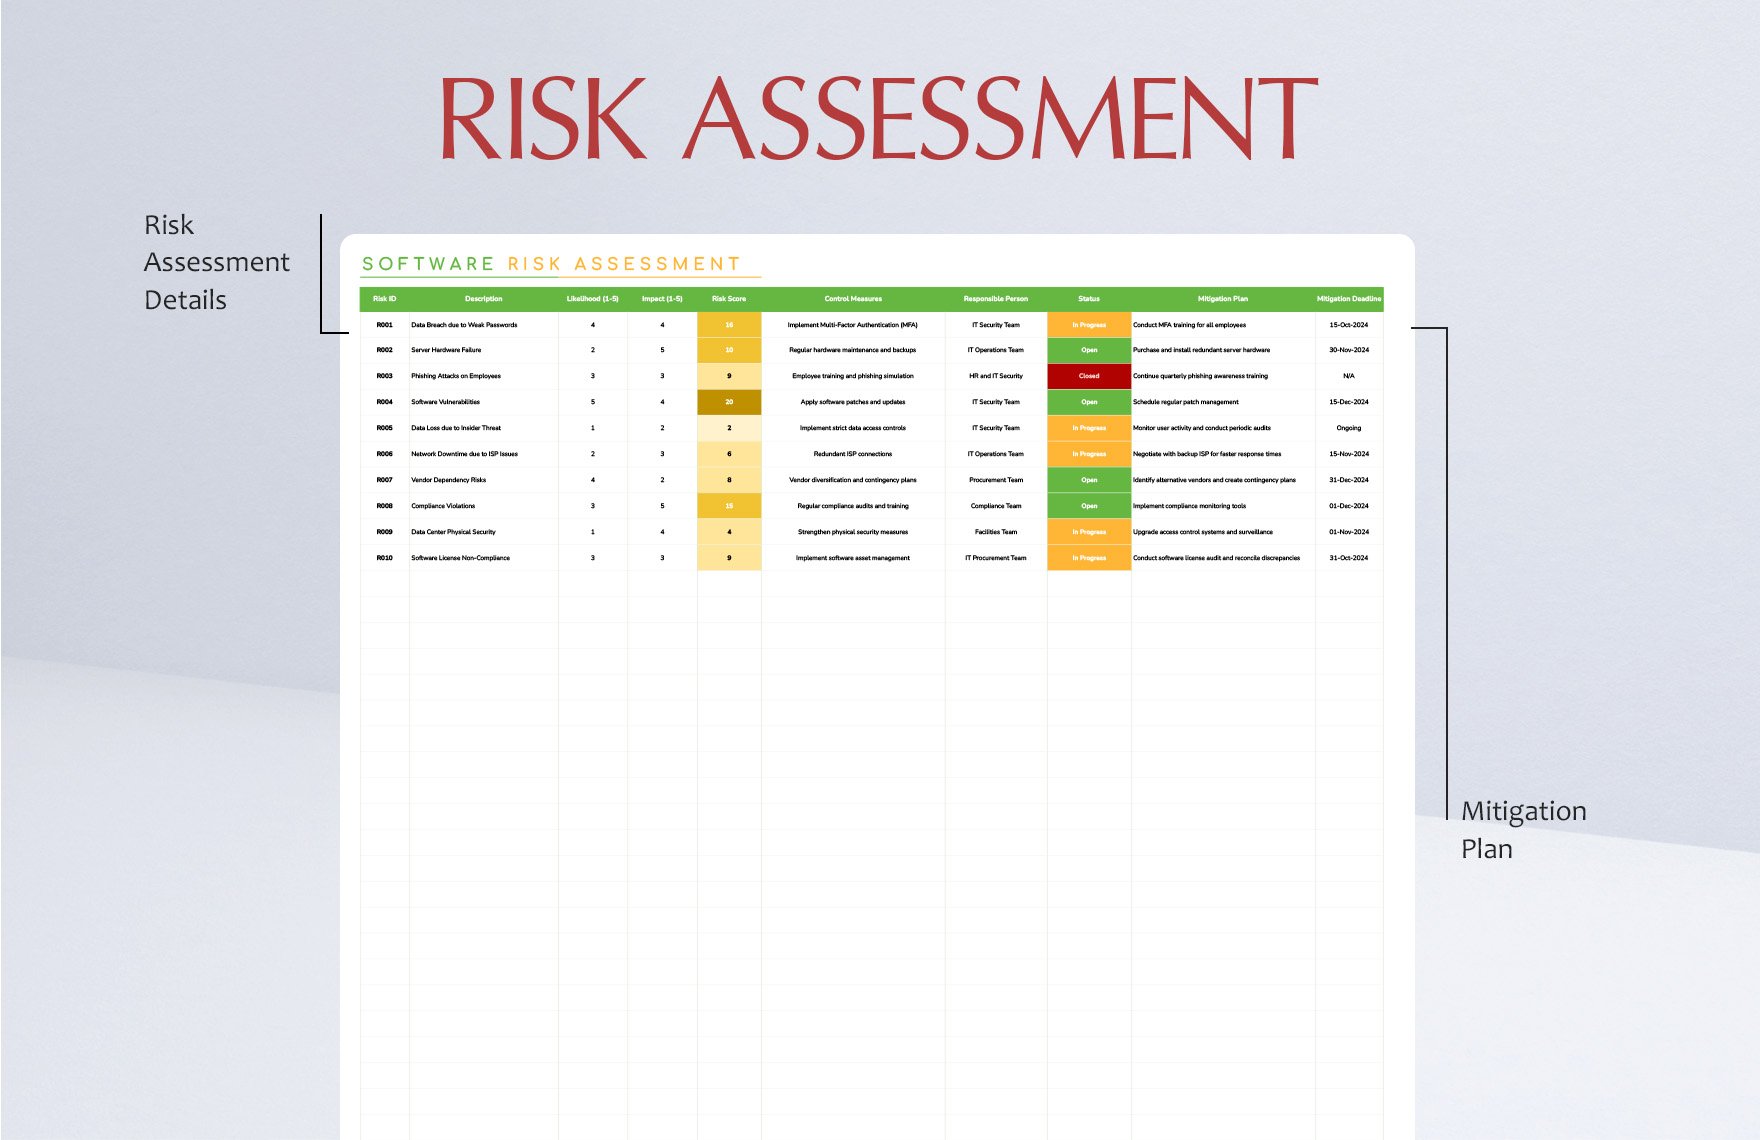
Start with a table structure. I recommend columns for: system/component, function, hazard description, potential consequence, severity rating, probability/frequency, detectability, risk priority number or risk matrix score, risk acceptability decision, risk control measure, residual risk reassessment, and responsible owner. That is the minimum. Anything less and auditors will ask questions you do not want to answer. The key mistake people make is rating severity too low for software issues. Hardware failures get rated high. Software bugs get rated "low impact" because nobody thinks about what a bad query does to patient results. In my experience, giving software risk a default severity of at least 4 out of 5 is more realistic. A corrupted test result goes to a physician. That is severity 5. Period. For the risk matrix, use a standard 5x5. Severity on one axis, probability on the other. Multiply them or map them through your matrix cells to get a risk score. Define clear cut-offs: low risk (green, accept with monitoring), medium risk (yellow, require mitigation), high risk (red, must mitigate before release). Keep those definitions documented somewhere in your quality system so the next auditor does not have to guess.
Fill in the template by walking through each system function. Do not skip the "what if the system generates a report at 2 AM and the timestamp is wrong" scenarios. Those edge cases are what cause problems during inspections. I learned this when a biopharma company's stability testing software had a clock drift issue that caused batch release dates to be off by three hours. The risk assessment had marked the timestamp function as "low risk" because nobody considered daylight savings time adjustments. That took three months of CAPA work to fix.
Get the Full Details
Common Pitfalls and What Actually Works
Most risk assessments I have reviewed are backward-looking. They assess risks after validation is already complete. That is backwards. The risk assessment should drive your validation protocol, not come after it. If a function is rated high risk, it needs comprehensive IQ/OQ/PQ. If it is low risk, a limited test suffices. I have seen the reverse happen constantly, where people write the protocol first and then try to justify the risk assessment. Another pitfall: treating all software the same. Not every module in your validated environment deserves equal attention. The dispensing module in an HPLC method gets more scrutiny than the audit log viewer. Use risk-based qualification to allocate effort where it matters. This approach can cut your validation documentation workload by roughly 40 percent in systems with many low-risk components. Interface risks are the biggest blind spot. Data flowing from one validated system into another is rarely assessed thoroughly enough. The sending system is validated. The receiving system is validated. Nobody validates that the data actually arrives intact. When we caught this issue, we added a data reconciliation check between the systems and tested it against boundary values. The risk score for the interface jumped from green to yellow immediately.
When the Template Approach Breaks Down
A spreadsheet-based Software Validation Risk Assessment Template works fine for systems with maybe a dozen functions. Once you hit twenty or more, the matrix becomes unwieldy and errors creep in. We migrated to a dedicated risk management tool for a GMP manufacturing execution system. It was slower upfront but eliminated cross-referencing mistakes and made it easier to link risks to test cases in the validation protocol. The template also fails when your system has dynamic risk factors. A standalone lab instrument has static risk. A cloud-hosted SaaS application that pulls in third-party data feeds changes risk profile as those feeds update. Static assessments become outdated quickly. If you are dealing with network-dependent systems, plan for periodic risk reassessment rather than treating the document as a one-time exercise. One more thing nobody mentions: the risk assessment is only as credible as the people who wrote it. If it is produced by a single vendor consultant who has never touched the equipment, inspectors will notice. Get your actual users involved in the hazard identification step. The operators know which screens cause the most frustration and which edge cases they work around with manual calculations. Those workarounds are risks you did not think of.