What the SPRS Self Assessment Score Actually Measures
The SPRS score is a numerical rating that comes out of the Supplier Performance Risk System, which DOD uses to evaluate how well a contractor meets cybersecurity requirements before they sign a contract. It's tied to CMMC and NIST SP 800-171, and it shows up during the DFARS clause compliance process. Most people encounter it when they're trying to bid on government work and suddenly realize their security posture needs to be quantified in a way that a procurement officer can compare across vendors. I've spent years watching companies panic over these scores, and the funny thing is most of the panic is unnecessary. The score itself is straightforward, but the path to getting a good one has enough traps that people consistently screw it up. Here is how it works in practice.
How the Sprs Self Assessment Score Is Calculated
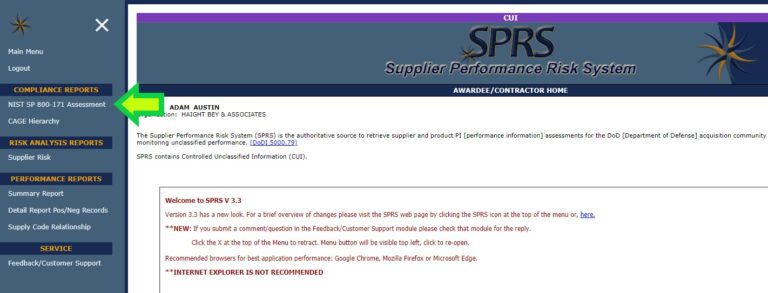
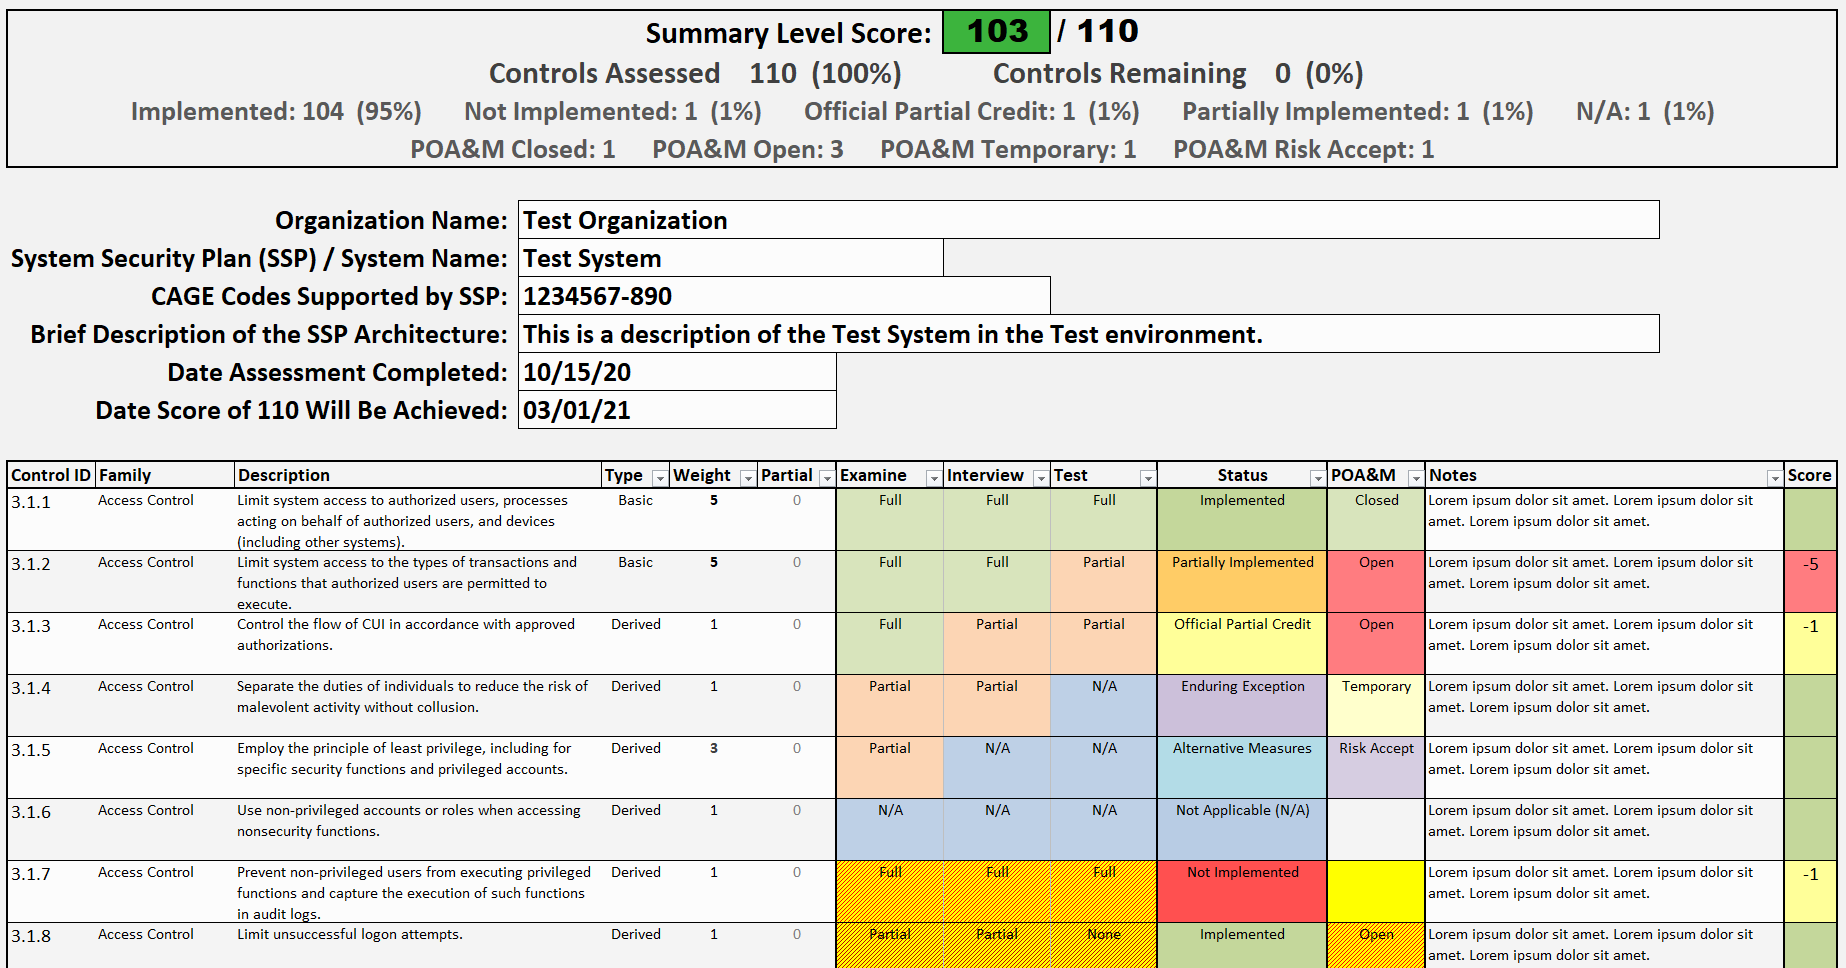
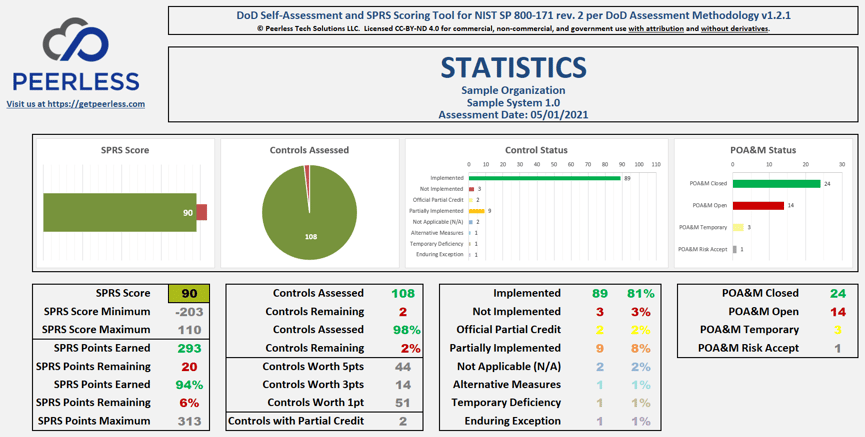
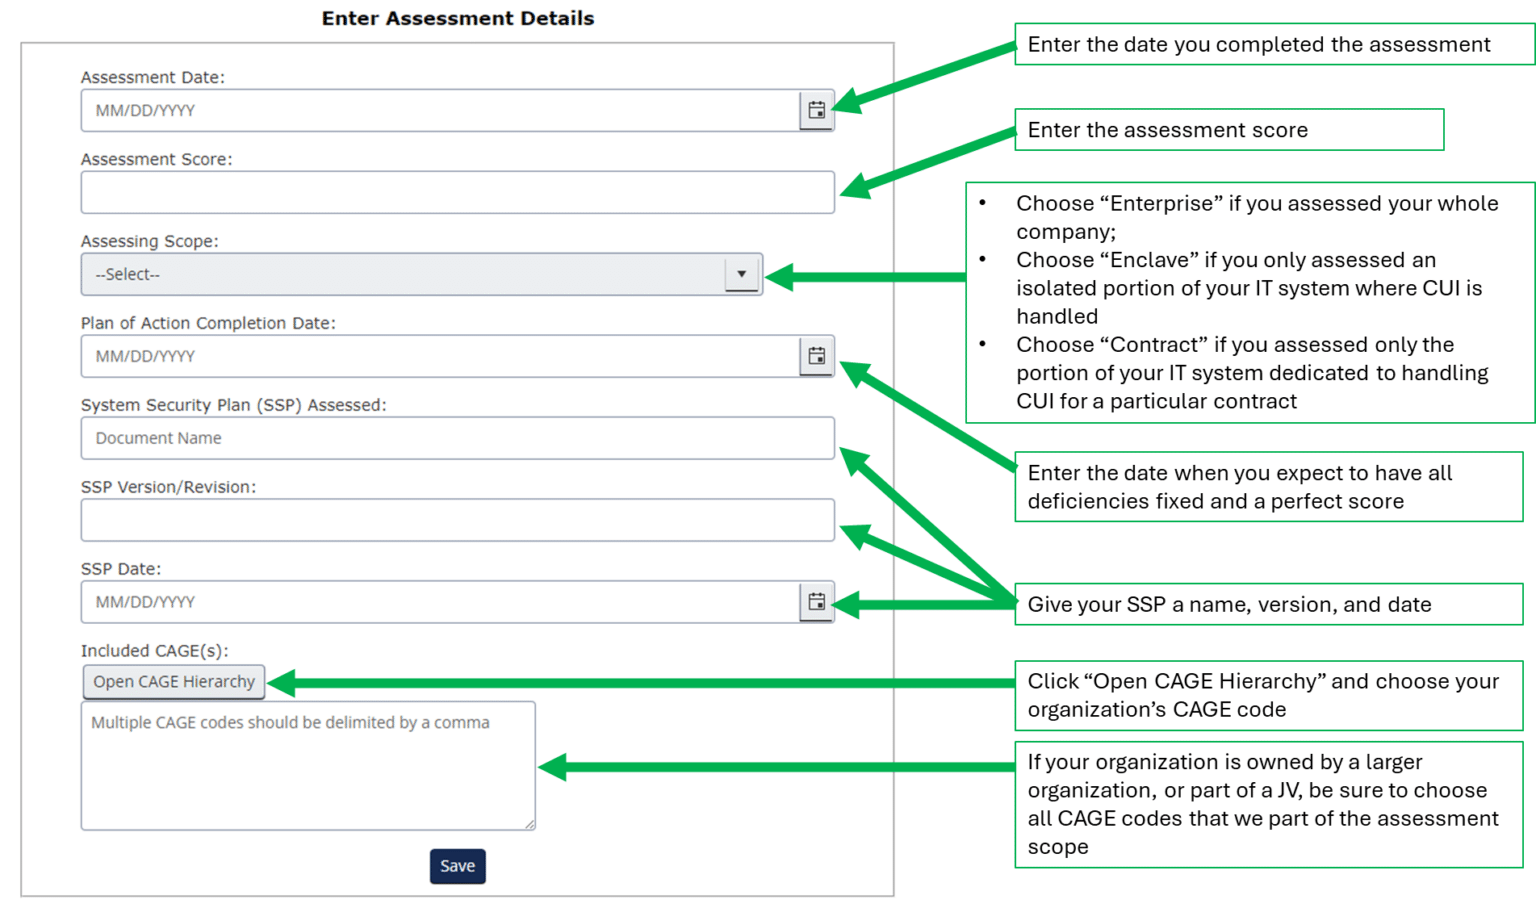
You start by completing the self-assessment within the SPRS portal. The assessment is built around the 110 control families from NIST SP 800-171 Rev 2. Each control has a maturity level, and you declare compliance or non-compliance with narrative evidence. The scoring formula then maps your declared compliance rate against a weighted distribution that emphasizes certain high-priority controls over others. The final output is a number between 0 and 110, where a higher number is better. Wait, that does not sound right at first glance. The scale actually goes from 0 to 110 points possible, and the score represents how many of those points you achieved. A score above 80 is generally what most contracts require, though some sensitive programs ask for 90 or higher. I remember working with a mid-size defense contractor who had an 85 score on paper but kept getting flagged during contract reviews. The problem was not the number, it was the evidence. Their self-assessment declared compliance on controls 3.13 and 3.14 but provided vague narrative responses like "we handle this internally" with zero supporting documentation. The reviewing officer could not verify anything, so they treated the entire submission as low-confidence and effectively nullified the score advantage. We went back and rebuilt those control responses with actual process documents, screenshots of access review workflows, and incident response plan excerpts. Their verified score stayed the same, but the confidence rating jumped from questionable to solid, and the contract evaluation cleared within two weeks instead of six.
The Practical Workflow Most People Get Wrong
Here is the sequence that actually matters. First you identify every system that houses CUI, not just the ones your IT department says are important. I have seen companies miss entire subnets that were quietly processing contract data because nobody communicated between the engineering team and the security team. Second you map each NIST control to those systems, not just to the organization as a whole. Third you declare compliance status and attach evidence. Fourth you review the calculated score and iterate before submitting. The fourth step is where the majority of failures happen. People treat the first calculation as final. They submit a 72 and wonder why their proposal gets bounced. I always run at least three revision cycles. The first pass identifies gaps, the second pass fills them with actual evidence, and the third pass cross-checks for consistency between the control declarations and the evidence artifacts. A control should never be claimed as compliant if the supporting document does not explicitly address the control requirement. This took me about 45 minutes per cycle on a medium-sized assessment, and it usually surfaces two or three issues that would have been caught by a reviewer later anyway. One thing nobody tells you about the SPRS portal: the scoring engine recalculates whenever you modify any control declaration. Sometimes it seems slow, and I have had sessions where the page hangs for a full minute after saving. Do not refresh. Just wait. I lost a complete revision once because I assumed the browser froze and hit reload, which reset my evidence uploads to their default empty state. It was 11 PM on a Friday and I had to rebuild from scratch the next morning. Save frequently, and export a local copy of your responses before every major editing session.
Get the Full Details
Common Pitfalls That Tank Your Score
The most common mistake is treating policy documents as evidence without verifying they actually cover the right controls. You can write a three-page information security policy and still score zero on control 3.1 because the policy talks about "confidentiality" in general terms without addressing the specific safeguarding requirement. The reviewer is looking for direct mapping, not aspirational language. Another pitfall is the assumption that all 110 controls apply equally. They do not. Some controls are marked as applicability-dependent, and marking every single one as applicable when only some are relevant creates an internal contradiction that reviewers notice immediately. If your system does not process payment data, claiming full compliance with financial control families while simultaneously having no financial data handling procedures looks suspicious. Be honest about applicability and document why each non-applicable control does not apply to your environment. There is also the issue of outdated evidence. I once reviewed a self-assessment where the control evidence referenced a firewall configuration from 2019, the incident response plan listed a former CISO, and the access review policy described a quarterly schedule that had been changed to monthly the year before. The score was technically accurate for the declarations made, but any reviewer with basic due diligence would flag the entire submission as unreliable. Evidence must be current and verifiable. A dated screenshot is worse than no screenshot at all because it signals negligence.
When the SPRS Score Is Not Enough
I need to be blunt about the limitations here. The SPRS self-assessment score is a first-pass screening tool, not a comprehensive security audit. It relies entirely on self-declared compliance with minimal verification in most cases. For high-sensitivity programs, especially those involving controlled unclassified information that supports weapons systems or intelligence-related contracts, the score alone will not satisfy the contracting officer. You may still be asked to provide additional documentation, undergo a formal security assessment, or achieve CMMC Level 2 certification through a third-party audit. The score also does not measure continuous compliance. A 92 today means nothing if your controls degrade six months later. I have watched companies treat the SPRS submission as a one-time checkbox exercise and then see their score drop the following year because they stopped maintaining their evidence trail. The system does not track drift automatically. You have to track it yourself. If you are preparing for a contract that requires more than a basic self-assessment, consider pairing the SPRS work with a gap analysis against NIST 800-171 before you start filling out the portal. This approach typically cuts the iteration time in half because you already know which controls will be problematic. I use a simple spreadsheet mapping each of the 110 controls to our current implementation status, notes on what evidence exists, and a priority flag for controls that are non-compliant or have weak evidence. Going into the SPRS portal with that spreadsheet in hand turns what could be a three-week struggle into a focused two-week effort.
The portal itself does not have a traditional download link since it is a government web platform, but you can access it directly through the SPRS website using your DUNS number and CAGE code credentials. Make sure your organizational profile is up to date before you begin, because incorrect metadata can cause submission delays that have nothing to do with your actual score.

A Quick Reality Check on Time Investment
A complete SPRS self-assessment for a small to mid-size contractor with moderate cybersecurity maturity typically takes between 20 and 40 hours of internal work, spread across security, legal, and IT teams. If your organization already maintains a robust NIST 800-171 compliance program, you are looking closer to 10 to 15 hours because most of the evidence already exists. If you are starting from scratch, expect the upper end or beyond, and plan to engage external help rather than attempting it alone under deadline pressure. The score itself is one output among several that matter in a government contracting context. Treat it as a checkpoint, not the finish line, and you will avoid most of the stress that comes with it.