Why most people never actually fix SQL injection properly
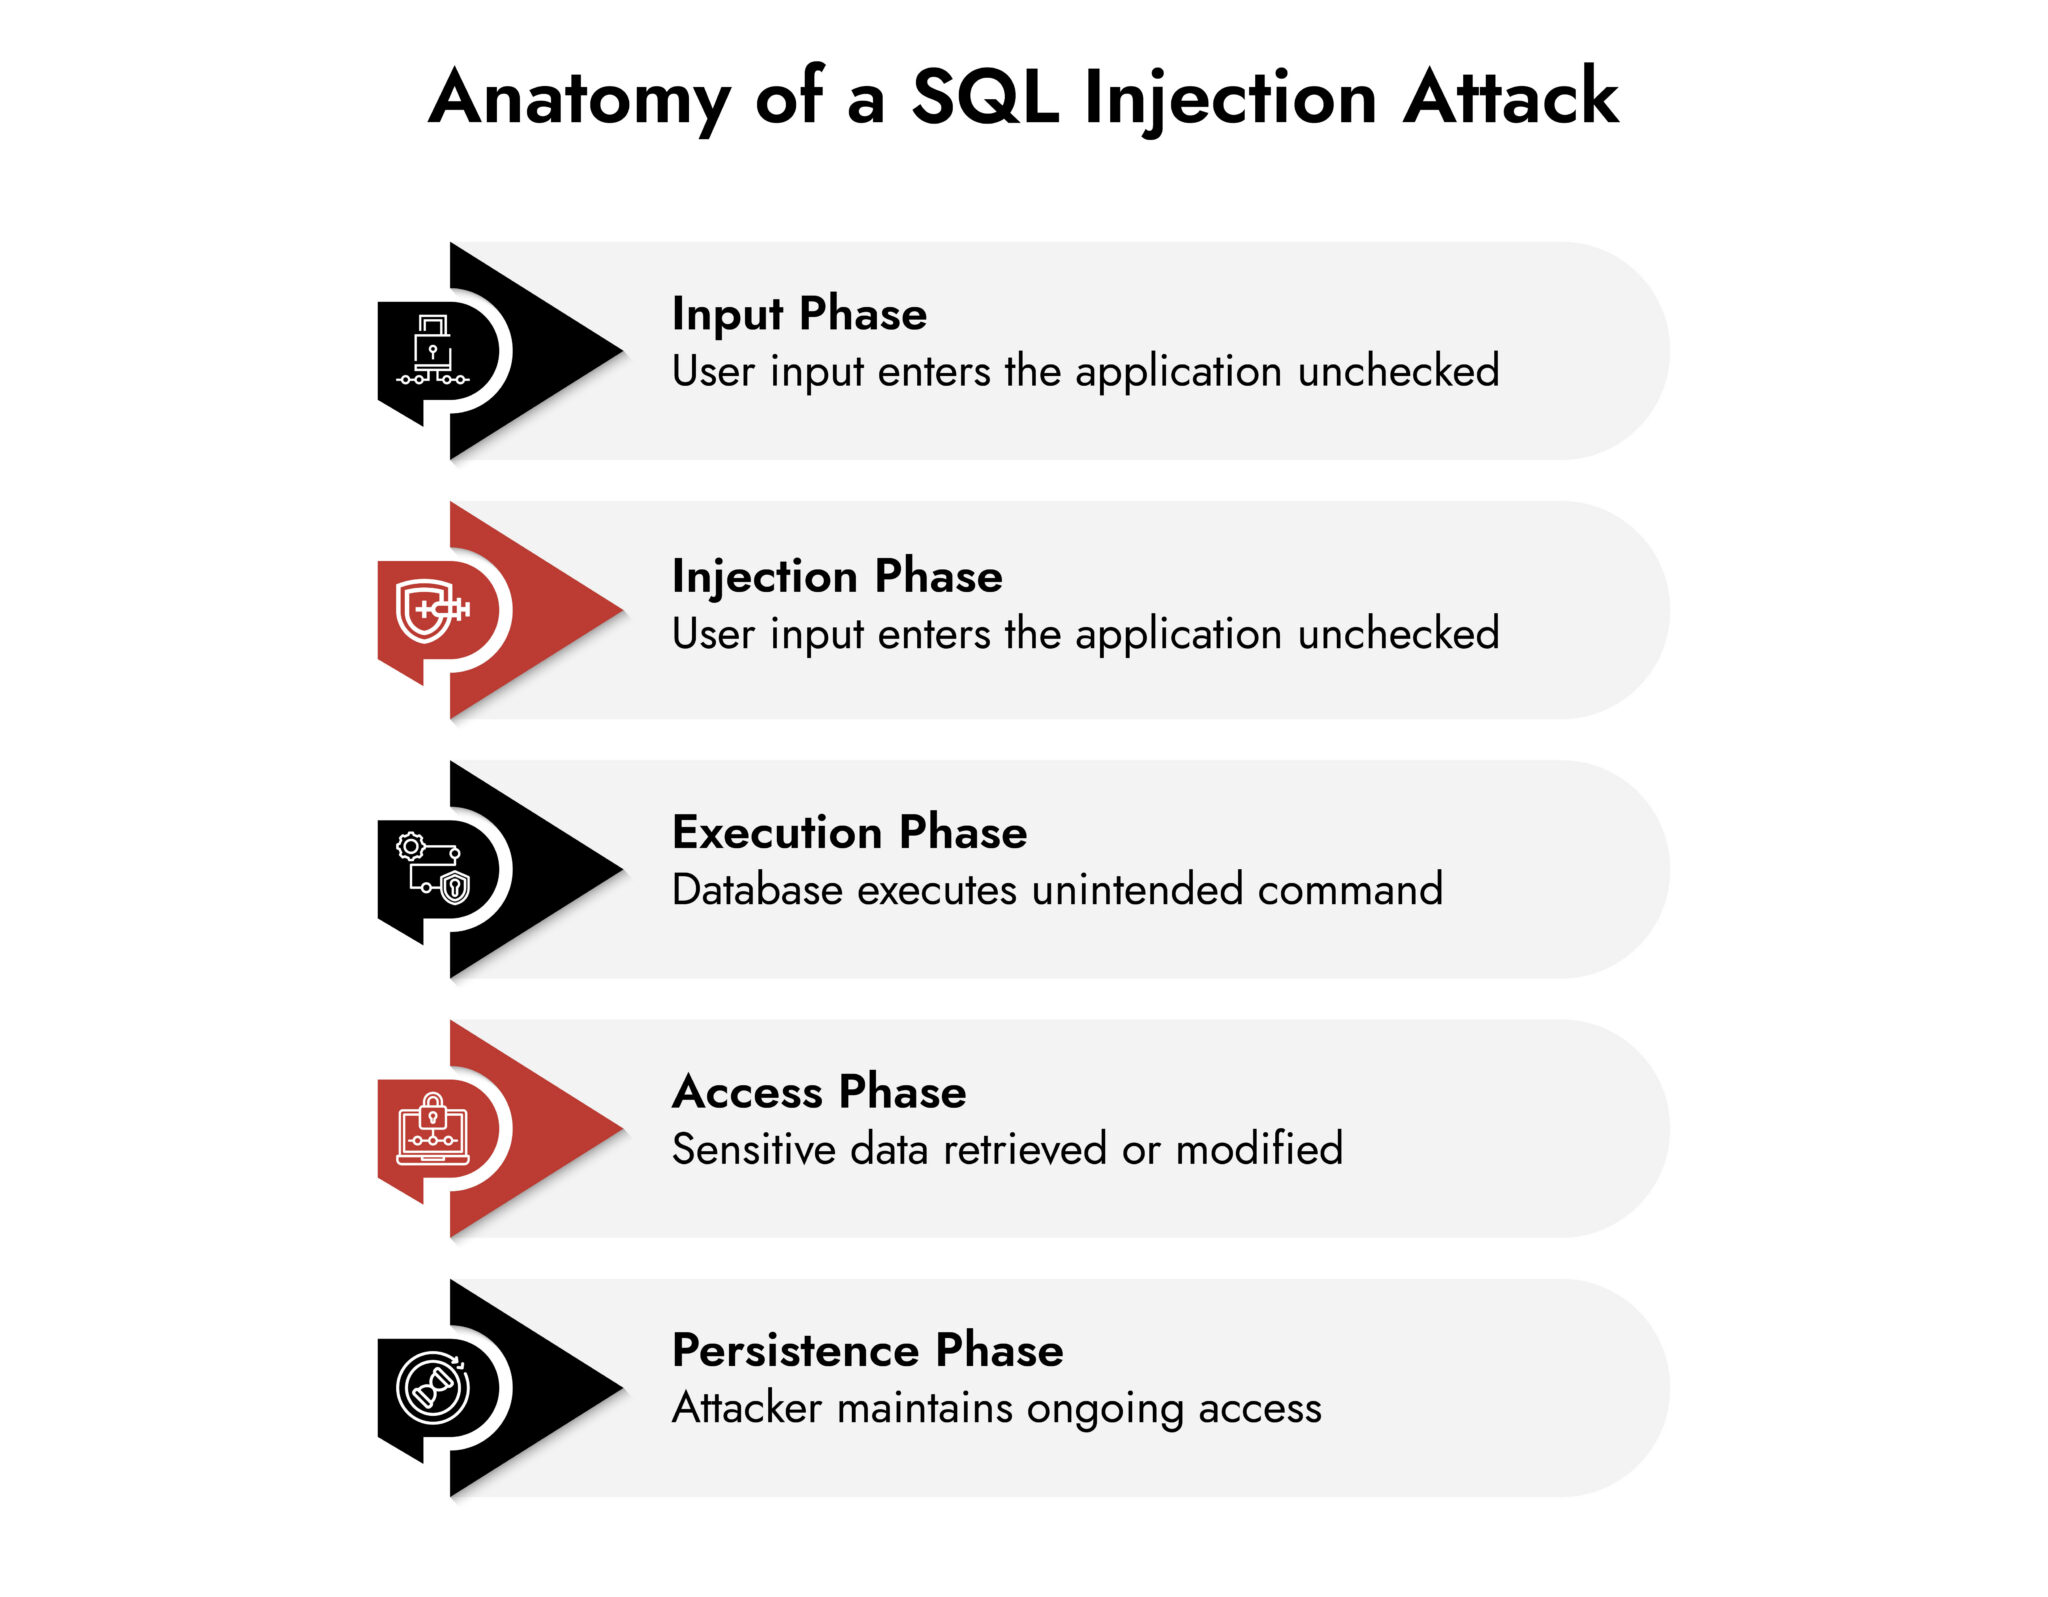
I spent about six years building and breaking database-driven applications before I stopped making rookie mistakes with query construction. The book that actually made things click for me is Sql Injection Attacks And Defense Second Edition, and I want to explain what it does well, what it misses, and how to actually use it instead of just reading it cover to cover. The second edition came out around 2010, and honestly a lot has changed since then. Modern ORMs, prepared statements as the default in most frameworks, and WAFs that catch even mediocre injection attempts have made the casual SQL injection attack far less common than it was. That said, the fundamental technique hasn't changed, and the book covers the anatomy of the attack better than most newer guides that skip straight to "use parameterized queries and you're done."
Sql Injection Attacks And Defense Second Edition
What this book gets right is the layering of attacks. Most beginners learn about UNION-based injection and stop there. They think they understand the problem because they can dump a database in a lab environment. The book walks through blind injection, error-based extraction, time-based techniques, second-order injection, and stored procedure manipulation. That progression matters because real-world targets don't usually leave the query structure exposed in a visible error message. The actual technique section starts with understanding how user input reaches the database. Most developers I've worked with skip this step. They see a form field and immediately start writing sanitization logic without mapping the full request path from entry point to query construction. The book emphasizes this mapping more than any other resource I've read. You need to trace every parameter, header, cookie, and URL segment that could make its way into a query before you can defend against it. I remember doing a code review on a PHP application in 2017 where the developer had properly parameterized every direct query but completely missed a case where input from a session variable was being concatenated into a stored procedure call. The session variable was originally set from user input three requests earlier. That kind of second-order injection is exactly the scenario the book covers in detail, and it's also the kind of bug that shows up in pentest reports with alarming frequency.
How to actually apply what's in the book
Reading the book will give you about forty percent of the practical value. The remaining sixty comes from applying the techniques in a controlled environment and then seeing them fail in real applications. I set up a local SQL injection lab using DVWA or WebGoat, work through every example in the book, and then deliberately introduce the vulnerabilities into my own test applications to verify I understand the mechanics. The book includes a section on defense strategies that most readers gloss over. It covers input validation using allow-lists rather than deny-lists, parameterized queries at the application layer, stored procedures with proper parameter binding, least-privilege database accounts, and output encoding. The key insight is that no single layer is sufficient. Input validation can be bypassed. Stored procedures can be invoked with malicious parameters. The database account shouldn't have permissions it doesn't need. These layers work together, and the book explains the interaction between them better than most defensive security literature. One thing the book doesn't address well enough is the relationship between ORM usage and SQL injection. Many developers using Hibernate, Entity Framework, or Django ORM assume they are protected from injection. They are partially correct. Parameterized queries handle the vast majority of injection vectors when you use the framework correctly. But these ORMs have their own vulnerabilities, and the book doesn't cover ORM-specific attack surfaces that have emerged since publication. Things like LINQ injection in Entity Framework or HQL injection in Hibernate require separate study.
Get the Full Details
A specific problem I ran into and how I solved it
I was auditing a legacy application in 2019 where the developer had implemented input validation through a regex-based filter that blocked common injection keywords like SELECT, UNION, and DROP. It looked secure on paper. It wasn't. The application ran on SQL Server, and I discovered that double-byte character encoding allowed the injection to slip through the filter entirely. The filter was checking ASCII values before the connection string converted the multibyte characters, and the query construction happened after that conversion on the server side. The fix wasn't adding more regex patterns or blacklisting more keywords. It was replacing the entire input validation approach with parameterized queries for every database interaction, removing the concatenation-based query building entirely, and adding a Web Application Firewall rule as a secondary layer. The book's chapter on layered defense strategies guided this approach, but the specific encoding bypass wasn't covered in depth. That kind of detail only comes from experience with real systems. Annoyingly, this same application had the SQL Injection Attacks And Defense Second Edition listed in its training materials for the development team. The team had read it. They just hadn't internalized the principle that input validation is never a primary defense. It's a supplementary layer at best.
What this book won't help you with
The second edition is limited by its publication date. Cloud database architectures, NoSQL injection, and the shift toward API-first applications mean that modern SQL injection defenses require a broader toolkit than the book provides. If you're working with MongoDB, Cassandra, or cloud-hosted databases with serverless query builders, the techniques in this book still apply conceptually but the specific exploitation and defense strategies differ significantly. The download situation is also worth mentioning. The official source is from the publisher, Packt Publishing, through their website or authorized resellers like Amazon. There are many unofficial PDF versions circulating on forums and file-sharing sites, but I wouldn't recommend using those. They're often outdated, may contain injected content themselves, and the author and publisher deserve compensation for the work. The book is reasonably priced and available in both print and legitimate digital formats. If you're looking for a free alternative to complement this book, OWASP's SQL Injection prevention cheat sheet covers the parameterized query approach with code examples in multiple languages. It's not as comprehensive as the book but it's current and freely available. For hands-on practice, PortSwigger's Web Security Academy has a well-maintained SQL injection lab section that covers both classic and modern variants.
The bottom line is that this book remains one of the better technical resources on the topic, even nearly two decades after publication. The fundamental concepts haven't aged poorly. What has changed is the tooling and the attack surface, so you'll need to supplement it with more recent materials on ORM vulnerabilities and cloud database security. But for understanding how SQL injection actually works and why naive defenses fail, it's still worth your time.