The JavaScript Checklist Nobody Talks About
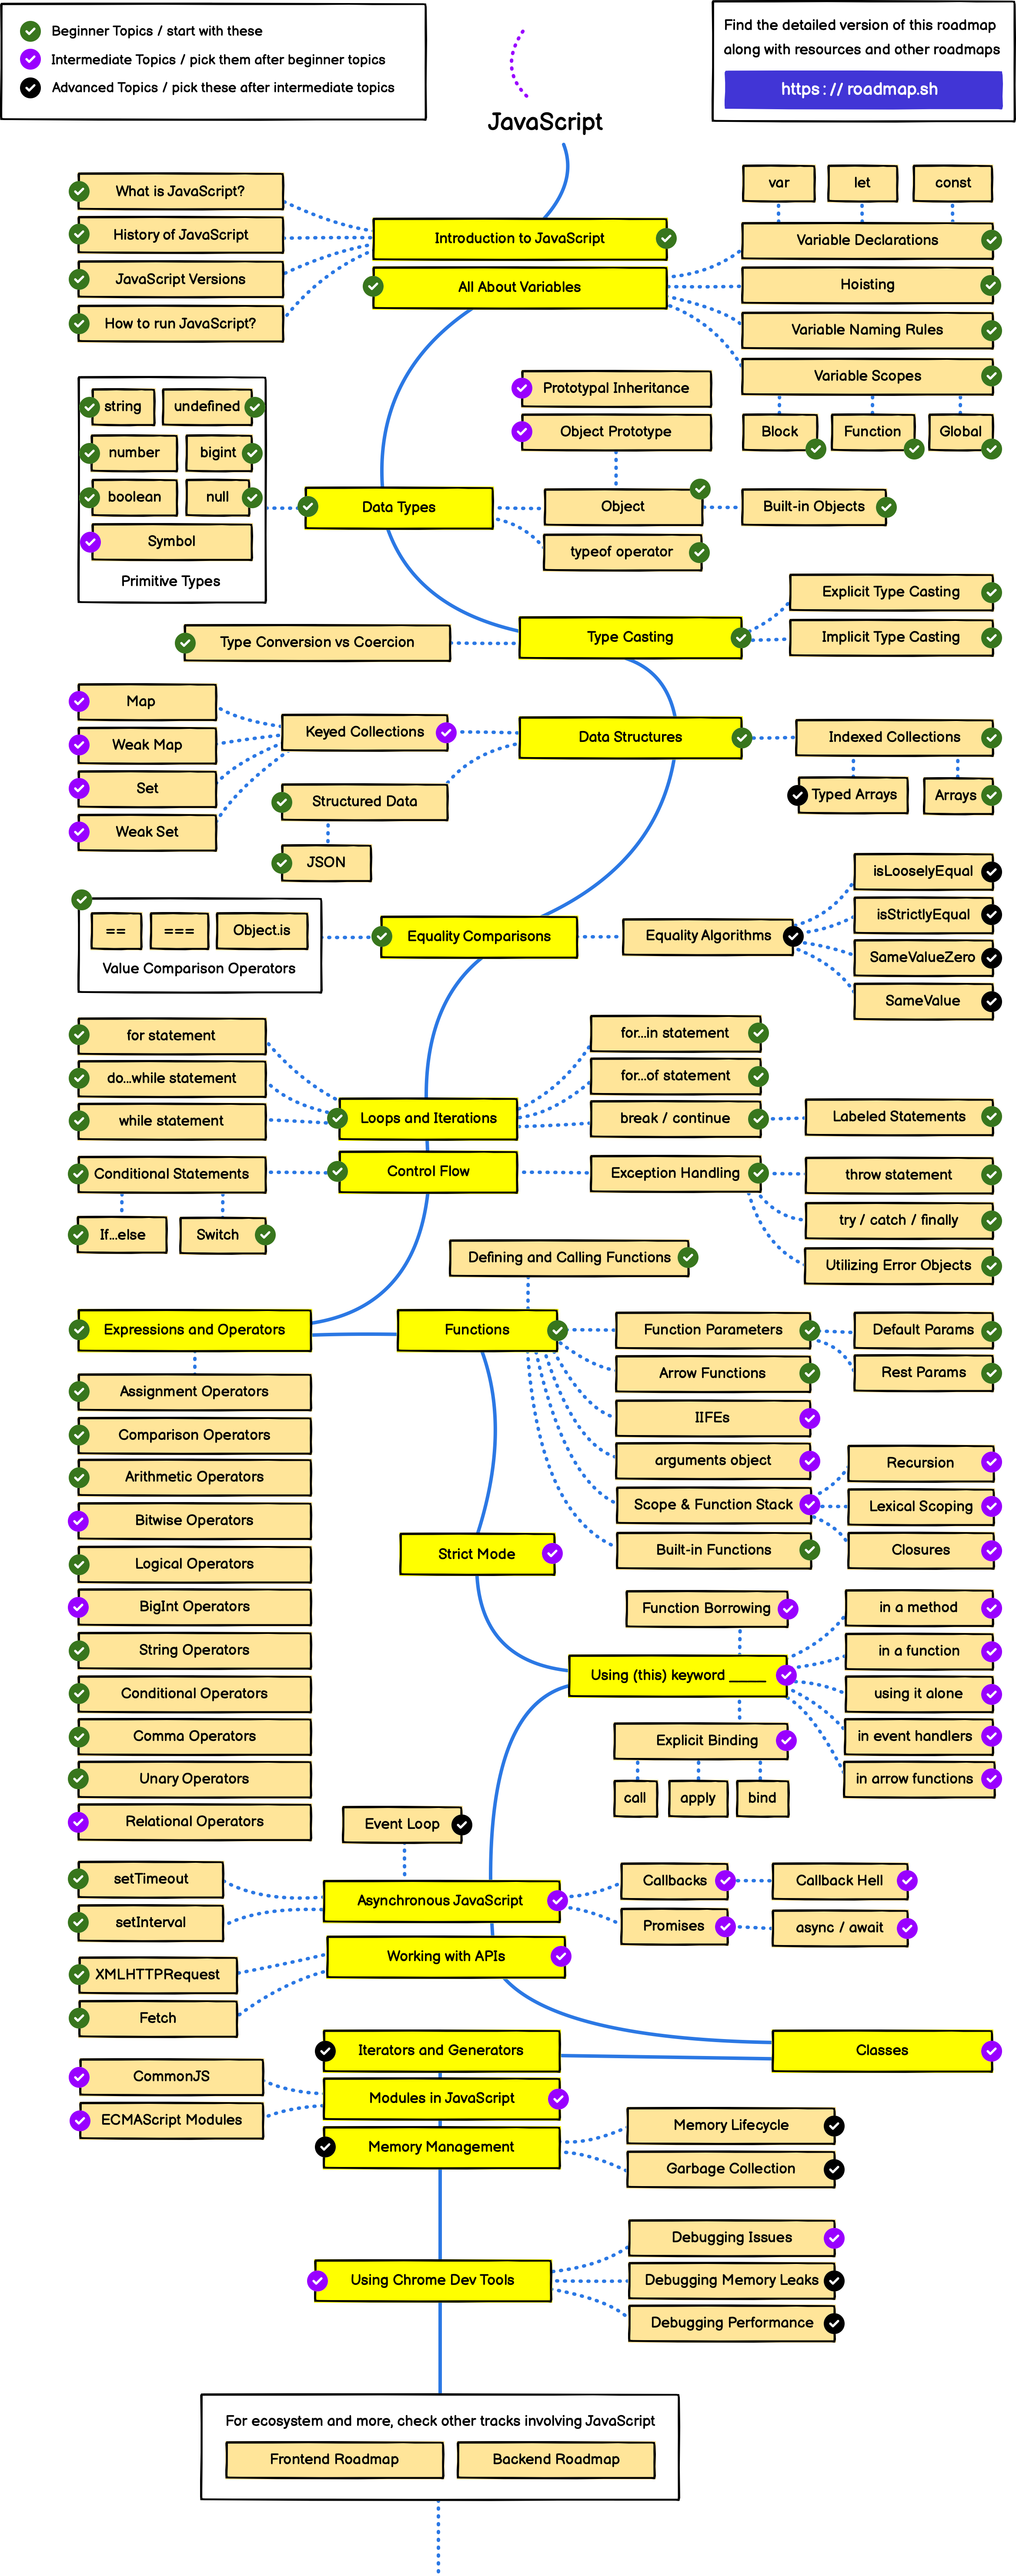
Most people look for a JavaScript checklist and immediately find lists of browser support tables or code review items that feel like they were written by someone who's never actually shipped a production app. The useful ones aren't the ones with fifty checkboxes. They're the ones that mirror the actual sequence of decisions you make before, during, and after writing code.Step By Step Guide For JavaScript Checklist
Start with environment setup, move to syntax validation, then dependency verification, and only then worry about optimization. That order matters more than most developers realize. I once spent six hours debugging a build failure that turned out to be caused by running the minification step before a polyfill was properly injected into the bundle. The error message pointed at webpack config syntax. It had nothing to do with webpack config syntax. After that, I started putting environment checks and polyfill injection before any minification step on every project. It added roughly forty seconds to the build but eliminated an entire class of silent failures.Step one is always the same: verify your runtime and tooling versions. Node version mismatches are the single most common source of "it works on my machine" complaints in JavaScript projects. Check your package.json engines field against what's actually installed. Run nvm ls or fnm ls to see what your shell is resolving to. If you're using a monorepo, check whether each workspace has its own .nvmrc file and whether your CI pipeline is reading it. Step two covers syntax validation across all target browsers. This isn't just about linting. ESLint will catch missing semicolons and undefined variables. It won't tell you that a customer using an older Samsung Internet browser is getting a SyntaxError because you used optional chaining. Use Browserslist to define your targets, then run @babel/preset-env with the correct configuration. The presets handle transpilation automatically, but only if your .browserslistrc file or the browsers key in package.json matches what your actual users are running. I've seen teams ship code targeting "last 2 versions" and then wonder why error rates spiked after a major OS update pushed older browser versions back into relevance. Step three is dependency verification. Run npm audit or yarn audit. Then run npm outdated. These are not optional. I've encountered projects where a minor version bump in a seemingly harmless utility library introduced a breaking change in a TypeScript type definition, and the build passed silently because the type checking was disabled in the CI pipeline. Check whether your dependencies declare their peer dependencies correctly. Missing peer dependency warnings from npm or yarn are easy to ignore but they indicate real conflicts that will surface later.
Step four addresses module resolution and bundling. If you're using webpack, rollup, or vite, your configuration file is as important as your application code. Verify that your entry points resolve correctly. Check that your aliases don't create circular dependencies. I once found a project where a path alias pointing to a shared utilities folder was resolved differently between development and production builds because the dev server was using a different node_modules resolution strategy. The bug only appeared in staging after deployment. Aligning the resolver configuration between dev and prod environments fixed it immediately. Step five is testing coverage, not percentage. A test suite with eighty percent coverage that misses your authentication flow and error boundary handling is worse than a fifty percent suite that covers the critical paths. Map your tests to the user journeys that would cause production incidents. Integration tests around your API client layer usually pay the highest return. I recommend spending the most time on tests that verify how your code handles unexpected responses, network timeouts, and malformed data. These are the cases that don't show up in happy-path unit tests but cause support tickets at two in the morning. Step six is performance budgeting. Before you ship, measure your bundle size. Use webpack-bundle-analyzer or vite-bundle-visualizer to see what's actually being included. Tree shaking only works when your dependencies are properly marked as side-effect-free in their package.json files. I've wasted hours tracking down why a library I thought was being tree-shaken was still adding fifteen kilobytes to the final bundle. The fix was usually that the library's main export was a CommonJS module wrapped in ESM, which prevented proper dead code elimination. Switching to the library's explicit ES module build path resolved the issue.
Step seven is error handling verification. Every async operation needs an error boundary or a catch handler. Promise rejections that aren't caught will fail silently in modern browsers and produce no console output unless you add window.addEventListener('unhandledrejection'). I always add that listener in development. It caught an unhandled promise rejection in a payment form that was silently failing and causing incorrect order confirmations. The fix took five minutes. The investigation took two days because nothing was showing up in the logs. Step eight is deployment verification. Check that your environment variables are correctly injected at build time and that no sensitive values are leaking into the client bundle. Use dotenv for local development and configure your build tool to replace environment variable references with compile-time constants. I once pushed a build where an API key was visible in the compiled JavaScript because the build tool was reading from process.env instead of injecting the value at build time. It wasn't a security breach because the key was restricted to our internal staging domain, but it was a close call. Verify your .env files are in .gitignore before every deployment. There are scenarios where this checklist approach breaks down. If you're working on a rapid prototype with no user base, running through all eight steps will slow you down unnecessarily. The checklist is designed for production code that needs to survive real traffic and real failure modes. For internal tools with five users, a subset covering steps one, three, and six is usually sufficient. For consumer-facing applications with high availability requirements, you should also add load testing and canary deployment validation to the list.
Get the Full Details
The biggest mistake I see developers make with JavaScript checklists is treating them as a one-time pre-launch activity. The checklist should be part of your development workflow, not something you fill out right before you push to production. Add environment verification to your pre-commit hooks. Run the dependency audit as part of your CI pipeline. Make the checklist invisible infrastructure rather than a manual ritual. That's how you actually catch problems before they reach users.