What People Get Wrong About the TCP/IP Model
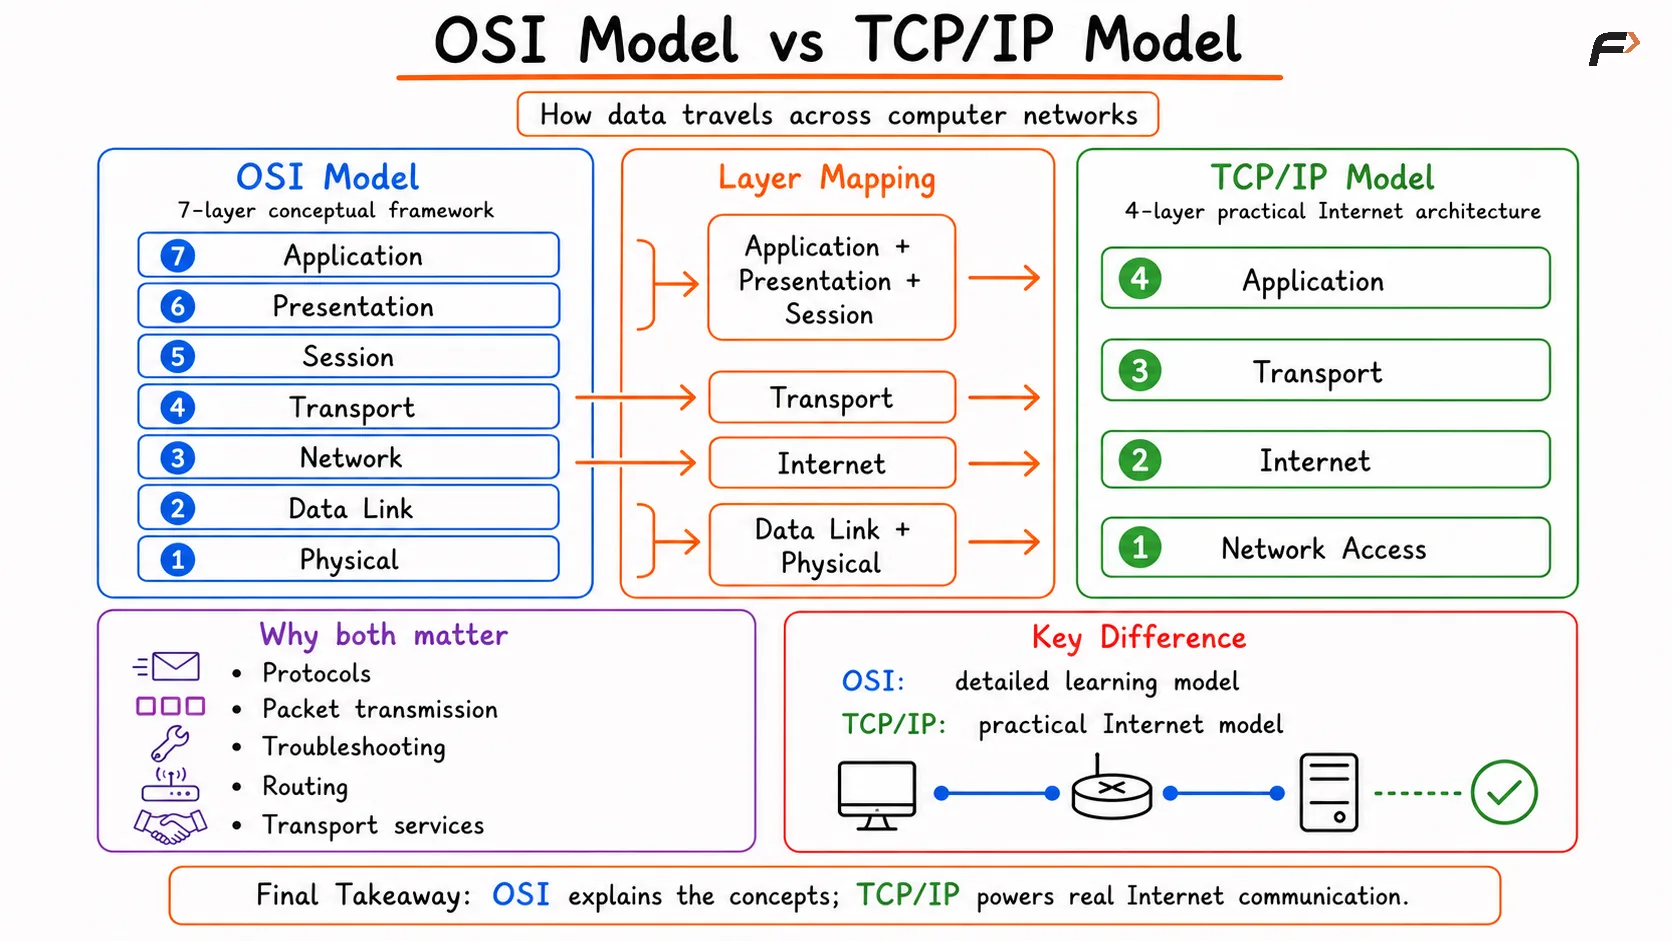
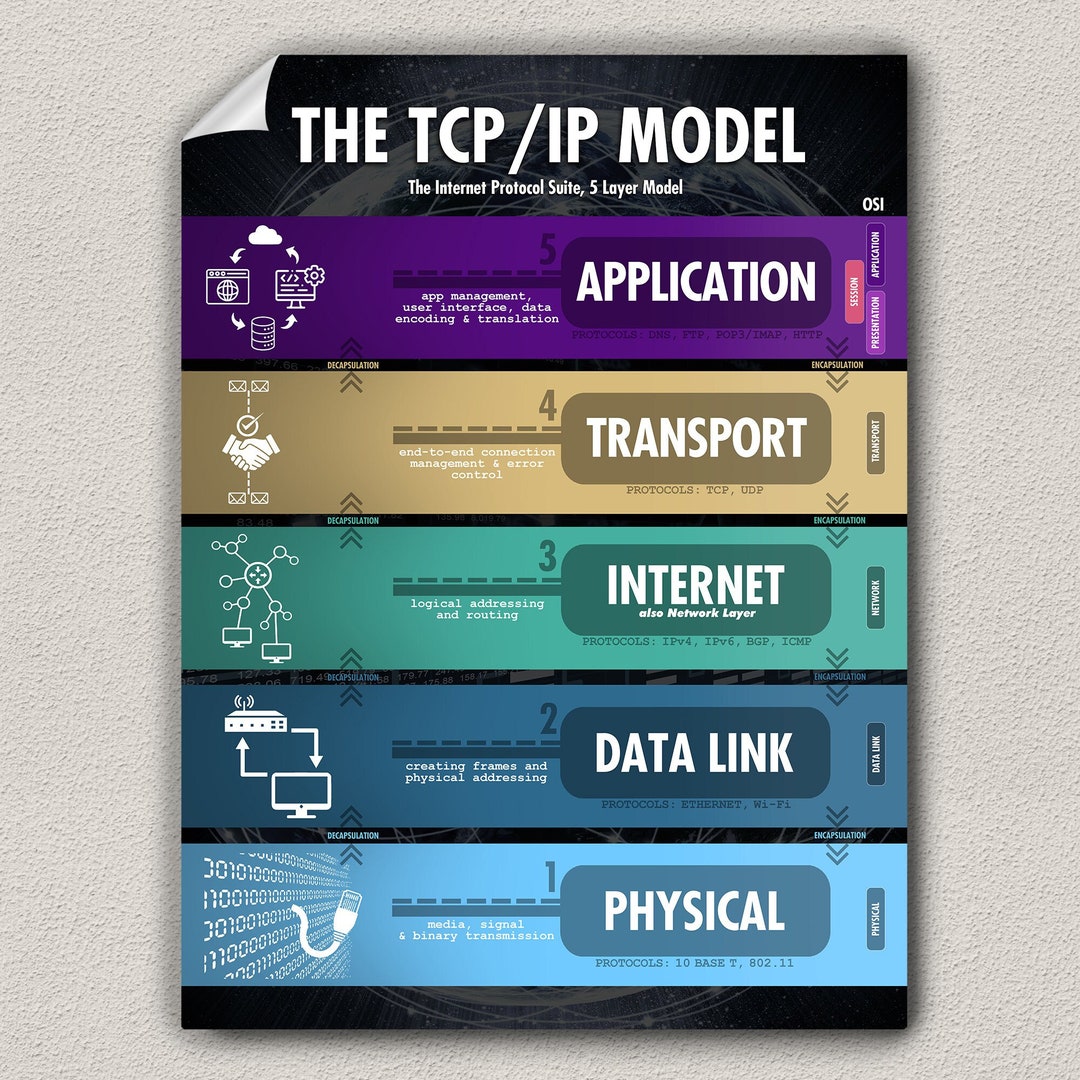
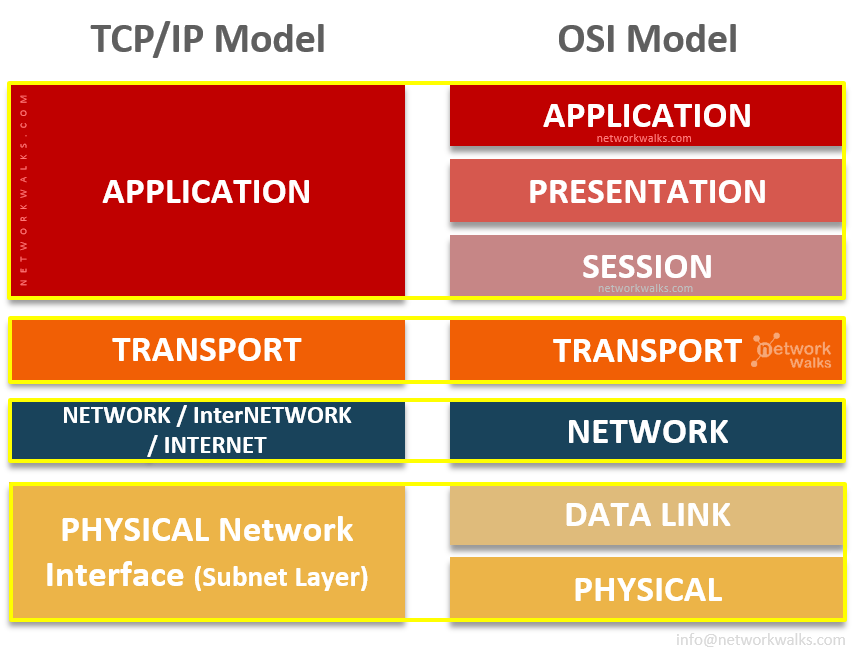
Most networking courses teach the OSI model as the canonical framework, and that's technically fine for academic purposes. The reality in production is that nobody in the industry actually thinks in seven layers when troubleshooting. The TCP/IP model, which boils everything down to four layers, is what you work with day to day. When you're staring at a packet capture or a core routing table, the four-layer abstraction maps better to what's actually happening on the wire. The Tcp Ip Model In Networking is not some dusty textbook concept. It's the mental model every sysadmin and network engineer uses while pulling their hair out at 2 AM. I spent years configuring Cisco routers and then spent another decade dealing with Linux-based infrastructure. The two worlds converge on the same four layers. You just need to understand what each one does in practice, not memorize the RFC definitions. Here's how it breaks down.
Application Layer
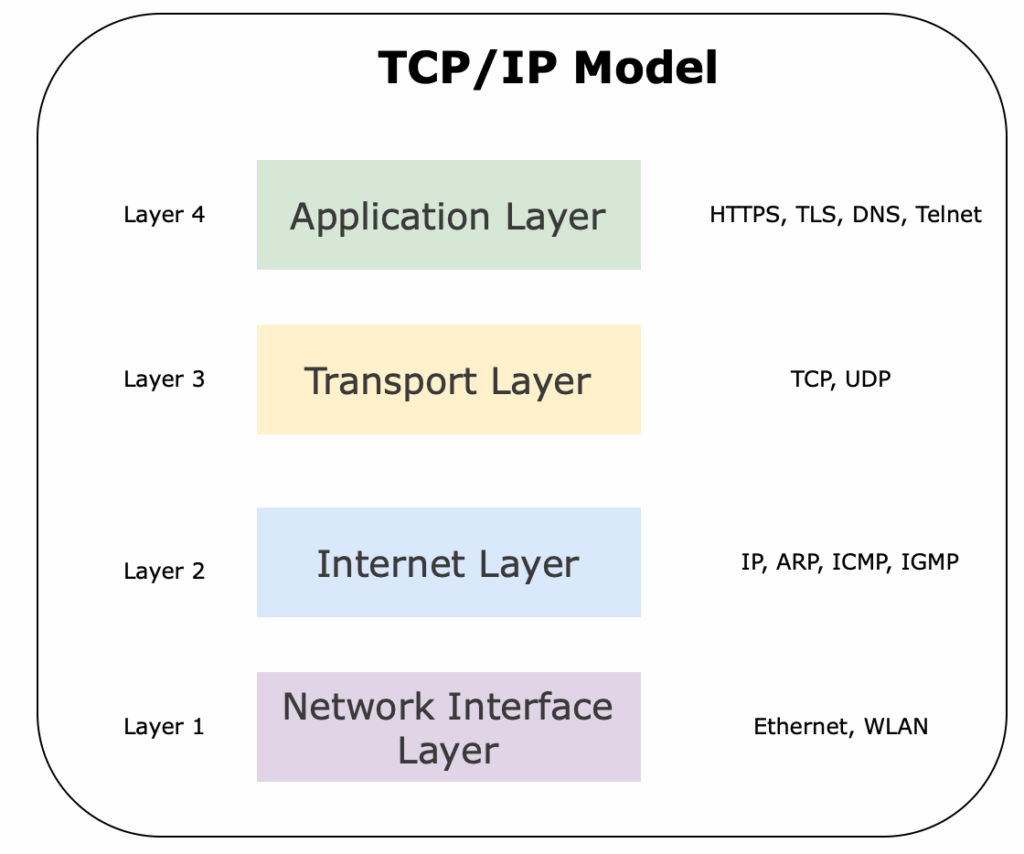
This is where your software talks to the network. HTTP, SSH, DNS, SMTP. Anything an end user or application directly invokes lives here. The confusion most people have is thinking the application layer is the same thing as "apps." It's not. Your browser is the client application, but HTTP is the protocol at the application layer. Same distinction applies to DNS, SSH, and everything else sitting at that top tier. Common pitfall: When someone says "the app is broken," 80 percent of the time it's not an application-layer problem at all. It's a lower layer issue masquerading as an app failure. A half-open TCP connection stack from a dropped link won't look like a bug in your code. It'll look like your service is hanging. If you're diagnosing properly, start by confirming whether the transport layer is even established before touching the application logic.
Transport Layer
TCP and UDP live here. That's it. Two protocols, wildly different behaviors, and both critical. TCP gives you ordered, reliable delivery with congestion control. UDP gives you speed with zero guarantees. The transport layer is responsible for port addressing and segmenting data into manageable chunks. The thing about TCP that nobody teaches you: the three-way handshake (SYN, SYN-ACK, ACK) is where most latency problems surface. A typical round trip over a managed WAN link is 50-100ms. That handshake alone eats 150-300ms before any application data flows. Over the public internet with poor peering, you can easily see 600ms to a second just for the handshake. This is why HTTP/2 and HTTP/3 exist and why keepalive connections matter so much. Counter-intuitive insight: TCP retransmissions don't always mean packet loss. Modern TCP stacks interpret rapid duplicate ACKs as an implicit signal to fast retransmit before timeout. If you're seeing retransmits in your capture, check the sequence numbers first. Out-of-order delivery causes retransmits even with zero lost packets. I encountered this exact scenario with a misbehaving NIC driver on an ESXi host. The driver was reordering packets at the hardware level, and the TCP stack below it was convinced the network was broken. Took me three hours and a Wireshark display filter to see it.
Get the Full Details

Network Layer
This is IP's domain. Routing, addressing, fragmentation. The IP header contains source and destination addresses, TTL, protocol identifier, and checksum. Routers operate here, making forwarding decisions based on routing tables. This layer handles the logical addressing scheme that makes global connectivity possible. The network layer is also where NAT lives, which is its own special brand of pain. Network Address Translation breaks the end-to-end principle that TCP/IP was designed around. It's a practical necessity given IPv4 address exhaustion, but it means devices behind a NAT gateway are invisible to external initiators without explicit port forwarding or UPnP configuration. I once spent a full day troubleshooting why a monitoring server couldn't reach a database host behind a corporate NAT. The routing was correct, the firewall rules allowed the traffic, but the return path was asymmetric because of a secondary internet uplink the network team had added without updating the NAT translation table. tcpdump on the target host showed the SYN arriving, but the SYN-ACK never made it back through the right gateway. Fix took about eight minutes once we found it.
Link Layer
Also called the network access layer or network interface layer. This is Ethernet, Wi-Fi, PPP, VLAN tagging, MAC addressing, ARP. The link layer handles frame construction, physical addressing, and error detection at the hardware level. ARP (Address Resolution Protocol) operates here, mapping IP addresses to MAC addresses on local segments. Hard-won lesson: The link layer is where you should start when something is completely down. IP won't route if you can't even resolve the next-hop MAC address. A flapping physical port, a misconfigured VLAN, or a corrupted ARP table will make everything above it appear broken. Check your physical indicators, verify your VLAN assignment, and run arp -a before you touch any IP-level configuration.
How the Layers Interact in Practice
Data flows down the stack on the sending side and back up on the receiving side. Each layer adds its own header (and sometimes trailer). By the time an HTTP request leaves your machine, it has accumulated headers from all four layers plus the link layer's frame check sequence. The reverse happens on receipt. Each layer strips its header, processes the information, and passes the payload to the next layer up. This encapsulation and decapsulation is what makes the layered architecture work. The beauty is that each layer operates mostly independently. Your HTTP implementation doesn't need to know anything about Ethernet frame construction or IP routing decisions. What beginners miss: The layers are a logical abstraction, not physical reality. Packets don't literally travel down wires labeled "layer 3" and then get promoted to "layer 4." It's an organizational framework that helps you reason about complexity. In actual hardware, these functions are often implemented together in ASICs and NICs that process entire frames in a single pass.

A Real-World Debugging Story
Here's a concrete example that demonstrates why understanding all four layers matters. A client reported that their API responses were intermittently slow, occasionally timing out entirely. The application worked fine from the office but failed from a specific remote site. Simple enough, right? The first step was ruling out application-layer issues. The API endpoint responded quickly from other locations, so I moved down to the transport layer. TCP connections were establishing, but I noticed frequent retransmits from the remote site in the packet capture. That pointed to the network or link layer. The network layer looked normal. Routing was correct, MTU values matched, and no IP-level errors. I dropped to the link layer and found the smoking gun: the remote site was using a Cisco switch with Spanning Tree Protocol enabled on an access port that connected to their VoIP phone and PC. The PC was actually connected through the phone's pass-through port, which meant the STP topology changes from the phone's VLAN were affecting the data VLAN. Every time the phone re-registered with the call manager, STP reconverged, causing a brief network partition that dropped existing TCP connections.
The fix was enabling PortFast on the switch port and configuring BPDU guard. This told the switch not to run spanning tree transitions on that edge port. Response times normalized immediately after the change. The root cause was entirely at the link layer, but it manifested as application-layer timeouts. Without understanding the full TCP/IP stack, you'd keep chasing the wrong problem.
IPv6 and the TCP/IP Model
IPv6 changes some things but not the fundamental layer architecture. The four layers remain the same framework. What changes is the addressing, the header format, and a few protocol behaviors. IPv6 eliminates ARP and replaces it with Neighbor Discovery Protocol (NDP), which operates at the link layer but uses ICMPv6 messages that technically sit at the network layer. This cross-layer behavior is normal and reflects the fact that real-world implementations don't respect theoretical boundaries perfectly. One practical difference: IPv6 link-local addresses (fe80::/10) are required for Neighbor Discovery, which means every IPv6 interface needs a link-local address even if it has a globally routable address. This is handled automatically by most modern OSes through stateless address autoconfiguration (SLAAC). If you're configuring IPv6 manually, don't skip the link-local address. NDP won't work without it, and you'll wonder why the next-hop resolution fails.
When the TCP/IP Model Falls Short
The four-layer model is pragmatic, not perfect. It was designed for Internet deployment, not for academic rigor. There are scenarios where the abstraction breaks down. Cloud computing, container networking, and SDN (Software-Defined Networking) blur layer boundaries in ways the original model doesn't account for. Overlay networks like VXLAN add virtualization on top of the physical infrastructure, meaning your traffic traverses additional encapsulation that doesn't map cleanly to any single layer. IPv6 transition mechanisms like dual-stack, tunneling, and translation also create hybrid environments where traffic from one protocol family behaves differently than you'd expect. A dual-stack host sends both IPv4 and IPv6 packets simultaneously, and load balancers sometimes pick the wrong protocol version based on stale connection tracking. If you're working in modern data centers, you'll also encounter protocols that don't fit the model neatly. QUIC runs over UDP but provides reliability features that traditionally belonged to TCP. Service mesh proxies like Envoy implement sidecar patterns that intercept traffic at multiple layers simultaneously. These are engineering solutions to real problems, not flaws in the model, but they require you to think beyond the simple four-layer abstraction.
The TCP/IP model is still the best framework for understanding network communication. It's not the only framework, and it's not complete, but it covers the vast majority of what you'll encounter in production. Focus on understanding how the layers interact, learn to trace problems through them systematically, and you'll be able to diagnose most network issues without excessive tools.