How Assigned Risk for Technology Policies Actually Works in Practice
Assigned risk pools exist because standard commercial insurers walked away from certain technology liabilities around 2018 and never came back. When a business can't place coverage through the voluntary market, the assigned risk program forces a participating insurer to take a turn writing the policy. The mechanics are straightforward, but the execution has enough wrinkles that people who've done it a handful of times still get tripped up. A Technology Assigned Risk Company isn't a single entity. It's the pool mechanism through which state guaranty associations or assigned risk plans distribute technology-related policies among member insurers. The exact structure varies by state. Some states handle cyber and tech liability under a dedicated program. Others slot it into broader commercial lines assigned risk plans. You need to know which applies in your jurisdiction before you submit anything. The pool assigns policies on a rotational basis. If three carriers participate in your state's tech assigned risk program and ten applications come in, each carrier gets roughly a third of the volume over time. The first carrier to receive a policy might not see another assignment for weeks. That rotation schedule matters if you're brokering for clients on tight timelines.
I ran into a specific problem last fall with a mid-size software company in Texas that needed E&O and cyber coverage urgently. Their broker submitted through the wrong assigned risk plan because Texas routes technology risks through the California Pool rather than the state's general assigned risk facility. The application sat in limbo for eleven days. What I did was call the Texas Department of Insurance directly and got a confirmation that tech-specific policies should route through the California Pool's tech unit. They resubmitted on a Tuesday and got a binding number by Thursday afternoon. Never skip that validation call.
How to Place a Policy Through the Assigned Risk Route
Start by confirming the applicant qualifies. Assigned risk isn't a default option anyone can use because they didn't like the quotes they received. You typically need documented evidence that the business was rejected by at least two voluntary market carriers, or that no carrier in the state was willing to write the risk at any price. Some programs accept a single decline with explanation. Others require two. Check the specific program rules. Next, gather the standard application materials plus whatever the tech-specific supplements require. This usually means a detailed description of the technology services provided, client contract summaries, data handling practices, incident response procedures, and sublimit elections. The more completely you fill out the tech questionnaire, the faster the underwriter can bind. Incomplete tech supplements are the single biggest reason assignments get delayed past the stated turnaround window. When you submit, include the loss runs for the past five years. Even if the business has no claims history, include a zero-loss certification. Underwriters in assigned risk programs review everything. Leaving it out creates the impression you're hiding something. It takes thirty seconds to attach and saves two days of back-and-forth.
Get the Full Details
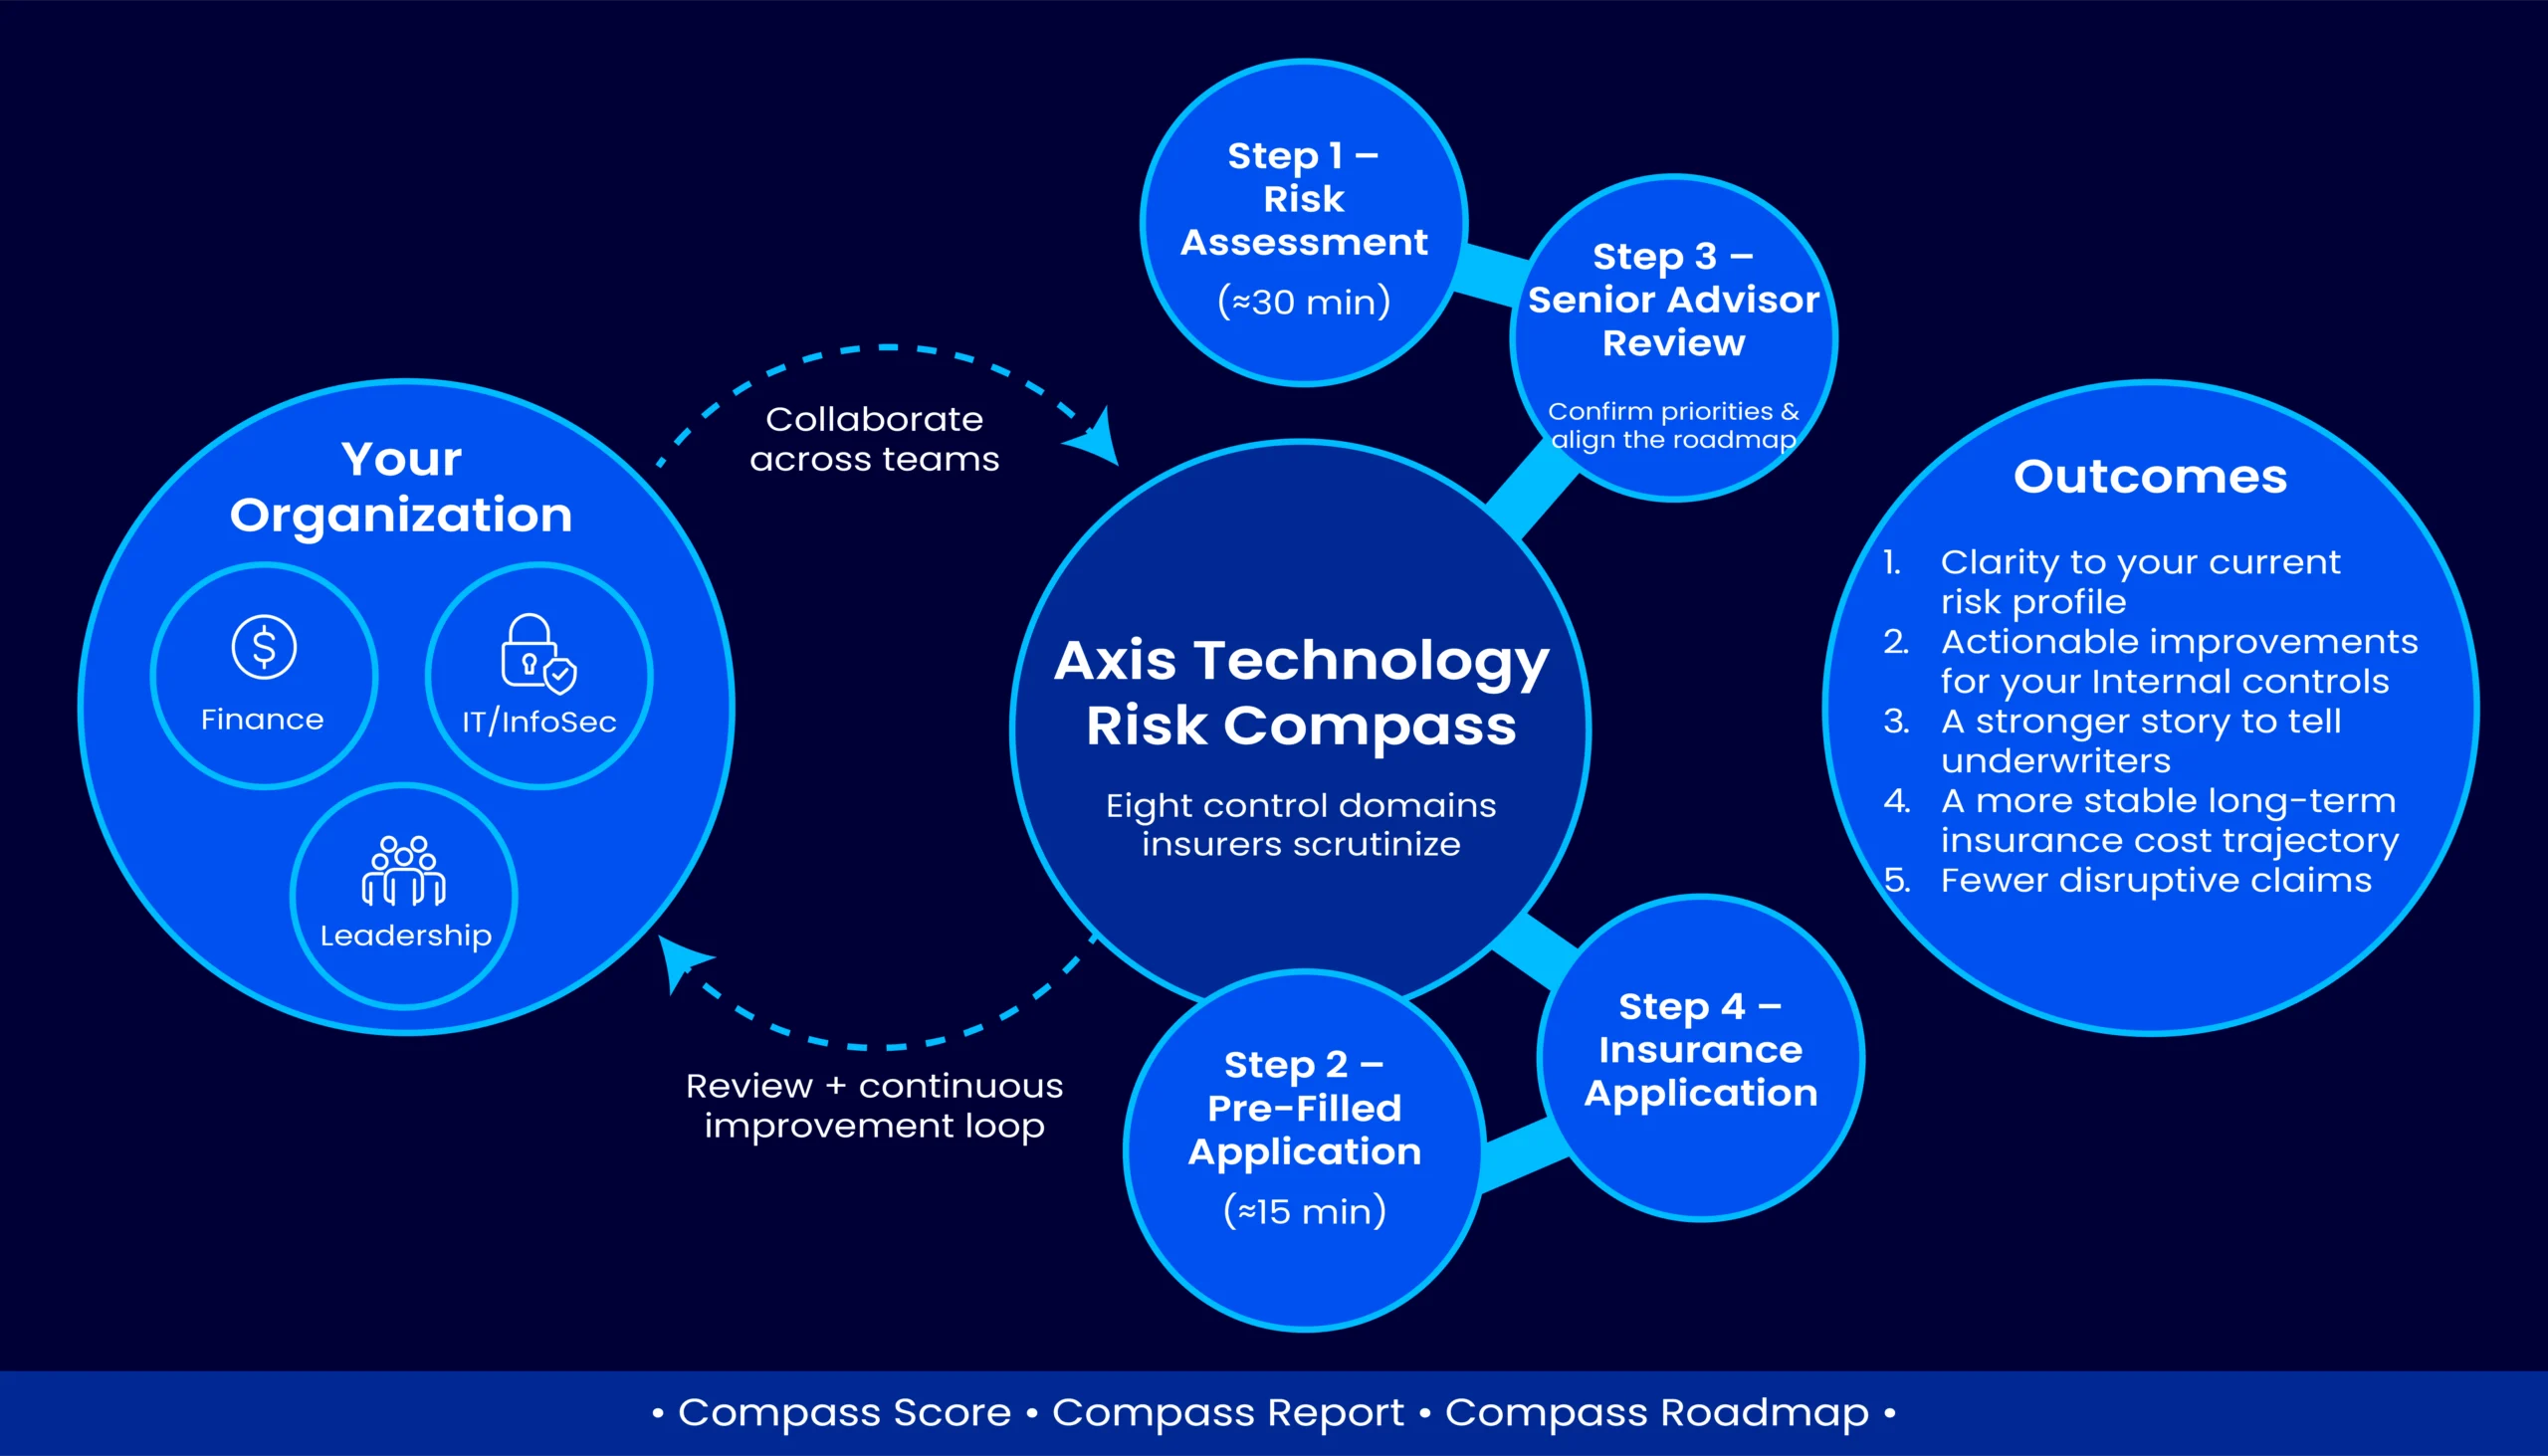
Expect the binding timeline to range from five to fourteen business days for standard tech liability. Cyber-heavy programs with enhanced security assessments can stretch to twenty days. If a client needs coverage sooner, ask about interim certificate options through the assigned risk carrier's contingent binder program. Not all pools offer this, but the ones that do can get a certificate issued within forty-eight hours while the full policy is underwritten.
Pitfalls That Break Assignments
The most common mistake is misclassifying the risk type. A company that writes custom software for healthcare clients triggers HIPAA-related cyber endorsements. If you mark them as a general technology E&O risk without the healthcare modifier, the underwriter either reassigns it internally or returns it for correction. Both outcomes add time. Screen for regulated industry clients before you start the application. Another issue I see regularly is the premium calculation disagreement. Assigned risk premiums are set by the pool's rating bureau, not negotiated. Brokers sometimes push back on the rate, but there's nothing to negotiate. The rate is the rate. What you can adjust is the limit structure, deductibles, and endorsement selections. Focus your conversation there instead of arguing about the base premium, which only wastes everyone's time. There's also a coverage gap that nobody warns you about. Assigned risk technology policies frequently exclude coverage for acts of war, nation-state cyber incidents, and sometimes even broad network outages caused by third-party infrastructure failures. If your client operates critical infrastructure or handles data for government contractors, this exclusion could be devastating. Request the full exclusion schedule before binding and flag any gaps that don't fit the client's risk profile.
I had a client in the financial technology space who didn't realize their assigned risk policy excluded regulatory fines and penalties. When the state AG launched an inquiry into their data handling practices, the claim was denied outright. We repositioned the coverage afterward through a voluntary market carrier willing to accept the risk at a higher premium, but the twelve-month gap in regulatory defense coverage was expensive to explain. Always verify what's excluded before you tell a client they're covered.

When Assigned Risk Isn't the Right Answer
If a business has clean loss history, strong revenue, and operates in a less regulated niche, pushing them through assigned risk is often the wrong move. Assigned risk premiums carry a loaded margin. They're typically fifteen to thirty percent above comparable voluntary market rates because the pool compensates participating carriers for writing higher-risk business. The policy terms are also more restrictive by design. Consider the alternative path first. Work with a wholesale broker who specializes in technology lines and has relationships with non-admitted or specialty carriers. Firms like AIG's technology practice, Chubb's cyber division, or Beazley's technology E&O program routinely write risks that assigned risk pools would also touch, but with broader coverage and more competitive pricing for well-underwritten accounts. Use assigned risk only when the voluntary market genuinely won't touch the account. Sometimes the voluntary market refusal is temporary rather than permanent. A carrier might have declined a submission during a hardening cycle, then opened that segment back up six months later. If your initial rejections came from carriers with stated concerns rather than blanket exclusions, revisit those same carriers after ninety days. Mention that you're exploring assigned risk as a backup. Carriers sometimes pull offers that were previously denied when they learn the account has alternatives.
Documentation to Keep on File
Maintain a complete paper trail for every assigned risk placement. This includes the two or more decline letters, the application submission confirmation, the carrier assignment notice, the policy wording with all endorsements, and correspondence about limit or deductible changes. Regulatory examiners and audit teams look for this documentation. If a client later alleges misrepresentation or inadequate coverage, your file should show exactly what was disclosed and what was bound. Some states require the assigned risk carrier to send a copy of the policy directly to the Department of Insurance. Verify this happens. A missing regulatory filing can create compliance issues for the insured, especially if they're required to maintain continuous coverage for licensing purposes. The process isn't fast and it isn't cheap, but for businesses that can't get placed elsewhere, it's the only reliable route to coverage. Get the classification right, submit complete documentation, and don't assume the assigned risk policy covers everything a standard tech liability policy would. The gaps are where the problems start.