How to Actually Implement a Technology Lifecycle Management Framework Without Losing Your Mind
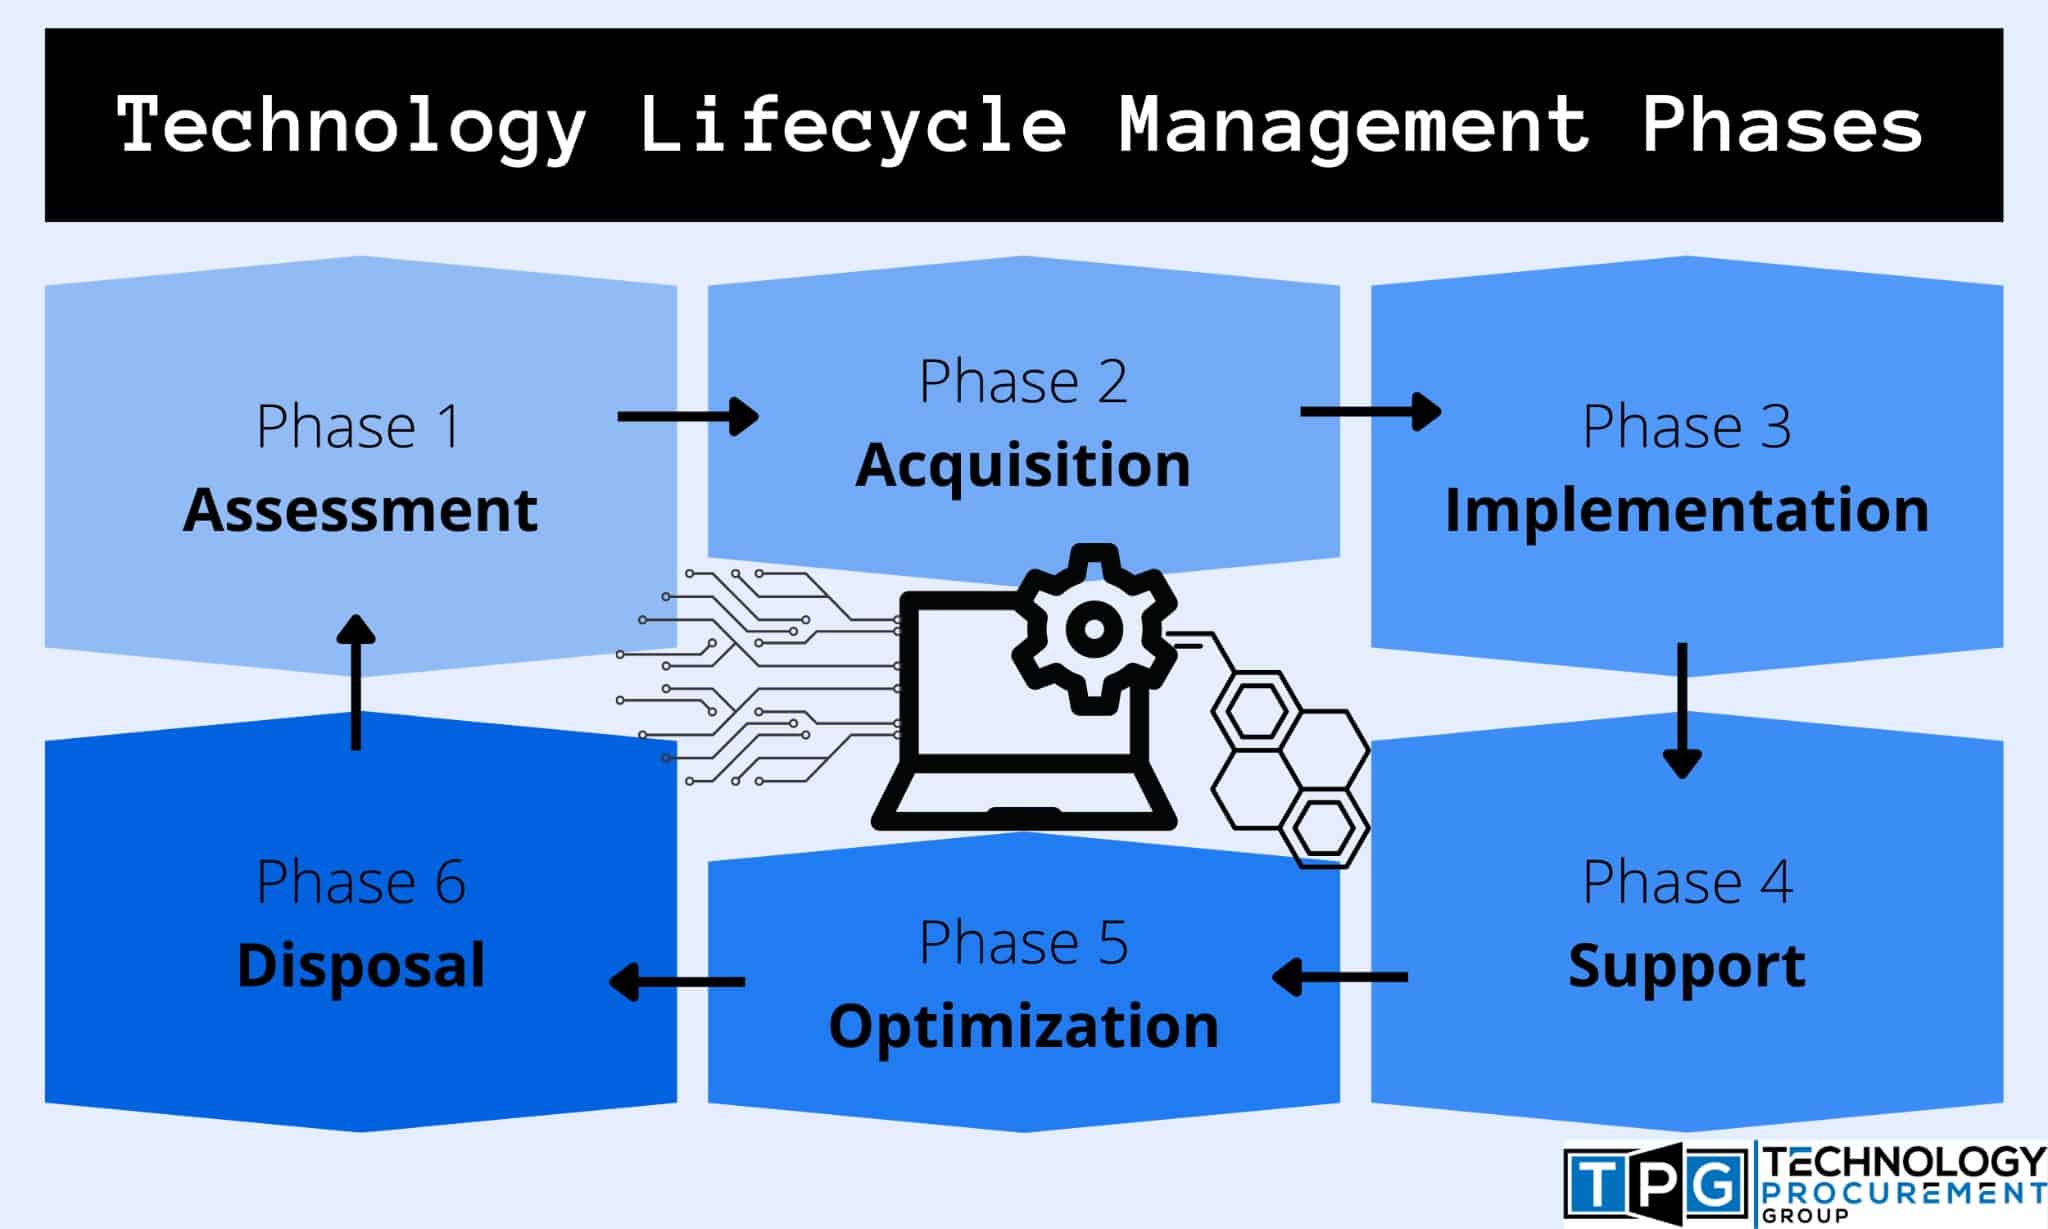
Most organizations try to manage technology lifecycle on spreadsheets. This fails because spreadsheets don't update themselves and half the data is two years stale. A Technology Lifecycle Management Framework is simply a structured approach to tracking every piece of technology you depend on—from initial procurement through active use to eventual retirement. The reason this matters is that unsupported software, end-of-life hardware, and orphaned licenses create real risk. Security gaps. Compliance failures. Surprise costs when a vendor drops support for something everyone still relies on. At its base, the framework tracks technology through six stages: procurement and acquisition, deployment and integration, operational use, maintenance and updates, retirement planning, and decommissioning. Each stage needs defined ownership, review triggers, and exit criteria. Without that, you're just maintaining a list with no actual governance behind it. The practical difficulty is that most IT departments already have competing priorities. Adding lifecycle tracking on top of existing operational work usually means either the framework becomes performative paperwork or it gets abandoned within six months. The way this actually works is by integrating lifecycle checkpoints into processes that already exist—change management, budget cycles, risk assessments. You don't create a separate workflow. You attach lifecycle considerations to workflows that are already happening.
Building the Foundation: Inventory and Classification
Before any framework delivers value, you need accurate inventory data. This sounds obvious and it's also where everything typically breaks down. I've seen organizations attempt a full lifecycle audit only to discover that 40 to 60 percent of their active assets had no owner, no purchase record, or a documented location that was wrong. Start by pulling data from your CMDB, asset management tools, and network discovery scans. Cross-reference vendor support databases to identify end-of-life and end-of-support dates. Then classify everything by three factors: support status, security criticality, and business dependency. A deprecated library used by one internal tool is a completely different risk than a deprecated encryption module used across twelve products. Once you have the baseline, you need a review cadence. Quarterly reviews for critical infrastructure. Annual reviews for standard operational technology. Event-driven reviews when new vulnerabilities are disclosed or when business requirements shift significantly. The cadence determines whether your framework stays relevant or becomes another document nobody reads.
Implementation in Practice: What I Actually Did
Last year I worked with a mid-size organization trying to implement this framework across their engineering and infrastructure teams. The problem wasn't the concept. It was that their procurement process and their operations process existed in completely separate systems with no shared identifiers. An asset had one ticket number in procurement, a different serial in the asset tracker, and yet another configuration ID in their monitoring platform. Mapping those together took three weeks of manual reconciliation before any actual lifecycle analysis could begin. The workaround was to establish a single internal asset identifier at the point of procurement entry. Every subsequent system—CMDB, license management, monitoring, security tools—had to reference that identifier. We wrote a lightweight middleware layer that normalized the data between systems. This cut the reconciliation time from weeks to roughly an hour for future additions. It didn't fix the historical data, but it prevented the problem from recurring. The retirement planning piece was where things got uncomfortable. Identifying what to decommission requires cross-functional agreement between security, operations, finance, and the business units that depend on the technology. Security wants to retire everything that's unsupported. Operations wants to keep running the old version because the migration carries risk. Finance wants to write off the remaining depreciation. The framework needs a clear escalation path when these groups disagree, otherwise decisions stall indefinitely.
Get the Full Details
Common Pitfalls and What Beginners Miss
Most people approaching this framework think the hard part is tracking active technology. It's not. The hard part is managing the transition period between stages. A system that's been flagged for retirement but not actually retired creates more risk than a system that's simply out of support. The retired system might still be running somewhere, still connected to a network, still receiving data feeds. I once found a production database still querying a server that had been formally decommissioned eighteen months earlier. The decommission documentation was complete. The actual machine never got turned off. Another counter-intuitive point: the lifecycle framework is not primarily a technical exercise. It's a governance and communication tool. The best implementation I've seen spent roughly sixty percent of its effort on stakeholder alignment and process integration and maybe forty percent on the actual technical tracking. You can have perfect inventory data and still fail if the people making purchasing decisions don't know about the lifecycle framework or don't believe it applies to their choices. Support status is another area where the data can be misleading. Vendor websites list end-of-life dates for products, but they rarely publish end-of-extension or extended-support pricing. A product might technically be in "standard support" but the extended support contract costs three times the original license fee. This changes the retirement calculation significantly. Build cost-per-year-of-support into your classification model rather than treating all support equally.
Limitations and When This Framework Won't Work
The framework has real bottlenecks. Initial data gathering is expensive and time-consuming. For organizations with more than five hundred distinct technology assets, a complete baseline inventory typically requires two to four months of dedicated effort from at least one full-time equivalent. During that window, you're making lifecycle decisions with incomplete data, which introduces risk. The framework also depends on consistent data entry at the point of procurement. If purchasing happens outside formal channels or through vendors who don't provide structured documentation, the framework loses accuracy from the start. I've seen this in organizations where individual teams used corporate cards to buy cloud services and software licenses without routing through procurement. Those assets were invisible to the lifecycle system for years. For smaller organizations with limited IT staff and under two hundred assets, a full Technology Lifecycle Management Framework may consume more resources than it saves. In those cases, a simplified risk-based audit approach—reviewing only critical and high-security assets quarterly while maintaining a basic inventory of everything else—often delivers comparable risk reduction at a fraction of the effort.
The framework works best when integrated into existing governance structures rather than operating as a standalone initiative. If your organization already has ITIL processes, enterprise risk management, or compliance frameworks in place, lifecycle tracking should feed into those rather than compete with them. When it's treated as an additional requirement on top of existing work, it tends to get deprioritized whenever things get busy.

A Practical Starting Point
If you're beginning this work, don't try to cover everything at once. Pick your top twenty most critical systems and run a complete lifecycle analysis on those. Document procurement date, vendor support status, current security posture, business dependency mapping, and recommended retirement timeline for each one. Use that as a proof of concept and a template for expanding to the rest of your environment. This approach lets you identify structural problems in your data and processes before you invest heavily in scaling the framework. It also gives you concrete results to show stakeholders, which makes securing ongoing resources considerably easier than presenting a theoretical implementation plan.