What Actually Happens When You Try to Implement This
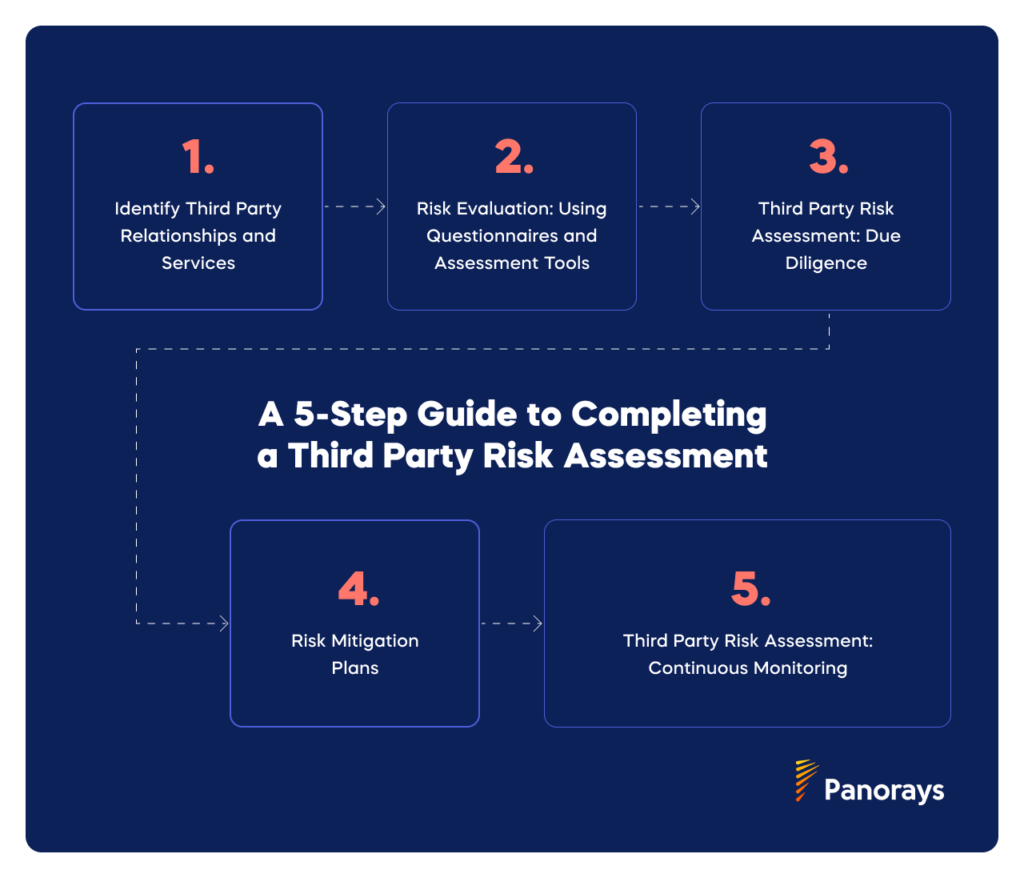
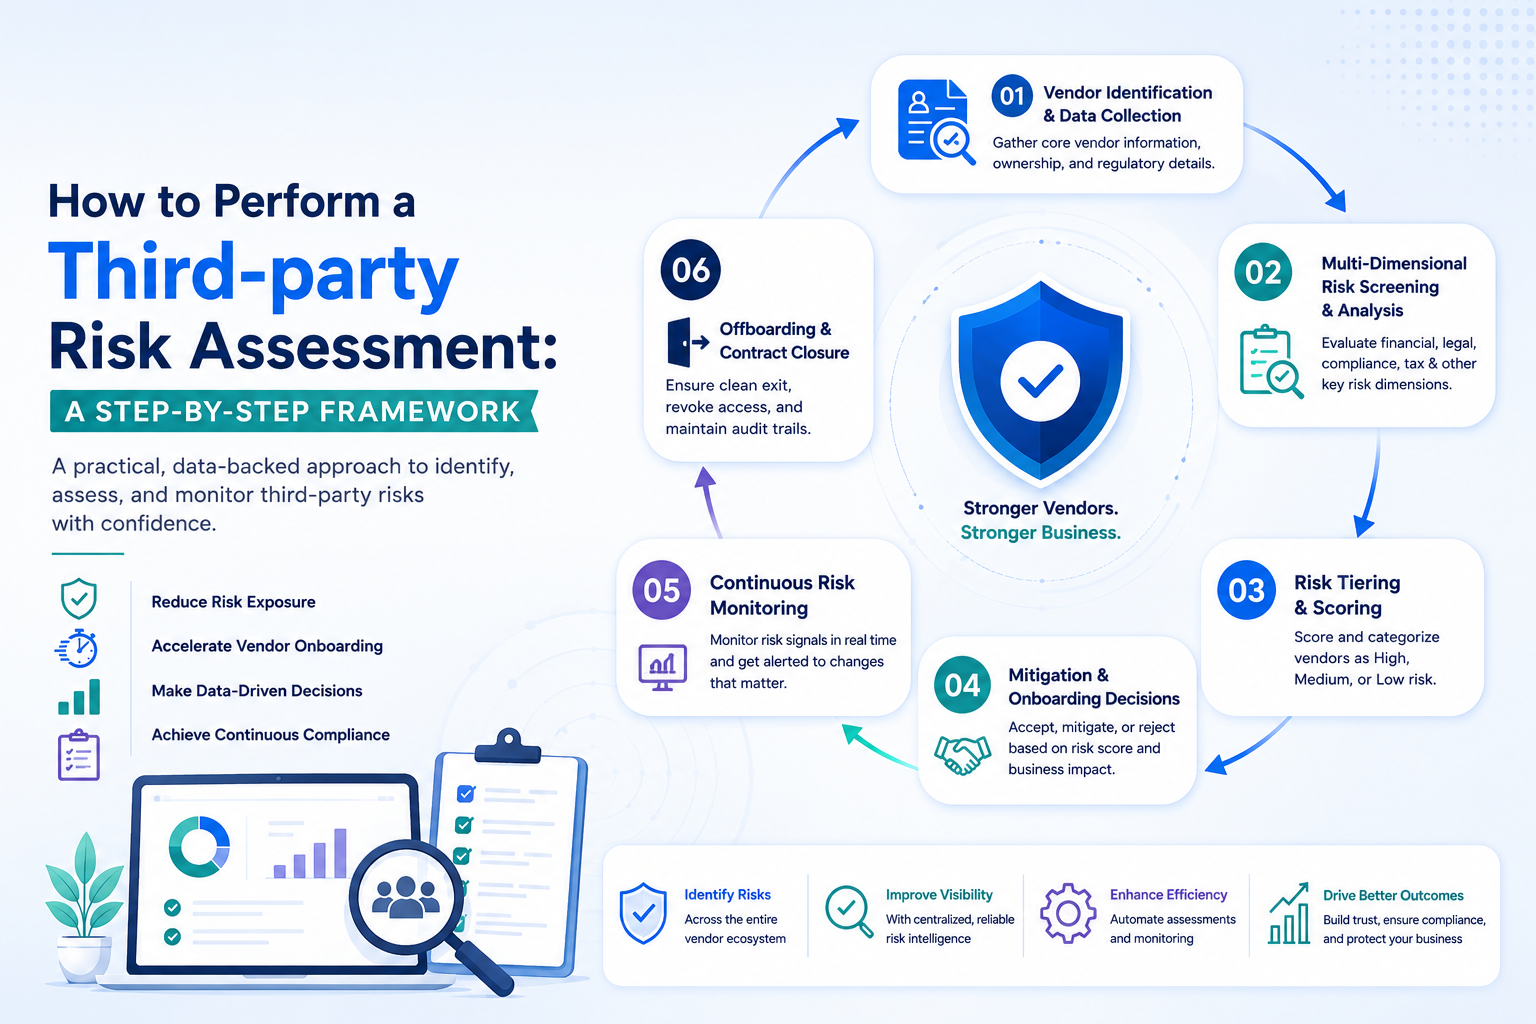
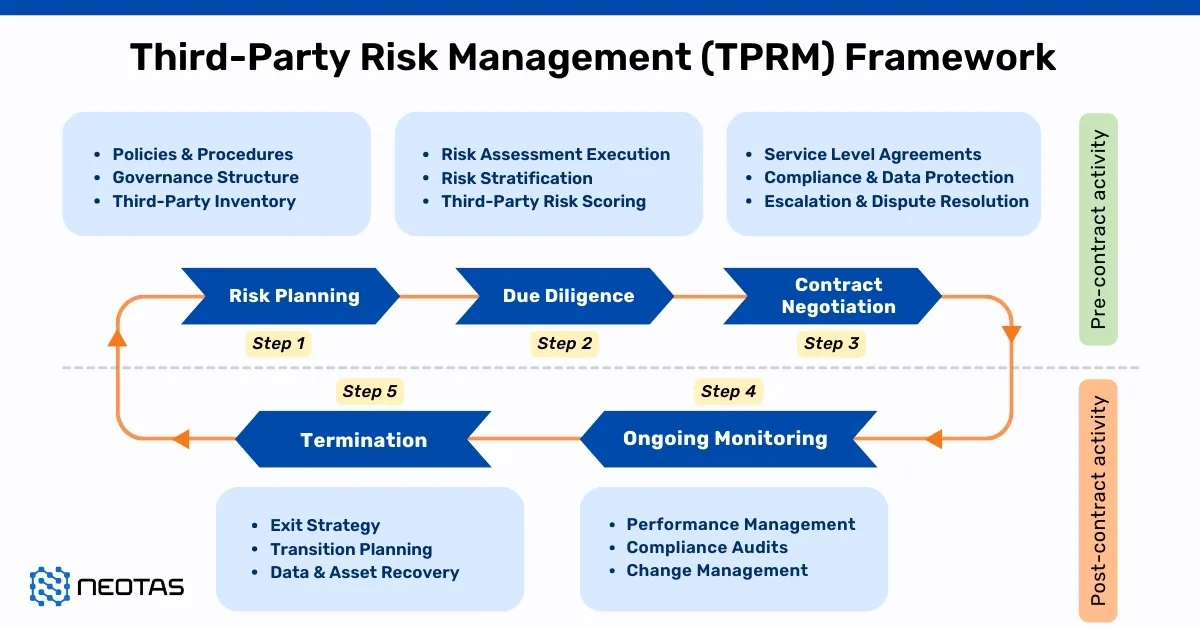
You spend weeks building out a Third Party Risk Assessment Policy. You get it signed off by compliance, you distribute it to the procurement team, and then you watch it collect digital dust while vendors keep shipping overpriced SaaS contracts through the back door. I have seen this repeatedly. The gap between the policy document and the actual workflow is where everything falls apart. A Third Party Risk Assessment Policy is not a single questionnaire or a security checklist. It is the governing document that defines how your organization identifies, evaluates, and monitors risk across the vendor lifecycle. The policy itself sets the rules. The procedures implement them. The tools execute them. Most people conflate the three. The standard framework breaks down into four phases. Triage determines whether a vendor relationship even requires a full review. Due diligence happens during onboarding for any engagement that crosses your risk threshold. Continuous monitoring runs after the contract is signed. Offboarding closes the loop when the relationship ends. The problem is that triage is almost always underfunded and rushed. If you send a medium-risk cloud vendor through a simplified workflow instead of a full assessment, you save about three to four business days per engagement. That seems reasonable until you realize that medium-risk is where most breaches originate.
My actual workflow looks like this. I start with a classification matrix based on data sensitivity, access level, and operational criticality. Every new vendor request gets tagged against those three axes before anyone opens a security questionnaire. I learned to do this after spending six months manually reviewing every single vendor intake form regardless of relevance. It took roughly two weeks per month in team bandwidth. Now it takes about two hours because 80 percent of requests are auto-flagged as low risk and routed to a condensed self-assessment. There is a counter-intuitive finding from working on these assessments repeatedly. The quality of a vendor security review is not determined by how many questions you ask. It is determined by which questions you refuse to ask. I once worked through a thorough Third Party Risk Assessment Policy that included over 200 questions across six domains. We received back an average completion time of eleven business days. The average response quality was poor. Vendors would either rubber-stamp answers or paste generic marketing copy into fields that required technical specifics. We cut the questionnaire down to thirty-two questions focused on access controls, incident response, data handling, encryption, business continuity, and audit transparency. Completion time dropped to two business days. Response accuracy increased measurably because we were asking the right questions instead of maximum questions.
What Most People Get Wrong About Execution
The biggest mistake I see is treating risk assessment as a one-time gate check. Vendors change. Their security posture changes. Their financial health changes. A SOC 2 report from last October is not evidence that your cloud provider is secure today. It is evidence that they met certain standards at a point in time. Point-in-time assessments create false confidence. I have watched teams approve vendors based on stale certifications and then spend three weeks containing an incident that the current audit report would have flagged immediately. Another thing that rarely gets discussed is the problem of sub-processors. You assess the primary vendor. You do not assess the primary vendor's primary vendor. This is where supply chain risk accumulates without anyone noticing. A mid-size SaaS company you trust completely might rely on a smaller logging provider with no security team and default passwords in their staging environment. The risk migrates downward until it hits an organization with zero formal controls. Your policy should require vendors to disclose their critical sub-processors and submit their own risk assessments for any sub-processor handling your data. I encountered a specific edge case that changed how I think about this entire process. We were evaluating a new identity provider for employee SSO. The vendor had a perfect SOC 2 Type II, clear encryption policies, and strong references. Everything looked clean on paper. During the risk assessment, I noticed their disaster recovery plan referenced a primary data center in Virginia and a secondary site in Oregon. Standard setup. Then I checked their actual disaster recovery test schedule and found they had not performed a full failover test in fourteen months. The policy said monthly. The evidence said quarterly at best. I asked for the most recent test report. They sent a summary that showed successful failover. I requested the raw logs. They could not produce them because the testing was conducted through a third-party firm and the logs were retained for only ninety days. The vendor's own security policy had a retention requirement of one year. They were already in violation of their stated policy.
Get the Full Details
I made the engagement conditional on them implementing a verifiable log retention process and passing an independent DR test before access was provisioned. They negotiated for six weeks. We ultimately accepted their commitment letter with quarterly monitoring checkpoints. The assessment took longer than it should have. The contract would have gone through without that detail if we had only reviewed documentation on its face. This is exactly the kind of gap that a thorough Third Party Risk Assessment Policy is designed to catch, but only if someone actually checks the evidence and not just the claims.
Practical Steps to Build Something That Actually Works
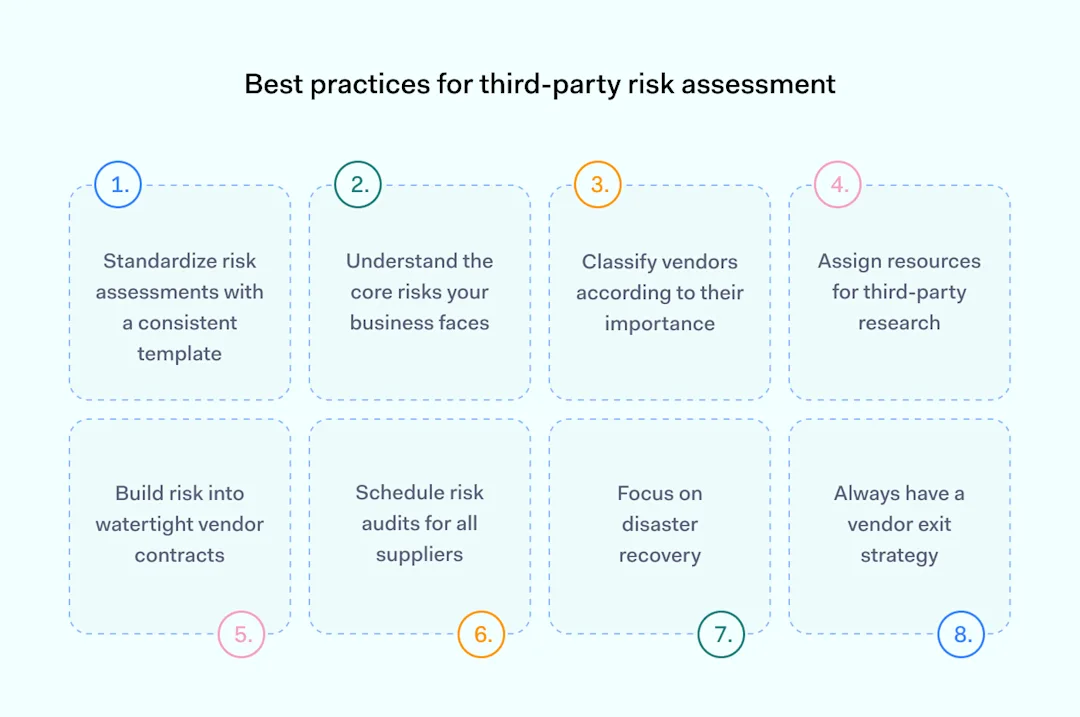
Start by defining your risk tiers. I use three levels. Low-risk vendors are those with no data access and no system integration. A newsletter provider or a software license reseller. They get a basic self-assessment. Medium-risk vendors handle non-sensitive data or have limited API access. They receive the full questionnaire plus a review of one current security attestation. High-risk vendors have direct access to production systems or PII. They get the full questionnaire, the attestation review, and a formal risk acceptance document signed by a designated authority within your organization. Use a standardized questionnaire framework. I recommend starting with the Information Security Forum standard questions or the CAIQ from the Cloud Security Alliance. Do not build your own from scratch unless you have a dedicated security team with available bandwidth. Custom questionnaires take about eighty hours to design and validate properly. Standardized ones are free and battle-tested. Fill in the gaps with five to ten questions specific to your industry requirements. Healthcare needs HIPAA-specific items. Finance needs GLBA and FFIEC considerations. Everything else can operate on the base framework. Build a monitoring schedule that matches your risk tier. Low-risk vendors get reviewed annually or upon material change. Medium-risk vendors get quarterly check-ins with updated attestations. High-risk vendors get monthly monitoring with continuous alert integration where possible. I integrate vendor risk scores into a simple dashboard rather than relying on spreadsheet trackers. Spreadsheets fail at scale. Once you pass about forty active vendor relationships, manual tracking becomes unreliable. The dashboard approach cuts review coordination time from roughly six hours per month down to about forty-five minutes.
Require contractual clauses that enforce your policy. This is the part most organizations skip. Your Third Party Risk Assessment Policy means nothing if the contract does not reference it. Include clauses that grant you audit rights, require notification of security incidents within seventy-two hours, mandate sub-processor disclosure, and allow termination for material security degradation. These clauses exist in your templates but are routinely negotiated away by procurement teams focused on closing deals fast. I have renegotiated removed clauses in about twelve percent of high-risk vendor contracts after the initial signing. That is twelve percent of engagements where you thought you had protection and did not.
When This Approach Breaks Down
Third party risk assessment does not work when your organization treats it as a compliance checkbox exercise. If the goal is merely to complete assessments on time rather than to genuinely understand the risk landscape, you will produce high completion rates with low actual risk visibility. I have seen teams hit ninety-five percent assessment completion while missing active credentials exposed in a vendor's public GitHub repository because nobody actually looked beyond the questionnaire responses. The approach also breaks down when legal and procurement operate in separate workflows from security. If procurement is scoring vendors on cost and delivery timeline while security scores them on risk, the two scores rarely align. The lowest-cost vendor often carries the highest unassessed risk. I recommend tying vendor approval to a unified scorecard that weights security risk at no less than thirty percent of the total evaluation. This changes procurement behavior noticeably within two or three quarters. There is also the problem of assessment fatigue. If every vendor relationship requires the same level of scrutiny, the process becomes unsustainable. I cap the total annual assessment workload at a level that allows each reviewer to handle approximately twenty-five full assessments per year with adequate depth. Beyond that threshold, quality degrades measurably and cycle times stretch to eight or nine weeks. When you hit that volume, you either increase reviewer capacity or you raise your risk tier thresholds to reduce the number of full assessments required. Both options require leadership visibility into the numbers.
If your organization has fewer than fifty vendors and does not handle regulated data, a full formalized policy may be overkill. A simplified risk register with quarterly reviews and a basic questionnaire gets you most of the benefit with a fraction of the overhead. The framework scales either direction. The question is whether the overhead matches the actual exposure.