What KPMG Actually Offers for Third Party Risk
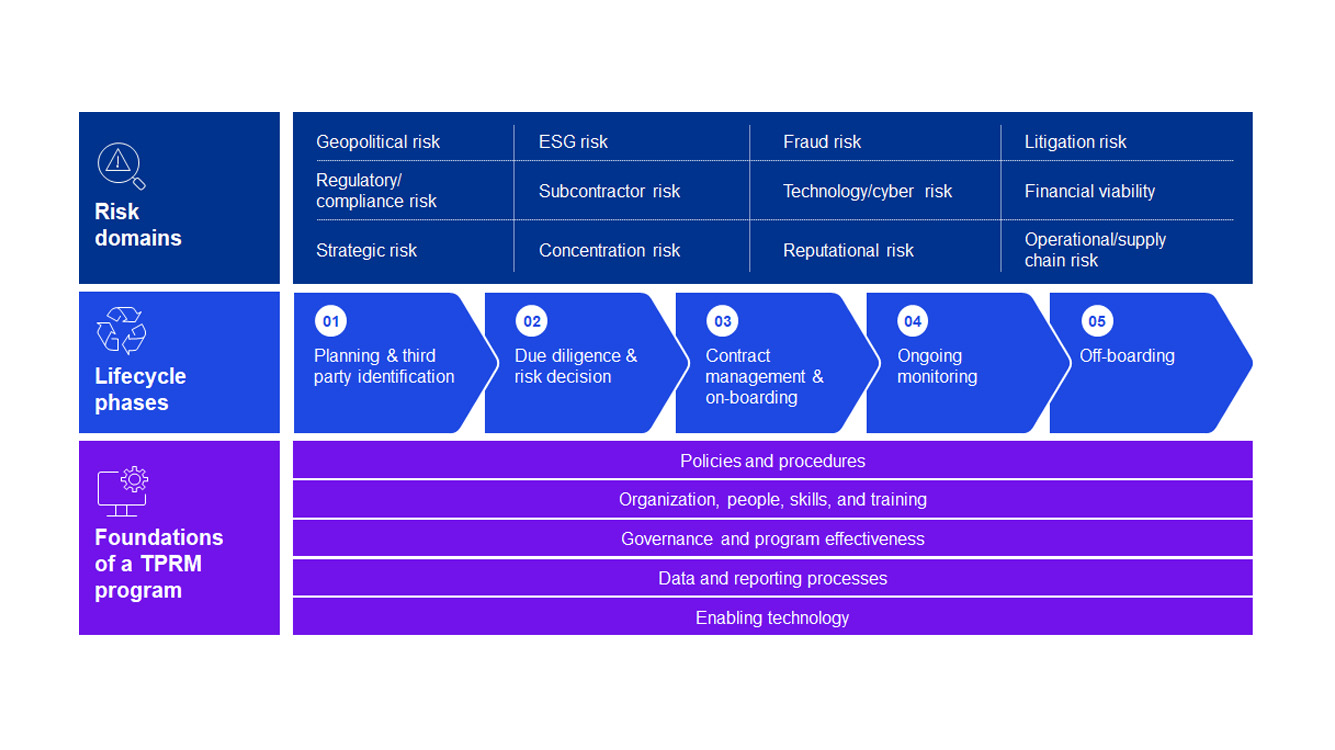
KPMG's Third Party Risk Management practice is essentially a blend of consulting framework design, technology enablement through tools like KPMG Clara, and ongoing managed services. It is not a single downloadable product you install and run on your own. You engage with their people, their methodology, and in many cases their platform. That distinction matters because people coming in expecting a free tool or a self-serve portal usually end up frustrated. The core deliverable is a risk management program built around the KPMG TRM framework. This covers vendor onboarding assessments, continuous monitoring, risk scoring models, and regulatory alignment — particularly around regulations like DORA in Europe, NYDFS 500 for New York financial services, and OCC guidance for US banks. If you are a regulated entity, that mapping is where most of the value sits initially. For non-regulated companies, it can feel like overkill until you actually face a contract dispute or an audit finding.
Getting Started with Third Party Risk Management Kpmg
Engagement typically begins with a scoping assessment. KPMG will want to understand your vendor ecosystem, your current state of compliance, your regulatory obligations, and what pain points are keeping your risk or procurement team up at night. From there they propose a roadmap. The timeline ranges wildly depending on scope. A focused regulatory alignment project for a mid-size bank might take six to nine months. A full end-to-end transformation including platform implementation and program redesign can stretch to eighteen to twenty-four months and easily cost several million dollars. The process generally follows these phases. First is discovery and gap analysis, where they map your current vendor inventory and assess maturity against recognized standards like ISO 27036 or the FTC Safeguards Rule. Second is framework design, which includes risk scoring methodologies, tiered assessment questionnaires, and approval workflows. Third is technology enablement, often involving KPMG Clara's risk modules or integration with existing GRC platforms. Fourth is operating model transition, where they help embed the new processes into your day-to-day operations and sometimes provide managed services to run them for a period. Fifth is continuous improvement and regulatory tracking. I worked through a KPMG TRM engagement about three years ago for a regional credit union. We had failed an exam because our third party risk program was effectively a spreadsheet in someone's inbox. KPMG came in, redesigned the program, and implemented Clara. The first three months were brutal. Our vendor inventory was a mess — roughly four thousand contracts with incomplete records, missing owners, and zero risk scoring. Cleaning that data alone took longer than the framework design. I learned pretty quickly that the platform is only as good as the data you feed it, and most organizations do not realize how broken their vendor master data is until they try to run a real assessment through a proper system.
One thing nobody warns you about is the assessment fatigue problem. When KPMG sets up continuous monitoring and automated questionnaires, your vendors start getting buried. Within six months of launch, our top two hundred vendors had received an average of eleven different assessment requests. Several of them stopped responding. We had to negotiate a single consolidated questionnaire framework and limit reassessments to high-risk vendors only. That alone cut assessment volume by about sixty percent and actually improved response rates from forty-two percent back up to seventy-eight percent. KPMG supported this, but it was our team that had to have the uncomfortable conversations with procurement and the vendor relationship managers. The risk scoring model is another area where theory and reality diverge significantly. KPMG will build a quantitative scoring model based on factors like criticality, data sensitivity, regulatory exposure, and financial stability. On paper it is elegant. In practice, you will find that eight out of ten vendors end up in the same risk band because the differentiators are too subtle. I pushed back on this during our engagement and we adjusted the model to include actual contractual controls and security posture evidence rather than relying mostly on questionnaire responses. The discriminative power improved noticeably after that change. There are real limitations to be aware of. The cost structure is steep. Annual managed services running a full TRM program through KPMG typically runs well into six figures, often much more depending on vendor count and regulatory complexity. The platform itself, if you go the Clara route, requires significant licensing fees on top of implementation costs. Turnover is another issue — KPMG rotates staff on engagements, and when your lead consultant moves to a different project, you lose institutional knowledge about your specific vendor ecosystem and internal politics. I have seen multiple engagements where the handoff between consultants caused six to eight weeks of productivity loss.
Get the Full Details
Another limitation is that KPMG's approach is heavily influenced by the regulatory environment of large financial institutions. If you are a smaller company or operate in a less regulated industry, some of the framework elements feel inherited rather than adapted. We had to push back hard on several controls that made sense for a global systemically important bank but were disproportionate for our thirty-million-asset credit union. The final program worked better because we stripped out the irrelevant pieces, but that required us to have strong internal judgment rather than deferring entirely to the consultant. If you are considering this path, the practical advice is straightforward. Get clear on what regulatory drivers actually apply to you before you sign anything. Do not let scope creep into areas you do not need. Insist on data quality remediation as a separate phase with its own budget and timeline — do not assume it will happen organically. And negotiate terms that protect you against consultant turnover, including knowledge transfer requirements and documentation standards. The engagement should leave you with a program your team can run independently, not one that requires KPMG on retainer forever. The bottom line is that KPMG's Third Party Risk Management offering is legitimate and thorough, but it is expensive and it works best when you have the internal capacity to push back on scope and tailor the framework to your actual risk profile rather than accepting a one-size-fits-all template. The tooling is solid. The methodology is sound. The execution is where most programs either succeed or fail, and that depends almost entirely on how prepared your organization is to do the unglamorous work of data cleanup, vendor communication, and internal change management.