Third Party Risk Management That Actually Works
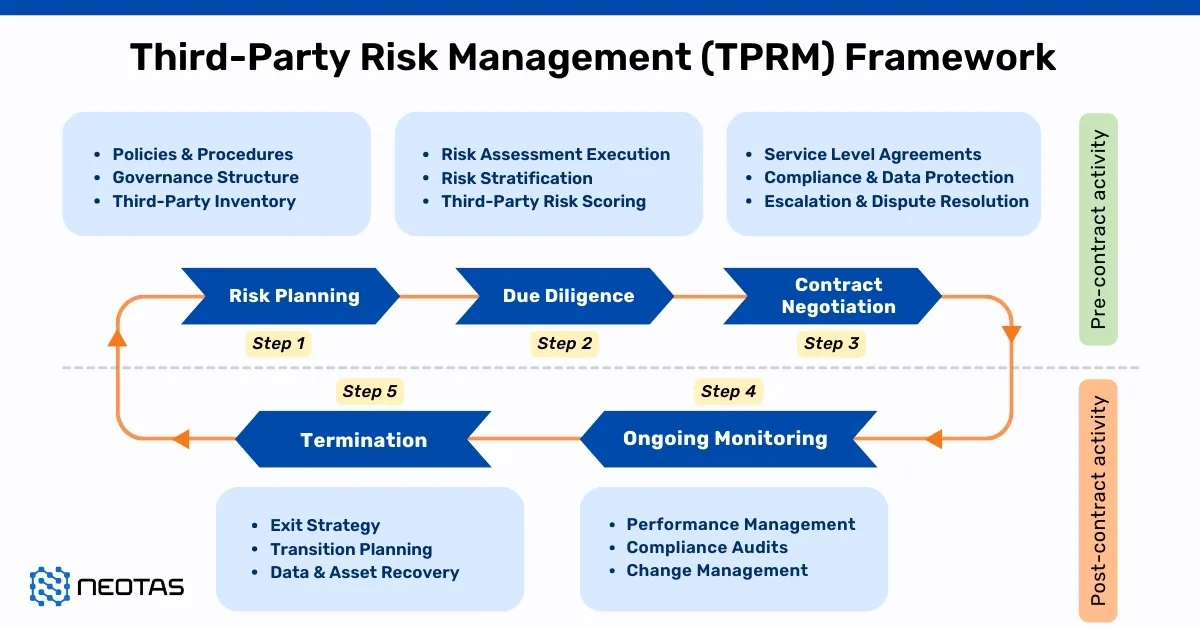
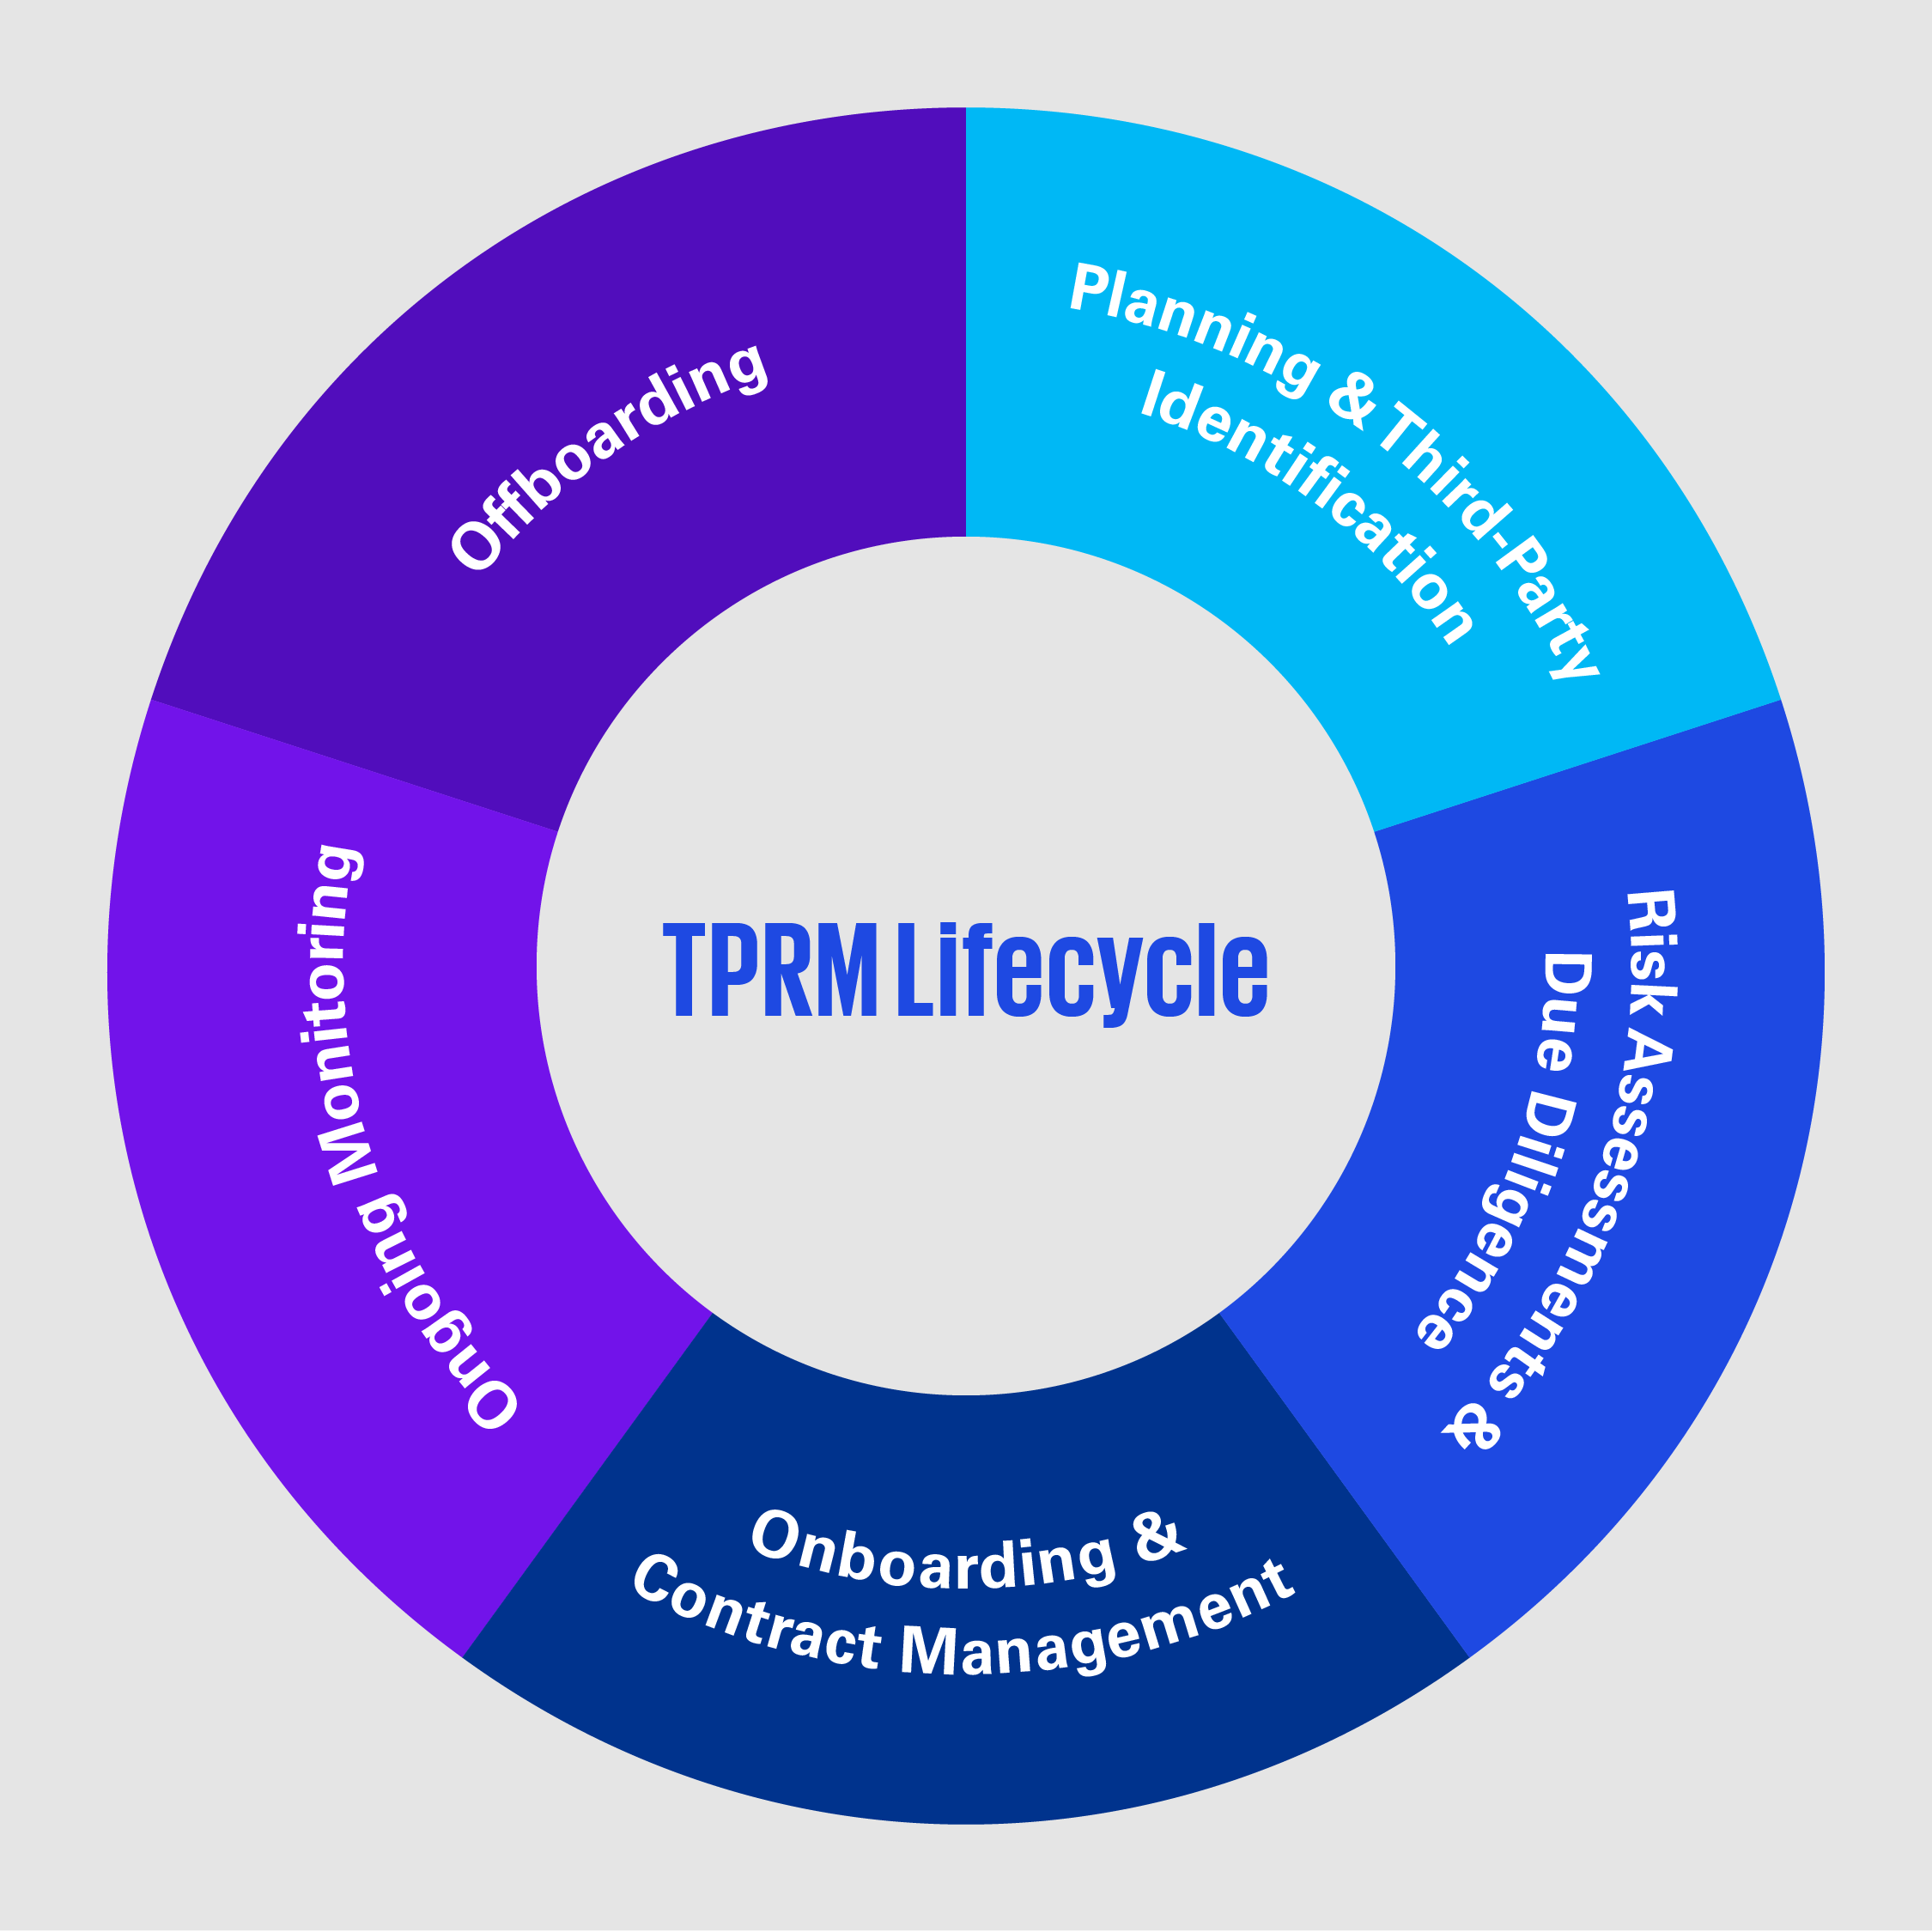
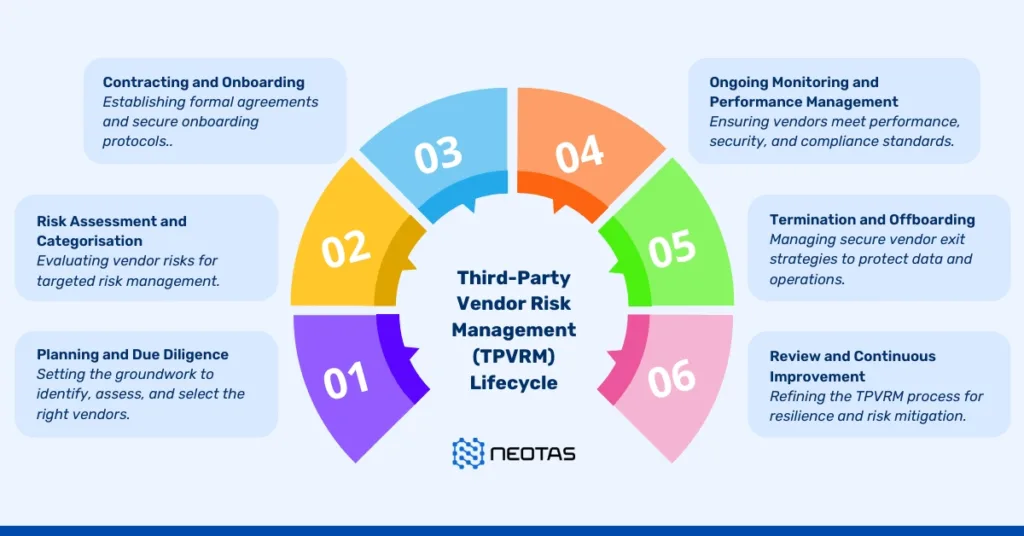
Most organizations treat Third Party Risk Management Tprm as a checkbox exercise. You send out a CAIQ questionnaire, get a 250-page SOC 2 report, stamp it approved, and then forget about it until the annual renewal date. That approach leaves you exposed to supply chain attacks, compliance failures, and operational disruptions that you won't understand until something breaks. I learned this the hard way after spending three months tracing a data flow issue back to a sub-subcontractor we had never actually assessed. The fundamentals are straightforward enough, but the execution is where people struggle. You need to identify every vendor relationship your organization has, categorize them by risk level, assess each one appropriately for their tier, and then continuously monitor them throughout the contract lifecycle. The problem is that most companies have thousands of vendor relationships and very few people to manage them. A mid-size enterprise typically touches 500 to 2,000 third parties at any given time, and maybe six to ten people on the risk team are responsible for all of them.
Building a TPRM Program from Scratch
Start with vendor discovery. You would think this is simple but it is not. Finance has one list of approved vendors. Legal has another for contracts. Procurement has a third. IT has software instances scattered across departments that nobody tracks centrally. Your first task is consolidating these into a single registry with standardized fields: vendor name, category, data classification, contract value, renewal date, and criticality score. Without this foundation everything else is guesswork. Next you need a risk tiering model. Not every vendor handling office supplies poses the same risk as one processing protected health information or managing your cloud infrastructure. I use a four-tier system based on two axes: what data the vendor can access and how critical the service is to operations. Tier 1 vendors have access to sensitive or regulated data and their failure would cause material business disruption. Tier 2 vendors handle non-sensitive data but provide critical services. Tier 3 vendors handle non-sensitive data with non-critical services. Tier 4 are everything else. This tiering determines the depth and frequency of your assessments. For Tier 1 vendors you need full security assessments including questionnaires, evidence requests, and ideally third-party audit reports. Tier 2 gets a lighter questionnaire with annual review. Tier 3 gets a basic screening. Tier 4 you might just verify they have a valid insurance policy and move on. The key is being ruthless about applying the tier consistently. I have seen teams give Tier 1 treatment to a vendor because the relationship manager felt guilty about pushing back on a long-standing supplier. That guilt becomes your risk.
Here is something most guides do not tell you: the biggest vulnerability in Third Party Risk Management Tprm is usually not your direct vendors. It is their subcontractors. When I ran into that data flow problem I mentioned, the initial assessment of our cloud provider looked clean. The SOC 2 report was solid. The security questionnaire responses were adequate. But when I traced where our data actually lived within their infrastructure, it turned out a sub-subcontractor in a different country was processing authentication data and they operated under a completely different compliance framework. Our original vendor had mentioned this in a footnote of their security documentation that nobody had read carefully. The workaround I implemented was requiring all Tier 1 vendors to disclose their entire subcontractor chain during onboarding and then assessing each one that touches our data. It added about two weeks to the onboarding process but it caught issues that a surface-level review would have missed entirely. Continuous monitoring matters more than annual assessments. A SOC 2 report tells you about a point in time, usually three to six months in the past by the time you receive it. Threats evolve constantly. I recommend pulling vendor security ratings from a service like BitSights or SecurityScorecard if your budget allows, setting up alerts for vendor security incidents through RSS feeds or their breach notification pages, and requiring vendors to notify you within 48 hours of any security event affecting your data. The 48-hour requirement should be in your contract. If it is not there now, add it as a contract amendment before your next renewal window. There are real limitations to this approach that deserve honesty. The questionnaire-driven model produces enormous volume of information that is largely unstructured and difficult to compare across vendors. A vendor can answer every question truthfully and still have a weak security posture because they misunderstand what the question means. The CAIQ controls are often too generic to capture your specific regulatory environment. You will also find that mature vendors complete assessments quickly while smaller vendors may need three to five rounds of follow-up just to provide adequate responses, which creates bottlenecks in procurement.
Get the Full Details

Some of the common pitfalls I see repeatedly include treating risk assessments as a one-way information gathering exercise instead of a collaborative process, which makes vendors less willing to be transparent. Another is failing to update assessments when vendor circumstances change, like a merger or acquisition, a new cloud provider, or a change in their data processing practices. These changes should trigger reassessment regardless of where you are in your cycle. A third pitfall is assuming that a vendor's certifications equal security. Having ISO 27001 or SOC 2 Type II certification does not mean they are secure today. It means they had controls in place during their last audit period. I once had a vendor maintain both certifications while their actual security team had been reduced by half and their incident response capability was essentially nonexistent. The certificates were still valid because they had not been audited yet. For smaller organizations without the resources for a full dedicated TPRM function, the practical alternative is to focus heavily on tiering and only apply deep assessment to your top twenty vendors by risk. The remaining vendors get a streamlined process. This is not ideal but it is realistic. Spending resources assessing a vendor that processes your catering invoices the same way you assess your core SaaS platform is a misallocation. Identify your critical dependencies first and work outward. The tools available range from specialized platforms like OneTrust, Prevalent, and SecuriVault to spreadsheet-based systems that are better than nothing. A properly configured GRC platform with automated questionnaire distribution and scoring can reduce assessment turnaround from weeks to days. But these platforms are expensive and complex to implement. A spreadsheet with consistent categorization fields and a shared review process can be effective for organizations under 200 vendors. The tool matters less than the discipline of actually following your process consistently.
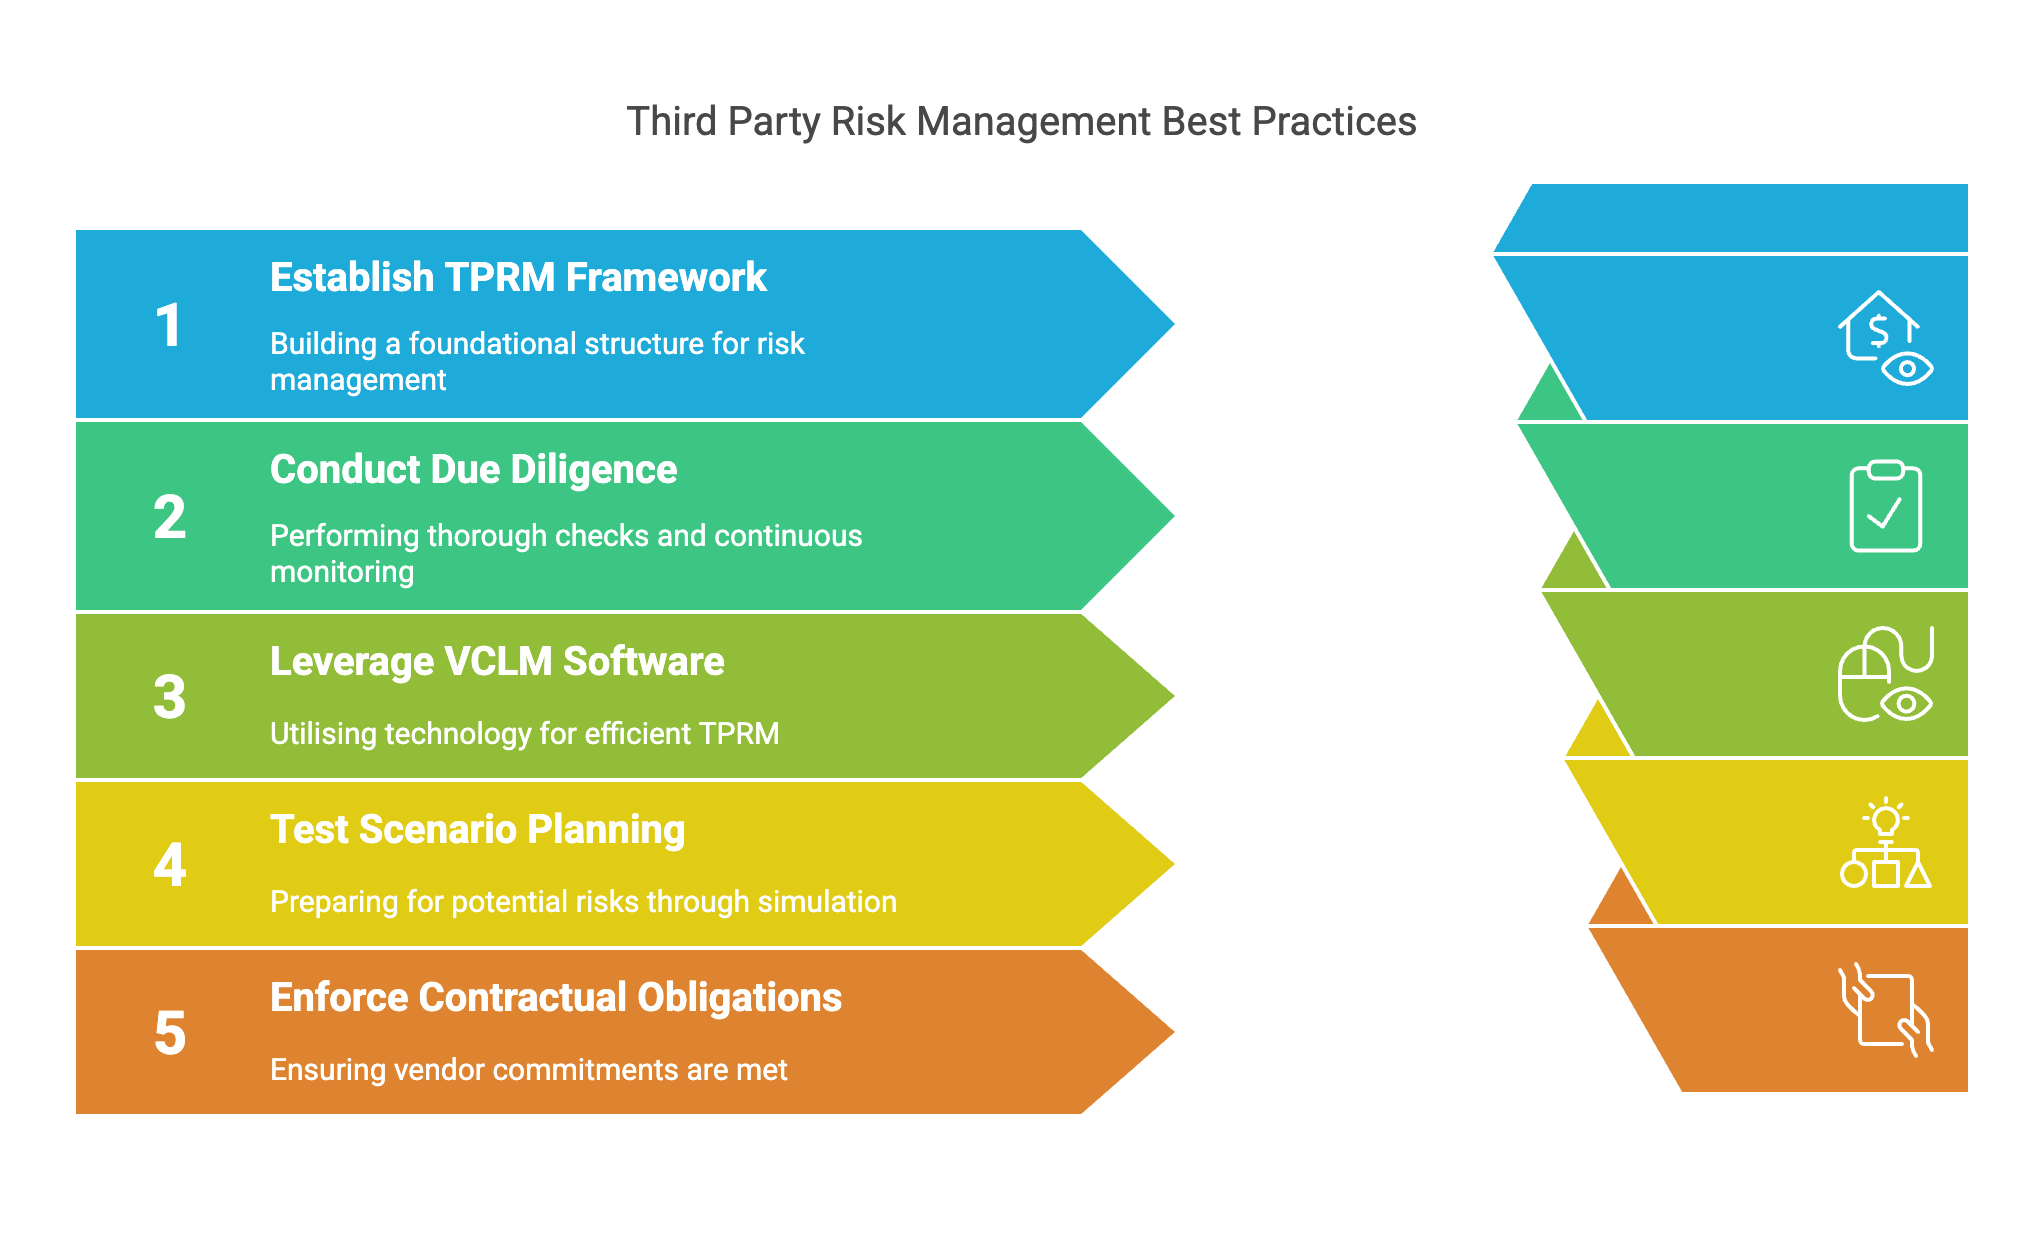
If you are starting from zero, here is a practical sequence. Month one: vendor discovery and registry creation. Month two: develop your tiering criteria and document them. Month three: assess your top ten riskiest vendors using your tiering model. Month four: implement continuous monitoring for those vendors and start the contract clause update process for the 48-hour breach notification requirement. Months five through twelve: work through the rest of your vendor population by tier, refine your criteria based on what you learn, and establish your ongoing review calendar. Third Party Risk Management Tprm is not a project you complete. It is a continuous operational discipline. The organizations that do it well are not the ones with the fanciest tools or the most comprehensive policies. They are the ones that actually read the subcontractor footnotes and update their assessments when things change.