UEFI in the Real World
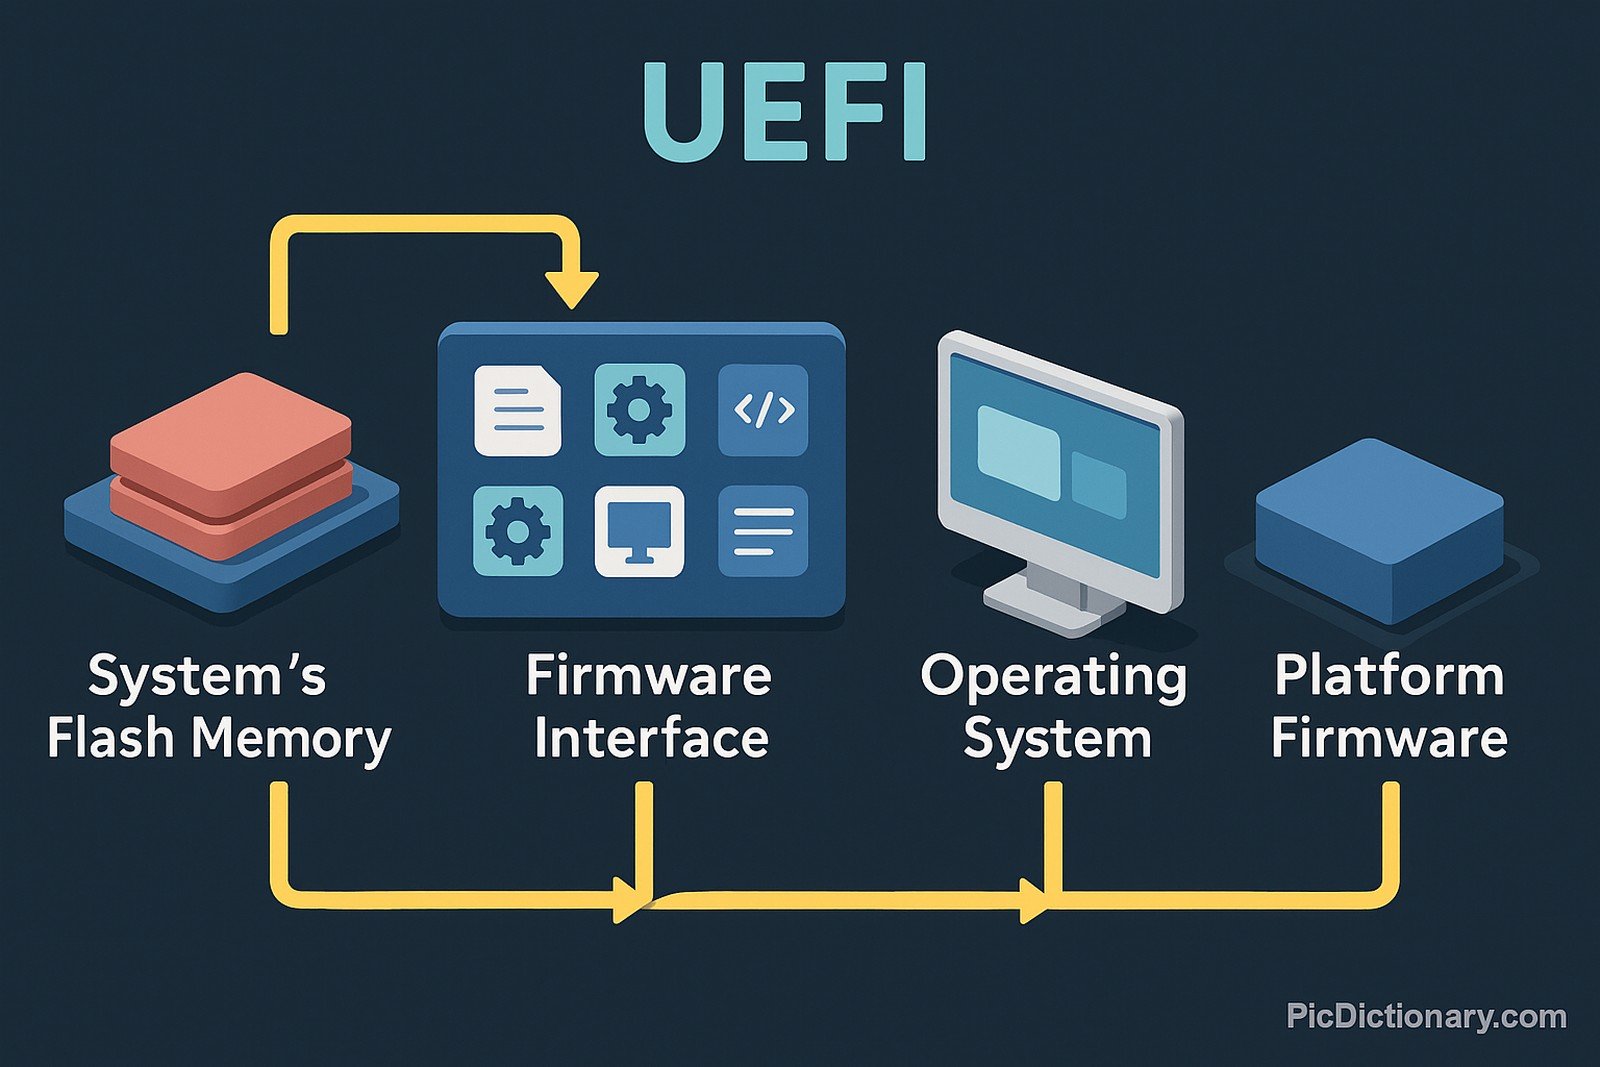
Unified Extensible Firmware Interface isn't something you "install" the way you install software on Windows or Linux. It's the firmware layer that runs before your operating system ever touches the disk. When people ask about downloading it, they're usually confused about what they're actually looking for. You don't download UEFI from a browser. You get it from your motherboard or device manufacturer, and it lives in non-volatile flash memory on the chipset. I spent about six years managing firmware rollouts across hundreds of workstations in a data center environment. The headaches I dealt with every single update cycle were never about the code itself breaking. They were about the environment around it. Things like secure boot key mismatches after a BIOS update, NVMe drive visibility disappearing between firmware versions, and the occasional nightmare where a failed power delivery during a flash brick's the entire motherboard. Those are the actual problems people encounter, not the theoretical ones you see in documentation.
Where UEFI Firmware Actually Lives
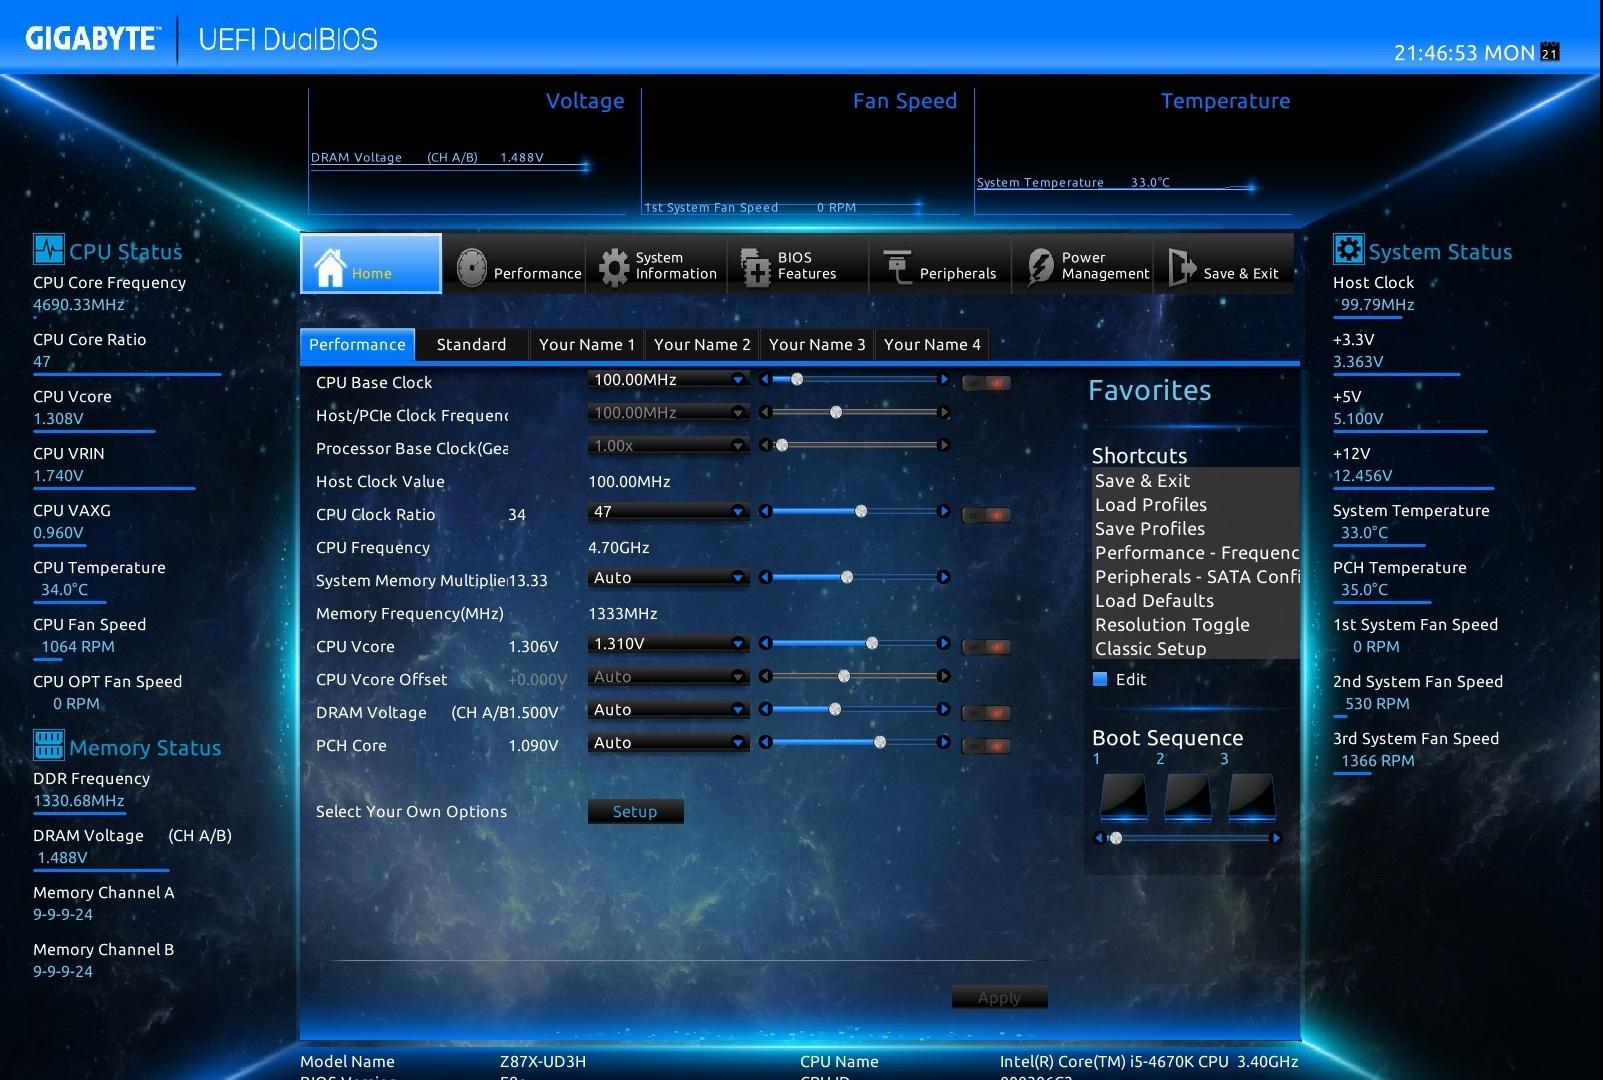
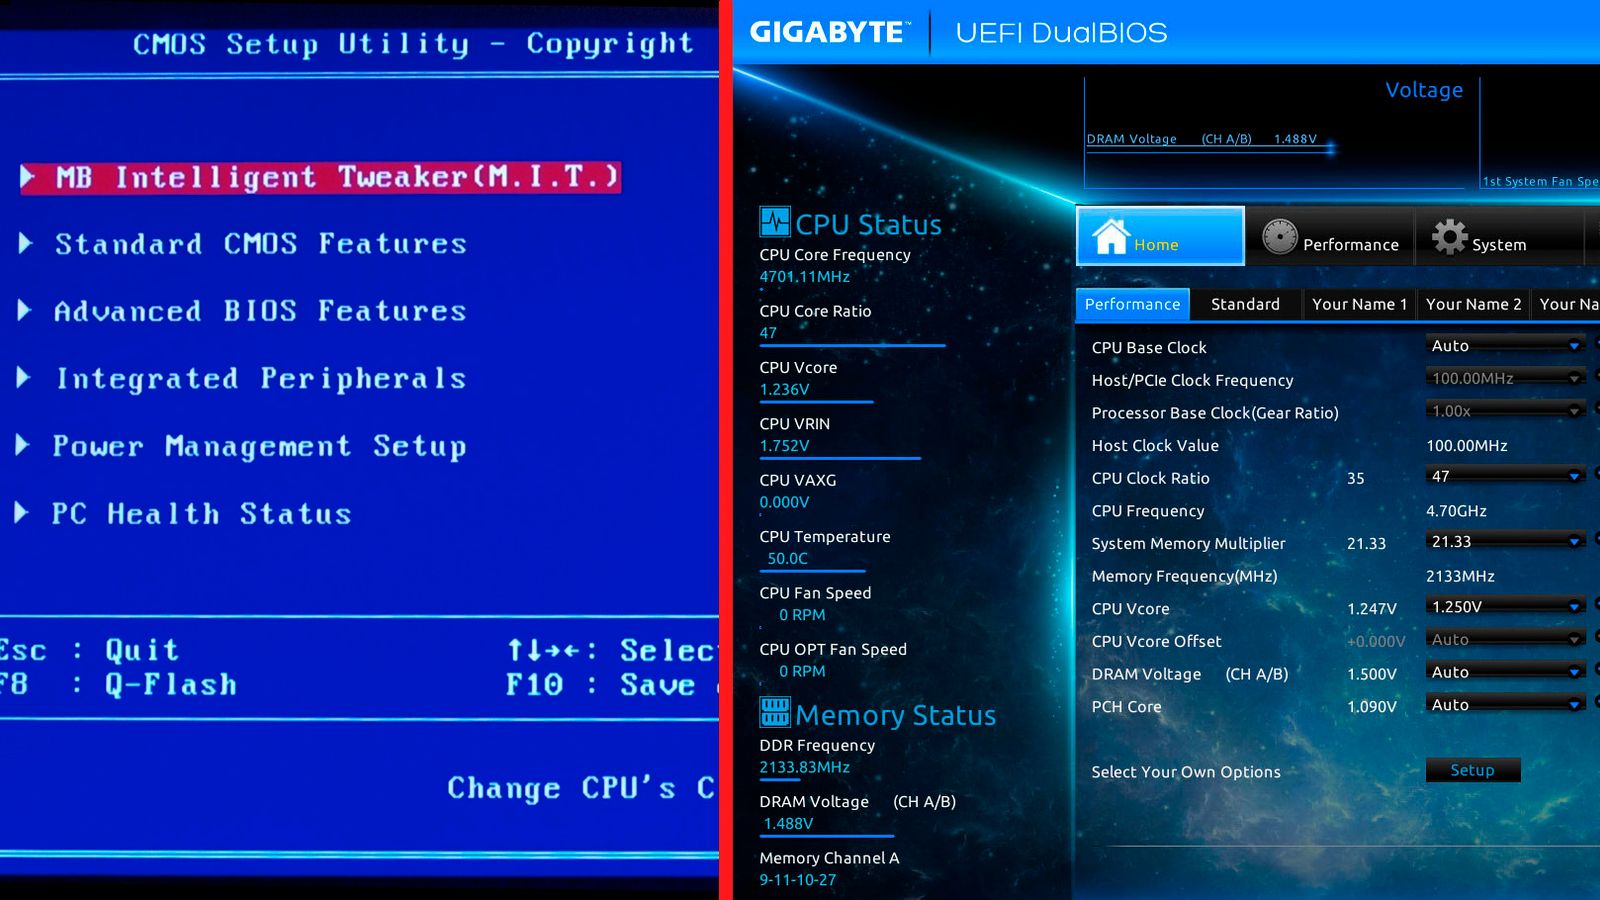
UEFI firmware is stored in a SPI flash chip soldered onto your motherboard or embedded device. On consumer systems, this is typically a 32MB to 128MB chip, depending on how much NVRAM and variable storage the manufacturer allocated. Server boards and enterprise devices often use larger chips because they carry more firmware components— BMC firmware, multiple payload modules, redundant backup firmware regions. The capacity matters because UEFI uses a file system structure called FAT32 inside the firmware volume, and the EFI System Partition on your boot drive also needs to stay compatible with that same FAT32 requirement. When you want to update it, you have three common paths. The first is flashing through the UEFI setup interface itself, usually labeled something like Q-Flash on Gigabyte boards or EZ Flash on ASUS. You drop the firmware file onto a FAT32 USB drive, enter the UEFI menu, and run the updater. The second is using a DOS-based flashing utility that requires a separate bootable USB. The third, which most enterprises prefer, is using a vendor tool like Dell Command Update or HP Image Assistant that can push firmware via WMI or PXE during imaging workflows. Each method has tradeoffs.
Secure Boot and What It Actually Does
This is where most people trip up. Secure Boot in UEFI isn't just a toggle that makes things more secure. It's a chain of trust that validates each stage of the boot process using cryptographic signatures stored in Platform Key databases. If a bootloader doesn't carry a signature trusted by your Platform Key, it won't load. Period. The problem is that not all operating systems or custom kernels ship with signatures that match your Platform Key out of the box. I had a client who was running custom-built embedded Linux systems on industrial PCs. After a BIOS update reset their Secure Boot keys to factory defaults, none of their kernels would boot. The workaround was enrolling their own Machine Owner Key into the Secure Boot database using the sign-verity tool in shim and then rebuilding their kernel with the appropriate signature embedded. This took about two hours of debugging because the documentation was scattered across three different vendor wikis and a Red Hat manual that was already outdated. The lesson here is that Secure Boot is not a set-it-and-forget-it feature. Every firmware update from the manufacturer can reset those keys, and you need a documented process for re-enrollment.
Get the Full Details

Common Pitfalls That Beginners Miss
The first pitfall is assuming that disabling Secure Boot fixes everything. It does fix boot issues with unsigned operating systems, but it also disables the measurement logs that many enterprise security tools depend on. If you're managing endpoints that report to a SIEM or need attestation, turning off Secure Boot creates a compliance gap that auditors will flag. The better approach is to understand which keys are actually in play and manage them properly. The second pitfall is related to NVRAM variables. UEFI stores configuration in non-volatile variables, and some of them are critical to boot behavior. Variables like Boot0001 through BootFFFF point to specific boot entries stored in the EFI file system on your drive. When you wipe a drive and reinstall an OS, those variables often persist in NVRAM but now point to nowhere. I've seen systems that refused to boot from a freshly installed Linux distribution because the old Windows boot entry was still first in the boot order, and the referenced EFI file no longer existed. The fix is entering the UEFI setup and clearing stale boot entries, then letting the new OS recreate them. Some motherboards don't expose a clean way to do this, which is annoying.
CSM and Legacy Boot: A Necessary Evil
Compatibility Support Module is UEFI's way of pretending to be legacy BIOS. It emulates INT 13h disk access, INT 10h video services, and other legacy interrupts that older operating systems and bootloaders expect. Most modern systems disable CSM by default because it adds complexity and can interfere with features like resizable BAR and full NVMe enumeration. But there are legitimate cases where you need it. If you're installing Windows 7 on hardware that lacks native USB 3.0 drivers in the installer, CSM gives you functional USB keyboard and mouse support during setup. If you're running certain RAID configuration utilities that only exist as 16-bit BIOS interrupts, CSM is required. The counter-intuitive part is that CSM and native UEFI boot can coexist on the same system, but they operate in separate worlds. A drive configured for UEFI boot won't be visible to CSM-based tools and vice versa. This matters when you're doing disk migrations or recovering data from a system that won't boot. If you're trying to clone a drive from a CSM-configured system using a UEFI-based live USB, the source drive might not show up at all. The workaround is either switching the target system to CSM mode temporarily or using a tool that can handle both modes.
What UEFI Cannot Fix
Firmware updates do not fix hardware failures. I've seen technicians spend hours troubleshooting what they thought was a boot configuration problem only to discover a failing CMOS battery or a degraded capacitors on the South Bridge. UEFI may report incorrect dates, lose its settings between reboots, or fail to detect drives intermittently. These are almost always hardware issues, not firmware issues. Updating the BIOS in these cases wastes time and introduces risk without solving anything. Another hard limit is that UEFI cannot compensate for fundamentally incompatible hardware. If your system requires UEFI-native drivers for a particular NVMe controller and your firmware version predates support for that drive, no amount of configuration tweaking will make it visible. The drive simply won't enumerate. In these cases, the only real solution is either a firmware update from the vendor that includes the driver, or accepting that the hardware combination is unsupported. Some manufacturers deliberately limit firmware updates to specific system models, so even if the driver exists in a newer firmware version, they may not release it for older boards. The practical takeaway is that UEFI is a layer you interact with infrequently but that sits between you and everything else on the system. Understanding how it works, what it can and cannot do, and how to recover when it breaks saves you far more time than any feature checklist ever will.