So you need to assess a vendor's security
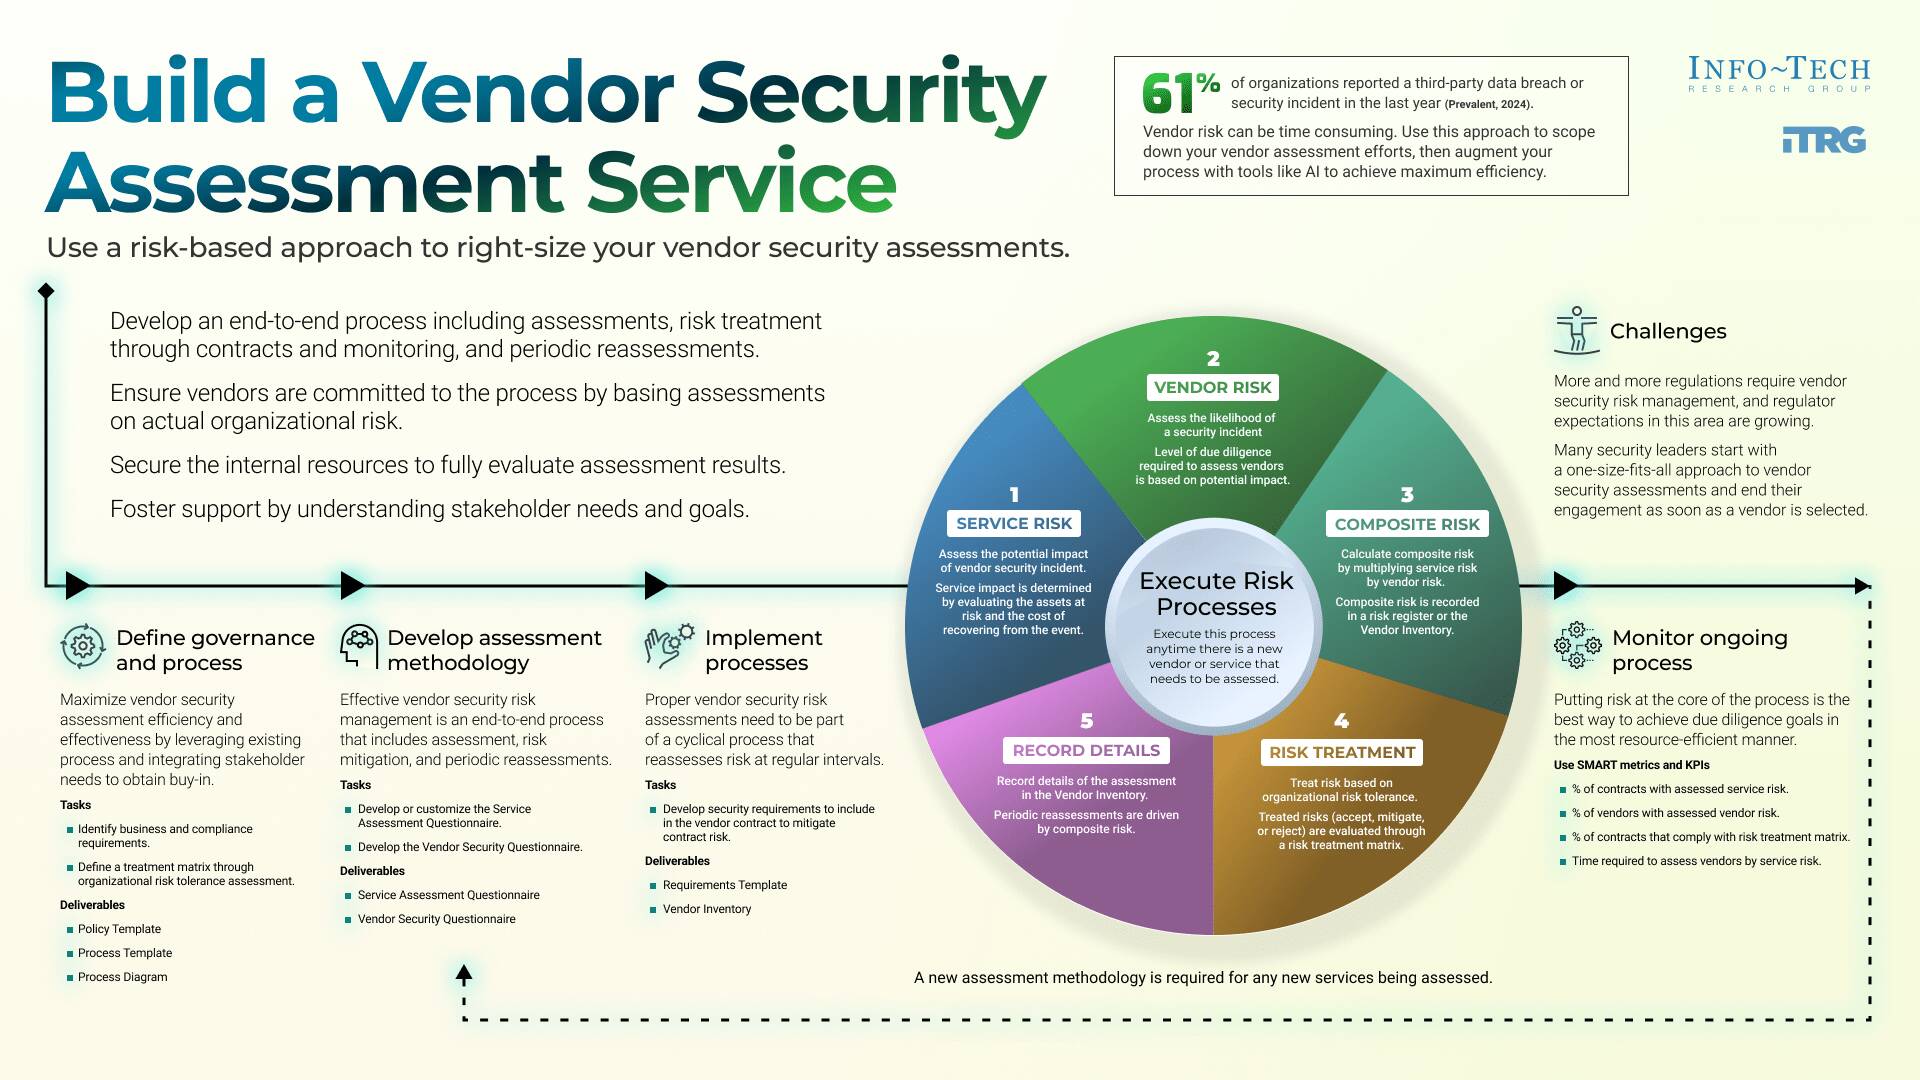
Pick up a standard Vendor Security Assessment questionnaire and fill it out in a day. Most people do. The result is a stack of PDFs that look impressive until a ransomware group compromises that same vendor three months later and your data goes with it. I've seen it enough times to know that the questionnaire is only the opening move. The real work happens after you stop pretending every checkbox matters equally. Before you send anything to anyone, figure out what risk tier you're actually dealing with. A cloud hosting provider for your staging environment does not need the same level of scrutiny as the company processing your customers' payment data. Most teams skip this step and either waste weeks on low-risk vendors or gloss over high-risk ones because they're already behind schedule. Tier them first. Tier 1 gets the full assessment, tier 2 gets a shortened version, tier 3 gets a self-attestation and a random audit spot-check once a year. This structure typically cuts assessment time by about seventy percent while focusing attention where it actually belongs. Then pick your evidence standards. SOC 2 Type II is the baseline most people accept without question. It's decent. But it covers only a narrow slice of security operations, usually the period from the last audit, and it doesn't tell you much about incident response speed or data handling procedures outside the audited scope. I learned this the hard way with a vendor who had a pristine SOC 2 report and still took fourteen hours to detect a lateral movement attempt during a breach. Their auditors never checked for detection velocity.
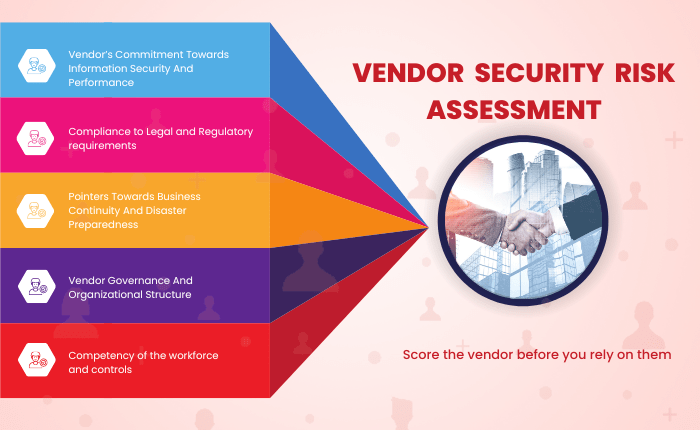
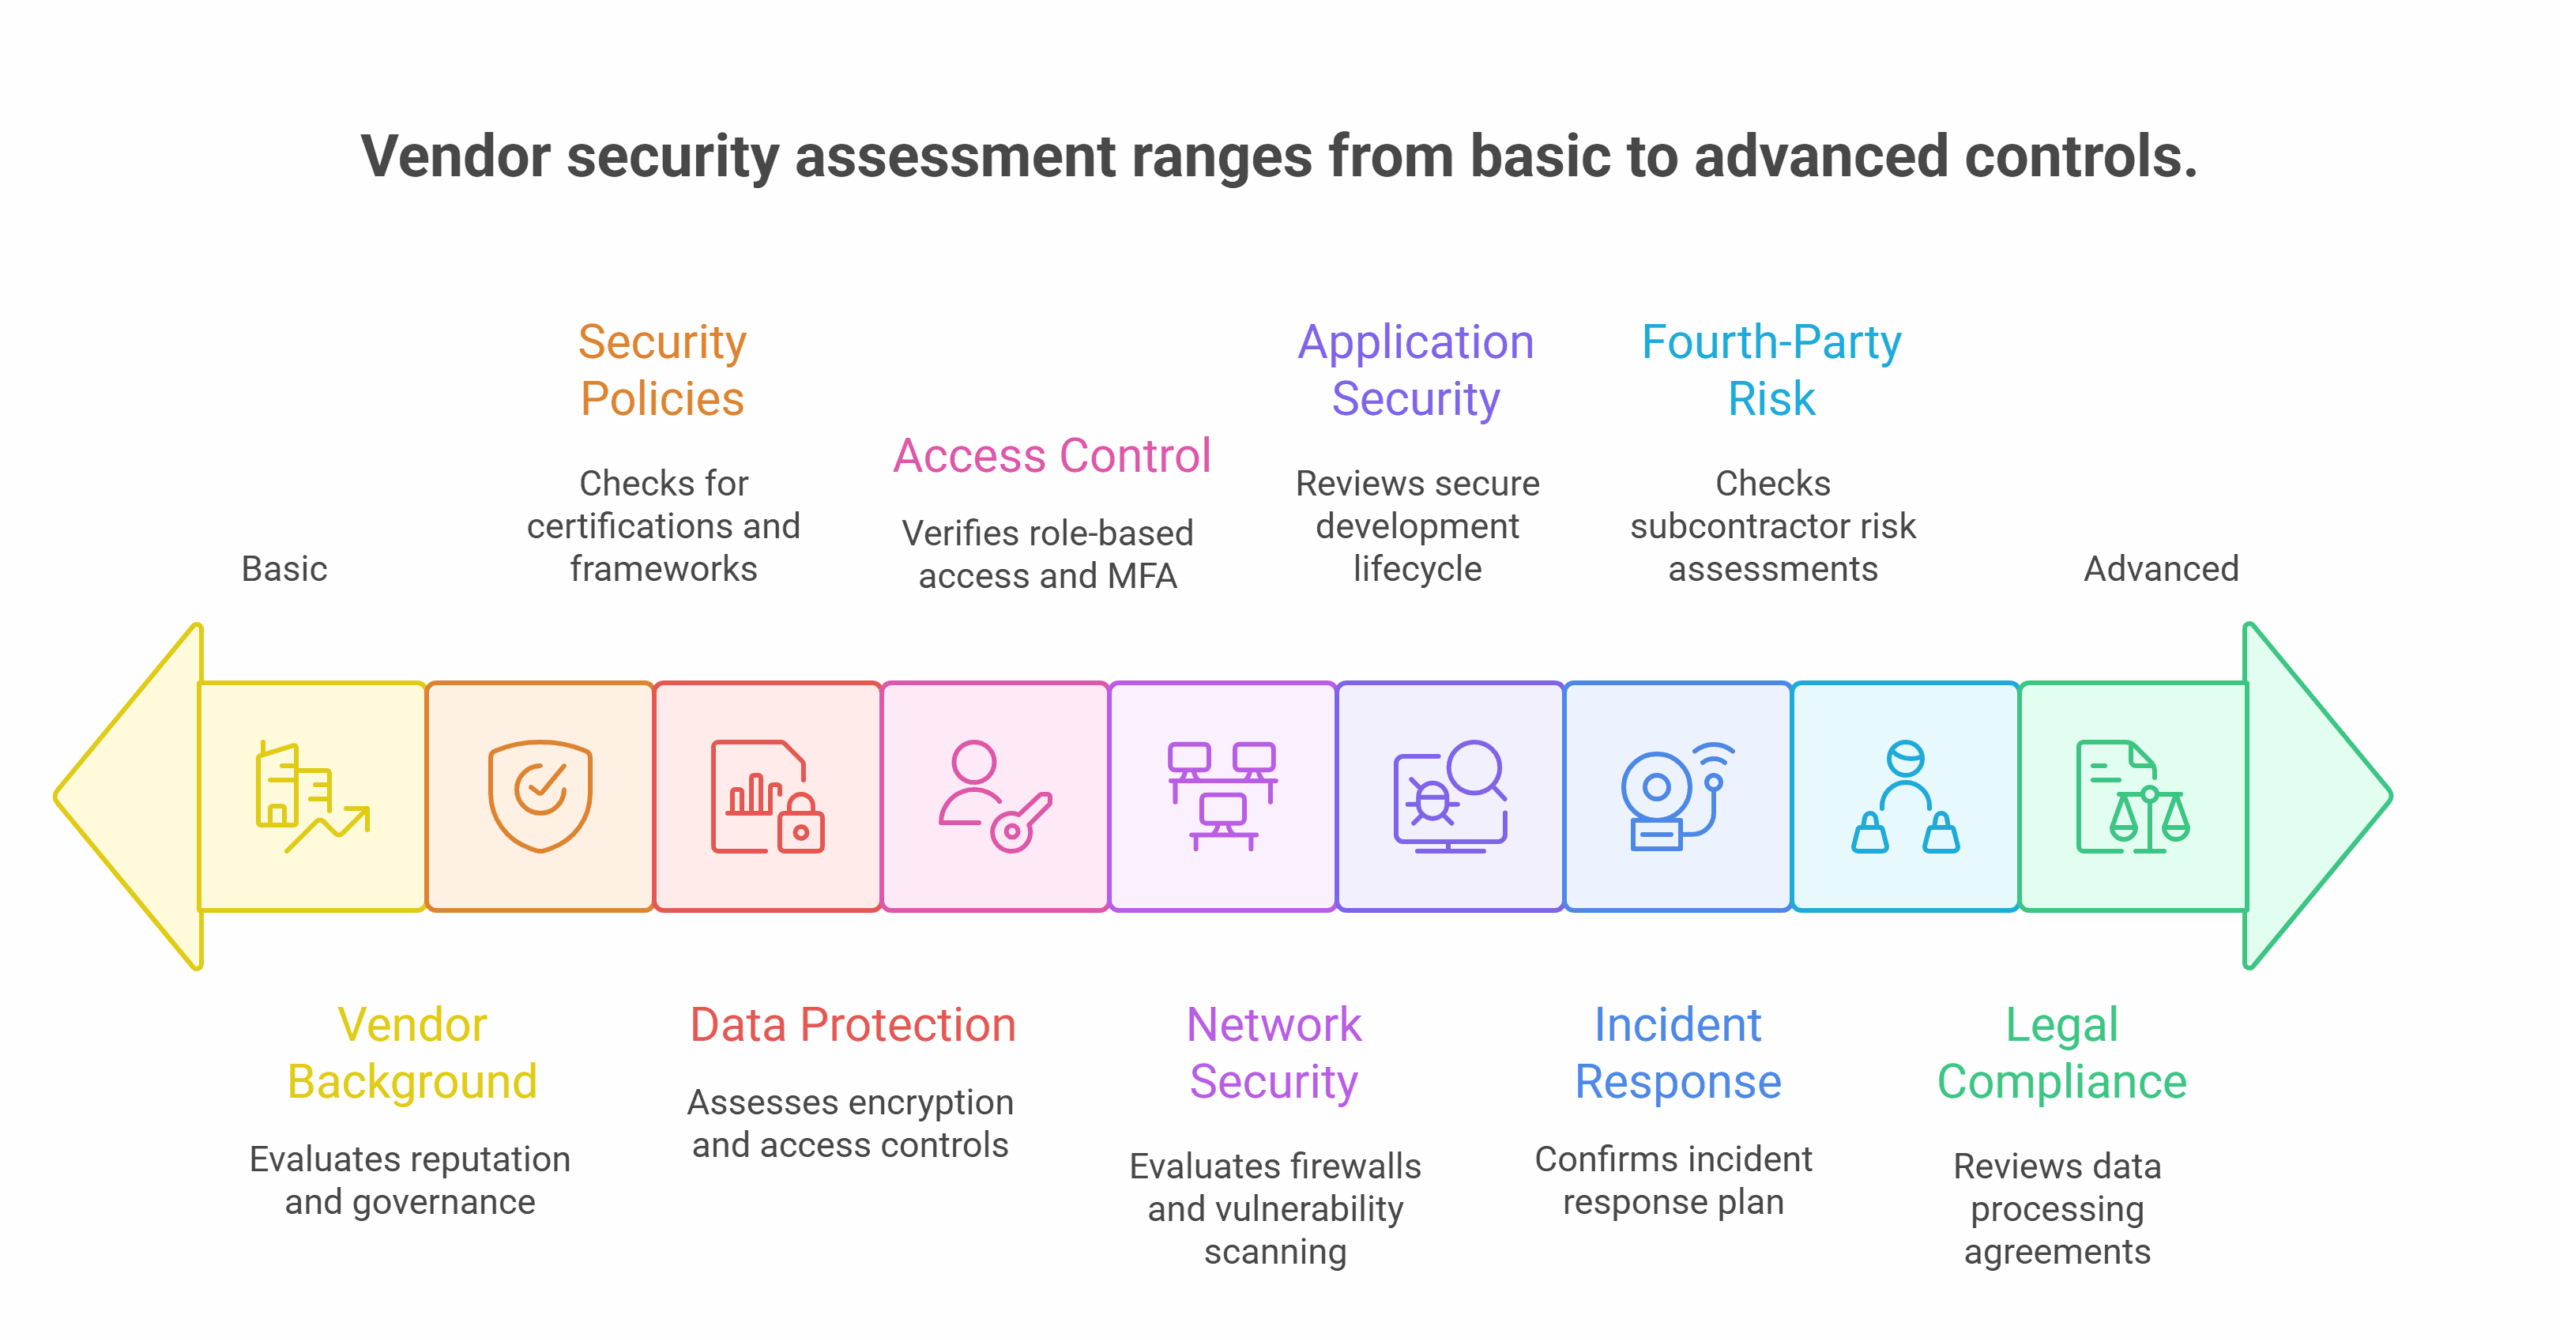
Here's what to ask for instead of just the SOC 2 certificate: your most recent penetration test summary with findings and remediation status, proof of encryption at rest and in transit with key management details, their incident response playbook (or at least the summary section they're comfortable sharing), and evidence of employee security training completion rates over the past twelve months. This combination gives you something close to what actually matters in a real compromise. It also takes about twenty minutes to evaluate if you have a checklist in front of you. Send the questionnaire at the same time you request these artifacts. Don't wait for the questionnaire responses before asking for proof. Vendors are slow to reply to generic requests. They are faster when you cite a specific document type and deadline. One vendor I worked with responded to a targeted artifact request within forty-eight hours but took three weeks to complete the full questionnaire. The artifact request was easier for them to route internally because it went straight to the security team instead of bouncing between legal, compliance, and operations. Once responses come in, score them against your tier criteria. Not on a vague satisfaction scale. Use a point system. Each evidence category gets a maximum score. Missing evidence for a tier-one vendor should disqualify them regardless of how reasonable their excuses sound. I used to bend this rule. I bent it for a analytics vendor whose product we needed and whose sales rep seemed genuinely stressed about missing documentation. Two years later their third-party breach exposed our user logs. I still think about that compromise.
There's a specific edge-case that catches almost everyone off guard. A vendor might have excellent security controls but share infrastructure with a poorly secured subsidiary or partner. You'll approve them based on their parent company's controls, then the subsidiary gets hit with a supply chain attack and yours goes down the same pipeline. I ran into this with a logistics vendor whose corporate security looked solid. Their documentation showed proper network segmentation and access controls across the board. I didn't catch the problem during the initial assessment. Three months into the relationship they acquired a smaller company and merged its IT infrastructure without updating their security policies. That merged environment had a known vulnerability that stayed unpatched for eleven weeks. When I realized the gap, I required them to isolate the legacy infrastructure and run a separate vulnerability scan within two weeks. It cost them about fifteen thousand dollars in emergency remediation and added three weeks to their patch schedule for the next quarter. The fix was straightforward but painful because nobody flagged the merger as a risk trigger during onboarding.
Get the Full Details

How to Handle the Assessment Data Once It Arrives
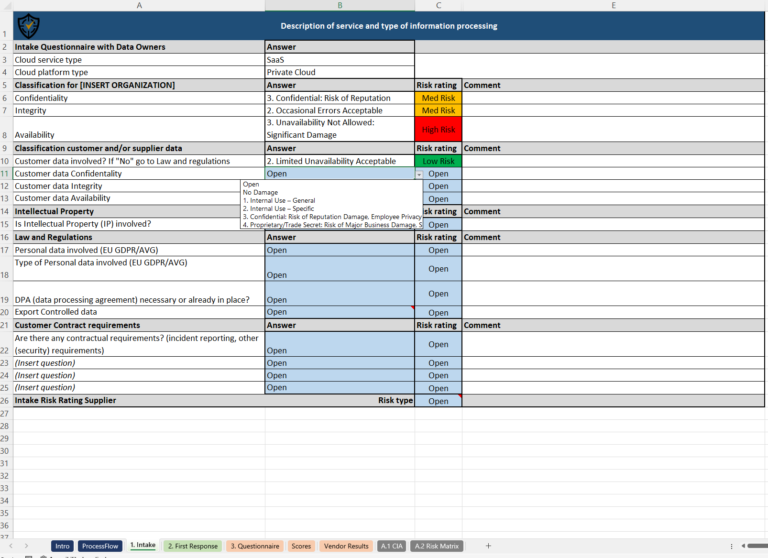
Most teams store assessment results in a spreadsheet or a shared drive and never look at them again until renewal time. This is where the process quietly fails. Put every assessment into a system that tracks expiration dates, flags missing renewals, and maintains a change log. If a vendor updates their security posture, you should see it documented somewhere rather than discovering it through a breach notification. I use a simple tracking sheet with columns for assessment date, evidence validity period, risk tier, outstanding findings, and next review date. It takes about ten minutes to set up and saves roughly an hour of panic during an annual audit when half your vendor portfolio has lapsed evidence. When you evaluate responses, watch for the differences between what vendors say and what they can prove. A vendor might claim they rotate credentials every thirty days but provide no logs or automated rotation documentation. They might say they conduct tabletop exercises but have no record of them happening. These gaps are normal. Not every claim needs to be a dealbreaker, but undocumented claims should lower the score. I adjust my scoring to penalize undocumented security practices by twenty percent per category because I've seen too many vendors treat their questionnaire answers as marketing material rather than operational facts. Findings don't disappear just because you accept them. Write a remediation plan with deadlines and assign ownership. Follow up at sixty and ninety day intervals. Most teams forget this part. They accept findings, mark the assessment complete, and move on. Vendors notice when nobody checks in. Urgency disappears the moment the paperwork is filed.
Common Pitfalls That Widen the Gap Between Theory and Reality
Assume every vendor will send back a fully completed questionnaire. Most don't. They return incomplete forms, redacted sections, or attachments that are clearly out of date. This isn't deception. It's organizational friction. Large vendors have hundreds of questionnaires flowing through their systems monthly. They do their best. Expect a round of clarification requests. Plan for two to three follow-up cycles before you have a complete picture. If you don't account for this delay in your timeline, you'll be rushed into approving incomplete assessments because leadership wants a clean vendor list by end of quarter. Another issue is over-reliance on standardized questionnaires like the Center for Security Standards or CAIQ templates. These are useful starting points but they cover generic controls that apply to most organizations. They miss the specifics of how your data flows through the vendor's environment. I add custom questions about data retention, destruction procedures, and sub-processor management because those details determine whether a breach at a vendor's sub-processor affects you directly. Standard questionnaires treat sub-processors as a footnote. They shouldn't be. There's also the problem of assessment fatigue. Vendors get pestered constantly. After the tenth similar questionnaire in a month, they start copying answers from previous responses instead of verifying current conditions. I've caught this multiple times. A vendor claimed their last penetration test was six months ago. When I asked for the report, the document date was from fourteen months prior and the findings listed vulnerabilities that had been patched. Asking for the raw report rather than accepting the summary catches this kind of stale data. It adds about five minutes to the evaluation process and prevents you from relying on outdated evidence.
Don't skip the conversation. Email-based assessments miss nuance. A fifteen-minute call with the vendor's security contact often reveals more than a week of questionnaire back-and-forth. You learn how they prioritize security work, whether they have dedicated resources or if it's a side project for someone else, and if they take third-party feedback seriously. I stopped relying solely on written responses after realizing that vendors who were actively engaged in improving their security posture were more likely to fix issues quickly when problems actually arose. Written answers can be polished. Phone conversations reveal whether someone understands their own controls or just memorized a script.
Where Vendor Security Assessment Completely Falls Apart
It doesn't work well for software-as-a-service products where you have zero visibility into the underlying infrastructure. No amount of questioning will replace a SOC 2 report or an on-site audit in those cases. You're trusting their documentation at that point. Accept that limitation and factor it into your risk calculation. If a tool is critical to your operations but the vendor won't provide adequate transparency, either find an alternative or treat the risk as accepted and compensate with compensating controls on your side, like stricter access restrictions and enhanced monitoring around that specific integration. Assessments also become meaningless when you apply the same depth to every vendor regardless of data sensitivity. I've seen teams spend three weeks assessing a parking lot cleaning service because they followed a blanket policy. That's wasted effort that pulls time away from vendors that actually handle sensitive information. Tiering solves this. It keeps low-risk vendors moving fast while directing energy toward the relationships that matter most. The biggest bottleneck I encounter is internal stakeholder alignment. Engineering wants assessments done quickly. Legal wants exhaustive coverage. Security wants everything. Someone has to make the call on what level of scrutiny each vendor receives. Without a clear decision-maker, assessments stall for months while teams debate whether a new tool qualifies as high risk. Establish a cross-functional review panel with final authority and meet quarterly to adjust tier classifications based on actual usage patterns rather than theoretical risk.
There's no perfect system. Assessments are snapshots in time, not guarantees. A vendor can pass every check today and fail tomorrow. The value is in building a process that catches issues early and forces accountability, not in creating a permanent shield. Build the process, maintain it, and move on to the next vendor.