Understanding How the Verizon MDM Platform Actually Works
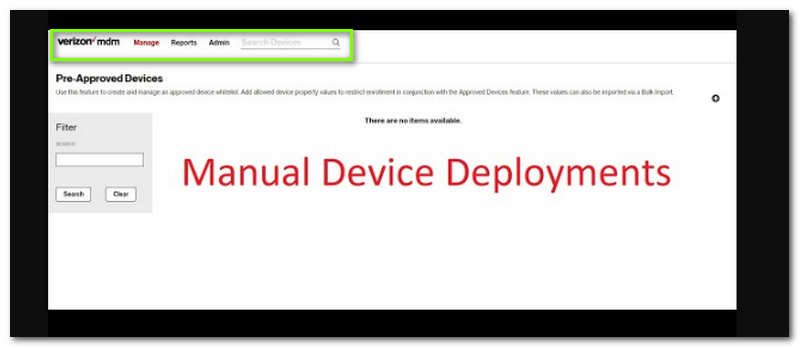
The Verizon MDM solution is built on a partnership with MobileIron, now part of Ivanti, though Verizon has its own branding layer on top of it. Most people who stumble onto this topic are IT admins at mid-size companies who got handed a handful of corporate iPhones and told to "secure them." You install the Verizon MDM profile, you enroll devices, and then you start discovering how much friction there is between what the manual says and what actually happens on the devices. I ran into this exact problem about two years ago when we rolled out 200 Samsung Galaxy devices alongside 150 iPhones. The enrollment documentation was decent for Apple but practically useless for Samsung's One UI skin. Device policies wouldn't stick to the Samsungs until I figured out that the Knox SDK was applying policies at a different hierarchy level than the MDM profile, and the conflicting rules were getting silently dropped. The workaround was disabling Knox-at-will and letting the MDM push Knox policies directly instead. The manual itself sits behind Verizon's partner portal and covers provisioning, policy configuration, remote wipe, geofencing, and app locking. It is organized by device type rather than by use case, which makes it slower to find things when you are troubleshooting on the fly. I usually skip straight to the policy enforcement section and the remote actions chapter. Most people waste time in the device enrollment section even though enrollment is mostly a one-click profile push through Apple's DEP or Samsung's Knox Setup. The sections that actually matter in practice are the policy templates. Verizon ships default profiles for standard roles like Sales Rep, Executive, and Kiosk Mode. These templates cover push-to-talk enablement, call restrictions, Bluetooth profiles, camera lock, and data usage caps. The Kiosk template is the one most useful beyond retail. It locks devices to a single app and disables all system navigation gestures, which is harder to achieve with native Android than Apple's Guided Access.
One thing the manual doesn't emphasize enough is how policy conflicts work. If you assign two device profiles to the same phone, the second one overwrites the first. This sounds obvious until you have a device enrolled in both the Sales template and the Security-Compliance template, then wonder why the app lock policy stopped working after you added the second profile. I learned this by watching compliance scores drop on fifty devices across a weekend with no changes. The fix was merging the overlapping policies into a single profile rather than stacking them. Important detail that nobody mentions in the quick-start guides: the Verizon MDM console caches device states for up to thirty minutes. When you push a policy or a remote command, the console will show it as successfully delivered within seconds, but the device may not apply it for half an hour depending on network conditions and battery optimization settings. This means testing a policy change by immediately checking a single device is unreliable. Wait at least forty-five minutes before declaring a policy deployment failed.
Enrollment Process and Common Breakpoints
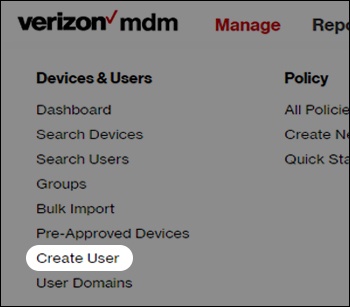
Device enrollment starts with obtaining the right tokens. Apple requires your Enrollment ID from the Verizon portal and your MDM server certificate. Samsung requires Knox Workspace setup and a valid Knox license key. The manual walks through this linearly, but the real process is not linear. I typically start with the Apple side because it errors out less often, then move to Samsung once the MDM backend is verified. If you flip the order, you will spend twenty minutes debugging the Apple portion only to realize the Samsung configuration broke the shared MDM connector first. The most common failure point is the APNs certificate for Apple devices. Verizon's portal generates it automatically, but it expires every year and the renewal process requires a full re-push of the configuration profile to every enrolled iPhone and iPad. Missing even one device means it stops receiving remote wipe commands and inventory updates. I set a calendar reminder six weeks before expiration and re-push during off-hours on a weekend. For Android devices, the biggest issue is the Samsung Knox container. Knox Workspace creates a sandboxed environment inside the OS, and MDM policies only apply inside that container unless you explicitly configure full-device management mode. The manual describes FDM but does not warn that Verizon's default Knox policy for most enterprise contracts enables Work Profile mode, not FDM. Switching to FDM requires un-enrolling the device and re-enrolling with a different profile type. That wipes the workspace and any apps installed inside it.
Get the Full Details

Push-to-talk provisioning through Verizon MDM works through the Zello integration. The manual covers basic assignment and channel configuration, but it skips over group assignment conflicts. If you assign a device to a Zello group through the MDM console and the user also manually adds it to a different group, the MDM policy will override the user's manual setting during the next sync cycle. This is useful for enforcing structure but destructive if you want users to customize their own channel lists on personal devices.
Policy Configuration That Actually Matters
The policy engine in Verizon's MDM supports over sixty individual settings per profile. The ones you will use repeatedly are password requirements, encryption enforcement, jailbreak detection, app allow-listing, and VPN settings. Password requirements and jailbreak detection are straightforward. App allow-listing is where most admin pain comes from. Adding an app to the allow-list through the console requires the app's bundle ID for iOS or package name for Android. If the bundle ID is wrong, the policy silently fails and the app installs but gets blocked on the next sync. I always verify bundle IDs through the Apple Developer portal or Google Play Console before adding them to the allow-list. Double-checking takes thirty seconds and prevents hours of support tickets from confused end users. VPN configuration through the MDM uses either IKEv2 or SSL tunnel mode depending on your VPN provider. Verizon supports custom VPN profiles for most enterprise setups, but the manual only provides examples for common providers like Cisco AnyConnect and Check Point. If you are using something like Palo Alto or Fortinet, you will need to build the profile XML manually. The schema is documented but the file is unforgiving. A single misplaced tag causes the VPN profile to reject silently on the device with no error message on the MDM side. Export a working profile from a test device, open the XML, and compare it against your new configuration. This saves more time than any amount of reading the policy reference tables. Data usage restrictions are available but throttled at the device level, not the app level. You can set a monthly data cap per device or per user, but the cap applies to total cellular data. If you need to restrict a specific app's bandwidth, you have to route that app through a VPN policy with application-level controls outside the MDM. The MDM console does not handle per-app bandwidth throttling on its own.
Remote Actions and Troubleshooting
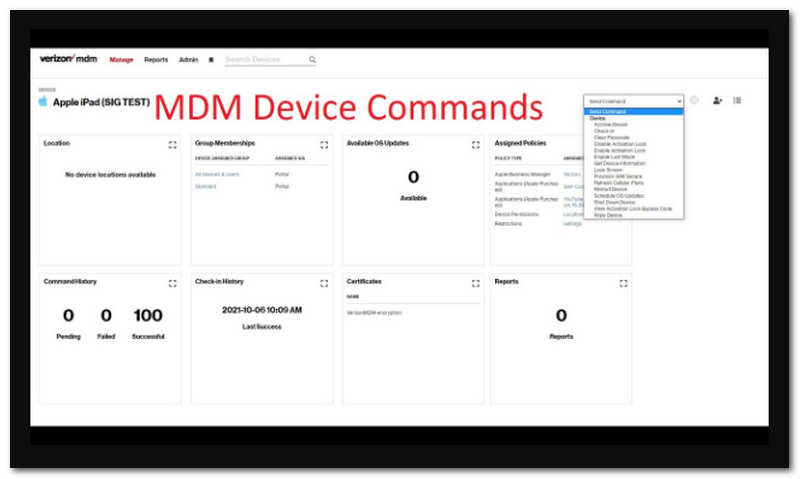
The remote commands available through the console include lock, unlock, wipe, restart, and policy refresh. These are standard for any MDM system. What the manual underplays is the timing behavior. A remote wipe on an Android device does not execute until the device checks back into the MDM server. That check-in interval is configurable per policy, and the default is often two to four hours to conserve battery. A wipe command queued in the console can sit in "pending" status for a long time if the device is offline or in battery-saver mode. I have watched devices stay in a pending wipe state for up to twelve hours before executing, and that gap matters when a phone goes missing and you need to act immediately. The most useful remote action nobody uses enough is the diagnostic log pull. Verizon MDM can collect device logs on demand, including kernel logs, app crash reports, and policy application traces. The logs are compressed into a zip file and delivered to the admin console within a few minutes. This is how I identified the Samsung Knox hierarchy conflict mentioned earlier. I pulled logs from ten non-responsive devices, found the same error pattern across all of them, and traced it back to the policy conflict. Without the diagnostic logs, I would have spent a week swapping devices and blaming hardware. Inventory reporting has two modes: on-demand and scheduled. Scheduled reports run on a timer you define and email results to configured addresses. On-demand reports generate immediately but take longer. The manual suggests scheduled reports for routine compliance tracking and on-demand for audits. In practice, scheduled reports miss devices that check in outside the report window. If your report runs at 2 AM and a device syncs at 3 AM, the device appears in the next day's report but not the current one. Scheduling on-demand inventory queries during business hours after a policy change gives you a more accurate picture of which devices actually applied the new settings.
Limitations and Workarounds
Verizon MDM handles standard enterprise device management well, but it has real limitations. First, it does not support macOS device management natively. If your organization uses Macs, you need a separate MDM or you can only manage them through web-based console restrictions, which are incomplete. Second, the console lacks fine-grained conditional access rules. You cannot build a policy that says "apply this setting only when the device is on Verizon's network AND the OS version is above 13 AND the user is in the Sales group." The rule engine is simpler than competitors like VMware Workspace ONE or Microsoft Intune. Third, the web interface is slow during peak hours and exports are limited to CSV format. PDF generation for audit reports is not available through the native console. When these limitations matter, the common workaround is pairing Verizon MDM with a lightweight supplementary tool for the gaps. A small Python script that queries the Verizon MDM API daily and flags devices missing required policies reduces the conditional access problem enough for most mid-market companies. For macOS management, switching the Macs to a separate MDM provider like Jamf Now costs nothing extra if you already have Intune licenses. The key is recognizing early that Verizon MDM is a solid foundation, not a complete ecosystem solution. The platform also lacks built-in BYOD segmentation beyond the basic work profile boundary. If you need different policy sets for employees who bring their own phones versus company-issued devices, you have to create separate enrollment paths and manage them manually. There is no automatic tagging system that detects device ownership type and applies policies accordingly. I resolved this by using device serial number ranges in my procurement system to flag company-owned units, then matching those serial numbers against MDM enrollment records in a spreadsheet before assigning profiles. It is manual but predictable.
Verizon Mdm User Manual – Where to Find It and How to Update
The manual is hosted on Verizon's enterprise support portal at verizonbusiness.com. You need a partner or business customer login to access it. The documentation page includes the current version number and a changelog. New versions publish roughly quarterly with feature additions tied to Apple and Samsung OS releases. I recommend downloading the previous version alongside the current one and keeping both on a shared drive. Version drift is the reason half the forum posts about this MDM are outdated — people read a 2023 guide while the 2025 console has reorganized the policy settings into different menus. Checking the version date at the top of the manual before following any procedure prevents a lot of confusion.