Communication tools after a breach aren't glamorous. They just have to work.
I spent a good chunk of my career building breach response communication frameworks, and the tools themselves are mostly boring. The difference between a clean notification process and a disaster comes down to whether your infrastructure can handle volume without breaking. People want long lists of software names, but the real problem is matching the tool to the situation. The core categories break down pretty quickly. Notification delivery platforms handle mass outreach. Dedicated breach response websites serve as the single source of truth. FAQ management systems reduce repetitive inquiry load. Communication hubs coordinate internal and external messaging. Social media monitoring tools track public sentiment in real time. Community forums let affected people share experiences. Call centers or hotlines handle complex individual cases. Webinars and live Q&A sessions give people a chance to ask questions directly. Press release distribution ensures journalists get consistent information. Here's what those look like in practice.
Notification platforms like Everbridge, Sendico, or EvenView push personalized breach notices through email, SMS, voice calls, and physical mail simultaneously. They handle opt-out compliance, delivery tracking, and regional regulatory requirements. The one you pick depends on your reach and jurisdiction. For a consumer-facing company with millions of customers across multiple states, Everbridge gives you the volume capacity and audit trail you need. A smaller org might get by with Sendico because it's lighter on setup and cost. Dedicated breach response websites are usually static pages hosted on a subdomain like breach.yourcompany.com. They contain the incident summary, what was exposed, what you're doing about it, and links to credit monitoring if applicable. Tools like Sitecore or even a simple HTML template work fine here. The trick is making sure the page stays live for years. I've seen companies let their breach page go dormant after six months, then get slammed again when a follow-up investigation expands the scope. The domain renewal got forgotten. FAQ management is where most teams underinvest. Platforms like Telligent or even a well-structured WordPress install can handle the question volume. The key is categorizing by data type, not by customer segment. A question about payment card exposure needs a different answer than one about health records. Mixing them confuses callers and creates legal exposure. A single FAQ page organized around data categories cut our inquiry resolution time from about 40 minutes per call to roughly 12 once we stopped answering generically.
Communication hubs like Slack or Microsoft Teams with dedicated breach-response channels keep internal teams from talking past each other. Legal, PR, IT, and customer support all end up in the same channel. It sounds obvious until someone posts a press statement draft in the general marketing channel and the PR team has no idea it's been shared externally. We built a simple protocol where any external communication had to be posted to #breach-legal-review first, and it prevented at least three bad launches in my experience. Social media monitoring with tools like Brandwatch, Sprout Social, or even Hootsuite's analytics tier lets you see what people are saying before the third-party blogs pick it up. The early warning matters because a viral tweet about your breach hits before your FAQ page is finished. I tracked a notification that landed on Reddit with three upvotes at 2 AM and was already at 4,000 by 8 AM. Having that visibility at 2 AM meant we could post a holding statement before the narrative solidified. Call centers range from professional services like Concentrix and Teleperformance to simpler IVR systems like Genesys Cloud. When a breach hits, the volume spikes 10 to 50 times normal within hours. The workaround most teams miss is pre-building script templates for the top ten questions before the breach happens. I learned this the hard way during a ransomware incident where our call center team spent the first 36 hours answering emails one by one instead of routing through structured scripts. We were drowning in repetition.
Get the Full Details
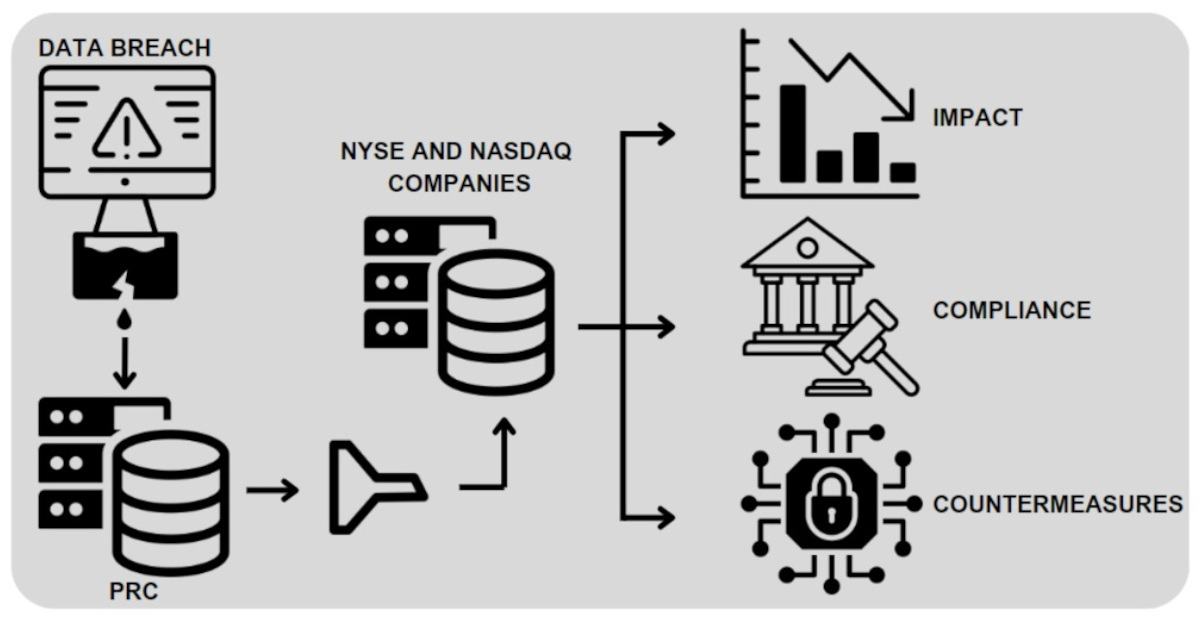
Webinar platforms like Zoom Webinar or Webex Events handle live Q&A sessions. These are overrated for most breaches. They work well when you've got a complex incident affecting a niche audience, like a financial services firm explaining how encrypted data was accessed. They're a waste when the breach is straightforward and most people just want to know if their data was in the file. I ran a webinar for a mid-level breach and had 14 people show up out of 200 registered. The FAQ page and email answers handled the rest. Community forums powered by Discourse or Vanilla Forums let affected parties help each other. This is surprisingly effective for enterprise breaches where employees need guidance on changing passwords, freezing credit, and recognizing phishing attempts. The self-moderation aspect reduces your support burden significantly. One downside: people will post incorrect information and you'll need active moderation. We had someone spread false details about our encryption standards that nearly caused panic until a team member corrected it in the thread. Press release distribution through Newswire, Business Wire, or PR Newswire ensures coverage reaches outlets consistently. The anti-pattern here is writing the press release before you have the full facts. I've seen teams rush a statement that gets retracted within hours, which destroys credibility faster than silence would have. Wait until legal clears the details. The trade-off is real but the alternative is worse.
The edge case that taught me the most
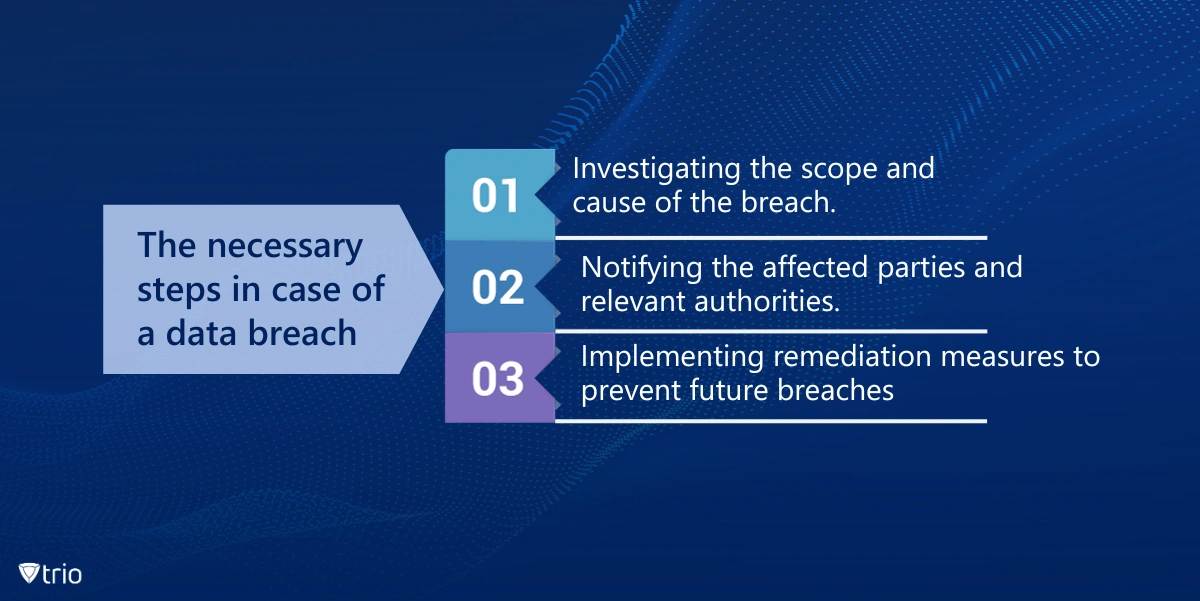
During a healthcare breach, we needed to notify over 200,000 patients with individualized letters meeting HIPAA requirements. The notification platform we'd chosen couldn't handle the variable data fields we needed—patient name, specific data types exposed, individualized remediation steps based on what was in their record. The vendor suggested a workaround that involved exporting CSVs, running them through a script, and reimporting them. That approach broke after the first 50,000 records because of character encoding issues with special names. The fix was switching to a hybrid model. We kept the platform for delivery tracking and compliance reporting but built a custom notification generator that pulled directly from the patient database using a stored procedure. It produced individually tailored PDFs for each person. The whole process took about three weeks to set up but cut the notification timeline from an estimated four months down to six weeks. The lesson: don't assume a single tool handles everything. Hybrid approaches exist for a reason.
What beginners get wrong
Most teams treat breach communication as a one-way broadcast. It isn't. The best engagement tools create feedback loops where you can adjust messaging based on incoming questions. If your FAQ page isn't generating new question categories that haven't been answered, your team isn't listening closely enough. I track question volume by category weekly. A spike in "did you sell my data" questions means the public narrative has drifted from what you intended, and you need a new FAQ entry, not just a social media response. Another common failure is choosing tools based on price rather than compliance features. A cheap notification platform might save you money upfront but lack audit logging required by GDPR or state breach notification laws. Every tool in your stack needs to produce documentation you can hand to regulators without a second thought. That single requirement should eliminate half the options on any comparison list.
When these tools don't help
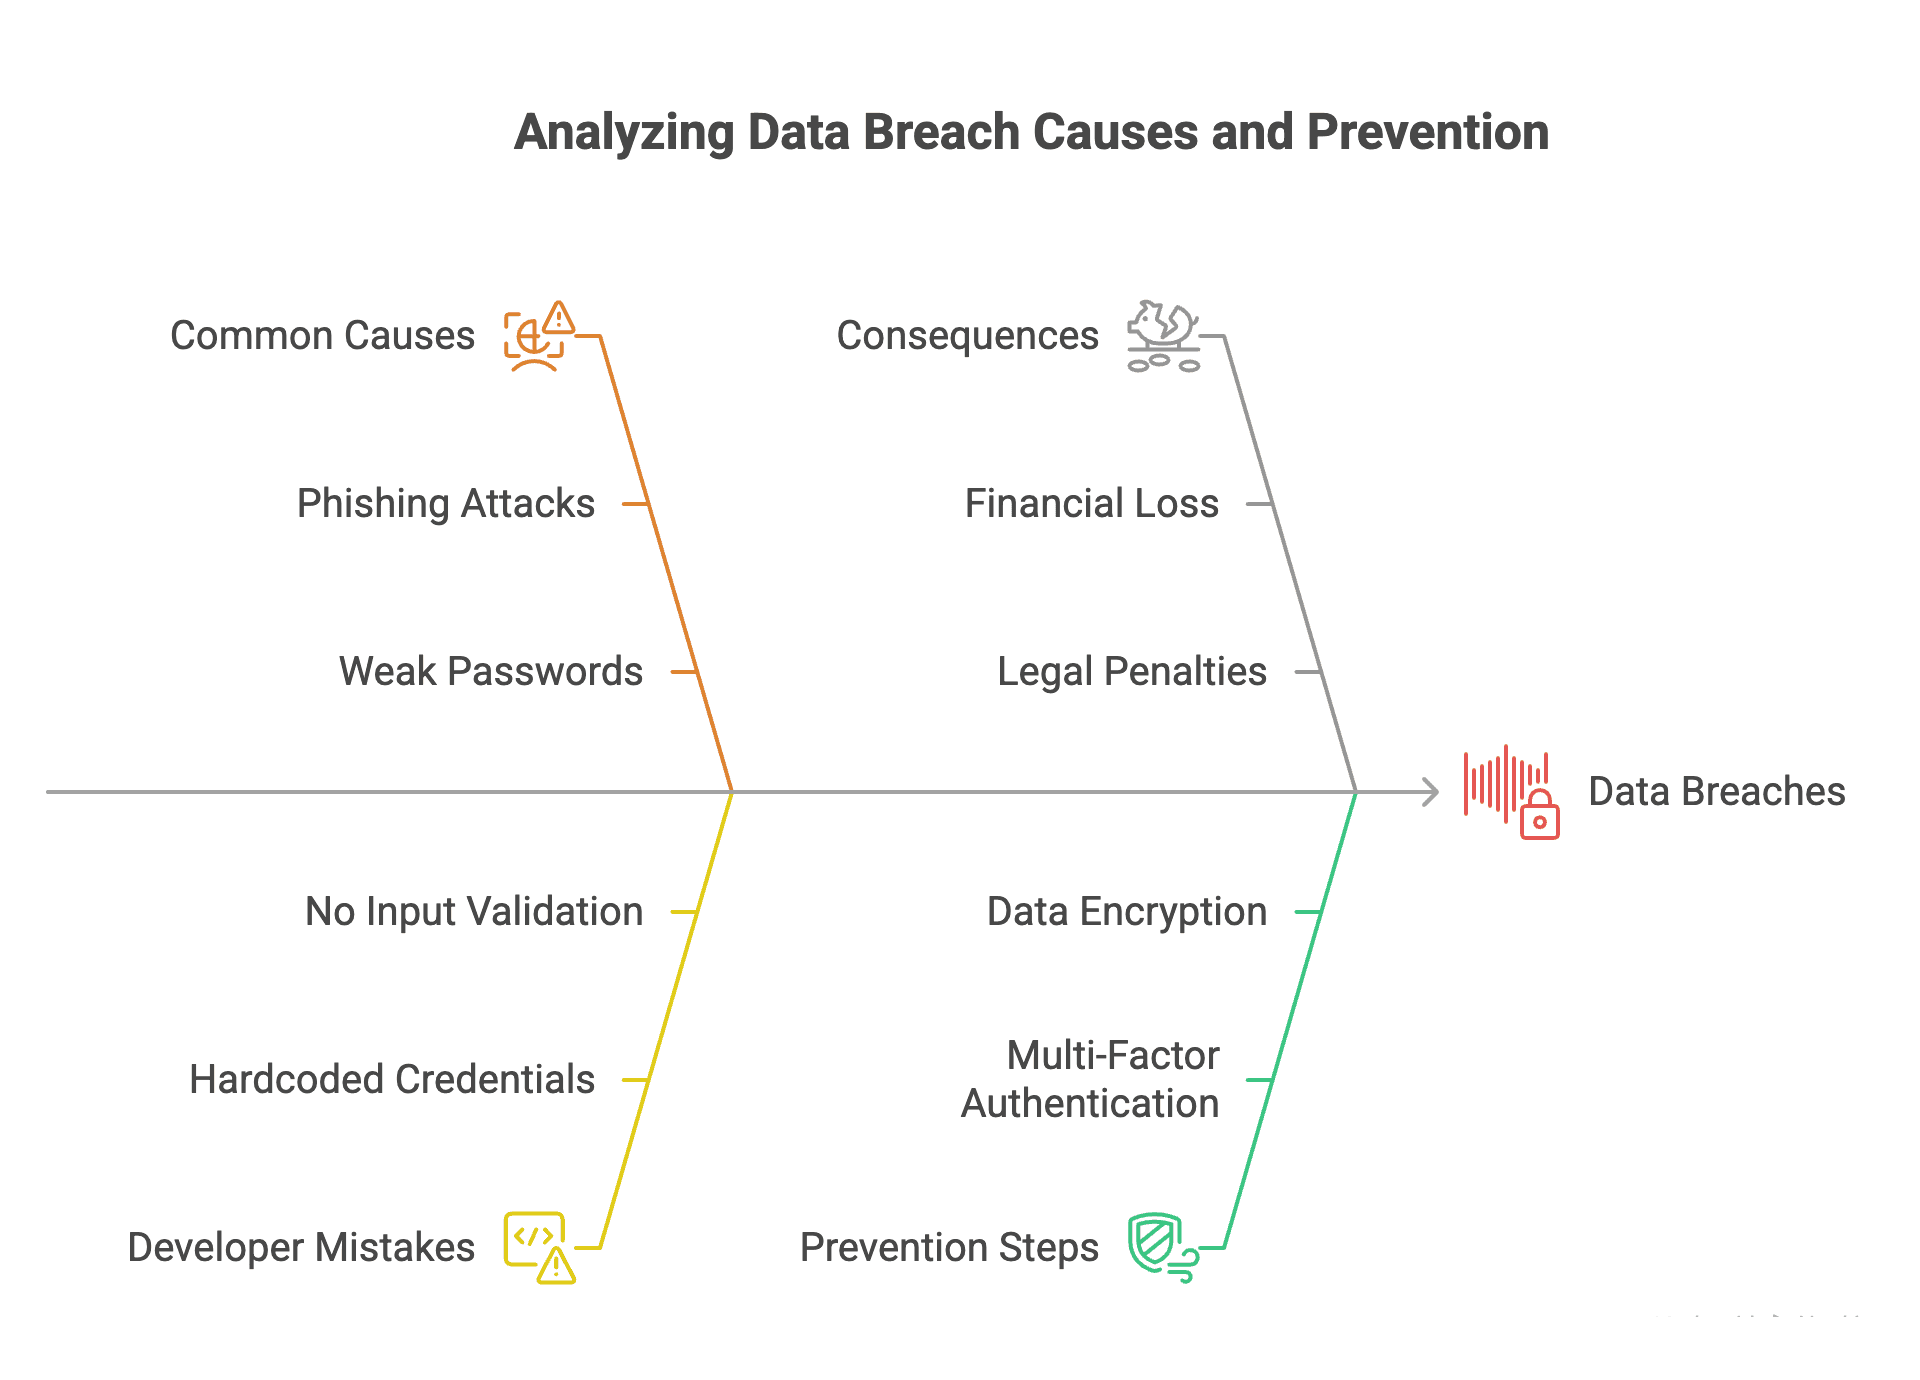
No tool fixes a bad incident response. If your technical investigation is still running when notifications go out, you'll have to issue corrected notices. That's exponentially more damaging than getting it right the first time. Tools amplify whatever process sits behind them. A sophisticated notification platform with sloppy legal review produces sophisticated wrong notices. The bottleneck is almost always internal alignment, not technology capability. Also, community forums and social media monitoring become liabilities if you don't have dedicated staff watching them. Unmoderated spaces fill with misinformation faster than you can correct it. I'd rather run a simple FAQ and email response pipeline than manage an active forum without staffing. The trade-off is real: less engagement potential but also less chance of your own platform becoming a source of secondary damage. The tools exist. The hard part is deciding which ones matter for your specific breach and having them ready before you need them. Most teams buy or configure these things under pressure, which is the worst possible time to learn that your platform can't handle your data volume or your jurisdiction requires specific logging formats. Build the stack during peacetime. Test it. Move on to the next thing until the next time you absolutely need it to work.