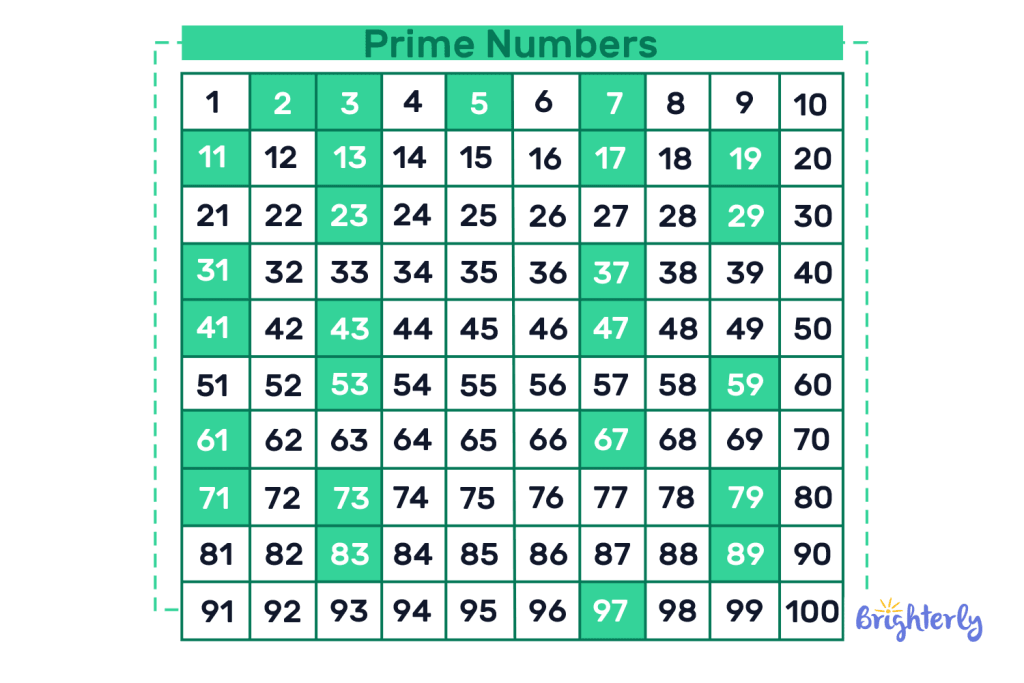
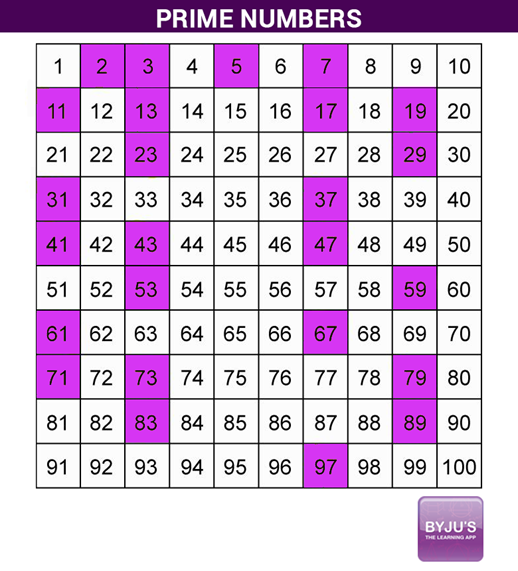
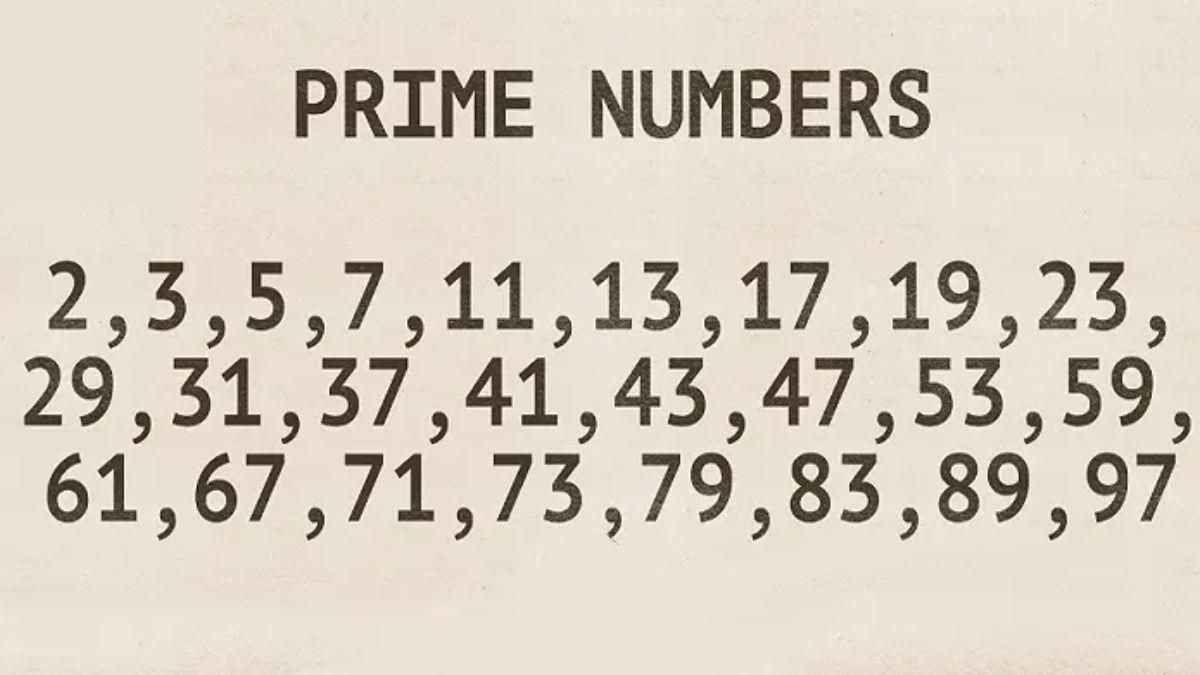
Understanding Prime Numbers and Why They Actually Matter
I spent a good chunk of 2019 debugging an encryption library where the prime number generation was slightly off. Not obviously wrong, just a subtle edge case around 128-bit primes that caused handshake failures in production. The root cause was a Miller-Rabin test implementing a too-small set of witness values. I had to write a custom primality verification routine from scratch just to get past that bottleneck. It cost me about three days of lost productivity, but it taught me a lot about what actually happens when primes go wrong. A prime number is a positive integer greater than 1 that has no divisors other than 1 and itself. That definition sounds simple because it is simple, but the implications are not. The distribution of primes follows the prime number theorem, which says the density of primes near a large number n is roughly 1/ln(n). This means primes get rarer as numbers grow, but they never stop appearing. The gap between consecutive primes can be arbitrarily large, which matters a lot if you're generating keys for RSA. In practice, most people who need primes are working in cryptography, hashing, or randomized algorithms. If you're building a hash table, a good prime-sized bucket count reduces collision clustering. If you're doing modular arithmetic, understanding multiplicative order and primitive roots comes directly from prime properties. For casual use, the Sieve of Eratosthenes is fine up to about 10 million. Beyond that, you switch to segmented sieves or probabilistic tests.
The Miller-Rabin primality test is the workhorse for checking large numbers. It runs in O(k·log³n) time where k is the number of rounds. For cryptographic-grade primes, you want at least 40 rounds, which brings the error probability below 2^-80. Deterministic variants exist for numbers under 3×10^24 using specific witness sets, but if you're generating 2048-bit RSA primes, you stick with probabilistic testing and move on.
Common Mistakes That Waste Time
The most frequent beginner mistake is assuming that any odd number that passes a quick divisibility check is prime. It is not. Pseudoprimes exist in quantity. A Fermat pseudoprime to base 2 like 341 will pass the basic Fermat test but is clearly 11×31. Strong pseudoprimes are even trickier because they pass Miller-Rabin for certain bases. The fix is straightforward: use multiple bases and accept that you're working with probability, not certainty, unless you use a deterministic bound. Another trap is generating primes sequentially and testing each candidate. This is dramatically slower than sieving a range and then picking from the survivors. If you need 1000 primes near 10^12, a segmented sieve over an interval of about 10^6 around that value will find them in seconds on modern hardware, while trial division on individual candidates could take minutes. There's also the question of how you generate primes for cryptography. You don't pick a random number and test it. You start from a random seed, force the top and bottom bits to the required values (most significant bit set for the right size, least significant bit set for oddness), and then sieve or test forward from there. This avoids accidentally generating primes with undesirable structural properties. Some implementations skip this and just test raw random numbers, which works fine functionally but introduces unnecessary variance in generation time.
Get the Full Details

When Primes Break Down as a Solution
Prime-based approaches are not universal. Hash table sizing with primes helps, but modern alternatives like power-of-two sizing with good mixing functions often perform better in practice, especially on processors where bitwise operations are cheap and predictable. The prime-divisor advantage is real but niche. In database indexing, composite keys with proper cardinality selection usually outperform anything prime-related. For quantum-resistant applications, prime factorization hardness is exactly what Shor's algorithm breaks. If you're designing systems meant to last beyond the next decade, relying solely on prime-based RSA or Diffie-Hellman is a liability. Switch to lattice-based cryptography like CRYSTALS-Kyber or NTRU. The transition is already happening in TLS 1.3 implementations and post-quantum standardization efforts from NIST. If you need a quick reference implementation, the GMP library's mpn_prime_next_prime function is solid for arbitrary-precision work. For smaller-scale applications, a precomputed prime table up to 2^16 combined with Miller-Rabin for larger candidates covers most practical needs without external dependencies. The whole pipeline from random seed to verified prime typically takes under 50 milliseconds on a modern CPU for a 2048-bit key, and under a millisecond for 256-bit primes used in ECC.
The takeaway is that primes are straightforward to define and perfectly adequate for most applications, but the edge cases where they cause problems are the ones that keep engineers up at night. Get the generation right, verify with proper tests, and don't treat them as a magic bullet when a different mathematical structure would serve you better.