Regulation Is Just Bureaucracy With Teeth
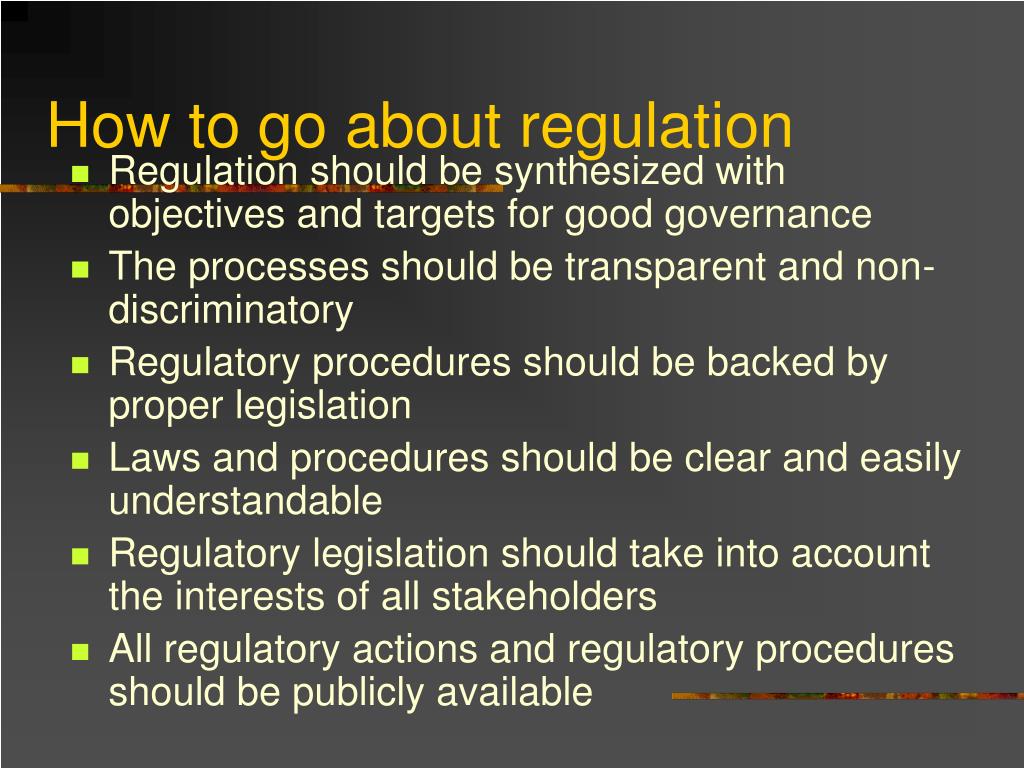
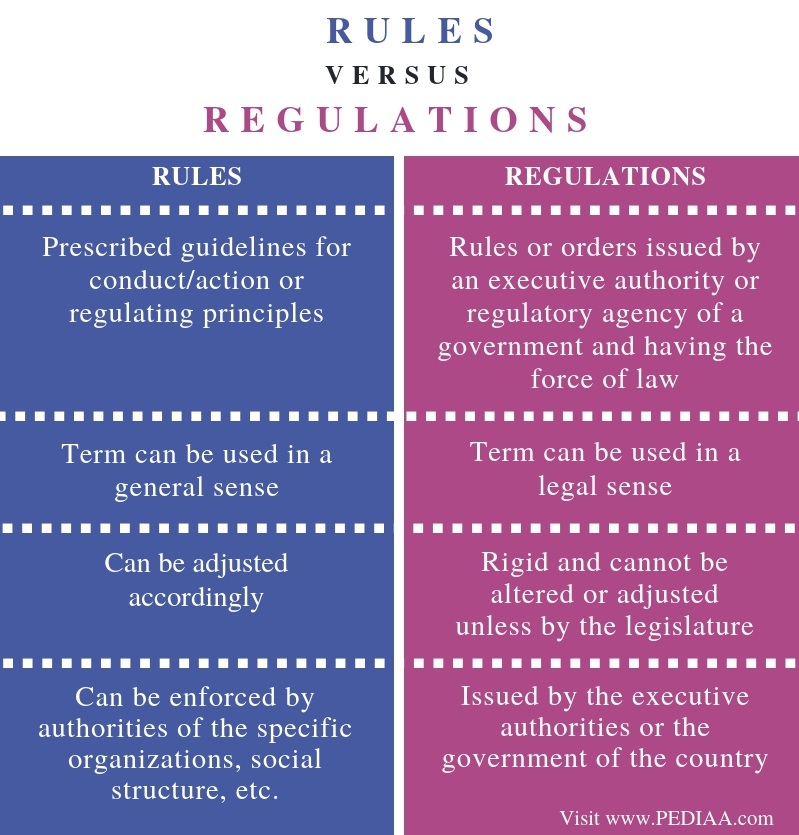
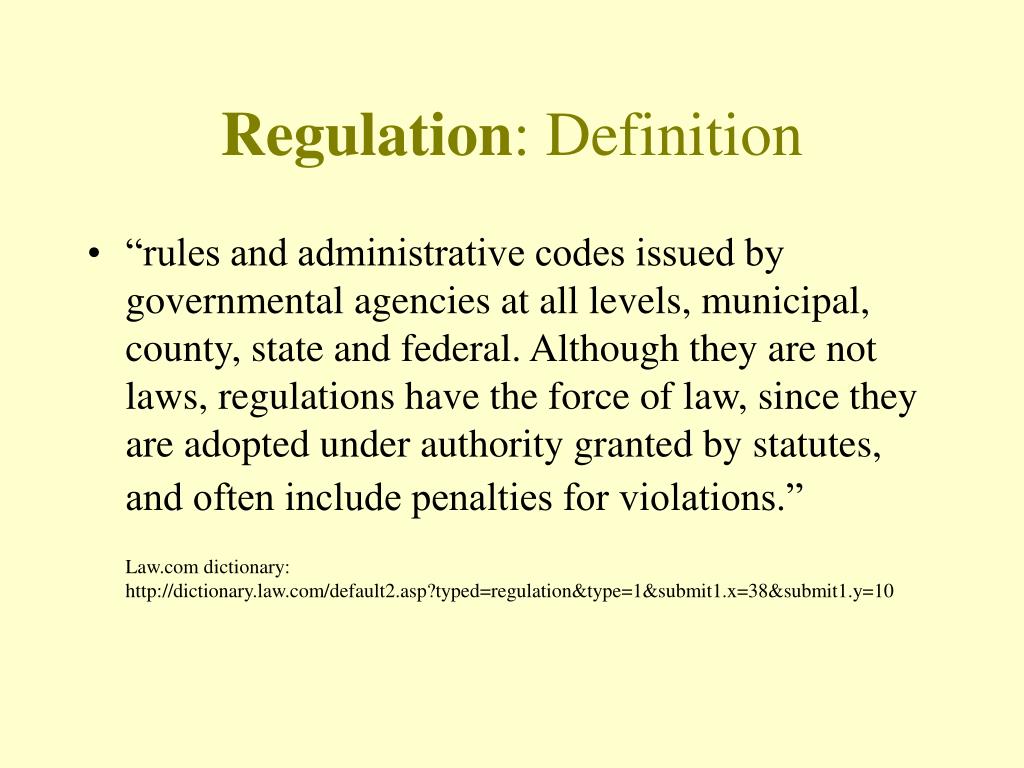
Regulation means rules imposed by an authority that you are legally obligated to follow, and if you don't, there are consequences ranging from fines to criminal liability. That is the textbook answer. The real answer is messier and involves understanding which authority applies, when it applies, and how to actually comply without spending your entire budget on consultants. I spent years dealing with compliance frameworks across fintech and data handling, and the thing nobody tells you is that regulation is not a single thing. It is a layered system of overlapping jurisdictions, interpretations, and enforcement priorities. GDPR is not the same as CCPA, even though they cover similar ground. PCI-DSS exists separately from SOC 2. They reference each other sometimes, contradict each other often, and neither covers everything you think they should.
What Does Regulation Mean in Practice
In practice, regulation means mapping your operations against every applicable framework, finding the gaps, and documenting how you close them. The mapping step is where most organizations fail. I once worked with a company that was fully compliant with PCI-DSS level 1 but completely blind to NIS2 requirements because their compliance team operated in a silo. The IT security team handled one framework, legal handled another, and nobody checked whether the overlap created a conflict. We found it three weeks before an audit when I was digging through network architecture docs to understand a latency issue. The workaround was straightforward: a cross-functional compliance matrix that linked every control requirement to an owner and a date, updated monthly. It cut our audit prep from six weeks to about ten days. The counter-intuitive part is that having more compliance certifications does not necessarily make you more compliant. SOC 2 Type II and ISO 27001 both aim at security controls, but they measure different things. SOC 2 is a attestation by a CPA firm about whether your controls operated effectively over a period of time. ISO 27001 is a certification of your information security management system against a standard. Passing one tells you nothing about the other. I have seen companies treat a SOC 2 report as a substitute for actual security hygiene. It is not. It is a snapshot of a point in time, prepared by auditors who had limited access and a standard engagement letter. Another thing beginners miss is that regulation is interpretive. The text of a rule is only half the story. The enforcement history matters more. When the SEC issued guidance on crypto asset securities in 2023, the actual rule text changed very little from prior statements, but the enforcement actions that followed it changed everything about how companies approached compliance. The risk was not in what the rule said but in how aggressively regulators chose to apply it. I had clients who ignored the guidance because it was not binding law, and then got hit with a enforcement action six months later. The cost of ignoring interpretive signals is always higher than the cost of addressing them upfront.
There are real downsides to treating regulation as a checkbox exercise. The biggest one is that compliance frameworks are static and threats are dynamic. Your SOC 2 report from last quarter does not protect you from a zero-day exploit that emerged this week. The framework gives you structure, but it does not give you resilience. I have seen organizations that passed every audit and still suffered a major breach because their controls were designed for the framework, not for the threat landscape. The workaround is to layer actual threat modeling on top of the compliance structure, not treat them as the same thing. Another limitation is cost scaling. Small teams with limited budgets can comply with lighter frameworks like SOC 2 Type I or ISO 27001 at a reasonable cost. But once you move into financial services or healthcare, the requirements compound. HIPAA plus state breach notification laws plus GDPR if you have any EU customers. The compliance overhead grows non-linearly, and by the time you add PCI-DSS on top of all of that, you are looking at a full-time compliance function just to stay current. There is no shortcut around this. The only mitigation is prioritization: focus on the frameworks your customers and regulators actually care about, not every framework that exists. If you are starting from scratch, do not try to comply with everything at once. Pick the framework your primary customers require, build it properly, document everything, and then layer the next one. Attempting parallel compliance on three frameworks simultaneously usually results in shallow compliance on all three and a lot of wasted money. I have watched two startups burn through their Series A on compliance overhead before they had product-market fit. Neither of them survived to face the audits they were preparing for.
Get the Full Details
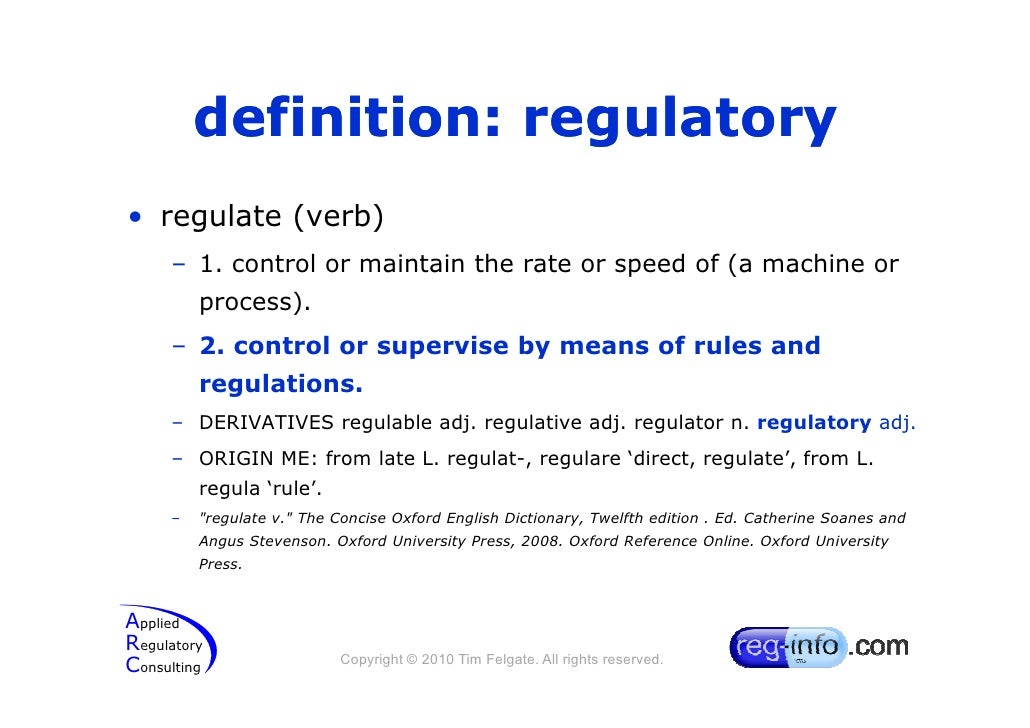
The bottom line is that regulation means living under a system of enforced rules that will be interpreted differently by different authorities at different times. The goal is not perfect compliance, which does not exist, but documented, demonstrable effort that holds up when someone with a grudge and a subpoena comes knocking. That requires ongoing work, not a one-time project.