The Thing Nobody Explains Properly
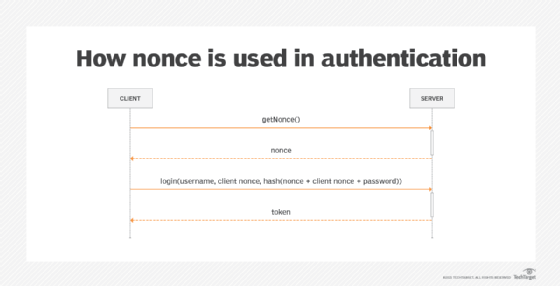
A nonce is just a number used once. That's the entire definition. It gets thrown into cryptographic operations so the same input never produces the same output twice. People overcomplicate it because the applications are broad, but the concept itself is straightforward. It shows up in three main places: cryptocurrency mining, authentication systems, and cryptographic hashing. In Bitcoin mining, miners adjust the nonce field in the block header until the resulting hash falls below the target difficulty. Each attempt changes the input by exactly one value, which completely reshuffles the hash output. That's why mining is essentially guessing numbers at high speed. The network adjusts difficulty roughly every two weeks to keep block times near ten minutes. When difficulty spikes, individual miners burn more electricity for the same expected return. I watched a small pool get squeezed out in 2021 when the hash rate surged and their electricity costs exceeded what they earned per share. They shut down within a month. In authentication, a nonce prevents replay attacks. You generate a random value, send it to the client, and the client includes it in the response. If an attacker captures that response and replays it later, the server sees the nonce is already used and rejects it. The nonce typically has a short TTL, usually somewhere between five and fifteen minutes. This is standard practice in OAuth flows and challenge-response systems. It's also how TLS session resumption works at a basic level.
How It Actually Works Under the Hood
When you're implementing a nonce system, the critical detail is uniqueness and unpredictability. A predictable nonce destroys the security property you're trying to achieve. I once audited a payment gateway where the developer used a sequential counter as the nonce instead of a cryptographically secure random generator. An attacker who saw two consecutive requests could predict the next nonce and forge authenticated transactions. We replaced it with os.random_bytes and added a timestamp window check. That patched the vulnerability without changing the rest of the flow. For mining nonces specifically, the 32-bit field limits you to roughly four billion attempts per block header configuration. Modern ASICs evaluate billions of nonces per second, so you exhaust that space in milliseconds. When you hit the limit, you modify the coinbase transaction or the extra nonce field in the Merkle tree and start the counter over again. This is why miners run thousands of parallel threads across different block header variants. The hardware is optimized for SHA-256, not for smart logic.
Pitfalls That Cost Me Time
Storing nonces in Redis works well until your cluster splits during a network partition. I had a situation where valid nonces disappeared from one shard and reappeared on another after reconciliation. Requests that should have been accepted got rejected because the server couldn't find the nonce in its local cache. The fix was using a consistent hashing strategy with replication factor of at least three, plus a fallback database lookup that checked multiple nodes before giving up. It added about twelve milliseconds of latency on average, which was acceptable for the reliability gain. Another issue people miss is nonce reuse in distributed systems. If two servers generate nonces independently without coordination, they can produce the same value. In my experience, this causes silent data corruption rather than obvious failures. The system appears to work until you query the logs weeks later and find identical transaction IDs appearing in different contexts. The workaround is either a centralized nonce service or per-server prefix concatenation with a unique identifier. Both approaches add complexity. There's no clean solution that doesn't require some architectural decision upfront.
Get the Full Details

When Nonces Fail Completely
Nonces don't solve everything. They won't protect against timing side-channel attacks where an attacker measures response time differences to infer information. They won't help if your random number generator is weak. They provide no protection against man-in-the-middle attacks unless combined with proper certificate validation and encryption. And they introduce their own attack surface through storage exhaustion, since every issued nonce needs to be tracked until it expires. If you need something stronger than nonce-based replay protection, consider moving to mutual TLS with short-lived certificates or adopting a token-binding protocol like RFC 8705. These are more complex to implement but don't suffer from the same storage and coordination problems. For most applications though, a well-implemented nonce with proper expiration and secure random generation is sufficient. Just make sure you test edge cases around clock skew, server restarts, and concurrent request handling before you ship anything to production.