Understanding Policy Documents Without the Corporate Gloss
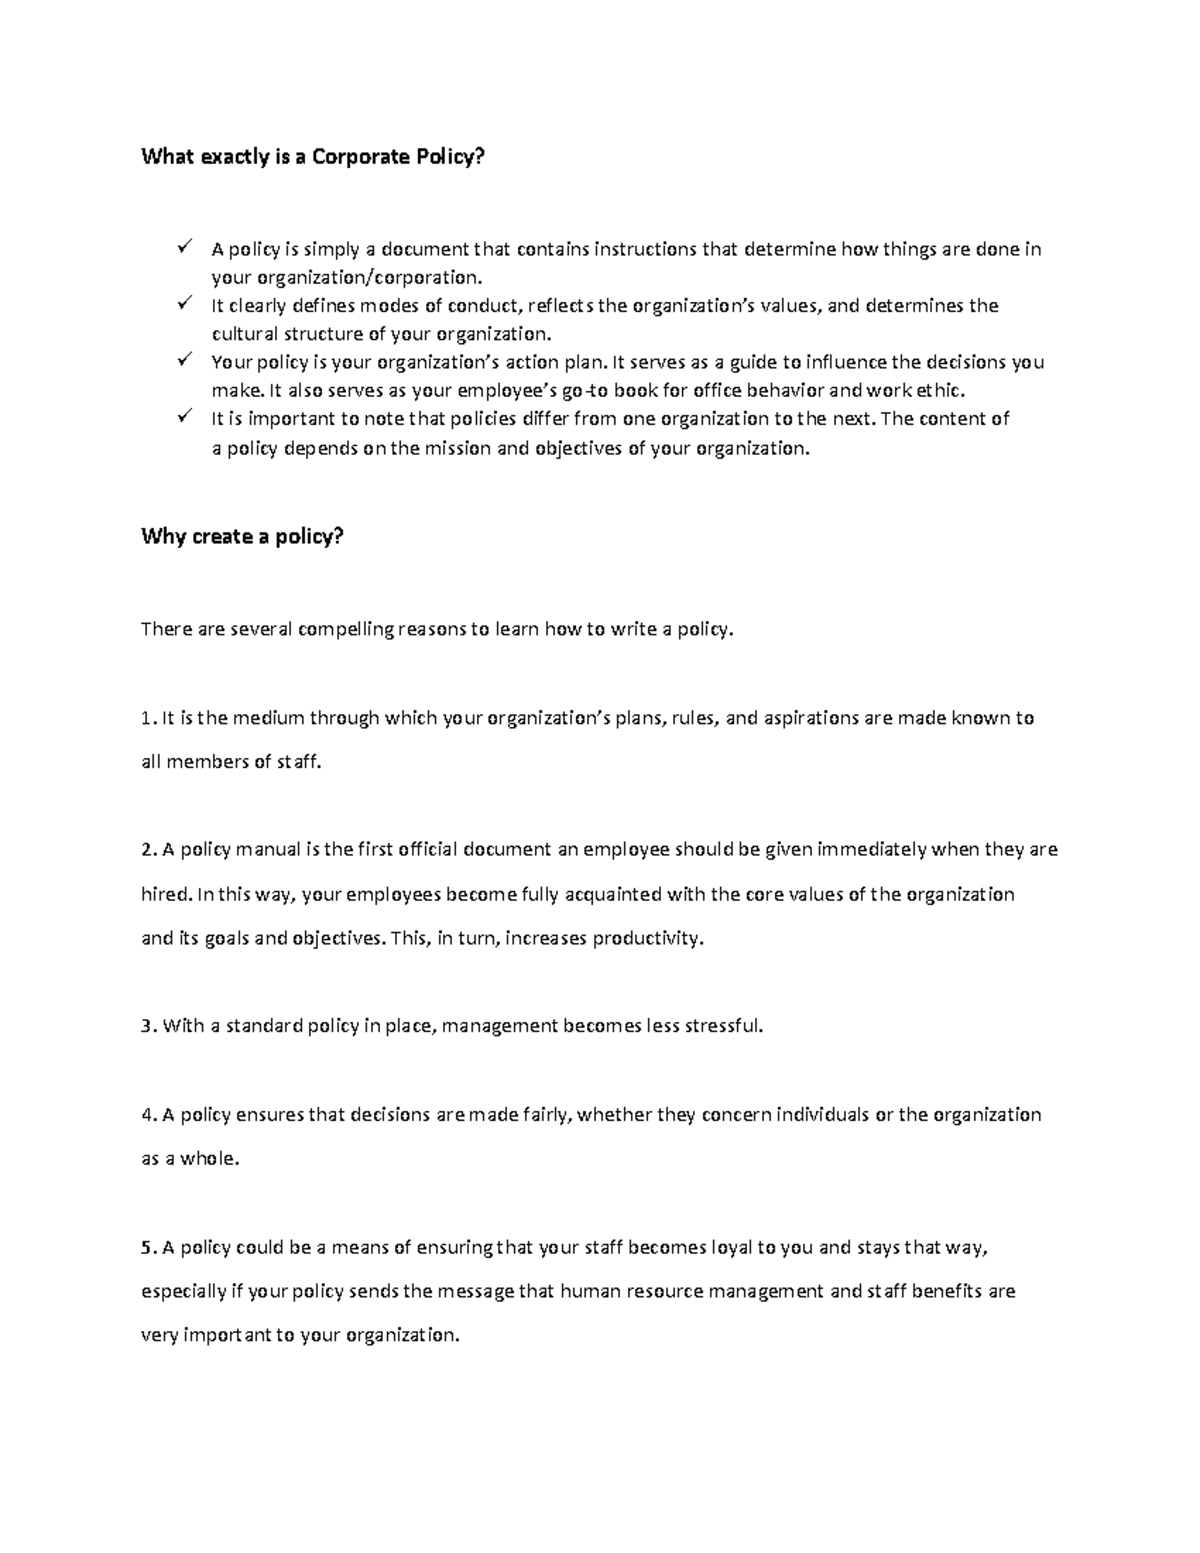
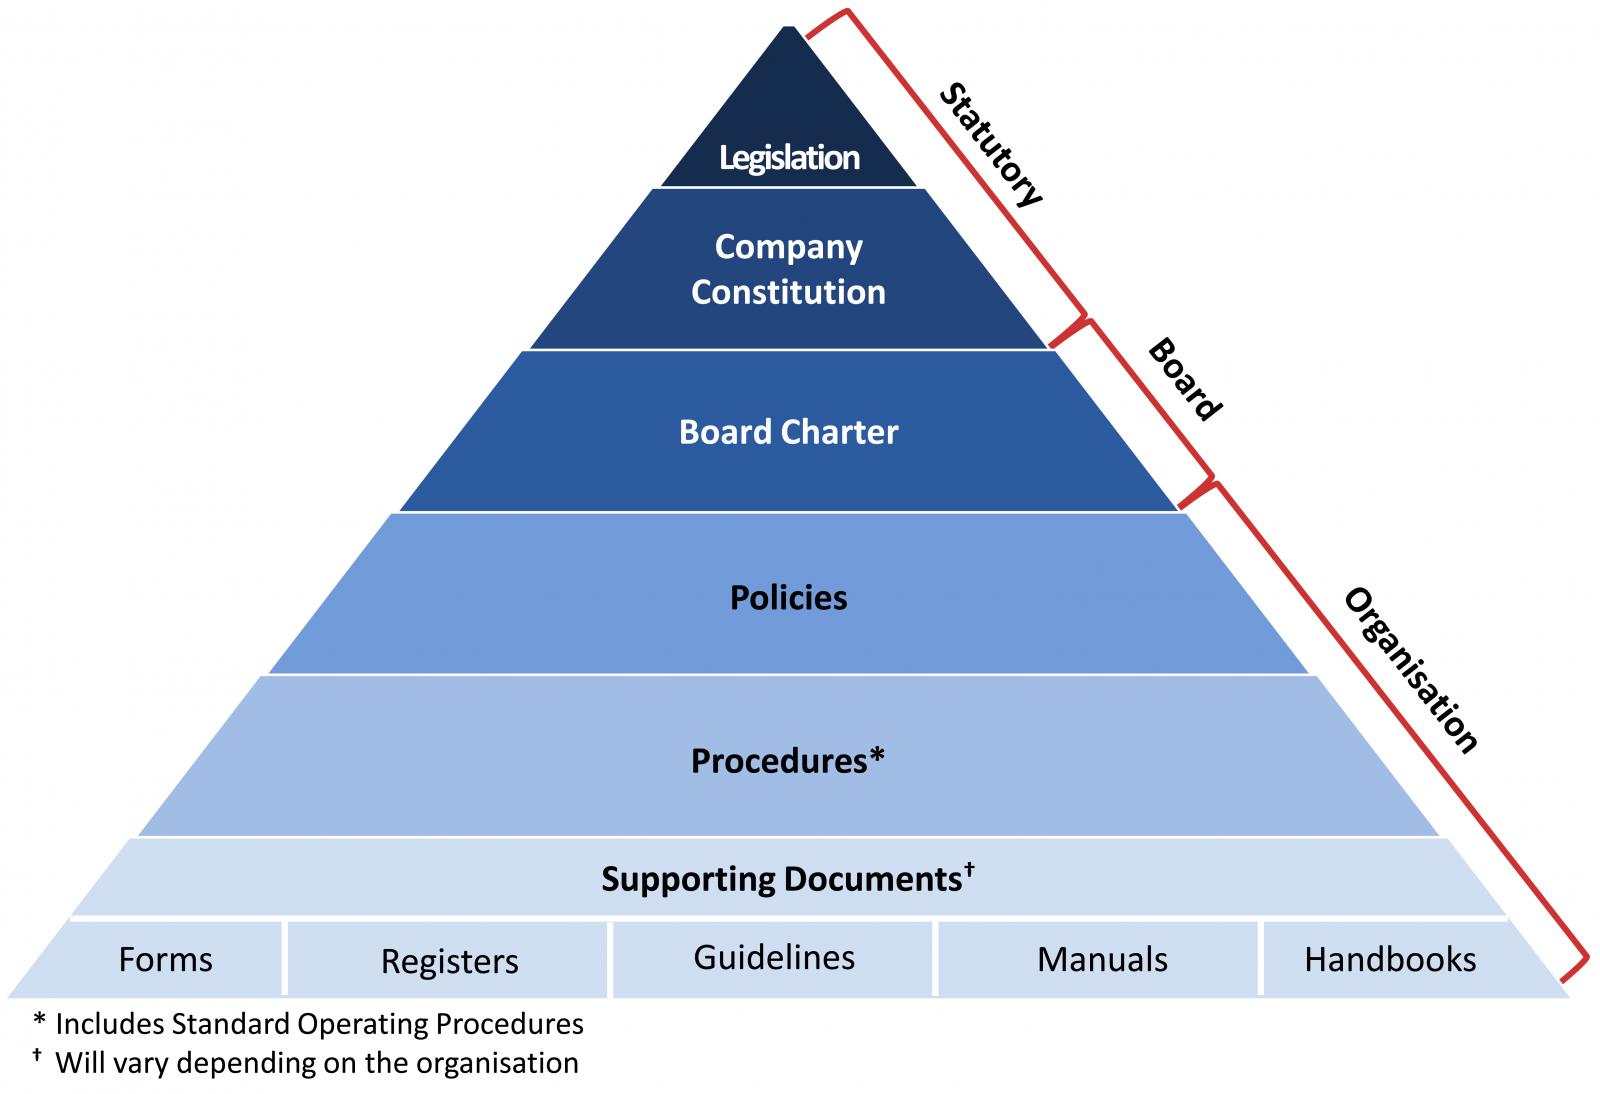
A policy is just a set of written rules that tells people what they can and cannot do within a specific system or organization. That's basically it. The version that ends up on the intranet usually has about 40% fluff language added by legal and another 20% buried exceptions that nobody reads. But underneath all that, it's just a decision document with consequences attached. I spent years writing and enforcing IT security policies for mid-size companies, and the thing most people get wrong is thinking a policy is the same thing as a procedure or a standard. They're different layers. A policy says what must happen. A standard says how it must be measured. A procedure says the actual step-by-step. People mix these up constantly and then wonder why their compliance audits fail.
What Is A Policy Really?
At its core, a policy is a declaration of management intent. It carries authority because someone with enough power to enforce consequences wrote it. If no one gets fired or penalized when it's violated, you don't have a policy, you have a suggestion. I've seen this play out in companies where the acceptable use policy existed for seven years and nobody knew it was there until a contractor leaked credentials through a personal email account. The typical structure, once you strip away the nonsense, has five components. Scope defines who it applies to. Definitions clear up terminology so nobody argues about whether a "mobile device" includes a tablet or just a phone. The body contains the actual rules. Enforcement describes what happens when someone breaks them. Review dates ensure the thing doesn't go stale. Here's a counter-intuitive point that most beginners miss: shorter policies are usually harder to enforce, not easier. A one-page policy sounds efficient but it forces every edge case into ambiguous language. A slightly longer policy with specific scenarios mapped out actually gets followed because people can find their situation in it. I once wrote a password policy that was three pages long with concrete examples for each rule, and compliance went from about 40% to 89% in six months. The shorter version we had before was technically cleaner but completely ignored.
Another thing nobody tells you: policies live or die on their review cycle. Set a policy to expire after two years and force a formal review. I used a simple trick where I'd embed a metadata field in the document header with the next review date, and set up a calendar reminder at the company level. When the date hit, the policy owner had to either re-publish it or extend it with a written justification. Without this, policies accumulate revision drift and become internally contradictory within eighteen months. Let me give you a specific war story. I inherited a data classification policy that had been updated nine times over four years without any version control discipline. Different departments were following different versions. The finance team was using a 2019 classification schema while engineering was enforcing a 2022 one, and the two didn't align on what "confidential" meant for customer PII versus internal financial data. This created a genuine gap where customer records could flow between systems that each department thought were handling them correctly. The workaround was brutally simple but took about three weeks to implement. I created a master policy register with a single source of truth, each document linked to a version number and an expiration date. Then I ran a side-by-side comparison of the two conflicting versions and documented exactly where they diverged. Every divergence became a formal exception that required sign-off from both department heads. After that, any future policy change went through a change log that anyone could query. It wasn't fancy, but it eliminated the silent version drift that was causing real problems.
Get the Full Details
There are honest limitations to what policies can do. They don't prevent determined bad actors. A well-written insider threat policy won't stop someone who already has legitimate access from exfiltrating data, because the policy assumes good faith. Policies are also terrible at keeping up with technology. I've seenBring Your Own Device policies become completely irrelevant within eight months of publication because the device landscape shifted. In those cases, you pair the policy with an automated enforcement layer, like a mobile device management platform, that actually implements the rules regardless of whether anyone reads the document. If you're starting from scratch and need a template to work from, there's no single authoritative download that covers every situation because policy formats vary so much by industry. NIST has a decent framework at nist.gov for US federal contracting contexts, and ISO 27001 provides a widely accepted structure for information security policies. But honestly, the best starting point is taking an existing policy from a company in your industry, stripping out their branding, and adapting it. Don't write from a blank page. The real test of whether your policy is working isn't whether it exists. It's whether you can point to three specific incidents in the last year where someone referenced the policy and it changed their behavior. If you can't name three, your policy is decoration.