The Basics, Then The Grind
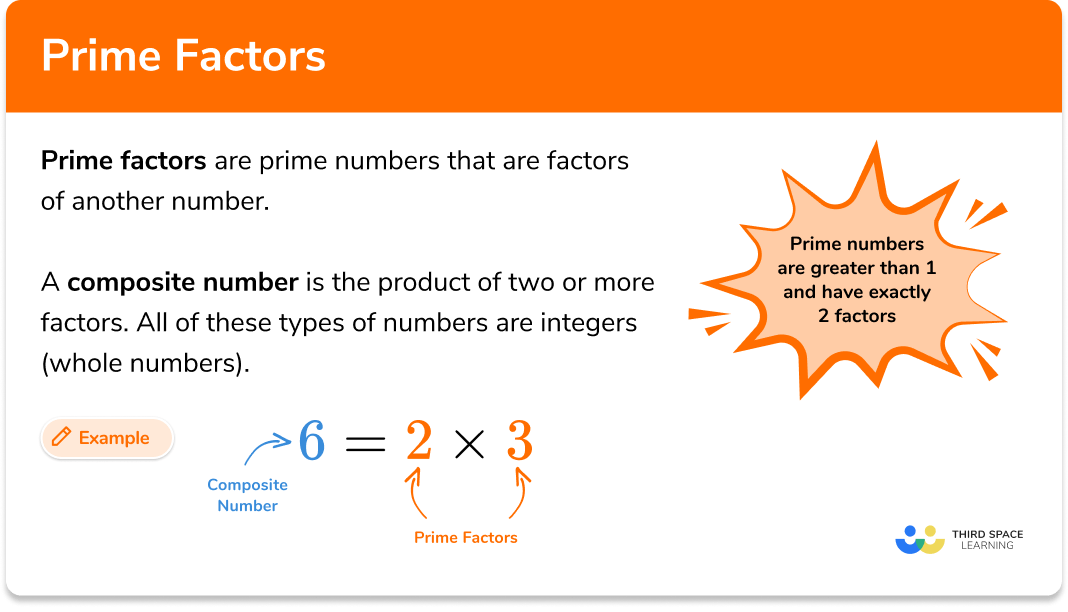
A prime factor is a factor of a number that is also prime. That's the textbook answer and it's not wrong, but it doesn't really tell you how you'll actually use this stuff. When I first started dealing with this, I kept treating it like a pure math exercise. It's not. It's a tool for breaking things apart, and that distinction matters when you're working with actual numbers, not just homework problems. Take 12, for instance. The prime factors are 2 and 3 because 2 times 2 times 3 equals 12 and both 2 and 3 are prime. That part is straightforward. The hard part comes when the numbers get big. Really big. And I don't mean calculator-big. I'm talking about numbers that make standard trial division feel like watching paint dry.
What Is A Prime Factor and Why It Matters More Than You Think
Here's where people usually trip up. They learn the definition, they factor a few small numbers, and then they hit a wall when something like 12,839 shows up and they have no idea where to start. The thing nobody tells you is that most of your time will be spent figuring out whether a number is actually prime or not, not finding the factors. I was working on a cryptography project a few years back and I ran into this number that I knew had to have small prime factors but couldn't crack it with any standard approach. Trial division up to the square root was viable in theory but in practice it was going to take hours on whatever hardware I had access to at the time. So I switched tactics and used Pollard's rho algorithm instead. It's not the most elegant method but it got me the answer in about ten minutes instead of however long trial division would've taken. I wish someone had just shown me that earlier.
How To Actually Find Them
Start with trial division because it works fine for small numbers. Divide by 2, then 3, then 5, then 7 and keep going up. Every time you divide evenly, write down that divisor and keep dividing the result. Repeat until you can't divide anymore. The divisors you wrote down are your prime factors. Here's the catch: trial division gets expensive fast. If you're factoring a number with a large prime factor, you're checking every single divisor up to the square root of that number. For a 20-digit number, that's millions of checks. I once spent an afternoon on a problem where the number I was factoring had a prime factor over 100,000 and I only realized it after I'd already run through every divisor below that. Not efficient. Not by any measure. For larger numbers, you want something smarter. Elliptic curve factorization is the go-to if you're comfortable with the math, and it's significantly faster than trial division for numbers in the right range. The downside is that it's harder to implement from scratch and there are edge cases where it stalls out. I've seen it fail on certain semiprimes that were specifically constructed to be resistant, though those are pretty rare in practice.
Get the Full Details
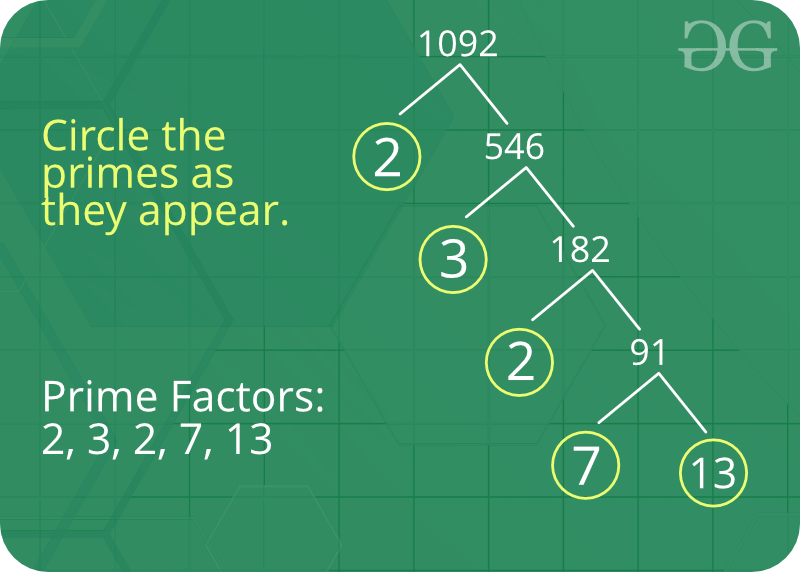
The Messy Parts
One thing that surprises beginners is that not all numbers break down the same way. Some numbers have repeated prime factors like 8 which is 2 times 2 times 2. Others have all distinct factors. And some numbers, like 1, have no prime factors at all. The number 1 is neither prime nor composite and it doesn't have a prime factorization. That's not a trick question, it's just how the definition works and it matters more than you'd expect when you're writing code or building algorithms. Another thing: the fundamental theorem of arithmetic says every number has exactly one prime factorization. Unique. Period. That sounds nice on paper but it also means you can't just find any set of factors and call it done. Your result has to match the unique factorization or it's wrong. I learned that the hard way when I was double-checking someone else's work and I accidentally accepted a factorization that had the right product but included a non-prime factor. The math was technically correct but the answer was useless.
When This Approach Falls Apart
If you're working with extremely large numbers, like the kind used in modern encryption, none of the methods I've mentioned are going to be sufficient on their own. We're talking numbers with hundreds of digits where even the best general-purpose factorization algorithms become impractical. That's the whole reason RSA exists and it's something you need to be aware of if you're working in this space. For most practical purposes though, the combination of trial division for small factors and Pollard's rho or elliptic curve methods for larger ones will cover whatever you're likely to encounter. I haven't needed anything more sophisticated yet and I've been working with this stuff for long enough that I've probably seen most common cases.