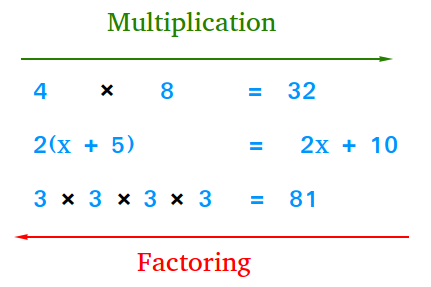
Factoring in math is just breaking things apart until they can't be broken any further.
The practical method is to start with whatever number or expression you're given and test divisors from smallest to largest. For numbers, you divide by 2, then 3, then 5, and keep going until the remainder is 1. For algebraic expressions, you look for common terms first, then check whether it fits a pattern like difference of squares or a quadratic that splits into two binomials. You write the result as a product, not a sum. That's the whole operation. I've been working with this stuff long enough to know that most people mess it up because they skip the first step. They jump straight to memorized patterns without checking if there's a greatest common factor hiding in plain sight. I had a student last year who was factoring 12x³ + 18x² and went straight to trying to find two numbers that multiply to 216 and add to 18, completely missing that both terms share a 6x². Took him twelve minutes to find it after I asked what they had in common.
What Is Factoring In Math
At its core, factoring is expressing a mathematical object as a product of simpler objects. In arithmetic, that means writing a composite number as a multiplication of primes. In algebra, it means rewriting a polynomial as a multiplication of lower-degree polynomials. The goal is always the same: reach a point where none of the factors can be decomposed further using the rules you're working within. There are some things about factoring that textbooks don't make clear. One is that factoring is not unique unless you specify an ordering and a domain. Over the integers, prime factorization is unique by the fundamental theorem of arithmetic, but over other rings that guarantee doesn't hold. I ran into this when a colleague was working with Gaussian integers and got genuinely confused why his factorization didn't match mine. We were both right. He was just using different units. Another thing people miss is that finding a factor doesn't require finding all factors. If you're testing whether a large number is prime and you find any divisor between 2 and the square root, you're done. The number is composite. You don't need the complete factorization to answer that question. This is the basis for most primality testing in practice, even though full factorization remains computationally expensive for sufficiently large numbers. RSA encryption depends on exactly this asymmetry.
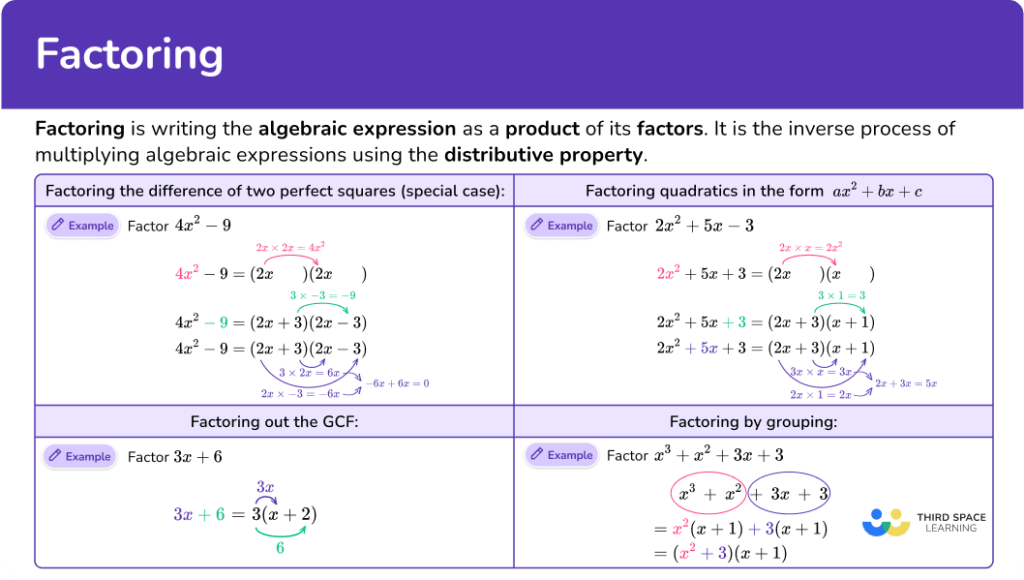
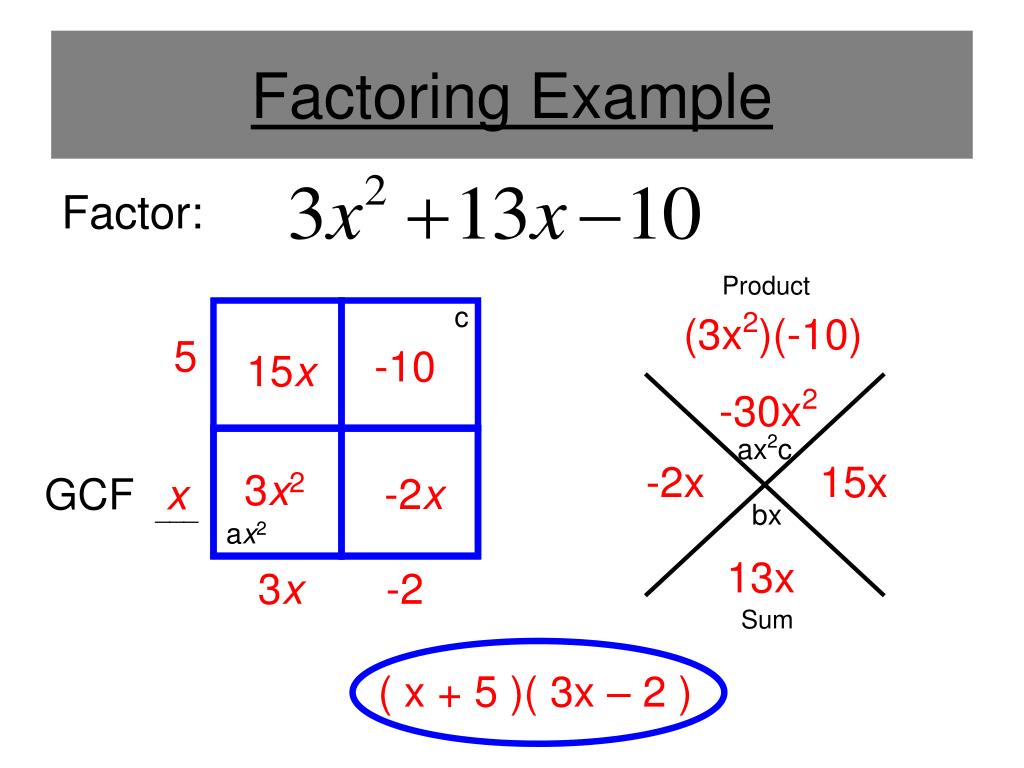
When factoring polynomials, the most useful tool after extracting the GCF is recognizing standard forms. The difference of squares pattern is ax² - b² = (a - b)(a + b). The sum and difference of cubes follow their own patterns. A quadratic trinomial ax² + bx + c requires finding two numbers that multiply to ac and add to b, then splitting the middle term and grouping. It sounds mechanical and it is. The trick is speed. You should be able to spot these in under ten seconds during a test. Here's a realistic edge case I encountered recently. I was factoring a polynomial over a finite field and kept getting results that looked correct but weren't. The issue was that in modular arithmetic, some numbers that seem irreducible over the integers actually factor. For example, x² + 1 is irreducible over the reals, but modulo 5 it factors as (x + 2)(x + 3). This catches people off guard when they're doing competitive math or coding problems that involve polynomial factorization over finite fields. The workaround is to always verify your factors by multiplying them back, and to remember that the field you're working in changes what's possible. There are limitations to factoring that no one advertises. It doesn't always work. Some polynomials are irreducible by design. You'll spend time trying to factor something that simply cannot be factored over the rationals, and you won't know that until you've exhausted the methods. The rational root theorem helps here, but it only gives you candidates. Testing each one takes effort. For polynomials of degree five or higher, there is no general algebraic solution for roots, and factoring is equally hopeless without special structure.
Get the Full Details
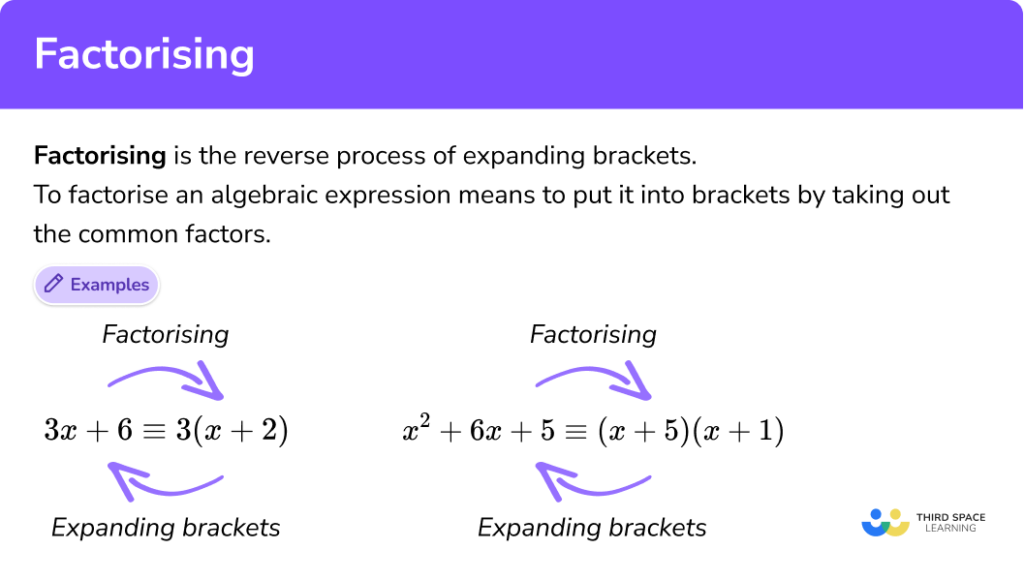
In computational contexts, integer factorization is the hard problem. The best known classical algorithm, the general number field sieve, runs in sub-exponential time but is still impractical for numbers with more than about 250 digits. This is why factoring has real-world consequences beyond homework. Shor's algorithm on a sufficiently powerful quantum computer would make it efficient, which is why people worry about current encryption standards. For everyday use, the workflow is straightforward. Identify the type of object you're factoring. Check for a greatest common factor. Test for standard patterns. If those fail, use systematic methods like the AC method for quadratics or trial division for integers. Always verify by expanding your factors. The verification step takes five seconds and prevents maybe ninety percent of errors.