Primes Are Just One Of Those Things You Need To Get Your Head Around Early
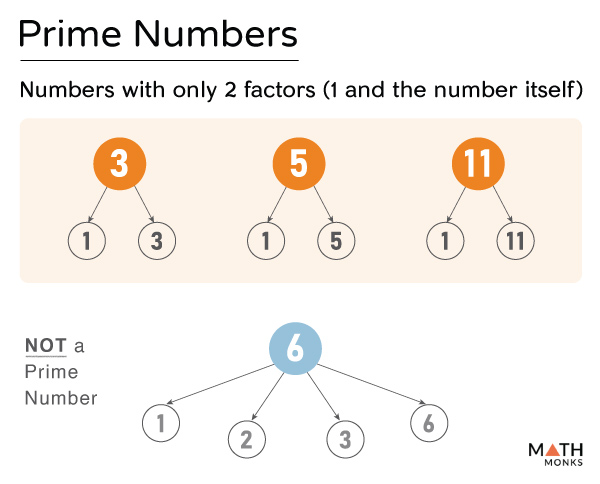
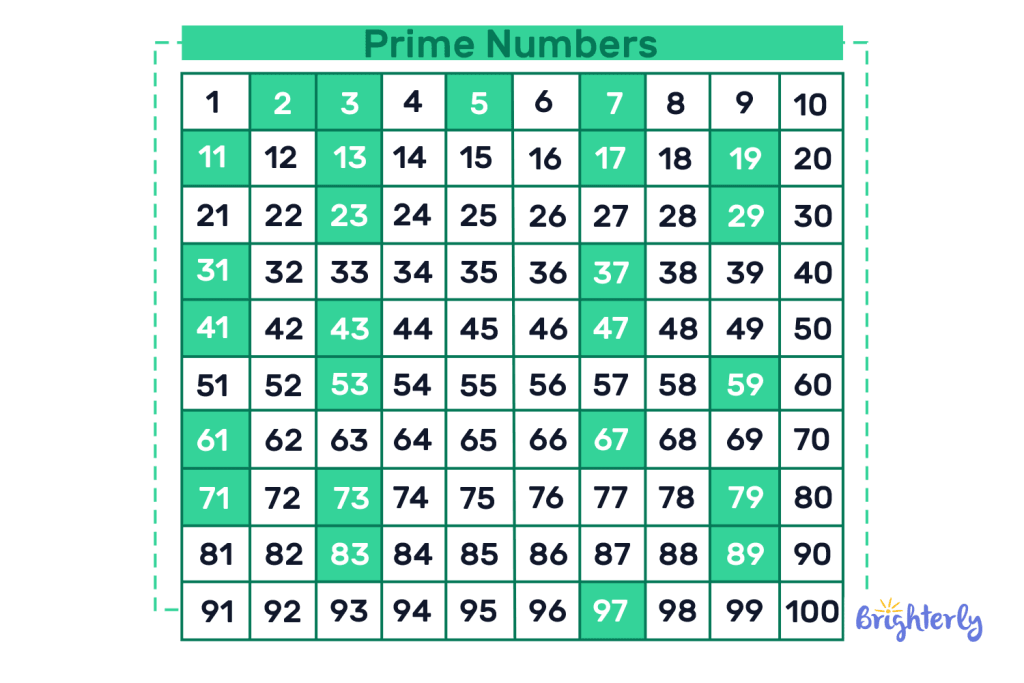
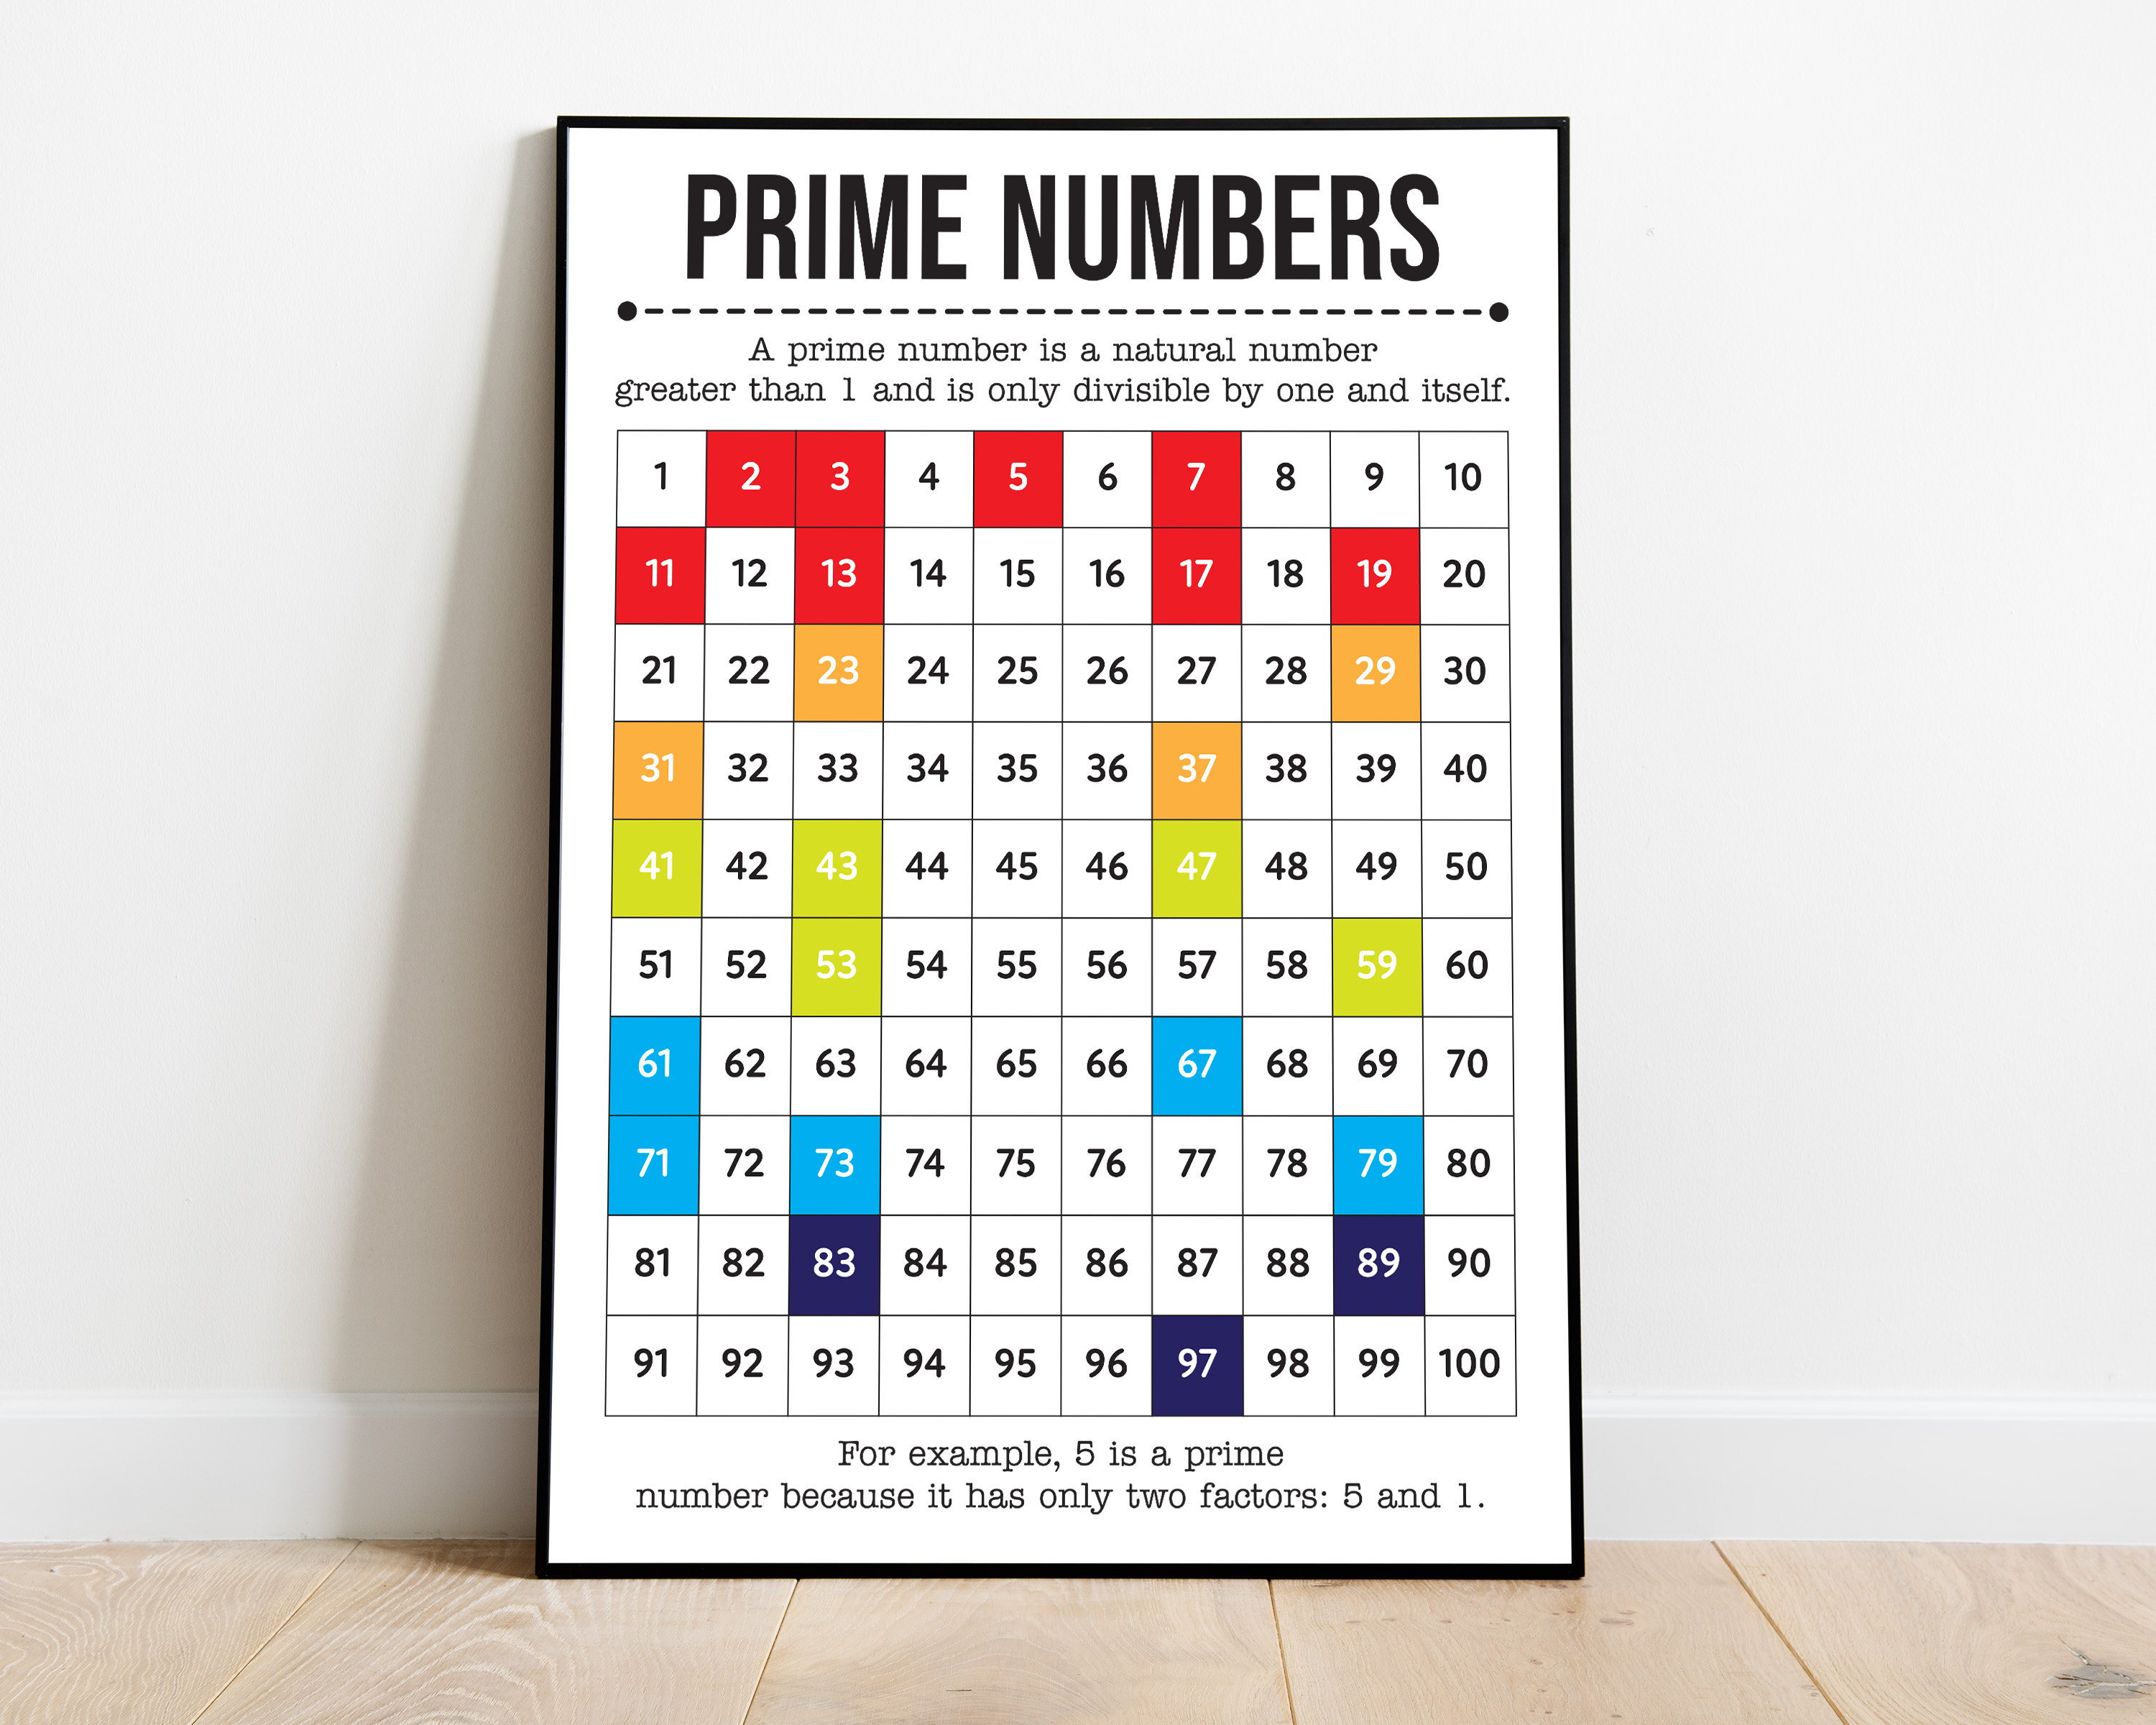
Prime numbers are whole numbers greater than 1 that have no divisors other than 1 and themselves. That is the textbook definition, and it is also the only definition most people will ever need. But if you have done any work that involves cryptography, number theory, or just building anything that relies on factorization, you quickly learn that the simple definition hides a lot of messy reality. I spent several years working on a project where we needed to generate large primes for RSA key pairs. The naive approach — just counting up from 2 and testing each number by trial division — sounds fine until you try it with a 2048-bit number. It will not finish in your lifetime. The workaround was switching to a Miller-Rabin probabilistic primality test. You pick a random odd number, run it through about 20 rounds of testing with different bases, and if it passes every single one, you treat it as prime with a false positive rate below 1 in 4^20. For most practical purposes, that is close enough. The thing about primes that catches people off guard is how unevenly they are distributed. There is no pattern you can write down and reliably predict the next one. The gaps between consecutive primes get larger as numbers grow, but they do not grow in any smooth or predictable way. I once had a bug in a system where we were generating primes for a hashing function, and the hash collisions spiked unexpectedly because we had been using a biased selection method that favored smaller primes. Once I switched to a uniform distribution across the full range, the collision rate dropped to what it should have been.
There are some truths about primes that feel wrong at first. One of them is that 1 is not a prime number. People argue about this constantly, but the reason is straightforward: if you include 1, the fundamental theorem of arithmetic falls apart. Every number would have infinitely many prime factorizations because you could insert as many 1s as you wanted. The math community decided decades ago that excluding 1 was cleaner, and it was the right call. Another counter-intuitive thing is that there are infinitely many primes, but they get scarce very quickly. The prime number theorem tells you that the density of primes near a number n is roughly 1 over the natural log of n. So around a million, about 1 in every 14 numbers is prime. Around a trillion, it is closer to 1 in 23. This matters if you are writing code that searches for primes — the further out you go, the more numbers you have to check before finding the next one. Here is a practical method for finding primes in the range most people actually care about:
If you need primes up to maybe 10 million, the Sieve of Eratosthenes is still the tool to reach for. It works by marking off multiples of each prime starting from 2. You write down all numbers from 2 to your limit, then cross out all multiples of 2, then all multiples of 3, then 5, and so on. Any number that remains unmarked at the end is prime. The time complexity is about O(n log log n), which makes it fast enough for everyday use on a modern machine. I used this exact approach in a competitive programming problem once and it generated the first million primes in under half a second on a standard laptop. But sieve methods hit a wall when your numbers get big. Memory usage scales linearly with your upper bound, and if you are trying to sieve past a few billion, you will run into RAM constraints quickly. That is when you move to segmented sieves or probabilistic tests. A segmented sieve breaks your range into small chunks that fit in cache, which keeps memory use manageable. It is the standard approach in libraries like GMP when you need to find primes in a large interval without allocating a massive array. The main pitfall I see people trip over is assuming that checking divisibility up to the square root of n is fast enough for anything larger than small numbers. It is not. For a 64-bit number, the square root is about 4 billion. Even a optimized trial division loop checking only odd numbers would take on the order of seconds per candidate, and you might be testing thousands of candidates before finding a prime. That is why probabilistic tests are the industry standard for anything above a few thousand bits.
Get the Full Details
Another common mistake is treating probabilistic primality tests as if they give you certainty. They do not. Miller-Rabin has a known error bound, and while it is astronomically small with enough rounds, it is not zero. For cryptographic applications, this is usually fine because the alternative — proving primality deterministically — is dramatically slower. The AKS primality test, which is deterministic and runs in polynomial time, is theoretically important but practically useless for real-world key generation because its constants are so large that it is orders of magnitude slower than Miller-Rabin for any number size you would actually encounter. If you are just learning about this stuff and want to experiment, there are a few freely available tools. Python's sympy library has a primerange function that implements a sieve and lets you generate all primes up to a limit. It is not the fastest thing ever but it is good for learning and small-scale work. For larger numbers, the openssl command line tool has a prime generation option that uses a solid implementation of probabilistic testing. And if you are working in C or C++, GMP is the library to use. The limits of prime-based systems are worth understanding too. RSA key security depends entirely on the fact that factoring the product of two large primes is hard. If someone finds a fast factoring algorithm — which is not known today but remains an open problem — everything built on that assumption becomes vulnerable. Post-quantum cryptography is largely a response to this uncertainty, with lattice-based and code-based schemes being proposed as alternatives that do not rely on prime factorization at all. It is a reminder that primes are a tool, not a permanent foundation.
For everyday use, the takeaway is simpler. If you need primes up to a few million, use a sieve. If you need primes for cryptography or large-number work, use Miller-Rabin with a reasonable number of rounds. Do not try to write your own trial division for anything beyond educational purposes. And keep in mind that the distribution of primes is irregular enough that any shortcut or heuristic will eventually surprise you if you push it far enough.