The Physical Reality of Routing and Switching
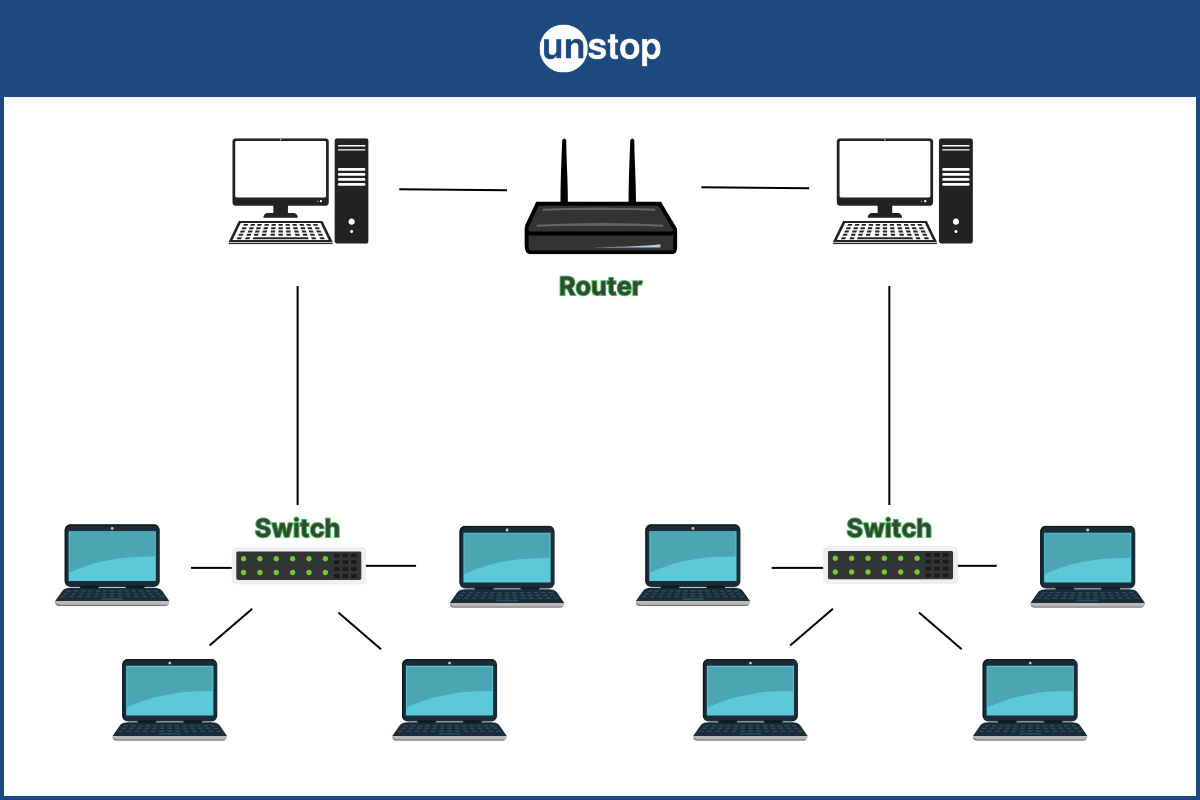
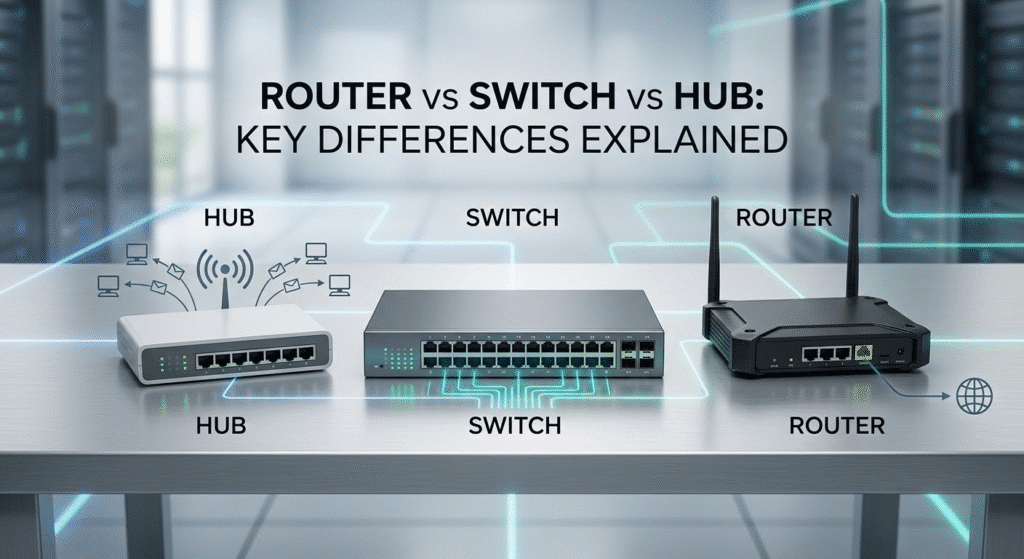
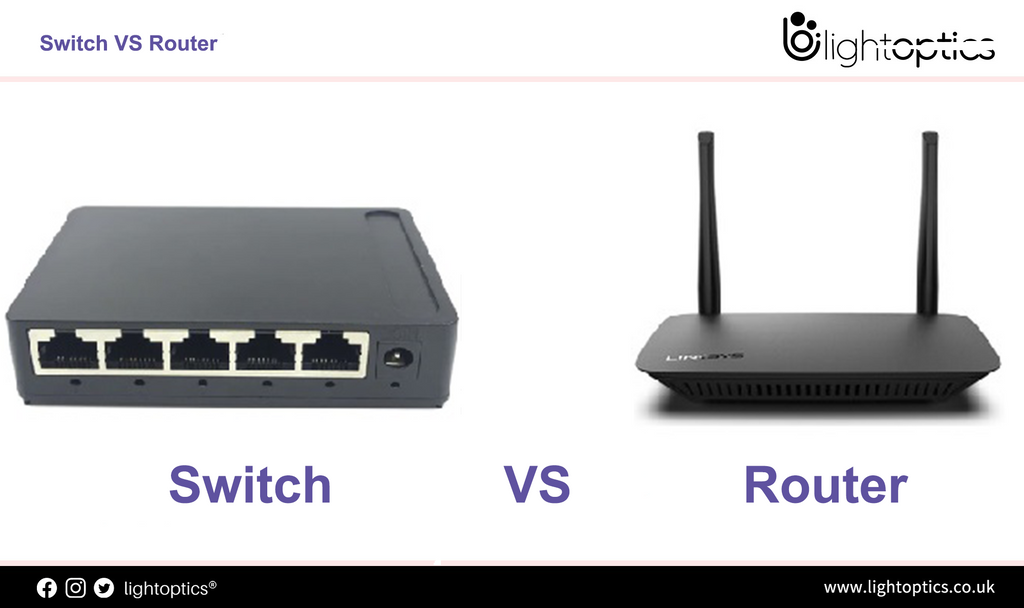
A switch moves frames between devices on the same local network. It learns MAC addresses by watching traffic, then forwards frames only to the port where the destination device lives. A router moves packets between different networks. It reads IP addresses, consults a routing table, and decides which interface to send traffic out of. That's the basic answer to the question What Is Router And Switch In Networking. I've seen people buy managed switches for reasons that have nothing to do with switching. You'll find them paying $400 for a 24-port L2 switch when the only feature they actually needed was an uplink that didn't drop packets under load. The hardware does exactly what it's supposed to do at that price point. You're paying for web management interfaces and VLAN support you might never configure.
How Switching Actually Works Under the Hood
When a switch receives a frame, it looks at the source MAC address and records it in its forwarding table along with the incoming port and a timestamp. Next time traffic needs to go to that MAC, the switch sends it only out that specific port instead of flooding it everywhere. This is called unicast forwarding and it's what separates a switch from a hub, which broadcasted everything to every port regardless. The forwarding table has an aging timer, typically 300 seconds. If a device stops sending traffic, its entry drops. This matters when you're troubleshooting why a port seems blocked or why devices can't reach each other. I once spent about forty-five minutes debugging what I thought was a faulty cable, only to find the switch had aged out an entry because the connected device went into a deep sleep mode and stopped transmitting for five minutes straight. A simple show mac address-table command would have told me that immediately instead of my multimeter sitting on the desk for an hour. Broadcast domains are another thing people get wrong. Every port on a standard switch is its own collision domain but all ports share the same broadcast domain unless you configure VLANs. A VLAN segments broadcast traffic at layer 2. It doesn't stop broadcasts entirely but it keeps them contained within the logical group. If you run a large flat network with fifty computers and a wireless AP, that AP's broadcast traffic reaches every single wired port. You'll see the effect in ARP requests and DHCP discover messages multiplying across the LAN.
Routing and the Decisions Routers Actually Make
A router connects networks by examining the destination IP in each packet and looking up the best path in its routing table. The routing table can be built manually through static routes or automatically through protocols like OSPF, EIGRP, or BGP depending on your setup. For a home or small office network, you're almost always dealing with a single default route pointing toward your ISP's gateway. The thing nobody tells you about home routers is that the routing function and the switching function live on the same chip in most consumer devices. They're not separate pieces of hardware. The router sits between your WAN and your LAN, performing NAT, DHCP, and firewall functions. The "switch ports" on the back are actually part of a built-in switch chip. Understanding this helps when you hit performance limits. A typical residential router handles maybe 100 to 200 Mbps of NATted throughput before the CPU becomes the bottleneck. Beyond that, adding another physical switch in front of the router's LAN port won't help because the bottleneck is the router's processor, not the switching fabric. I ran into this exact problem at a client's warehouse last year. They had a high-density camera system pushing continuous video back to a central NVR. The router was maxing out its NAT throughput and cameras were dropping frames intermittently. The fix wasn't a better switch. It was bypassing the router's LAN side entirely by configuring the NVR and the camera management server on the same subnet with a dedicated layer 3 switch handling inter-VLAN routing at line rate. That moved the routing work off the commodity device and onto hardware designed for it. Performance went from about 180 Mbps aggregated to nearly 900 Mbps across the camera network.
Get the Full Details

Where the Line Between Switch and Router Gets Blurry
Layer 3 switches exist and they complicate the clean distinction between these two devices. A layer 3 switch can perform both switching and routing functions. It builds a MAC address table like a normal switch and it also maintains routing tables like a router. Inter-VLAN routing on a layer 3 switch happens at hardware speed through ASICs instead of through software on a CPU. This is why enterprises prefer them for internal routing between VLANs. The practical implication is straightforward. If you need to route between VLANs inside your network and you want wire-speed performance, a layer 3 switch is the right tool. If you need to connect to an external network with a WAN interface and run dynamic routing protocols against an ISP, you need a router. Some devices do both and they're often called routers in marketing material even though they include a built-in switch. Check the datasheet carefully before you buy something expecting it to handle a task it can't actually perform. Here's a counter-intuitive point about MTU. When you route between networks, every hop can fragment packets if the MTU shrinks. Most home networks run 1500 byte MTUs on everything. But if you add a VPN tunnel or an MPLS link somewhere in the path, the MTU drops to around 1400 or even 1350 bytes. Your layer 2 switch doesn't care about MTU at all. It forwards frames based on MAC addresses regardless of frame size up to its jumbo frame limit. The router is what encounters the MTU mismatch and either fragments the packet or drops it and sends back an ICMP fragmentation needed message. If that ICMP message gets blocked by a firewall, your TCP connection stalls completely. Troubleshooting this usually means checking the path MTU between two endpoints, not checking the switch logs since the switch has no visibility into IP-level problems.
Practical Setup and Configuration
For a basic home network, you plug your modem or ONT into the WAN port of your router. Your computer, phones, and other devices connect to the LAN ports on the router or to an additional switch plugged into one of those LAN ports. The router assigns IP addresses via DHCP and translates private addresses to your public IP through NAT. Traffic destined for the internet leaves through the WAN port. Return traffic comes back and the router routes it to the correct internal device based on its NAT translation table. If you add a switch to expand your wired ports, place it on the LAN side of the router. Never place a switch between your modem and the router's WAN port unless you understand what you're doing and have equipment that supports bonding or failover configurations. Putting a switch there will create a broadcast loop or prevent the router from establishing its WAN connection properly. I've seen this happen more times than I care to count during weekend IT support calls. For VLANs, configure them on your switch first, then set up the router interface to route between them. On a managed switch you create the VLANs, assign ports to them, and configure the uplink to the router as a trunk port carrying tagged frames for each VLAN. The router needs sub-interfaces or SVIs (Switched Virtual Interfaces on a layer 3 switch) to route traffic between those VLANs. This takes about twenty minutes on a modern managed switch if you've done it before and about an hour if you're reading documentation for the first time.
Common Pitfalls That Waste Time
Cable management isn't just aesthetic. I've worked in server rooms where someone ran Cat5e cables next to high-voltage power lines and wondered why their switched network had consistent errors on specific ports. Ethernet is sensitive to EMI at higher speeds. Cat5e struggles past 1 Gbps over long runs when placed near interference sources. Cat6 or Cat6a has better twist density and shielding options. The difference shows up as CRC errors in switch port counters, which slowly throttle throughput without taking the link completely down. Another issue is spanning tree protocol. If you accidentally create a loop by connecting two switches with two cables, spanning tree will block one of those links to prevent a broadcast storm. This is a safety feature but it means you're leaving bandwidth on the table. Properly configured, spanning tree converges in about 30 to 50 seconds after a topology change. During that window, your network is partially or fully unavailable. Rapid PVST+ or MST reduces convergence time to under a second, but you need switch hardware that supports it and you need to configure it correctly on every switch in the bridged domain. Unmanaged switches have their own limitations. They don't support VLANs, they don't give you port statistics, and they flood broadcasts to every port. For a small setup with five or six devices this is fine. For anything larger, you'll notice the performance degradation from excessive broadcast traffic, especially if you have wireless access points, IP cameras, or IoT devices generating background noise on the network. A $60 unmanaged switch will work until it doesn't, and then you'll be dealing with a network that feels slow without any obvious single point of failure.
Power over Ethernet is another area where people make mistakes. A standard PoE switch delivers up to 15.4 watts per port under the 802.3af standard. PoE+ (802.3at) goes to 30 watts. PoE++ (802.3bt) can deliver up to 90 watts. If you plug a high-power device like a PTZ camera or a wireless access point into an 802.3af port, it will either not power on or it will malfunction under load. Check the power budget of your switch before deploying devices. A 24-port PoE+ switch with a 370-watt budget can only power about twelve devices at full 30 watts simultaneously. If you try to connect fifteen, some ports will negotiate down or refuse power entirely depending on how the switch handles budget allocation.
When to Choose One Over the Other
You need a router when you're connecting to an external network, whether that's your ISP's internet or another site through a VPN. You need a switch when you're expanding the number of devices on your local network or when you need to segment traffic at layer 2 with VLANs. Most setups need both. A router at the edge and one or more switches on the internal LAN. The downside of routers is that they introduce a processing bottleneck. Every packet between VLANs or between your LAN and the internet passes through the router's CPU. Switching within a VLAN on a layer 2 switch happens in hardware with near-zero latency. That's why the recommendation in enterprise environments is to keep traffic local whenever possible and only route when necessary. Design your VLANs so that communication stays within the same broadcast domain when you can. Route only at the boundaries where it's required. There's no universal answer that covers every scenario. A $30 consumer router handles a small apartment network without issues. A $2000 enterprise router with multiple WAN links and advanced routing protocols is overkill for the same setup and introduces configuration complexity that creates more problems than it solves. Match the tool to the actual traffic volume, the number of devices, and the segmentation requirements. The specifications on paper matter less than what the device actually does under load in your specific environment.