The Basics Nobody Puts Into Plain Words Anymore
Information and Communication Technology covers the entire stack of systems we use to store, process, transmit, and retrieve data. That includes hardware like servers and switches, software ranging from operating systems to enterprise applications, networking infrastructure such as fiber optic backbones and wireless access points, and the protocols that glue it all together. It is not one thing. It is a layered discipline that overlaps with computer science, electrical engineering, and organizational management. When people ask
What Is The Information And Communication Technology
, they are usually looking for a simple definition. The honest answer is that ICT is the umbrella term for anything that handles information flow in a digital context. You use ICT every time you authenticate to a VPN, sync files across cloud storage, or route VoIP traffic through a session border controller. The concept itself is broad by design, which is also why it causes confusion in practice.How It Actually Works Under the Hood
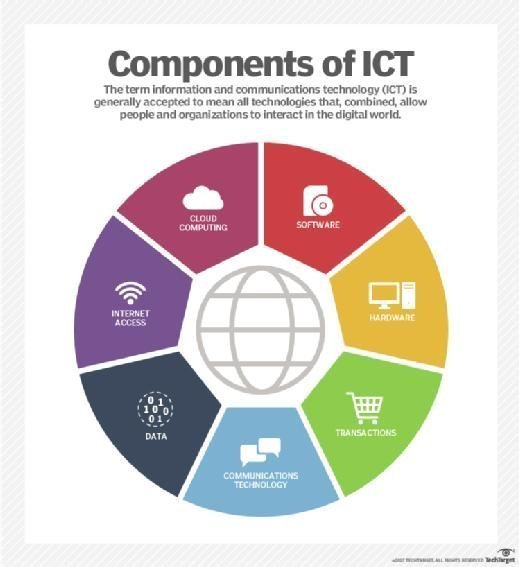
Data enters the system as bits, gets packaged into frames, routed through networks using protocols like TCP/IP, processed by software stacks, and then stored on disk or served back to an endpoint. The OSI model still helps engineers debug problems, even though most modern tools abstract most of those layers away from daily work. In an enterprise environment, you will typically see these components working together:
- Network layer: routers, switches, firewalls, WAN accelerators, and SD-WAN controllers that move packets between sites
- Compute layer: physical servers, virtual machines, containers, and edge nodes that run applications
- Storage layer: SAN, NAS, object storage, and redundant array configurations that hold data at rest
- Application layer: ERP systems, CRM platforms, messaging services, and custom internal tools that end users interact with
- Security layer: identity providers, zero trust gateways, SIEM platforms, and encryption key management systems that protect everything else
I used to think the separation between these layers was clean. It is not. When I was troubleshooting a latency spike at a mid-size logistics company, the issue turned out to be a misconfigured MTU on a WAN link that sat between two MPLS circuits. Packets were being fragmented downstream, which caused retransmissions that cascaded into application timeouts. The symptom looked like an app problem. The root cause was a 1500 byte MTU set on an interface that needed 1492 bytes due to PPPoE encapsulation overhead. I changed the MTU, adjusted the TCP MSS clamping on the firewall, and the issue cleared within an hour. That kind of cross-layer dependency is why ICT professionals need to understand more than one stack. The biggest mistake I see is treating ICT as purely a technology purchase problem. You can buy every licensed tool on the market and still have a broken information flow if your data architecture, governance policies, and operational workflows are not aligned. I worked on a project where a healthcare organization spent over two million dollars on a new EHR integration platform. Six months later, they were still manually exporting reports from three different systems because the data mapping had not been validated against actual clinical workflows. The technology worked. The process did not. Another counter-intuitive reality is that more connectivity often creates more friction. Adding redundant paths, failover clusters, and multi-region deployments introduces consistency problems. Distributed databases like Cassandra or CockroachDB solve partition tolerance but sacrifice strong consistency under normal conditions. You have to decide which guarantee matters for each workload instead of defaulting to "connect everything." I ran into this when a fintech team expected their new API gateway to transparently load-balance across three geographic regions. The client sessions drifted, token validation failed intermittently, and support tickets doubled. We implemented sticky sessions with region-aware routing and cut the ticket volume in half within two weeks.
Get the Full Details

Here is a point most beginners miss: communication technology is not interchangeable with information technology. IT focuses on how data is processed and stored within organizational systems. Communication technology focuses on how data moves between those systems and external endpoints. ICT merges both. When you separate them in your planning, you get siloed budgets, conflicting SLAs, and blame games during outages.
Practical Steps for Setting Up a Functional ICT Environment
If you are building or restructuring an ICT setup, start with inventory and documentation before buying anything. I cannot stress this enough. A network diagram drawn from memory is worse than no diagram at all. I spent three days documenting a client's infrastructure by tracing cable runs and reading switch configurations because their existing diagrams were from 2018 and completely inaccurate. The process revealed twelve undocumented devices, including a rogue access point connected to the guest Wi-Fi VLAN that was capturing unencrypted traffic from the main corporate subnet. From there, follow a structured approach:
- Audit existing systems: catalog hardware, software licenses, network topology, data flows, and integration points. Use tools like Nmap for discovery, Lansweeper or Snipe-IT for asset tracking, and network packet brokers for traffic analysis.
- Define requirements with measurable outcomes: instead of saying "we need better collaboration tools," specify that field technicians must sync work orders offline and reconcile within five minutes of reconnection, with data integrity verification on merge.
- Design with failure in mind: assume every component will break. Plan for single points of failure in power, network, and storage. Document failover procedures and test them quarterly, not annually.
- Implement in stages with rollback plans: migrate one subsystem at a time. Keep the old system running in parallel until the new one proves stable for at least thirty days under production load.
- Establish monitoring and alerting early: configure metrics collection for bandwidth utilization, error rates, latency percentiles, and storage IOPS. Set thresholds based on actual baselines, not generic recommendations.
- Train operators, not just administrators: the people who manage the systems should understand the business processes they support, and the end users should know basic security hygiene and troubleshooting steps.
Where ICT Falls Short and What to Do Instead
No ICT framework handles every scenario well. Centralized cloud architectures introduce vendor lock-in and dependency on internet uptime. On-premises solutions require capital expenditure and specialized staff. Hybrid models add complexity in management and security boundary definition. There is no universally correct answer. When you are dealing with legacy systems that lack modern APIs, you will hit integration walls. I once spent six weeks building a custom middleware layer using Apache Camel to connect a 2003-era manufacturing execution system to a modern cloud dashboard. The legacy box only spoke SOAP over HTTP with WS-Security enabled. The cloud platform expected REST with OAuth2. The middleware handled the protocol translation, certificate management, and message queue buffering. It worked, but the ongoing maintenance burden was significant. In cases like this, a phased replacement strategy or a dedicated integration platform as a service (iPaaS) might have been more sustainable long-term, even if the upfront cost was higher. Security remains the persistent weakness across all ICT implementations. Zero trust architectures reduce the blast radius but increase operational complexity. Multi-factor authentication prevents credential theft but does not stop phishing or insider threats. Encryption protects data in transit and at rest but becomes irrelevant if key management practices are weak. I have seen organizations deploy end-to-end encryption only to discover that their backup procedures stored decrypted keys in the same repository as the encrypted data. The security measure existed on paper but not in practice.
The practical takeaway is that ICT is a continuous engineering discipline, not a one-time deployment. The systems you build today will need reconfiguration within eighteen months as workloads shift, security threats evolve, and organizational requirements change. The professionals who treat it as a permanent responsibility tend to have fewer crises than those who treat it as a project with an end date.