Understanding the Human Layer of Security
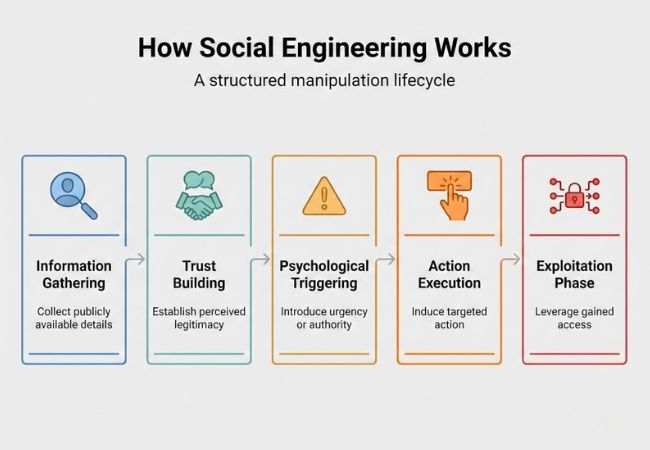
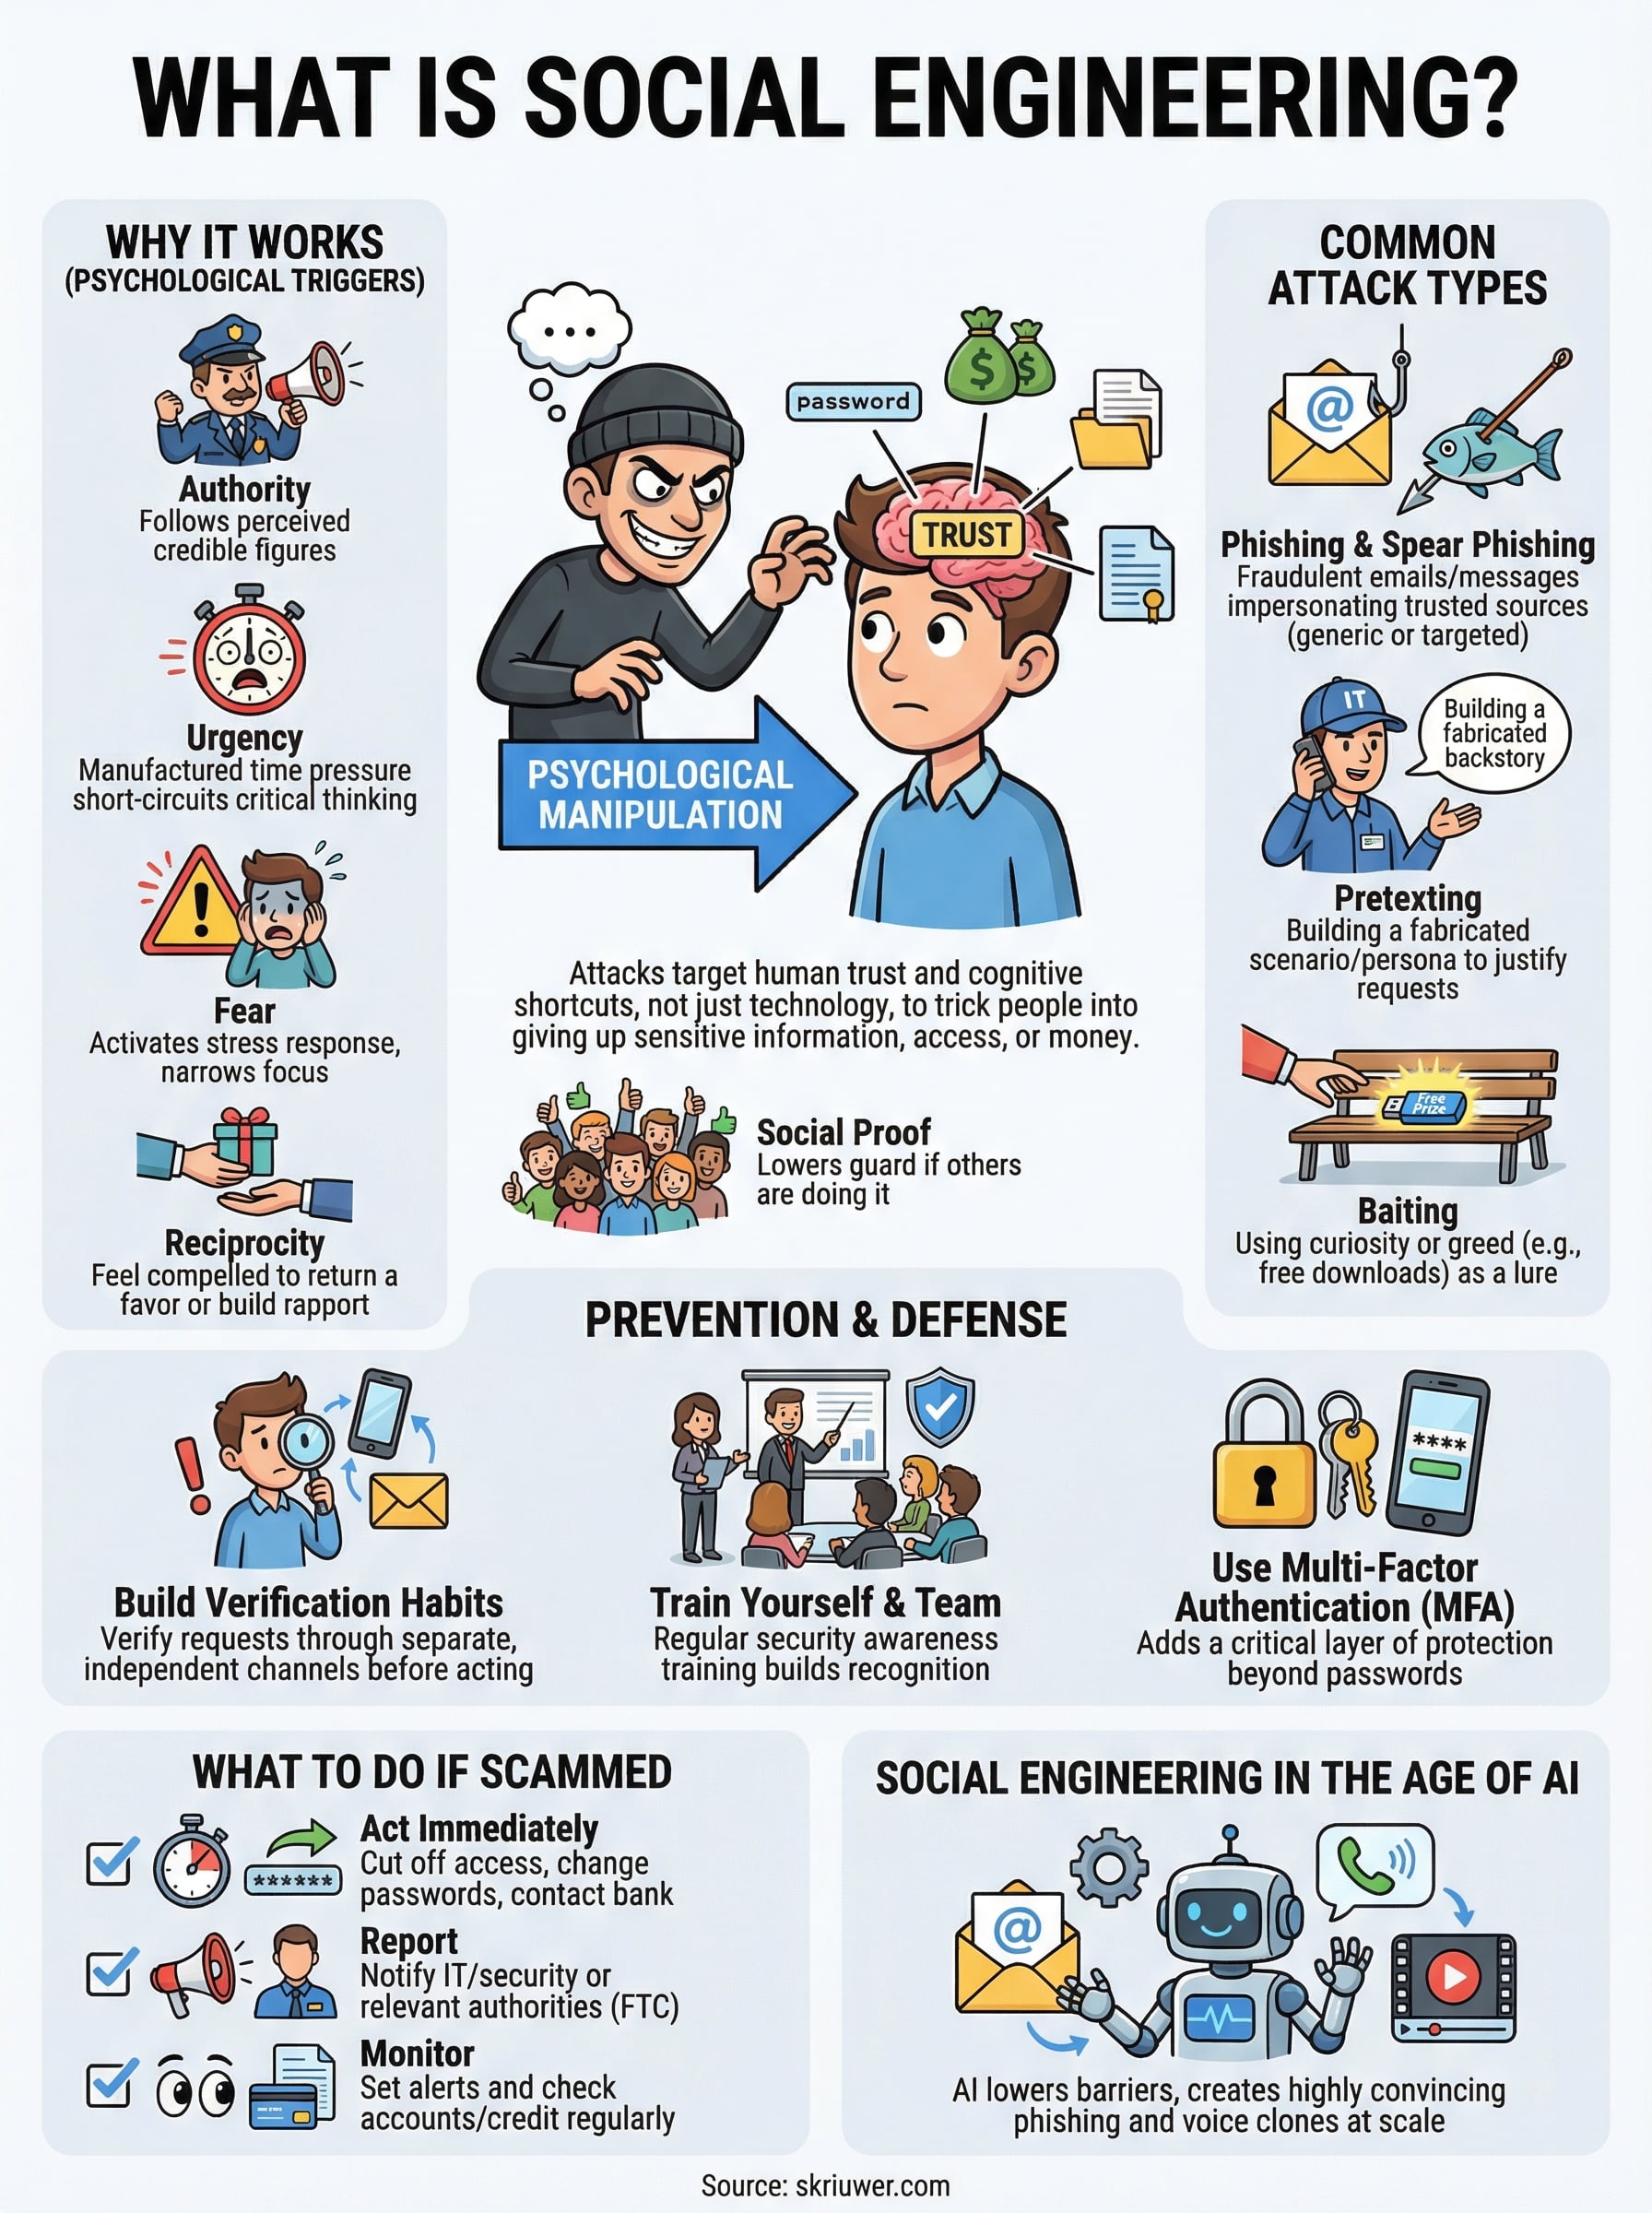
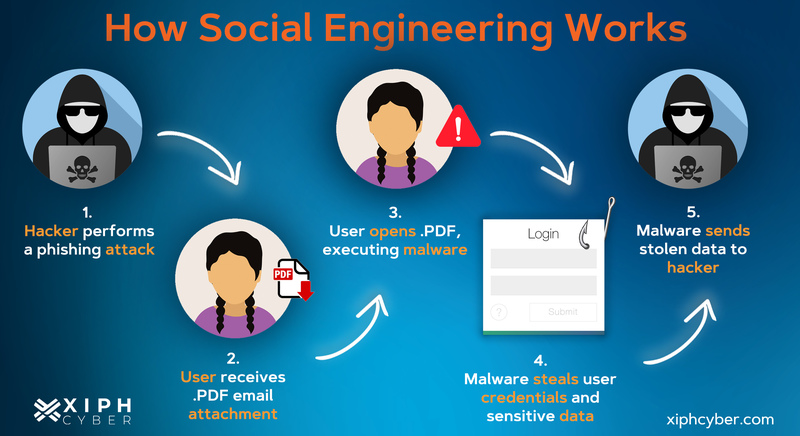
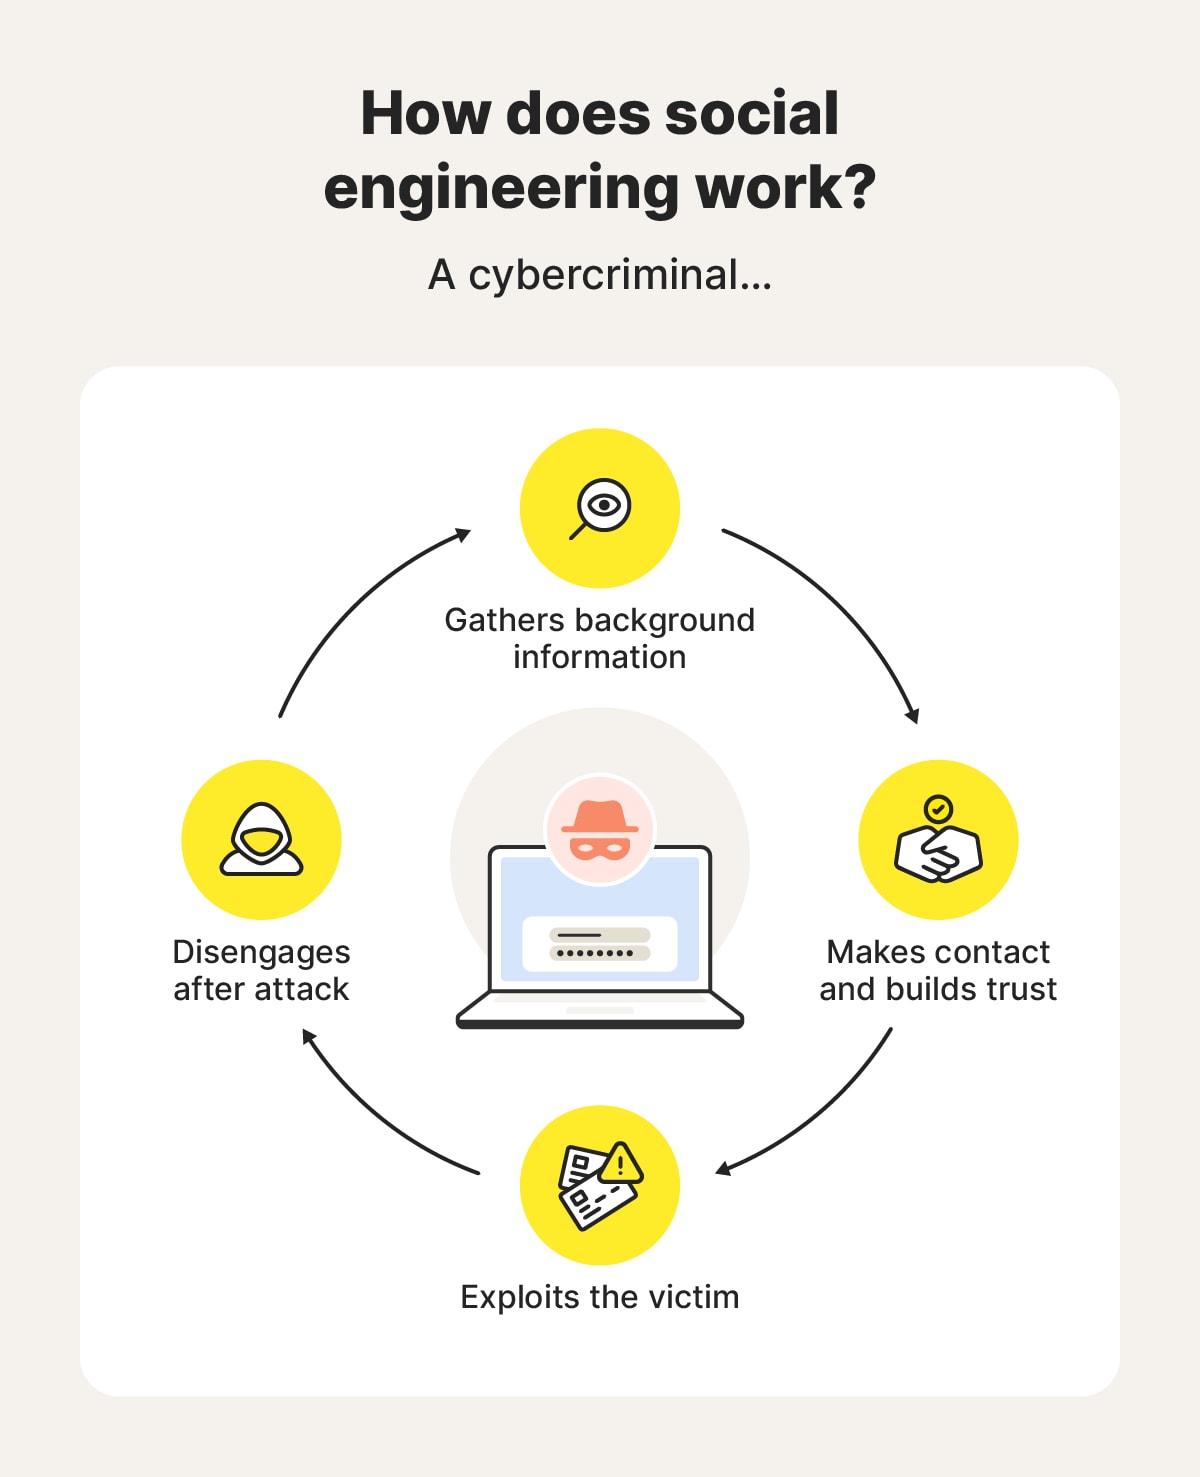
Most security breaches don't involve sophisticated exploits or zero-day vulnerabilities. They involve someone clicking a link because their boss asked them to. I've spent years watching organizations pour millions into firewalls and endpoint detection, only to have everything compromised through a phishing email that looked slightly off but convincing enough to panic someone into action. The role of social engineering in security is fundamentally about exploiting human psychology rather than technical weaknesses. It's the practice of manipulating people into breaking normal security procedures or revealing confidential information.What Is The Role Of Social Engineering
Social engineering functions as both an offensive weapon and a defensive lens. On the attack side, it gives threat actors a way in when every technical perimeter is hardened. On the defense side, understanding it changes how you build security awareness programs instead of just checking compliance boxes. The most common vectors are phishing, pretexting, baiting, tailgating, and Q&A tricks disguised as legitimate requests. Phishing remains the dominant entry point globally, accounting for the vast majority of initial access scenarios in breach reports. Pretexting involves creating a fabricated scenario to gain trust. Baiting uses physical media or download links that look too valuable to ignore. Tailgating is the simplest and most overlooked, just walking through a secure door behind someone who holds it open. I was running a red team engagement last year against a mid-size healthcare organization. Their email filtering was solid, their employees had completed training modules the year before, and their physical access controls were tight on paper. The engagement took three days. On day one, I registered a domain that differed by one character from their internal portal URL. Day two, I had seven people handing over credentials. Day three, I walked into the building using a cloned badge I'd copied from a photo of one of the credentialed employees' desk badges taken during a casual conversation at a coffee shop near their office. The whole thing took about four hours of actual social interaction spread across the three days. The security team's response time was impressive, but they'd already lost access to their patient records system.
The nuance most people miss is that social engineering works differently depending on organizational culture. In a high-stress environment with clear hierarchy, people comply faster because not complying feels risky. In a flatter organization, you get more skepticism but also more independent thinking, which means you have to be more creative with your approach. There's a counter-intuitive insight here that most awareness programs miss. More training doesn't necessarily make people harder to socially engineer. In fact, well-meaning but fear-based training can create anxiety that makes people snap at quick responses under pressure. The best results come from repeated, low-stakes practice with realistic scenarios, not annual compliance videos. People need to build muscle memory for slow-down behaviors, not memorize definitions. Another thing beginners consistently get wrong is thinking technical indicators matter. They don't. The domain might look clean. The SSL certificate is valid. The sender name matches their VP. None of that matters when the person receiving the message is already in a time crunch and sees something that triggers urgency. Your assessment should focus on context and timing, not headers. From a defensive standpoint, the role of social engineering awareness should be woven into incident response and change management processes, not treated as a separate initiative. When you're rolling out new systems or policies, that's when social engineering resistance drops. People assume new means legitimate. They assume change means approval. This is when you see the highest success rates for insider-facilitated compromises. One specific workaround I use when designing internal tests is embedding subtle errors in otherwise perfect communications. A small typo in a CEO's name. An unusual signature format. A slightly wrong department reference. These seem minor but they're actually reliable stressors that slow people down and trigger verification behavior. The goal isn't to trick someone, it's to give them a reason to pause. There are real limitations to relying on social engineering awareness alone. You will always have outliers, people who are either too confident or too distracted to respond appropriately, and the problem compounds at scale in large organizations. No amount of training eliminates risk. The practical approach combines awareness with technical controls that reduce the blast radius, like email gateway filtering, multi-factor authentication everywhere, and principle of least privilege applied consistently. Physical security assessments often reveal the fastest path to compromise because most organizations treat it as secondary. I've walked into buildings with no visitor management at all, just by asking politely at the front desk and mentioning a name from a publicly available staff directory. The person at the desk was doing exactly what they were trained to do, which was being helpful, not suspicious. Being helpful and being suspicious are different skills, and most people aren't trained in both.