Verizon Business Mobile Secure Is a Unified MDM Platform, Nothing Fancy
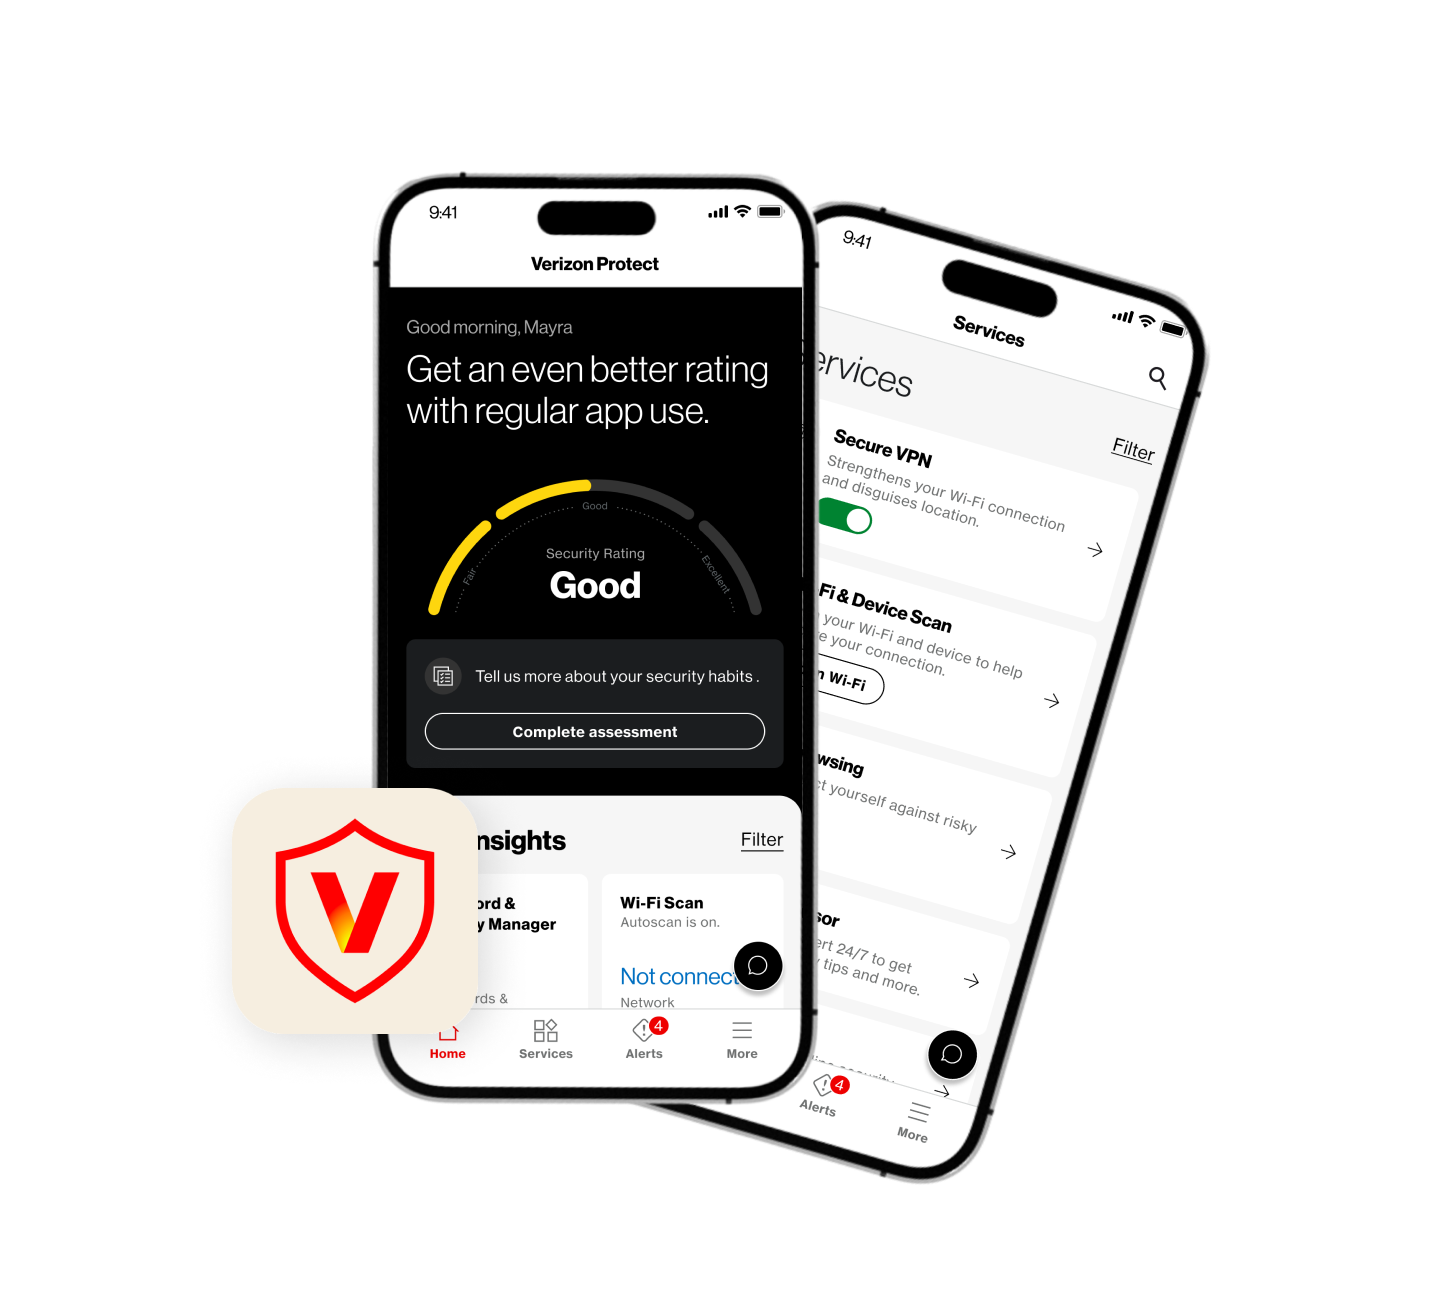
It is Verizon's own mobile device management and security stack for enterprise customers. The product lets IT teams remotely provision, monitor, and lock down company-issued phones and tablets. It covers iOS, Android, and increasingly Windows and macOS devices. You pay a per-device monthly fee. That is the basic structure. On paper it is a zero-touch enrollment and policy enforcement platform sold alongside Verizon business wireless plans. In practice, it lives inside the Verizon Cloud portal and integrates with your existing EMM provider through their partnership layer. If you have a fleet of 50 iPhones for salespeople, you use this to push certificates, set passcode rules, wipe lost devices, and bundle corporate apps before the phone ever reaches the user's hands. I have managed deployments ranging from 12 devices to over four thousand across multiple verticals. The platform works, but it is not the most polished EMM in the market. The real value shows up when you are already on a Verizon Business Wireless plan and want to bundle device management into one bill and one support case. Separating it out from your core carrier relationship usually does not make financial sense.
The architecture hinges on Apple Business Manager and Google's Zero-Touch Enrollment for true zero-touch provisioning. Without those integrations configured correctly, you are back to manually enrolling every device, which defeats the entire purpose. I spent two weeks last year untangling a client's deployment because their ABM account had stale credentials that had been rotated by the parent company's finance team. The portal showed devices as enrolled, but the policies were silently failing to apply. The fix was pulling the ABM token from the device profile settings and re-authorizing it through the Apple portal with an updated Service Account token. Took about forty-five minutes once I knew where to look.
How It Works in Practice
You start by creating a service request through your Verizon account rep or the portal. They provision the secure container and give you admin access to the management console. From there you configure your device categories, set password policies, choose which apps get pushed, and define what happens when a device is reported lost or an employee leaves. The enrollment flow is:
Get the Full Details

- Step one: Configure Apple Business Manager or Google Zero-Touch with your org's credentials.
- Step two: Create device groups based on department or role.
- Step three: Define security policies like encryption requirements, jailbreak detection, and app blacklist rules.
- Step four: Attach your app catalog or link to your existing MDM app store.
- Step five: Ship devices or hand them to users with the QR code or automatic enrollment prompt.
Most of the friction comes from the policy creation phase. Verizon's policy templates are fairly generic. They cover standard corporate needs, but if you have compliance requirements like HIPAA or FTC Safeguards, you will spend time building custom configurations on top of their base templates. It is doable. It just adds time to the initial rollout. Data classification is another area where people run into issues. The platform handles basic containerization, separating personal from corporate data. But it does not do content-aware DLP the way dedicated solutions like Versafe or VMware Workspace ONE can. If you are shipping devices to healthcare or financial services teams, you need to know that limitation upfront. I had a logistics company try to force compliance with FDA 21 CFR Part 11 requirements and discovered halfway through that the audit logging depth was insufficient. They ended up running a parallel audit trail through their existing SIEM, which doubled their reporting overhead.
Where It Falls Apart
The biggest problem I see repeatedly is the console UX. It is functional but dated. Searching for a specific device across a large fleet takes multiple clicks. Bulk actions are limited compared to competitors. If you have 2,000 devices and need to push a policy change, expect to spend twenty to thirty minutes in the console doing things that would take five minutes in a more modern EMM interface. Another blind spot is cross-platform parity. Android policies lag behind iOS policies in terms of granularity. Certain Android enterprise features like selective wipe or specific MDM-only app restrictions do not always map cleanly through Verizon's wrapper. I learned this the hard way when a retail client enrolled 800 Android Go phones and found that half their intended restrictions were silently ignored because the device profile did not support the underlying Android Enterprise mode they assumed was active. Support response times vary by your contract tier. Standard business support will route you through general troubleshooting first, which adds delay. If you are paying for premium support, you get a dedicated account manager and faster escalation, but that tier starts at a significantly higher price point. For mid-market companies, the support gap can be frustrating during an active breach or mass device compromise scenario.
Alternatives Worth Considering
For small teams under 100 devices, the bundled value is reasonable and the single-vendor relationship simplifies billing. Beyond that, you should compare total cost against dedicated EMM platforms like Microsoft Intune, SOTI, or Jamf, especially if you need advanced features like custom compliance reporting, third-party integration APIs, or deeper Android customization. Verizon Business Mobile Secure works best as a middle ground, not as a best-in-class EMM solution. If you are already deeply invested in the Verizon ecosystem and want a simple, good-enough mobile security solution without managing multiple vendor contracts, this product does the job. Just budget extra time for the initial configuration and be aware of the gaps before you commit to a long-term deployment.