Configuring Active Directory on Windows Server 2008
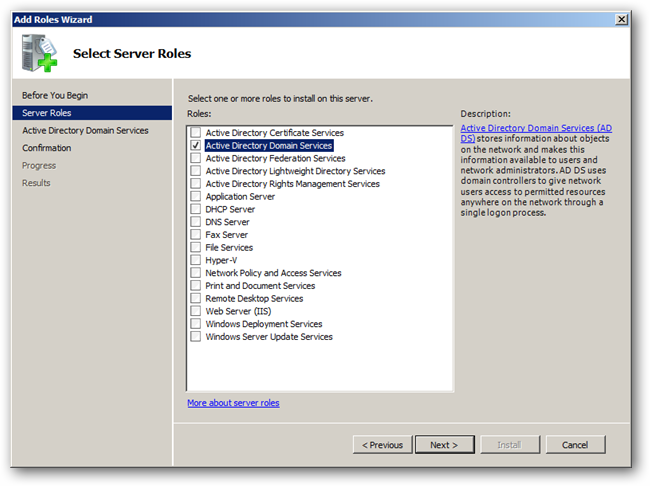
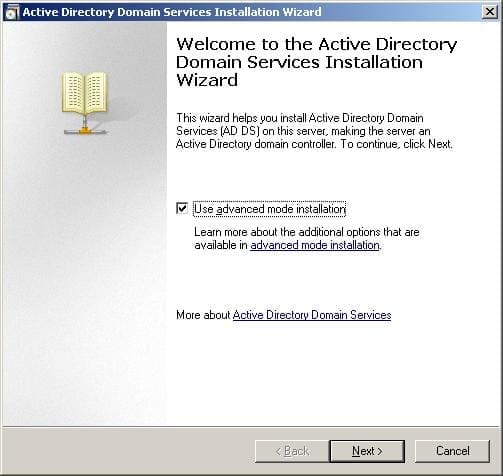
Promoting a server to a domain controller in Windows Server 2008 isn't complicated, but it's easy to miss details that bite you later. The process starts with adding the Active Directory Domain Services role through Server Manager. You click Add Roles, check AD DS, and follow the wizard. After the role installs, you run dcpromo from the command line or click the alert in the right-hand panel of Server Manager. At that point you choose between creating a new domain in a new forest, joining an existing domain, or adding a new domain to an existing forest. For a fresh deployment, you'll pick new domain and enter your root domain name. The wizard will ask you to set the DSRM password. Don't skip this or reuse a password you've used elsewhere. I once watched someone use their admin password for DSRM, got locked out of single-user mode after a bad install attempt, and had to boot off the DVD just to reset it. There are a few screens that matter more than most people realize. The SYSVOL location. The default is fine for most deployments, but if you have separate disks, putting SYSVOL on its own volume keeps replication traffic from contending with your database. The DNS settings matter too. Windows Server 2008 will offer to install DNS automatically if it's not already present. It's usually the right call, but if you already have a trusted DNS infrastructure, you can uncheck that box and point the DC at your existing servers.
Windows Server 2008 Active Directory Configuration Answers
Prerequisites aren't heavy. You need a static IP address, a valid hostname under 15 characters, and the local Administrator password. Your time zone should be correct because replication timestamps depend on it. A ten-minute clock skew between two DCs can cause replication to fail silently until you check the event logs. The server also needs the proper forward and reverse lookup zones in DNS before promotion, though the wizard will catch most issues. Here's something beginners typically get wrong. After promotion completes, don't immediately repurpose the server for other workloads. I saw a team install SQL Server on their new primary DC within an hour of promotion. The system became unstable because AD DS and SQL Server were fighting over memory and disk I/O. Keep DCs dedicated. Run AD-specific tools, not random applications. Replication between domain controllers uses a topology that the Knowledge Consistency Checker builds automatically. Under normal conditions you don't need to touch it. But in a multi-site environment with limited WAN links, the default topology might push too much replication traffic across a slow connection. You define sites and subnets in Active Sites and Services, and the KCC calculates intra-site and inter-site replication differently. Intra-site uses multiple partners and near-real-time notification. Inter-site relies on scheduled replication intervals that you can adjust per site link. Set the interval to something reasonable like 15 to 60 minutes depending on your bandwidth, and enable compression if the link is narrow.
For FSMO roles, five exist and most admins only worry about the first two. PDC Emulator and RID Master are the ones that matter for daily operations. Schema Master and Domain Naming Master are rarely touched unless you're adding a new domain or modifying the schema. Infrastructure Master runs per domain and handles cross-object references. If you have only one domain controller in each domain, the Infrastructure Master can become problematic because it holds onto stale data. The workaround is simple: if you're in a single-domain environment with just one DC, delegate the role to a global catalog server or just accept that it will function differently. Microsoft documented this behavior. One edge case that trips people up involves restoring a domain controller from backup. You can't just restore the AD database and expect replication to fix everything. If the DC was the owner of any FSMO role, you need to perform a non-authoritative restore first, then let it replicate. If it held the PDC Emulator role and you restore it to a point before the current timeline, you risk creating a USN rollback. That means another DC in the domain could reject replication because it thinks the restored DC has future changes. The only clean fix after a USN rollback is to take the restored DC offline, demote it, and rebuild it. I learned that the hard way on a client's exchange server setup where the DC had been partially restored from a failing disk image. Monitoring replication health is straightforward but underused. Run repadmin /showrepl on each DC and check for errors. The output shows each replication partner, the last success time, and any failures. If you see persistent failures, repadmin /replsum gives you a quick summary. Pair that with checking Event ID 1311, 1988, and 2042 in the Directory Service log, and you'll catch most issues before they become problems.
Get the Full Details
Another common mistake is leaving the default Group Policy settings untouched on a new domain. The built-in Domain Admins group has far too much access for modern environments. Create a separate administrative account structure with delegated permissions using the Delegation of Control wizard. Restrict Domain Admins to actual infrastructure tasks and use separate accounts for day-to-day management. It takes extra time upfront but cuts down on accidental misconfigurations later. If you're deploying in a virtual environment, pay attention to snapshot practices. Taking snapshots of domain controllers is generally discouraged because it can cause USN rollback scenarios similar to the restore problem above. If you must snapshot a DC, ensure the snapshot tool is AD-aware and coordinates with the replication process. Otherwise, stick to VSS-based backups that don't involve VM snapshots. The whole setup process for a standard single-domain, single-site environment takes roughly 20 to 30 minutes from start to finish if nothing goes wrong. Multi-site with DNS integration and FSMO role transfer might take an hour or so. Anything longer usually means there's a DNS issue or a network connectivity problem between sites that needs troubleshooting first.