How AS/NZS 4360 Risk Management Actually Works in Practice
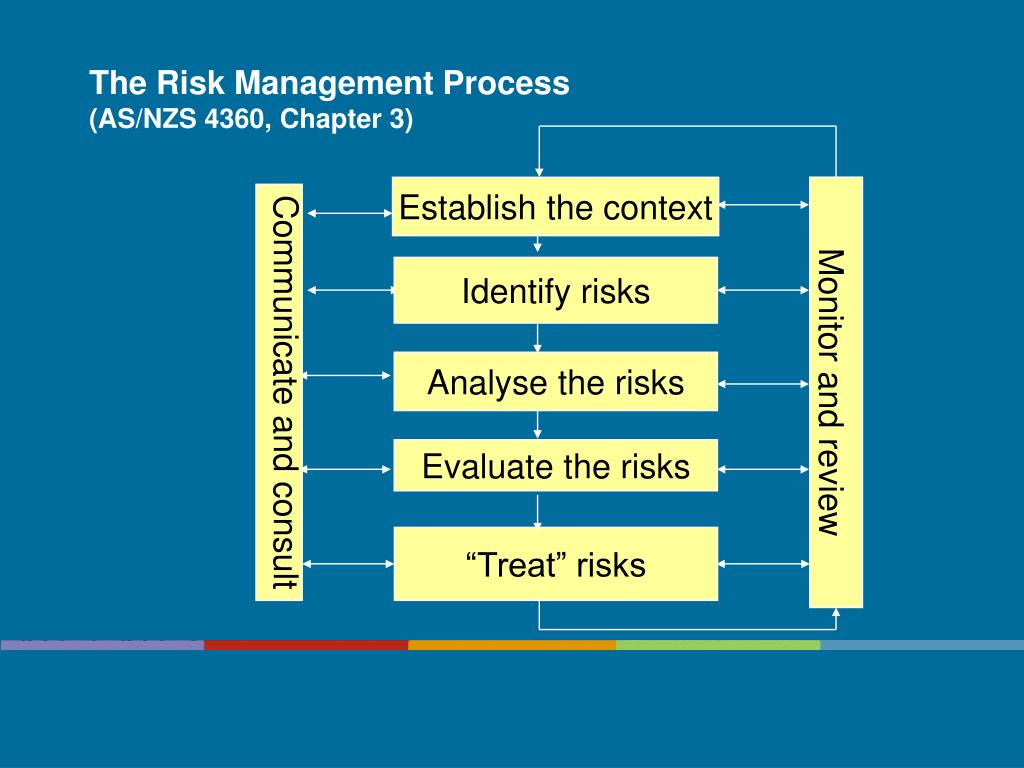
AS/NZS 4360 Risk Management was the original Australian/New Zealand standard for handling risk in organizations. It was published in 1995 and revised in 2004, before being replaced by AS/NZS ISO 31000 in 2009. If you are working with legacy documentation or older compliance frameworks, you will still encounter it. Understanding how it functions matters even if you have moved on to newer standards. The standard lays out a straightforward five-step process. I know that sounds oversimplified because people tend to treat risk management frameworks like they contain some hidden complexity, but the original document is refreshingly direct about what it expects you to do. The steps are establish context, identify risks, analyze risks, evaluate risks, and treat risks. That is it. Most organizations overcomplicate it because they add layers of bureaucracy on top of a simple model. The first thing I always tell people who inherit this framework is that the "establish context" step is where projects go to die. Not because it is hard, but because everyone treats it as a checkbox exercise and writes three paragraphs of filler that nobody reads. Context establishment requires you to define the external and internal environment, set the scope, and establish the risk criteria your organization will use. Risk criteria means the thresholds against which you measure whether a risk is acceptable or not. Without clear criteria, your analysis has no anchor point. A project I was on once had risk criteria defined as "whatever the board says feels wrong," which made the entire subsequent process meaningless. We spent two weeks rewriting the criteria into measurable terms before we could proceed.
Identify, Analyze, and Evaluate: What People Get Wrong
Risk identification is not the same as listing problems. You identify sources of risk, events that could occur, and their potential consequences. The standard distinguishes between these three elements deliberately. Sources are where risk comes from. Events are what might happen. Consequences are what follows. Mixing them up is the most common mistake I see in risk registers. When you analyze risk, you consider the likelihood and the consequence. Likelihood is not just probability in a statistical sense. It includes how often something might occur and whether controls are in place. Consequence covers financial impact, reputational damage, safety implications, and operational disruption. The standard allows qualitative, semi-quantitative, or quantitative approaches. Most teams default to qualitative because it is faster and requires less data. I recommend semi-quantitative whenever possible. Assigning rough numeric ranges to consequences makes it easier to prioritize later, and it does not require expensive modeling software. A matrix with five levels for likelihood and five for consequence is usually sufficient. Evaluation is where you compare analyzed risks against your risk criteria and decide which ones need treatment. Here is a counter-intuitive point that beginners consistently miss: the purpose of evaluation is not to eliminate all high risks. It is to determine which risks require action and which can be accepted, monitored, or transferred. Treating every significant risk with the same level of intensity is a waste of resources. I once audited a department that had spent four months creating detailed treatment plans for thirty-seven risks, only to realize later that twelve of them were below their acceptance threshold and six were effectively uninsurable anyway. They had conflated identification with prioritization.
Treatment Options and Documentation Requirements
Risk treatment under AS/NZS 4360 offers several options. You can avoid the risk entirely by changing the activity. You can reduce likelihood or consequence through controls. You can transfer it through insurance or contracts. You can accept it consciously. You can retain it and monitor it. The standard explicitly warns against treating risks without considering whether the treatment itself introduces new risks. I have seen organizations implement a control measure that eliminated one risk and created three larger ones. It happened because nobody did a follow-up identification after the treatment was put in place. Documentation under this standard is minimal compared to later frameworks. You need to record the context, the methodology, the identified risks, the analysis results, the evaluation decisions, and the treatment plans. That is significantly less paperwork than ISO 31000 requires. The trade-off is that the standard provides less guidance on integration with strategic planning and governance structures. If your organization needs risk management embedded at the board level with regular reporting cycles, you will find ISO 31000 more useful even if you started with 4360.
Get the Full Details

Where AS/NZS 4360 Falls Short
I want to be clear about the limitations. The standard assumes a somewhat linear process. Real organizations do not work in clean sequential steps. Risk identification and analysis happen simultaneously in practice. The framework does not address dynamic or emerging risks well. It was designed for a more stable business environment. It also lacks explicit guidance on quantitative risk modeling techniques, which matters if you operate in sectors like finance or engineering where probabilistic methods are expected. Another practical issue is that the standard does not prescribe any specific tools or software. This is fine if you have experienced practitioners, but it creates ambiguity for teams that expect a more prescriptive approach. Some regulators and auditors still reference 4360 in contracts and procurement documents. If you are working under those conditions, you need to demonstrate compliance with the process steps even if your organization uses ISO 31000 internally. The mapping between the two is straightforward. ISO 31000 covers the same five steps but adds principles, a framework, and continuous improvement elements on top.
Practical Workaround I Have Used
Here is a specific edge case that came up recently. I was working with a client who had a legacy AS/NZS 4360 compliance requirement from a tender document, but their existing risk register was built in a modern tool that exports to ISO 31000 formatting. The auditor wanted to see 4360-specific language. Rather than rebuild the register, I mapped each ISO 31000 field to its 4360 equivalent and added a cover sheet showing the correspondence. The mapping took about twenty minutes. The auditor accepted it. This happens more often than you would think. Standards bodies and procurement departments often copy language from old documents without updating references.
Accessing the Document
The standard itself is available through Standards Australia and Standards New Zealand. You will need to purchase a copy. There is no free official version. Some organizations keep outdated copies circulating internally, which is fine for reference but not reliable for compliance purposes. If you are doing this for certification or contractual reasons, buy the current available edition and note the publication date. Any training materials or templates you build should reference the specific version you are using.