Setting Up Your Study Environment
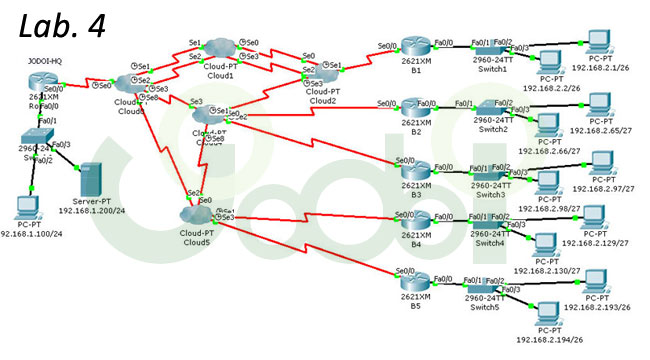
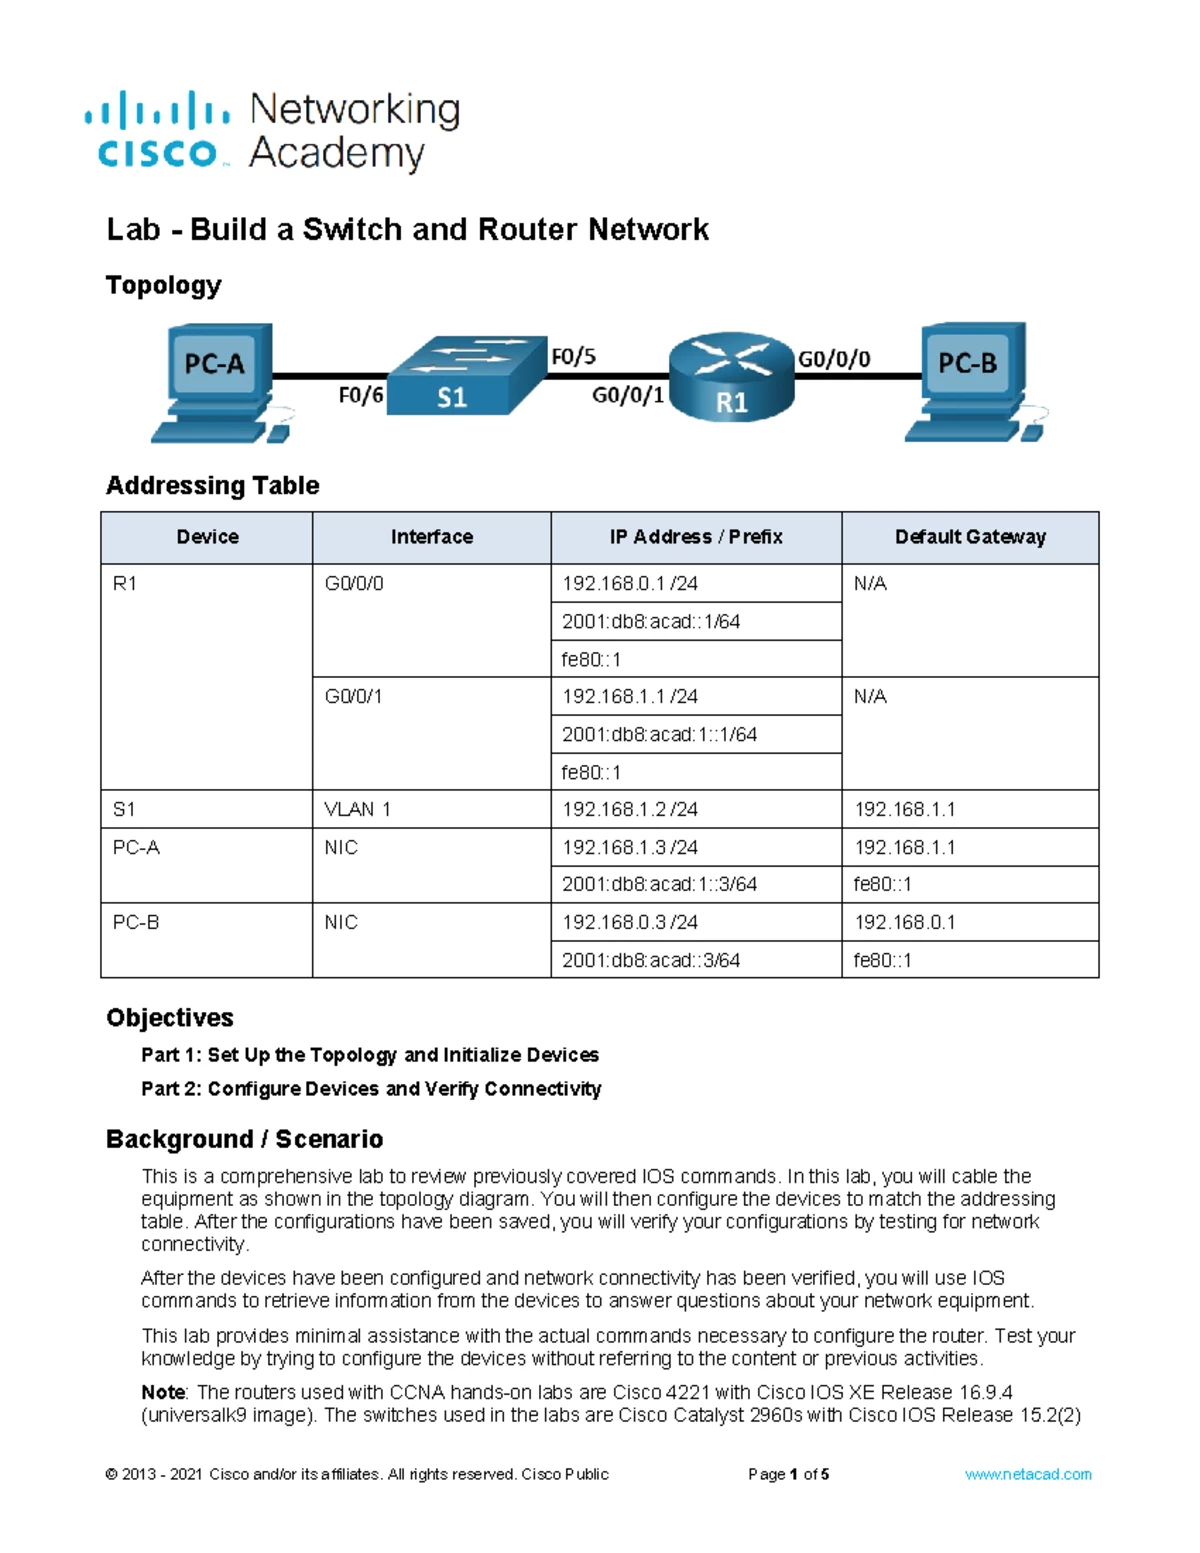
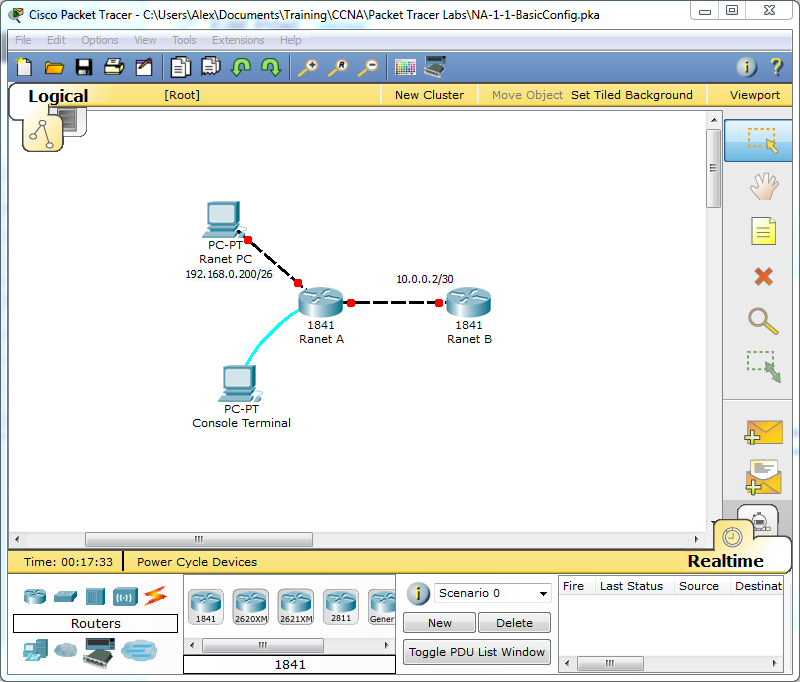
Start by downloading Packet Tracer from the Cisco Networking Academy portal. It is free if you have a student account, which takes about five minutes to set up. The software runs on Windows, Mac, and Linux. I have seen people try GNS3 instead, but that requires VirtualBox, KVM, or VMware as a hypervisor, and the boot time alone adds twenty minutes to every lab session. Packet Tracer loads in under thirty seconds. Once installed, launch the application and create a blank workspace. The first thing you need is a router. Drag one from the devices panel onto the canvas - the 1941 model is fine for most exercises. Then add a switch, any of the 2960 series works. Connect them with a straight-through copper cable. Double-click the link and make sure the red X is gone, meaning the physical layer is up. Now comes the part most beginners rush through. Click the router, go to the CLI tab, and press Enter. You will land at user exec mode, indicated by the router> prompt. Type enable to enter privileged EXEC mode, then configure terminal to enter global configuration mode. From there, set the hostname with a command like hostname R1. Simple, but if you skip this step, every subsequent command will reference the default name, and your documentation becomes useless within an hour.
I ran into a specific issue last year while preparing for the 200-301 exam. I had configured OSPF on three routers using loopback interfaces, but the routes were not appearing in the routing table. I spent forty-five minutes checking network statements, area assignments, and hello timers before realizing the loopbacks were set to /32 masks by default. OSPF treats /32 loopbacks as host routes, not network advertisements, so the neighbors never formed properly. The fix was adding ip ospf network point-to-point on each loopback interface. This forced OSPF to treat the link as a point-to-point adjacency, which resolved the issue immediately.
Basic Switch Configuration
Click the switch, navigate to CLI, and enter privileged EXEC mode. Create VLANs with vlan 10, then name Sales. Assign ports to that VLAN using interface range fastethernet 0/1-24, followed by switchport mode access and switchport access vlan 10. This takes about two minutes per VLAN. Do not forget to configure the trunk port if you are using multiple switches. Without a trunk, VLANs do not pass between devices, and your entire multi-switch topology becomes isolated. There is a common misconception that VLAN 1 is insecure by default. It is not, unless you actively move user ports into it. The real vulnerability is untagged traffic on trunk ports. If you do not prune VLANs from trunks, every VLAN traverses every link, which increases broadcast domain size unnecessarily. I once had a lab with twelve VLANs on a two-switch topology, and the CPU on both switches spiked to eighty percent during spanning-tree recalculations. Pruning unused VLANs from the trunk dropped CPU usage to under ten percent within minutes.
Get the Full Details
Router Interface Setup
On the router, configure the first serial interface with interface serial 0/0/0, then ip address 192.168.1.1 255.255.255.252. Add clock rate 64000 if this is the DCE end of the connection. Most textbooks omit this detail, but without a clock rate, the serial link stays down. I have lost count of the number of students who spend an hour troubleshooting a dead serial interface before discovering the cable was plugged into the DTE side instead of DCE. Static routes are straightforward but often misconfigured. Use ip route 10.0.0.0 255.0.0.0 Serial 0/0/0 to reach a remote network. The third parameter is the exit interface, not the next-hop IP. This matters because some routing protocols require a directly connected path, and specifying the interface instead of a next hop can change how the route is installed in the routing table. Dynamic routing with OSPF or EIGRP is more scalable but introduces convergence time. For a small lab with fewer than ten devices, static routes usually converge instantly and eliminate troubleshooting overhead.
Common Pitfalls and Workarounds
One issue I encounter regularly is Spanning Tree Protocol blocking ports unexpectedly. The default bridge priority is 32768, and whichever switch has the lowest MAC address becomes the root bridge. In a lab with mixed hardware, this can produce counter-intuitive topologies. Force the root bridge with spanning-tree vlan 10 root primary, which adjusts the priority to 24576 automatically. This takes about ten seconds and eliminates hours of spanning-tree debugging. Another problem involves NAT configuration on routers. Beginners often configure ip nat inside source list 1 interface Serial 0/0/0 overload but forget that ACL 1 must match the internal network, not the external one. I once had a lab where ping failed from inside to outside despite correct NAT rules. The issue was the ACL referenced the wrong subnet mask - it used /24 instead of /30 on the serial link. Changing the mask resolved the translation immediately. This kind of detail is rarely covered in official curriculum but appears frequently on the exam.
Verification Commands
After configuration, verify with show ip interface brief to check interface status. Look for up/up on all connected ports. If you see up/down, the physical layer is working but the protocol layer is not - usually a clock rate or encapsulation mismatch. If you see down/down, check the cable and device power. show running-config displays the current configuration, but it scrolls past quickly. Pipe the output with show running-config | include interface to see only interface lines. This filters the output to roughly twenty lines instead of two hundred. For OSPF verification, use show ip ospf neighbor. You should see full adjacency states, indicated by FULL. If you see INIT or 2-WAY, the neighbor relationship is incomplete. Check hello timers with show ip ospf interface. Mismatched hello or dead intervals prevent adjacency formation, even if the IP addresses are in the same subnet. I once spent thirty minutes troubleshooting a stuck 2-WAY state before discovering the dead timer was set to 40 seconds on one router and 20 seconds on the other. Matching the timers resolved the issue immediately.

Limitations of Packet Tracer
Packet Tracer simulates behavior rather than replicating real hardware. Certain commands that work on actual Cisco IOS are unsupported in the simulator. For example, ipv6 nd ra-lifetime does not function in Packet Tracer 8.2, even though it works on real routers. If you are preparing for the exam, this is acceptable, but if you are practicing for production work, the gaps become significant. I recommend supplementing Packet Tracer with Cisco DevNet sandboxes for hands-on experience with actual IOS versions. Another limitation involves performance. Packet Tracer can handle roughly fifty devices before UI responsiveness degrades noticeably. Beyond that point, CPU usage spikes and configuration changes take several seconds to apply. For large topologies, consider CML (Cisco Modeling Labs) or EVE-NG, though both require paid licenses or virtual machine management. For CCNA-level labs with fewer than twenty devices, Packet Tracer remains adequate and avoids the overhead of hypervisor setup.
Saving Your Work
Always save your configuration with copy running-config startup-config. This writes the running configuration to NVRAM, ensuring it persists after a reboot. I have seen students lose hours of configuration because they forgot this step and the simulator crashed. The command takes approximately five seconds and prevents data loss. Alternatively, use write memory, which is the older synonym and produces identical results. If you are using Packet Tracer, save the .pkt file regularly. The application can corrupt files during unexpected exits. I recommend saving every ten minutes as a habit. File corruption is rare but devastating when it occurs, especially if you have not backed up recent changes. Keep a versioned folder structure with dates in the filename, such as lab_2024_03_15.pkt. This makes it easier to recover previous configurations without relying on automated backups.
Final Recommendations
Build labs incrementally. Start with a single router and verify basic connectivity before adding complexity. Each additional device introduces new failure points, and troubleshooting becomes exponentially more difficult as topology grows. A two-router lab with static routes takes about fifteen minutes to configure and verify. Adding OSPF increases setup time to roughly forty-five minutes. Adding a switch with VLANs adds another twenty minutes. Budget your time accordingly and verify at each stage rather than completing the entire topology before testing. Document your configuration as you go. Use banner motd to add notes directly in the CLI, or keep an external text file with commands and explanations. I maintain a markdown file with every lab configuration, including the purpose of each command and any issues encountered. This takes an extra five minutes per lab but saves hours when reviewing for the exam or troubleshooting similar configurations in the future. The investment pays for itself within the first week of study.