CCSK v4 Exam Questions – A Practical Guide
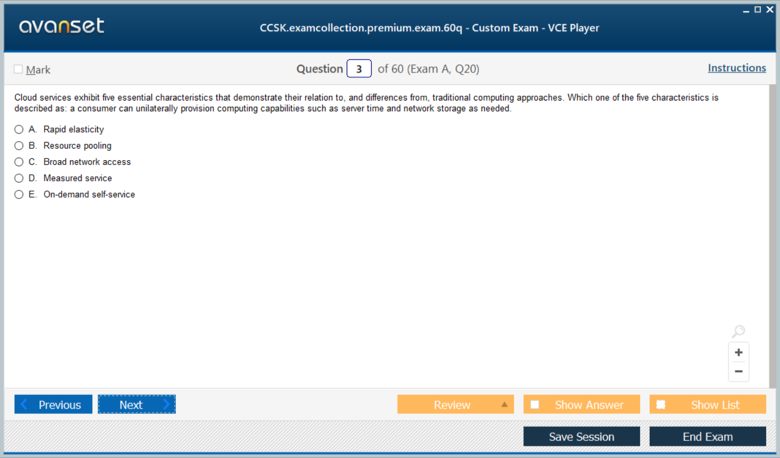
The CCSK v4 exam was updated by the Cloud Security Alliance to align with current cloud security practices. The exam covers eight domains: Governance, Risk, and Compliance; Legal Issues; Enterprise Risk Management; Infrastructure Security; Application Security; Data Security; Security Incident, Event, and Workflow Automation; and Operational Procedures. Passing requires a score of at least 70% on 60 multiple-choice questions within 90 minutes. I spent three weeks studying for this. Not because the material is impossible, but because the questions are deliberately tricky. They don't test whether you can define a concept. They test whether you can pick the best answer when four options all seem reasonable. I learned that the hard way on a practice set where three out of four choices were technically correct, but one was clearly the intended answer based on CSA framework language.
Where to Find Ccsk V4 Exam Questions
The official CCSK exam questions come from Cloud Security Alliance's own study materials. Their official study guide and practice questions are the closest thing to the real exam you'll get. Several third-party sites offer dumps and question banks, but those carry real risk. Using expired or inaccurate dumps can actually hurt your preparation because you'll memorize wrong answers. I'd rather see someone fail by knowing the material than pass by memorizing a question bank that doesn't reflect the current exam. The CSA website offers the Official CCSK Study Guide, which includes sample questions. Cloud Security Alliance also partners with Pearson VUE for exam delivery. Their website has a candidate handbook that walks through the exam format and content outline. That handbook alone is worth reading twice.
How the Exam Actually Works
The v4 exam shifted away from pure memorization toward scenario-based questions. You'll get a short real-world situation and have to pick the correct action or principle. For example, you might see a scenario about a company migrating workloads to a public cloud and be asked which governance control should be implemented first. The options will include things like "implement IAM policies," "conduct a risk assessment," "sign the CSP contract," and "deploy a SIEM solution." Here's the counter-intuitive part most people miss: the answer is almost never the technical solution. CSA frames cloud security as a governance-first discipline. In that scenario, the correct answer would likely involve risk assessment or governance processes before any technical controls. I've seen candidates pick the technical answer because it felt more concrete. That's the trap. The exam rewards understanding the CSA framework hierarchy, not your personal opinion on what makes sense technically. Another nuance that trips people up is the difference between CSP and CSPC responsibilities under the CSA Cloud Controls Matrix. Shared responsibility is a huge topic on the exam, and the questions love to blur the line between what the cloud provider owns and what the customer owns. I had to draw out responsibility matrices for compute, storage, networking, and data for each major cloud model before the concepts actually stuck. Once I visualized it, the exam questions became much easier to parse.
Get the Full Details
Study Strategy That Actually Worked
Don't read the study guide cover to cover in one pass. Read it twice with active recall in between. First pass: read through and highlight anything you don't know. Second pass: close the book and try to explain each domain from memory. The gaps you find are where you need to focus. The CSA Cloud Controls Matrix spreadsheet is dense. I used it as a reference, not a study tool. What worked better was the ENISA cloud security guide and the NIST SP 800-144 guidelines. These gave me the contextual understanding that the exam questions are built on. The CCSK doesn't ask "what is encryption" — it asks "which encryption approach aligns with CSA guidance for a specific cloud deployment scenario." Here's something I wish someone had told me: the exam draws heavily from the CSA Top Threats to Cloud Computing report. If you haven't read that, spend time on it. Questions about threats like abuse of credentials, insecure APIs, and misconfiguration show up repeatedly. Understanding the threat landscape matters more than memorizing control definitions.
When I took my first practice exam, I scored around 55%. The questions felt familiar but the scenarios made me second-guess myself. I switched to a different study approach — I started reading each practice question aloud and explaining why the wrong answers were wrong, not just why the right answer was right. That changed my score from 55% to 78% over the next two weeks. The act of articulating the reasoning forced me to understand the material at a deeper level.
Known Limitations and Caveats
The CCSK v4 is a foundational-level certificate. It tests breadth, not depth. Don't expect it to prepare you for hands-on cloud security work. It will give you the vocabulary and framework awareness, but you'll still need practical experience to apply it. I passed the exam and still struggled in my first real cloud security role because I couldn't translate the framework language into actual configuration tasks. The exam also references specific CSA documents that get updated. If you're studying from older materials, some questions may reference controls or guidance that has since been revised. Always verify you're using the most current study guide from CSA's website. The v4 update itself addressed several of these gaps, but keeping your materials current matters. There's no lab component. If your goal is hands-on cloud security skills, consider pairing CCSK with a technical certification like CCSP or a vendor-specific security course. CCSK gives you the policy and governance foundation. Something like the AWS Certified Security – Specialty or Azure Security EngineerAssociate will fill the technical gap.
What to Expect on Exam Day
The exam is delivered through Pearson VUE, either at a test center or online. Online proctoring requires a quiet room, a clear desk, and a functional webcam and microphone. I took it at home and the proctor checked my room setup for about ten minutes before starting. Make sure you have your ID ready and your testing space is prepared in advance. Technical issues during the exam are rare but stressful when they happen. The 90-minute window is enough if you don't overthink each question. I finished with about twelve minutes to spare. The questions that made me pause the longest were the scenario-based governance ones where two answers felt equally correct. For those, I went back to first principles — what does CSA framework guidance prioritize? Governance before technology, risk assessment before remediation, shared responsibility clarity before control implementation. That heuristic got me through most of the tough ones. If you're preparing for the exam, start with the CSA official study guide, supplement with NIST and ENISA references, and do at least one full timed practice exam before scheduling. The gap between reading the material and answering exam-style questions is real. Bridge it early.