Working with Cisco Ise Ordering Guide — What It Actually Is
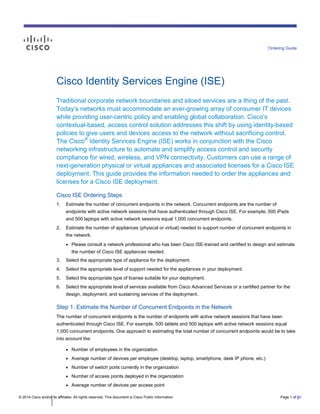
When you first land on a Cisco Ise Ordering Guide, you might expect a clean table that maps product names to SKUs. In practice it is less like a menu and more like a maze with a few dead ends. I have gone through this enough times now that I know where the tripwires are. The ordering guide itself is a Cisco-published reference document that tells you which parts number goes with which deployment size, feature bundle, and subscription term. It is the thing your procurement team will ask for before they will cut a purchase order. The real problem is that the guide does not always talk in a single language. You will see part numbers for perpetual licenses, subscription licenses, technology packages, and professional services all layered together. If you miss one line about whether a bundle includes a specific module, you end up waiting six weeks for a replacement order. I learned that the hard way once when I ordered what I thought was a complete ISE implementation package, only to discover the order did not include the Mobility Service Engine component we needed for wireless onboarding. That missing piece sat on my desk for three weeks while I tried to figure out whether I could add it later or had to cancel the whole order.
How to Read a Cisco Ise Ordering Guide Without Losing Hours
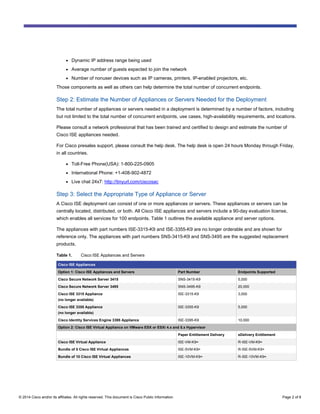
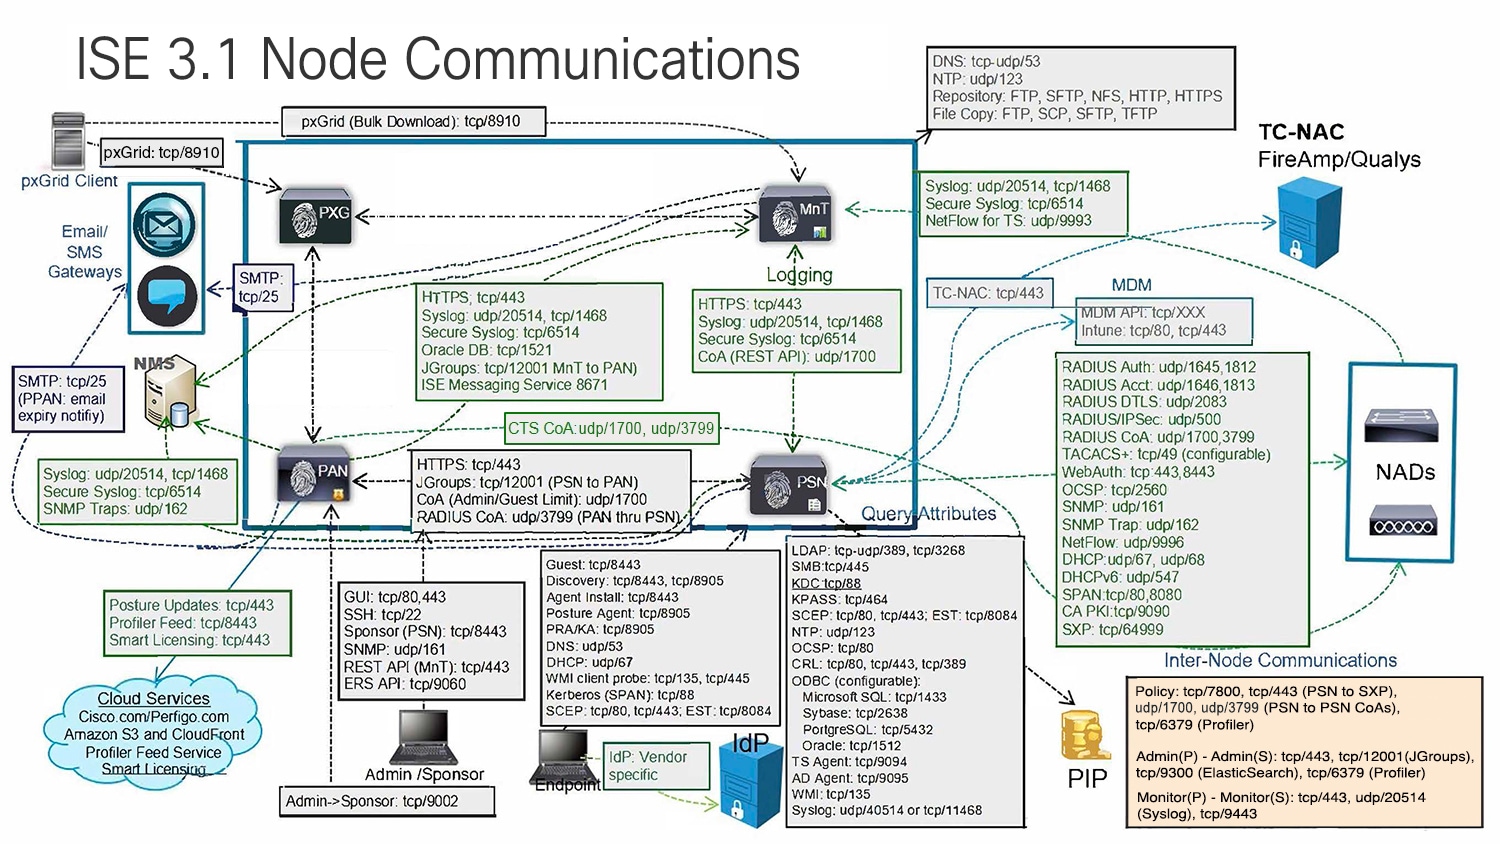
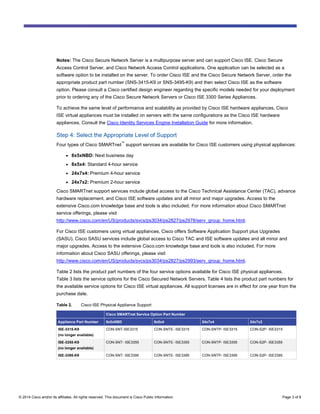
Start by locating the SKU table for your deployment tier. Cisco typically organizes these by Small, Medium, Large, and Very Large installations, with thresholds based on the number of endpoints and Policy Service Nodes you plan to run. The guide will list a base license part number, then a series of optional add-ons below it. Do not skip the footnote section. That is where Cisco puts the stuff that actually matters, like which subscription term gets you price protection or whether a particular hardware appliance ships with licenses already baked in. One thing the guide makes reasonably clear is the distinction between the Administration, Monitoring, and Policy Service roles. You pick the role bundles based on what your architecture requires, not on what sounds impressive. A dual-PSN high availability pair with a dedicatedAdministration node is the most common production pattern, and the ordering guide reflects that with specific part numbers for each. If you are running a smaller deployment, Cisco also offers a combined Personal Edition path that collapses several roles into a single SKU. It works fine for labs and offices under roughly 100 endpoints, but it hits a wall pretty quickly if you start pushing certificate-based device onboarding at scale. The licensing model shifted over the years, and the ordering guide still carries artifacts from both the old and new structures. You will see references to Technology Packages alongside Base Plus bundles. A Technology Package is essentially a feature add-on license, like Native MDM support or Threat Control. These are priced separately and stack on top of a base subscription. I once misread a Technology Package line item as included in a bundle and wound up with a gap in profiling coverage that took two months to correct because the patch license had to flow through a separate procurement queue.
The Parts You Should Actually Check Before You Submit
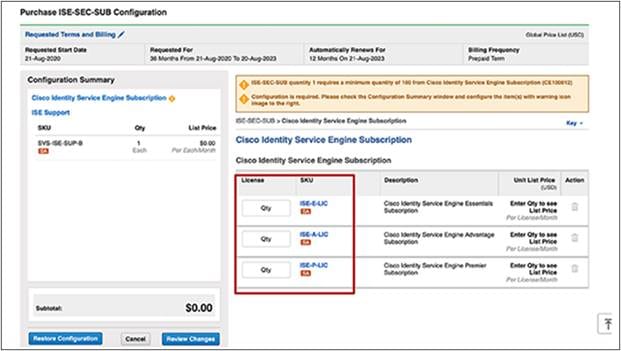
There are three things I always verify before I send an order through. First, confirm the subscription term. Cisco typically offers one-year, two-year, and three-year terms, and the per-node cost drops noticeably at the longer commitments. If your project timeline is uncertain, a one-year term gives you flexibility but costs more overall. Second, check whether you are ordering hardware appliances or virtual instances. The part numbers differ, and mixing them in the same order can cause reconciliation issues at the vendor level. I prefer virtual for dev and staging because the lead time is shorter, but production deployments usually go with the dedicated appliances for consistent throughput. Third, and this is the one most people miss, look at the upgrade path part numbers. Cisco has a habit of discontinuing older license tiers when new versions ship, and the ordering guide rarely warns you about that in bold type. I found this out when upgrading from ISE 2.7 to 3.1. The old perpetual licenses were not directly transferable to the new subscription model, and I had to place a bridge order that cost roughly fifteen percent more than a fresh purchase would have. The ordering guide does mention the upgrade path somewhere in an appendix, but you have to dig for it.
Get the Full Details
Where the Ordering Guide Falls Short
The main limitation of any Cisco Ise Ordering Guide is that it assumes you already know your deployment topology. If you are still figuring out whether you need separate Authentication and Policy nodes or can consolidate, the guide will not help you decide. It assumes the architecture is fixed and then lists SKUs against that assumption. Another issue is regional availability. Some part numbers exist only in certain Cisco regions, and the guide does not always flag which ones. I once tried to order a monitoring node license for a site in APJ and discovered the SKU was not registered in that region's catalog. It took a call to the Cisco account team to resolve, which delayed the order by about ten business days. There is also the matter of accessory software. The ordering guide focuses on the core platform licenses, but a real ISE deployment usually needs a RADIUS client license set, SNMP polling licenses for NPM integration, and sometimes a WebAuth template license. These are listed in separate sections of the guide, and they are easy to overlook. I stopped assuming anything was included after my second order came back incomplete.
A Practical Walkthrough
Here is how I typically work through a new order. I start by confirming the endpoint count and the node roles from the network design doc. Then I pull up the ordering guide and find the base bundle for that tier. I check the subscription term and pick three years unless there is a good reason not to. Next I scan the Technology Packages for anything my use case needs, like Profiler Plus or TrustSec. I add the appropriate SKUs for each. Then I verify the HA pair part numbers if I am doing production. Finally I do a line-item review against the original scope to catch anything missing. This process usually takes me about forty-five minutes for a standard deployment, longer if the topology is nonstandard. If you are doing a very small setup, the ordering guide offers a simplified path through the Personal Edition bundle. It covers the basics, and for a single site under fifty devices it is adequate. But I would not rely on it if you plan to grow beyond that. The licensing model becomes cumbersome once you need to add nodes, and you end up placing multiple orders instead of one clean purchase. The ordering guide is not a perfect tool. It is a reference document written for procurement professionals who may not know the difference between an Administration node and a Policy Service Node. That mismatch means the onus is on you to read carefully and verify assumptions before submitting. I have learned to treat every line item as provisional until it shows up on the packing slip. That habit has saved me more than once.