What the CJIS Limited Access Certification Actually Is
The CJIS Limited Access Certification is a compliance requirement under the FBI's CJIS Security Policy. It's not a test you study for with flashcards. It's a short e-learning module followed by an assessment you take once per year. You complete it through your agency's designated training portal — usually a platform like GovTrain or directly through the CJIS Division's own system. The "test answers" people search for are just the correct responses to the multiple-choice questions at the end. There are usually five to ten questions, and you need a passing score of 80% or higher. Most people get it right on the first try because the material is straightforward. I've walked several new hires through this process over the years. The frustrating part isn't the content. It's the logistics. Your agency might require you to complete it within 30 days of hire, or before you're granted any system access at all. If you're working at a state or local law enforcement agency, a court, or a vendor that handles CJI data, you'll need this certification on file. The CJIS Security Office tracks it, and agencies get audited on compliance.
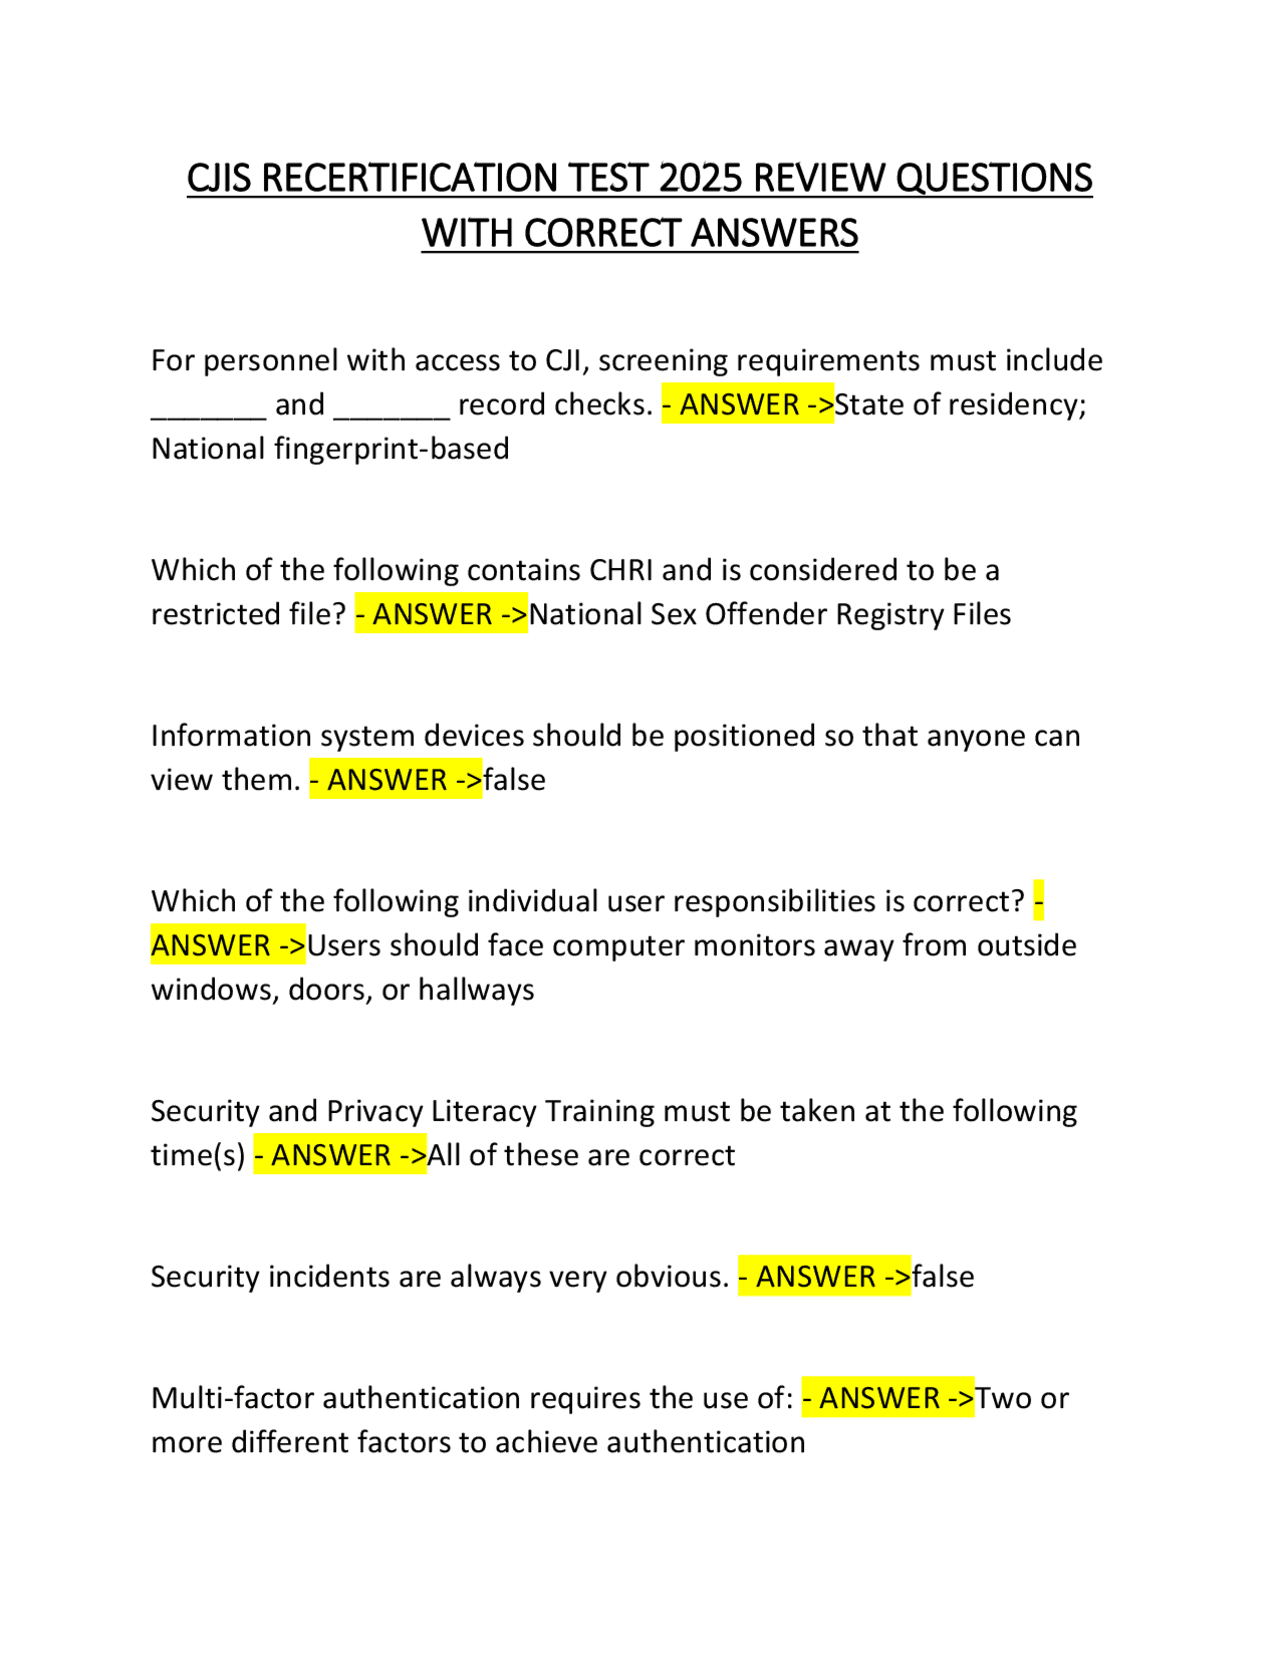
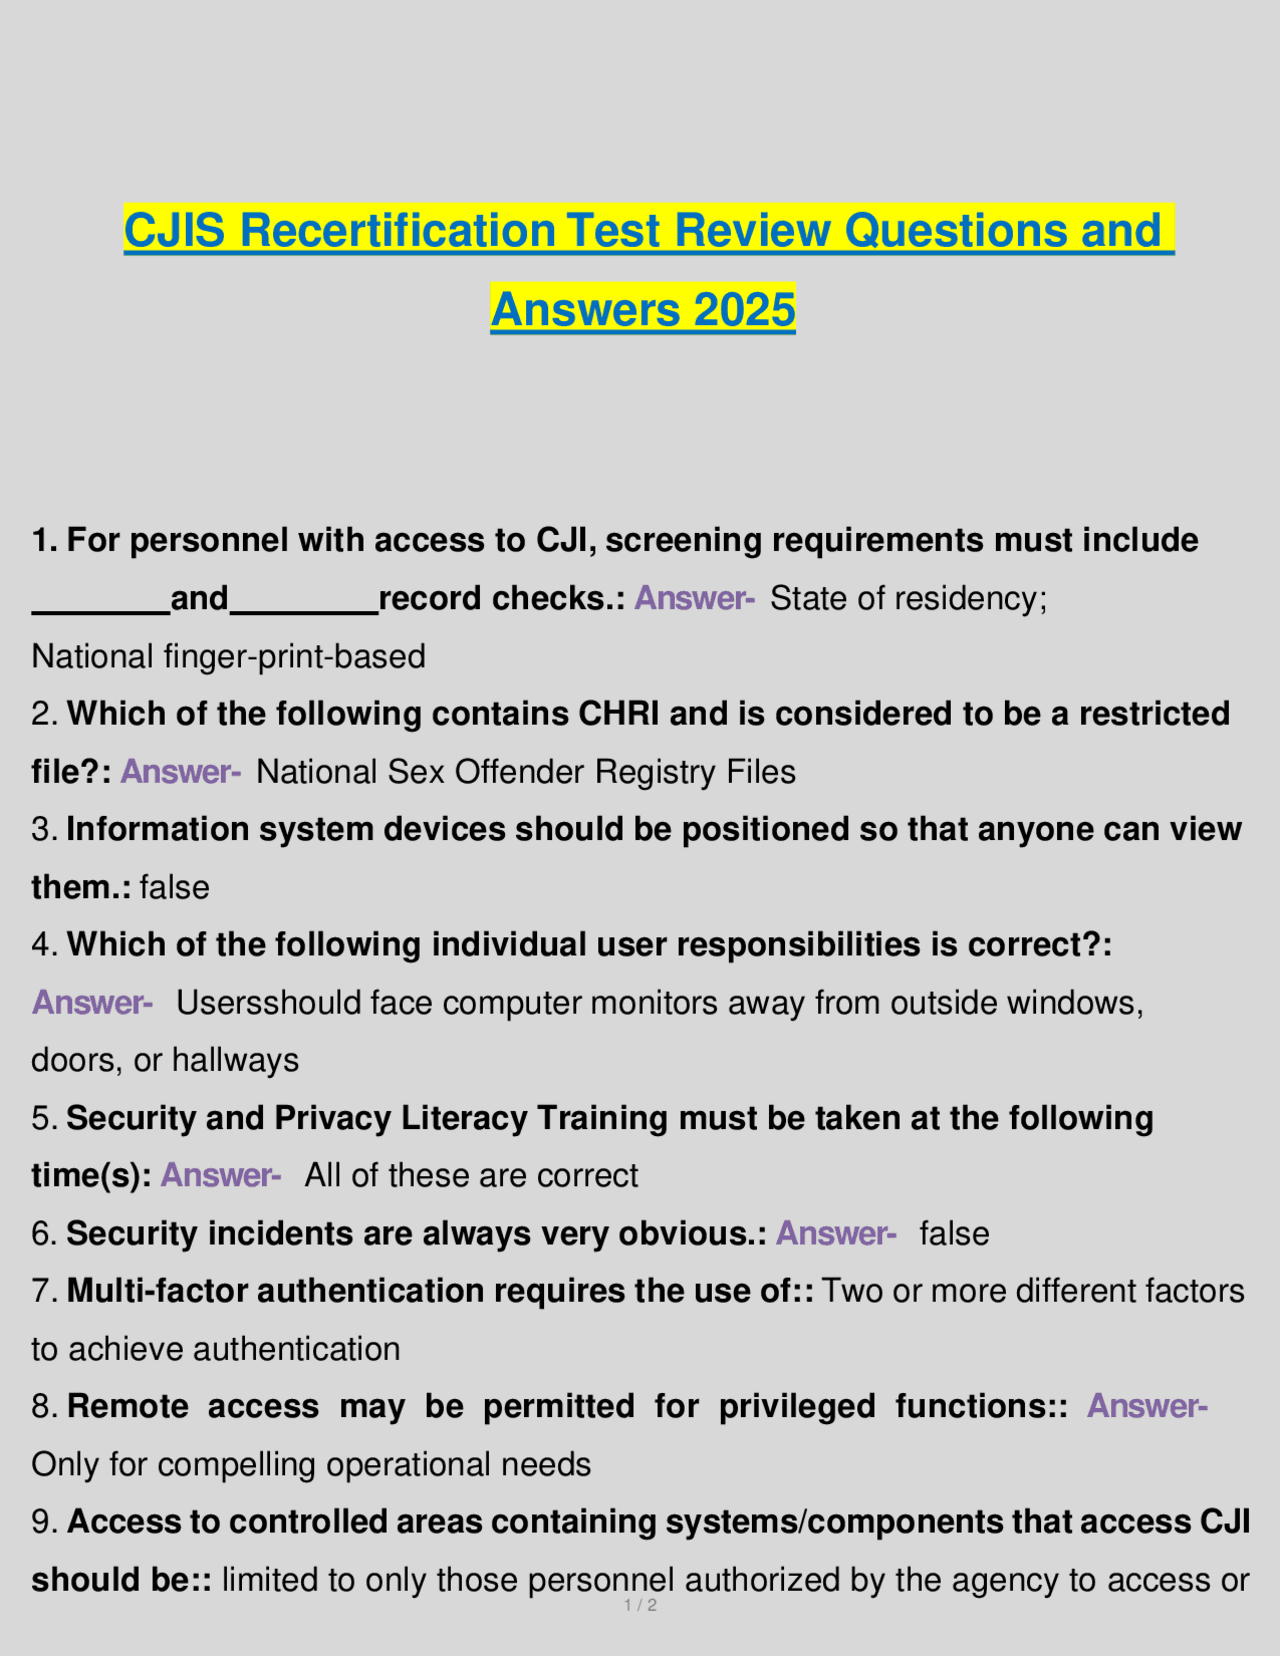
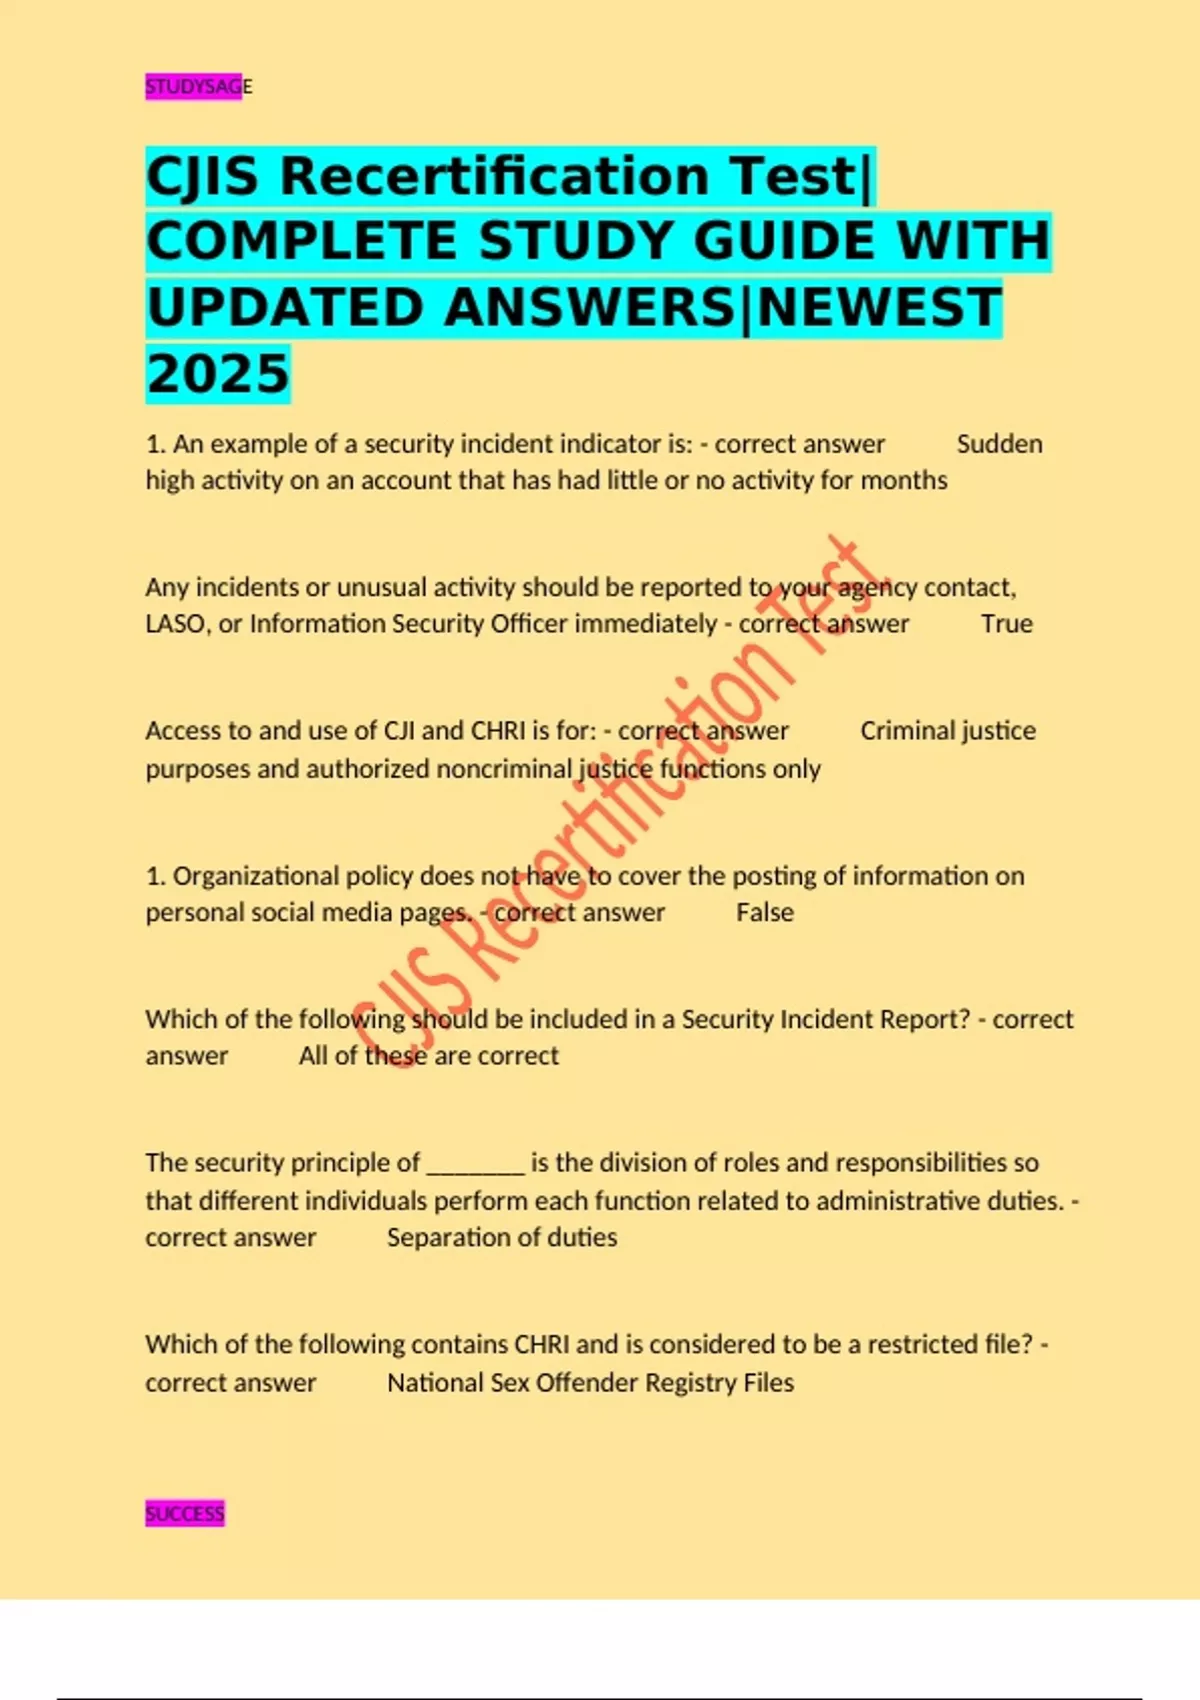
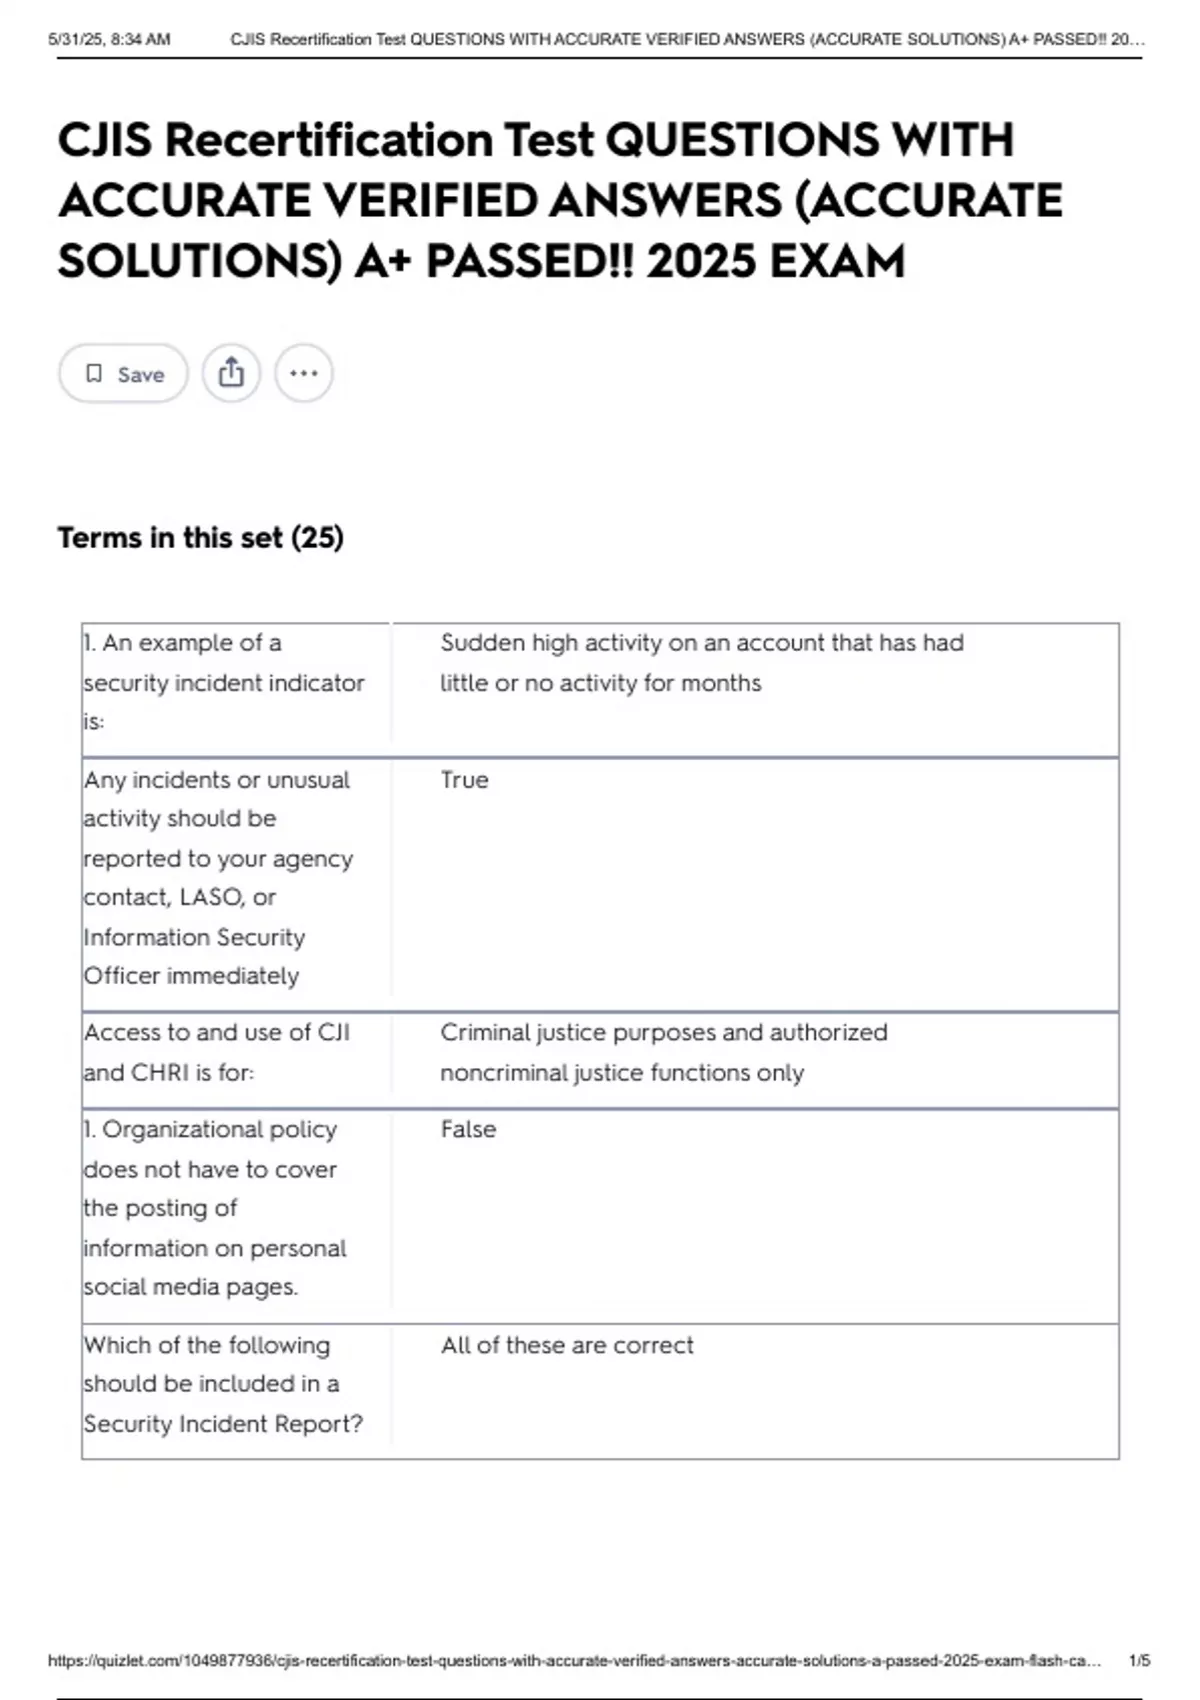
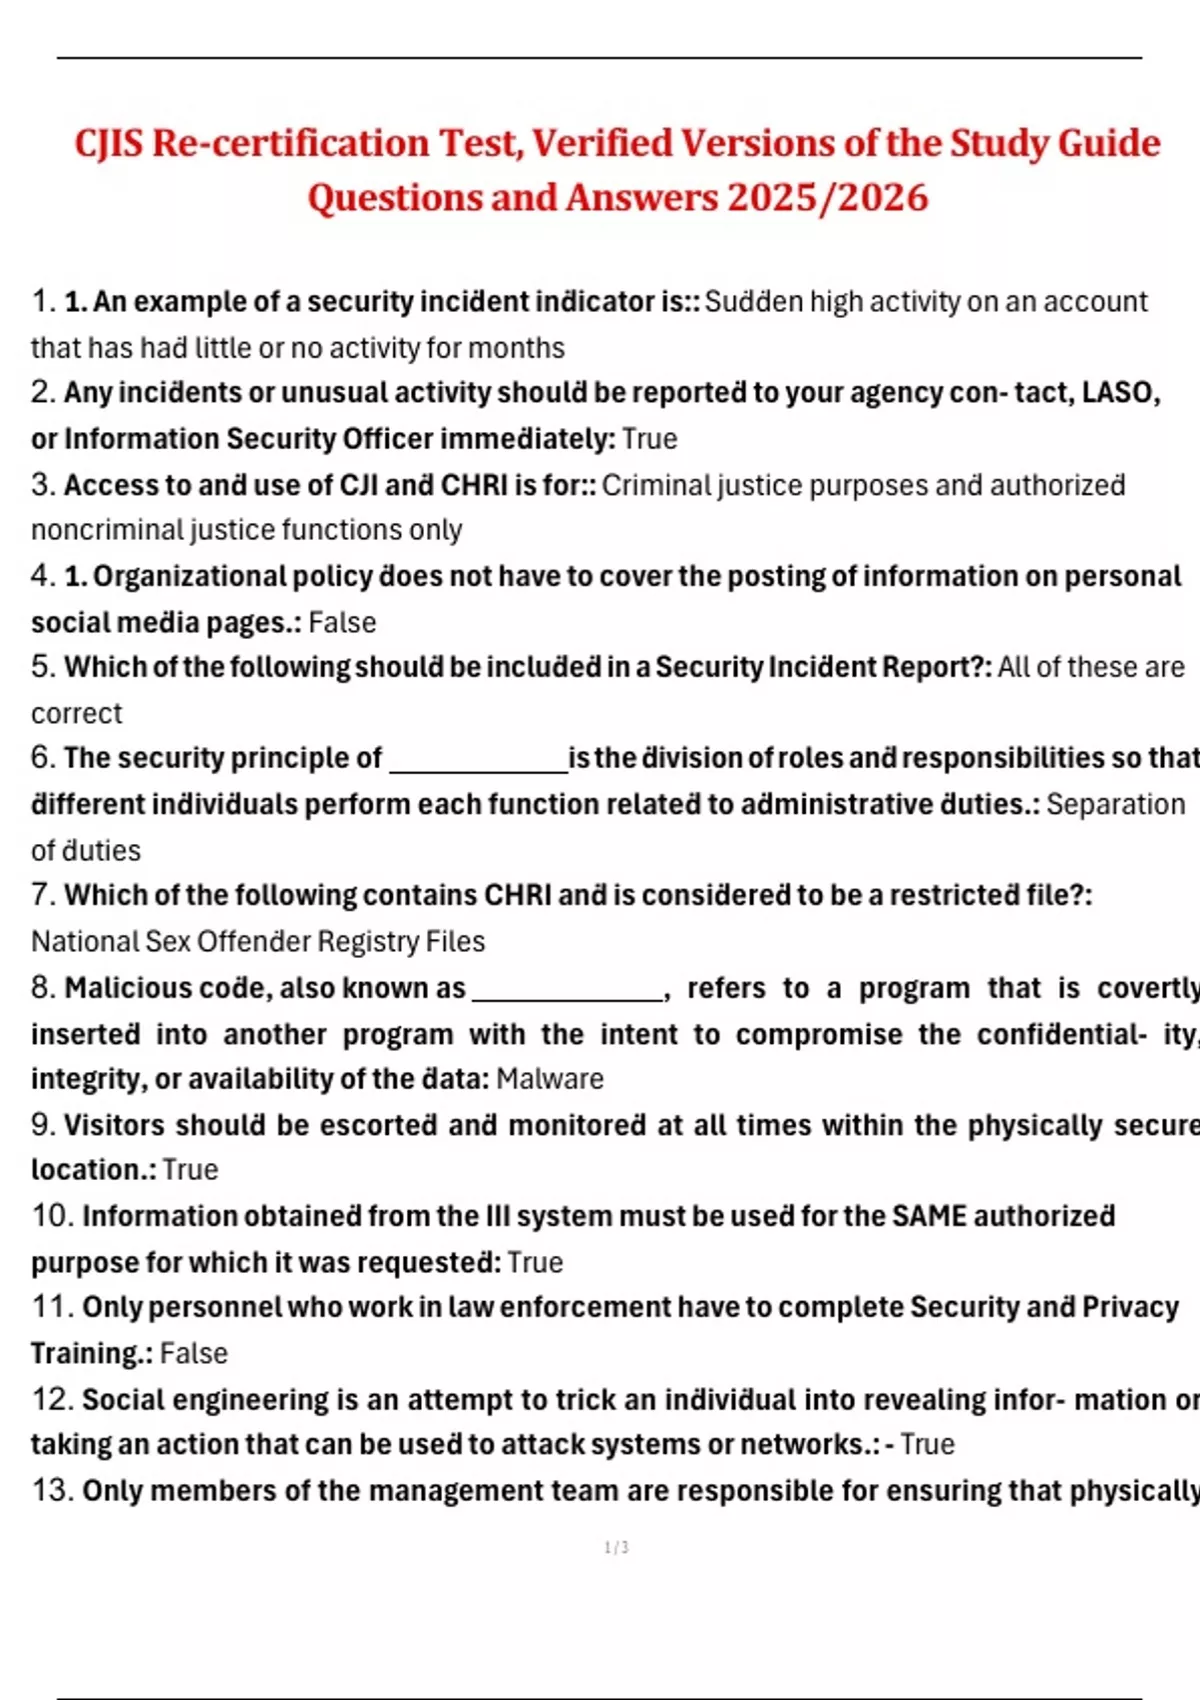
Cjis Limited Access Certification Test Answers
Here's what you actually need to know to pass. The questions cover three main areas: authentication procedures, data handling and storage, and access controls. The authentication section asks about multi-factor authentication, password requirements, and locking your screen when you walk away. The data handling section covers how to properly encrypt CJI, where you can store it, and what counts as a valid medium. The access controls section deals with role-based access, least privilege, and when to request new access versus when to revoke it. Some people try to memorize specific answer keys they find online. That won't work reliably because the questions can be randomized, and the assessment platform may shuffle the order. What works instead is actually reading the module material. The answers are in the training content itself. I learned this the hard way back in 2022 when a colleague of mine spent an hour looking up answers online and still failed because the questions on his assessment didn't match the ones he'd found. He went back, read through the module in about twelve minutes, and passed on retake.
How to Complete the Certification
Step one is getting your agency to register you with the CJIS training system. This is usually handled by your supervisor or compliance officer. They'll create a user account and send you a link. Step two is completing the required modules. The Limited Access module takes roughly 20 to 30 minutes. You'll watch video segments, read policy excerpts from the CJIS Security Policy, and occasionally respond to inline knowledge checks. Step three is the final assessment. You get two attempts. If you fail the first one, you usually have to wait 24 hours before retaking it, though this depends on your agency's configuration. One thing that catches people off guard: the CJIS Security Policy was updated significantly in version 5.4, and again in 5.5. Some older answer guides floating around the internet are based on outdated policy. If you're using someone else's study notes, make sure they reference the current version. The changes around 2023 mostly affected the remote access and mobile device sections, which showed up in my last certification cycle as a couple of questions I hadn't seen before.
Get the Full Details
Common Pitfalls
The biggest mistake I see is people rushing through the module without actually reading the material. They click through the videos at 2x speed, skim the policy documents, and then wonder why they missed a question on acceptable media for storing encrypted CJI. The second mistake is not reading the question carefully. A few questions are worded to test whether you noticed a specific detail. For example, one question asks about the difference between "encrypting CJI at rest" and "encrypting CJI in transit." Both are required, but the policy specifies different standards for each. NIST 800-111 covers one, NIST 800-122 covers the other. Another issue is time limits. Some agencies configure their CJIS training portal with a session timeout. If you leave the module open too long, you get logged out and lose your progress. I've had this happen twice. The workaround is simple: save your progress frequently and don't open other tabs while you're in the module. If your session times out, just log back in and you'll pick up where you left off in most configurations.
What Happens After You Pass
Your passing score gets recorded in the CJIS system and is tied to your agency's account. You don't get a certificate to frame. You get a completion record. Your agency is responsible for maintaining that record and producing it during audits. The certification is valid for one year from the date you pass. You'll need to retake it annually. Some agencies track this for you and send reminders. Most don't, and you'll find out the hard way when your access gets flagged during a compliance review. There's no penalty for failing the assessment beyond having to wait and retake it. There is a penalty for not having a current certification on file, and that comes from your agency, not from CJIS. Agencies take this seriously because non-compliance can affect their ability to access CJI at all. The FBI can suspend an agency's CJIS access if too many of their personnel are out of compliance. That's a nuclear option, but it's happened.
Bottom Line
The CJIS Limited Access Certification isn't difficult if you put in the twenty minutes it takes to properly complete the module. The questions are directly tied to the material. Looking for shortcuts usually costs you more time than it saves. If you're doing this for work, treat it like the compliance checkbox it is, finish it quickly and correctly, and set a reminder on your phone for twelve months from now so you don't forget the annual renewal.