Cobit 5 For Information Security Is More Troublesome Than It Should Be
Most organizations treat Cobit 5 as a governance framework that magically solves their information security problems. It does not. What it actually does is give you a structure to map your security practices against 37 defined processes. That mapping exercise is where most people get stuck, usually because they expect the framework to tell them what controls to implement. It does not. It tells you what processes should exist, and the gap analysis part is entirely on you. The first thing you need to do is pick your scope. Cobit 5 has enterprise-level and domain-level approaches. If you are a mid-market company running security for one business unit, trying to apply the full enterprise model will consume about 800 hours of effort for minimal return. Start with the four governance objectives: ensuring framework suitability, ensuring stakeholder needs are met, ensuring risk optimization, and ensuring resource optimization. Those four cover roughly 60 percent of what security audits actually test for in practice. After that, map your existing policies to the 37 COBIT 5 processes. I spent three weeks doing this exercise at a client engagement and found that about 40 percent of their documented policies did not map cleanly to any COBIT process. They had written their own process for handling third-party vendor risk assessments that looked nothing like APO13. That is not necessarily a failure. It just means your control framework is partially customized, and you need to decide whether to adapt your policy to fit COBIT or document the deviation and justify it. The second option takes more effort during an audit but is sometimes the right call.
Process maturity assessment is the next step. COBIT 5 uses a scale from 0 to 5 for each process. A maturity level of 2 means processes are repeatable but not yet institutionalized. Level 3 means they are defined and documented. Most organizations I have worked with sit at level 2 across the board for their security processes. The jump from 2 to 3 is where the real work happens, and it usually requires formalizing SOPs that either do not exist or exist only in someone's head. This transition typically takes 4 to 6 months of dedicated effort for a team of three to five people.
The Process Maturity Model Is Where Things Get Messy
COBIT 5 defines six maturity levels for each process, and here is the part most practitioners miss: the model assumes a linear progression from ad hoc to optimized. Your actual security operations do not work that way. You might have an incident response process at maturity level 4 in some areas and level 1 in others, depending on which tools you use and how recently you updated procedures. The framework does not account for this variance well. I worked through a scenario where we had automated vulnerability scanning at maturity level 4 but manual patch approval workflows sitting at level 2. The auditors wanted a single maturity rating for the entire integrated process. There is no guidance in the framework for handling hybrid maturity states within a single process domain. We ended up splitting the process into two separate assessments and documenting the variance explicitly. It satisfied the auditors, but it also highlighted a genuine gap in the maturity model's design. Another thing that catches people off guard: COBIT 5 does not provide specific control objectives for technical security implementations. It describes what should be managed, not how to manage it technically. If you are looking for guidance on encryption standards, access control matrices, or network segmentation models, you will not find them here. You need to layer ISO 27001 or NIST SP 800-53 on top of COBIT 5 for the technical detail. This combination is standard practice but it is worth noting because it means COBIT 5 alone cannot serve as a complete security framework.
Get the Full Details
A Real Problem I Faced Mapping Controls
During an implementation project for a financial services client, we encountered a situation where their existing cybersecurity policy had been built around the NIST Cybersecurity Framework. Every control objective referenced NIST categories: Identify, Protect, Detect, Respond, Recover. COBIT 5 uses a completely different taxonomy organized around governance and management objectives. Mapping NIST to COBIT 5 is possible but not straightforward because the two frameworks categorize similar activities differently. The specific problem arose with their third-party risk management process. Under NIST, this fell under the Protect category as PR.IP-12. Under COBIT 5, it split across APO13 (Manage Risk), BAI09 (Manage Changes), and DSS05 (Manage Security Services). Our mapping exercise produced 14 cross-references for a single business process. The auditor who reviewed our work questioned whether we were double-counting or understating coverage. We resolved this by creating a control ownership matrix that showed which COBIT process owned the governance aspect and which owned the operational aspect, then assigned a single process owner per COBIT process while noting the NIST equivalents as supplementary references. This took about two weeks to build and maintain but prevented the duplication argument from derailing the audit. The workaround I recommend for anyone doing this mapping: build your initial matrix in a spreadsheet, then validate it against an actual audit checklist from the regulatory body relevant to your industry. Financial services should use FFIEC or SEC guidelines as the validation source. Healthcare should use HIPAA. Generic enterprise can use SOC 2 criteria. If your COBIT mappings do not align with the regulatory expectations, adjust the mapping before presenting it to auditors.
What COBIT 5 Gets Wrong About Information Security
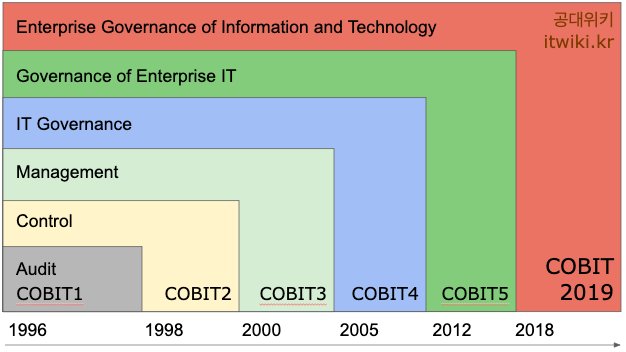
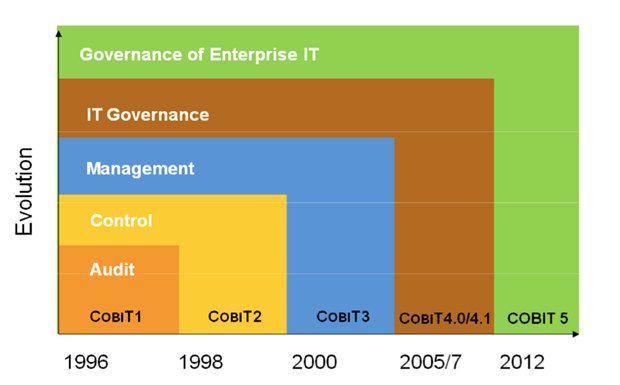
The framework was published in 2012 and updated in 2018. Neither version adequately addresses cloud security governance in a way that feels current. The DSS category has process DSS05 covering security services, but it treats cloud as an infrastructure concern rather than a governance concern. If you are running workloads across AWS, Azure, and GCP simultaneously with different security configurations, COBIT 5 gives you no structured way to govern that complexity. You end up applying the same process descriptions to fundamentally different environments, which produces control gaps that the framework does not help you identify. Another limitation is the absence of a dedicated information security domain. COBIT 5 has five domains: Evaluate, Direct and Monitor; Align, Plan and Organize; Build, Acquire and Implement; Deliver, Service and Support; and Monitor, Evaluate and Assess. Information security is embedded across all of them rather than treated as a standalone function. This design choice makes sense from a governance perspective but creates practical confusion for security teams who need to demonstrate that their function operates independently from general IT operations. If your organization requires a clear separation between security governance and IT governance for regulatory reasons, you will need to define that boundary yourself. COBIT 5 does not provide it. The maturity model itself has a structural weakness: it rewards documentation over effectiveness. A process can achieve maturity level 4 with thorough documentation and consistent execution but still fail to prevent incidents because the underlying controls are poorly designed. I have seen this happen twice in my experience. In both cases, the organization scored well on COBIT 5 maturity assessments while their actual security posture remained weak. The framework measures how well you follow your own processes, not whether your processes are good enough. This is a fundamental distinction that the literature does not emphasize enough.
Practical Implementation Timeline
For a typical organization with 500 employees and basic IT infrastructure, a realistic timeline for a COBIT 5 for information security assessment is 12 to 16 weeks. The breakdown is roughly three weeks for scope definition and stakeholder alignment, four weeks for process mapping against existing controls, three weeks for maturity assessment, two weeks for gap analysis, and two to four weeks for remediation planning. This assumes you have at least one person dedicated full-time to the effort and access to your existing policy documentation. If your policies are incomplete or outdated, add another four to six weeks for policy development before you begin the mapping exercise. Cost estimates vary significantly based on whether you use internal staff or engage external consultants. Internal-only implementations typically run 400 to 600 labor hours. Adding a consultant familiar with COBIT 5 adds roughly $40,000 to $75,000 depending on scope and geography. Certification through ISACA costs approximately $1,750 for non-members and $1,150 for members, including the exam and one year of membership.

When to Use COBIT 5 and When to Choose Something Else
COBIT 5 works well if your primary need is governance alignment and executive reporting. It gives you a structured way to demonstrate that security practices are managed, measured, and aligned with business objectives. If your organization faces regulatory scrutiny from bodies that recognize COBIT frameworks, the investment pays for itself in reduced audit preparation time. The framework is also useful if you are preparing for a SOC 2 Type II audit and need a governance backbone to organize your evidence. It does not work well if your goal is technical security improvement. If you need guidance on network architecture, encryption key management, or endpoint protection strategies, COBIT 5 will not help you. Use ISO 27001, NIST 800-53, or CIS Controls for that purpose. It also does not work well for organizations that are still building their basic security hygiene. Trying to implement COBIT 5 governance processes on top of incomplete or inconsistent security controls usually produces a framework that looks good on paper but fails during actual incident response. Get your foundational controls working first, then layer governance on top. The 2018 update added digital innovation and AI governance considerations, but these sections feel bolted on rather than integrated. The core framework remains unchanged from the 2012 version. If you are starting fresh in 2024 or later, consider whether COBIT 5 is the right choice or whether COBIT 6 or a newer governance framework would better serve your needs. The principles are similar but the 2018 changes address some of the cloud and data governance gaps I mentioned above.
One final note that many people overlook: COBIT 5 assumes a stable organizational structure. If your company undergoes mergers, acquisitions, or significant restructuring, your process mappings and maturity assessments become quickly outdated. I have seen two organizations where a single acquisition rendered six months of COBIT 5 mapping work obsolete within two weeks. Budget for ongoing maintenance, not just initial implementation. Plan for quarterly reviews of your process mappings and annual maturity reassessments to keep the framework relevant.