Building a Coding Checklist That Actually Works
Most coding checklists are garbage. I've seen people spend hours building elaborate multi-page documents that end up collecting digital dust because nobody actually uses them. A good one takes about twenty minutes to set up properly, and once it's in place, it catches issues that would otherwise take days to track down. The reason they fail is simple: people write them at the wrong time. You shouldn't draft a Coding Checklist before you've shipped a few projects without one. Once you've had enough code committed to remember the specific errors that keep sneaking through, then you write it down. I learned this the hard way when I spent three days building a perfectly formatted checklist for a React project, only to realize half the items didn't apply because we'd changed our routing approach mid-sprint. Started over from scratch after that. Taken five minutes the second time around.
What a Coding Checklist Actually Is
A Coding Checklist is a practical, living document that captures the repeating tasks, verification steps, and gotchas you encounter across your development workflow. It's not a tutorial. It's not documentation for someone who has never touched your codebase. It's a personal reference for things you already know but keep forgetting under deadline pressure. Think about the last time you deployed something and immediately noticed three bugs you'd definitely have caught if you had just paused and run through your usual validation steps. That gap is exactly what a checklist fills. The brain is not designed to hold procedural details reliably when you are already juggling context, and nobody exceptions made.
How to Build One Without Overthinking It
Start with a plain text file or a note-taking app. Not a fancy tool. Not a project management platform. Something boring. I use a single markdown file stored in my dotfiles repository, synced across machines. It lives at the root level so it's always visible. The tool doesn't matter. The habit does. Gather your material first. Open your recent commit history and scan for commits that look like "fix", "hotfix", "cleanup", or "update". Go through the last two months of work and note every time you caught an issue that should have been caught earlier. Group similar patterns together. You'll find that most checklists boil down to roughly eight to twelve recurring categories. Here is what mine looks like after about six months of iteration:
Get the Full Details
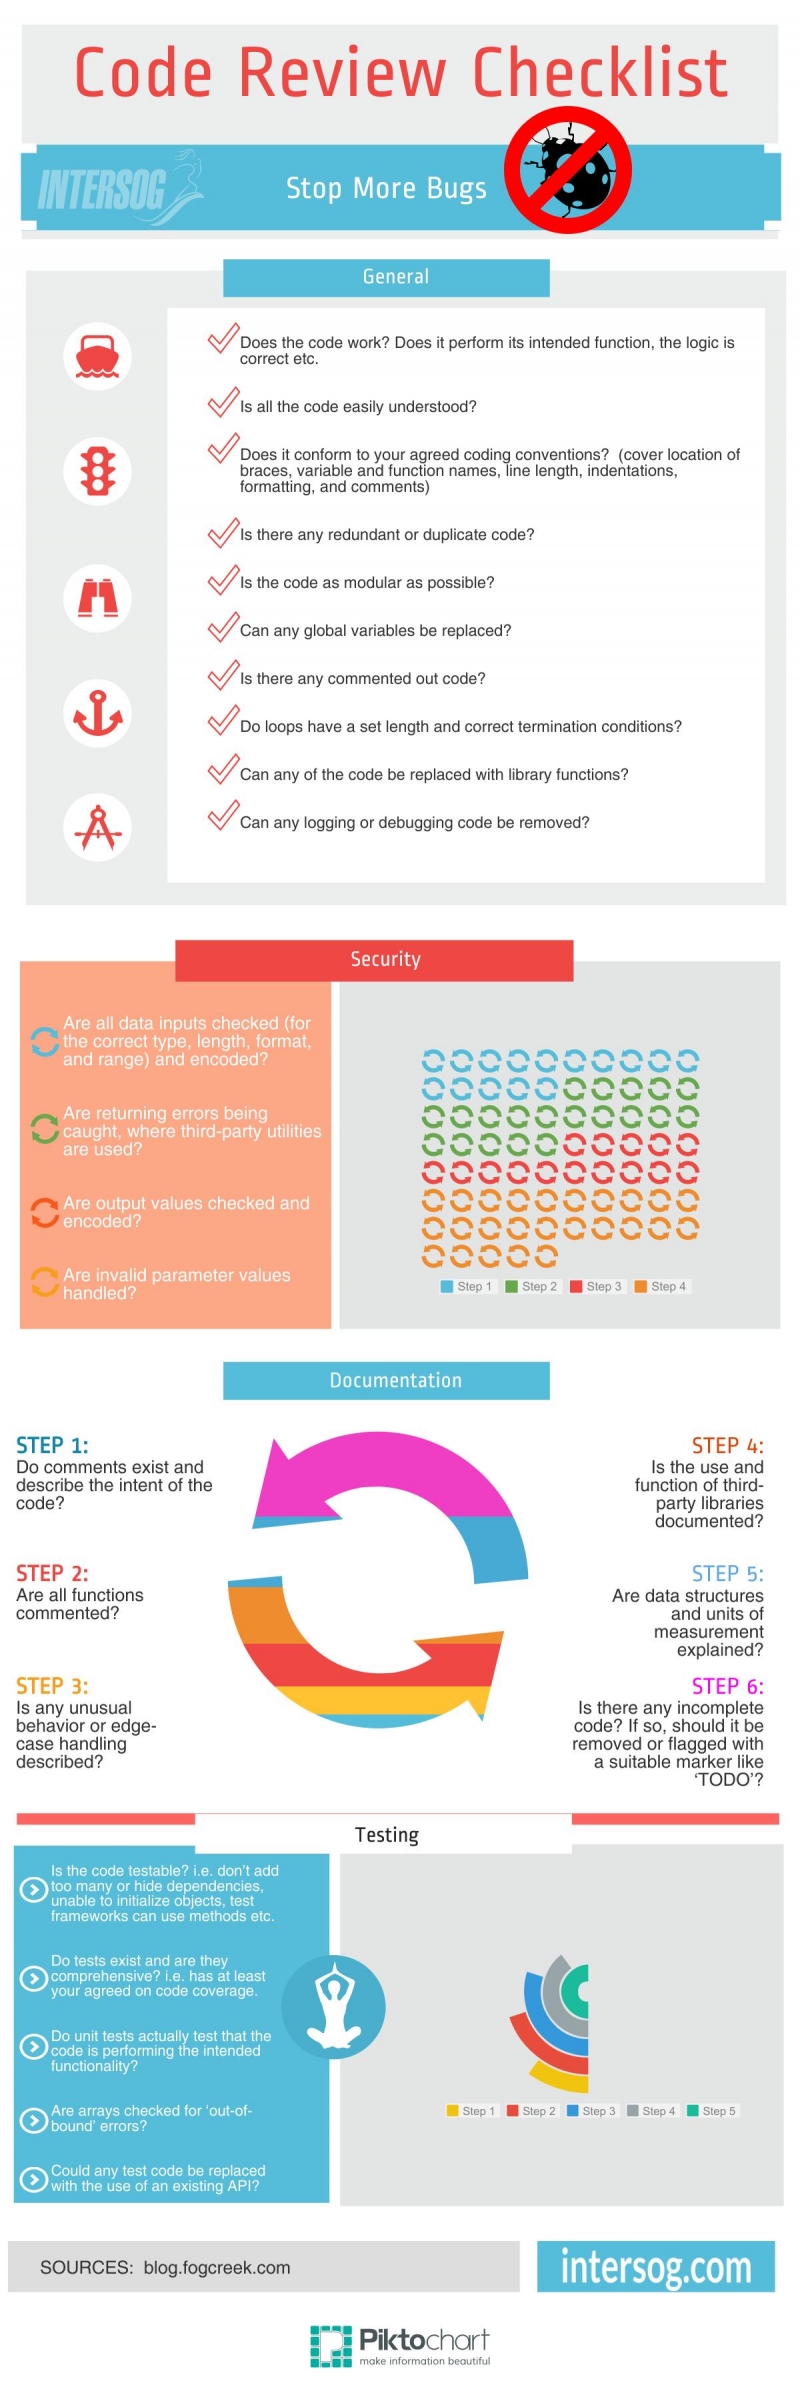
Pre-commit: Lint passes, type checks clear, no console.error statements left in the code, .env variables verified against the staging environment. Before deployment: Database migrations tested on a duplicate schema, environment variables confirmed in the target system, dependent services checked for breaking changes. Post-deployment: Smoke test hit, health endpoint returns 200, error tracking dashboard shows no spike in the last five minutes, critical user flows tested on production.
Documentation: README updated if config changed, API endpoints documented if new routes were added, version bumps reflected in changelog. That's it. Eight items across four categories. Takes about ninety seconds to scan before any significant push.
The Edge Case Nobody Warns You About
Checklists fail when they become static. I discovered this when we migrated a Node.js service from Express to Fastify and everything in our existing list became irrelevant overnight. Half the items were now wrong, and the ones that were still valid were buried under outdated procedures. I had a PR sitting there with failing tests for forty-five minutes because the checklist didn't mention that Fastify requires explicit schema validation while Express lets that slide by default. The fix was adding a migration sub-section to the pre-deploy checklist with Fastify-specific steps. Took ten minutes. I wish I'd done it that day instead of debugging blind. The rule is straightforward: whenever you change your stack, framework, deployment pipeline, or testing strategy, immediately audit your checklist. Cross out what no longer applies. Add what you just learned the hard way. If you don't do this within forty-eight hours of the change, you will forget and the list becomes noise again.

Advanced Nuances Beginners Miss
One thing most people don't realize is that a checklist should include negative assertions, not just positive ones. "Verify the feature works" is almost useless. "Verify the feature works AND verify the old behavior still functions" is actionable. Regression detection is the whole point. When I audited our codebase after a major refactor last year, I found we had zero test coverage on the login flow because our checklist only ever included "login works" without specifying that existing session handling must remain intact. We shipped a version where users could log in but their existing sessions were invalidated silently. That cost us about six hours of hotfix work and a frustrated support team. Another counter-intuitive point: your checklist should be shorter than you think it needs to be. The moment it passes fifteen items, compliance drops sharply. People start skipping. I saw this firsthand when a teammate maintained a forty-two-item checklist for their Python microservices. He stopped reading it after the twentieth item and just scanned the rest. Eventually he skipped the checklist entirely. I reduced my own list to the core twelve items and now I actually run through every single one before pushing. Length is not the enemy of thoroughness. Brevity is.
Where Checklists Break Down Completely
A coding checklist cannot replace automated testing. If you think checking off items manually is enough to prevent bugs, you are wrong. Checklists catch procedural gaps, not logic errors. They do not run your tests. They do not inspect your code. What they do is ensure you have not forgotten to do something you already know you should do, like running migrations before deployment or verifying environment configuration. If you are in a domain where correctness is critical, like financial systems or medical software, a checklist is a supplementary layer, not a primary defense. You need proper test suites, code review, and static analysis in addition to the checklist. Using a checklist as your main quality gate is like using a seatbelt and calling it a car crash prevention system. The only real downside I have found is maintenance overhead. Checklists drift. They need updating whenever your process changes, and some people treat them as permanent documents when they should be living ones. If you find yourself spending more time maintaining the checklist than it saves you, it is too complex and needs to be cut back, not expanded.
Download a template, start filling it in after your next release cycle, and update it the moment something goes wrong that the list should have caught. That is all there is to it.