Windows isn't one monolithic blob. It's a collection of subsystems that overlap, duplicate, and sometimes contradict each other.
If you've ever opened Task Manager and seen svchost.exe running as twenty different processes, you've already seen the components at work. Each svchost instance is a separate host process group, and they're there because of how Windows was architected over decades. You don't install components in Windows the way you install apps on Linux. They're layered, often redundant, and tightly coupled to the kernel in ways that aren't obvious until something breaks. I spent years troubleshooting enterprise Windows deployments, and the thing that confused most people wasn't any single component. It was the fact that three different components could do the same job depending on which version of Windows you were running. Group Policy used to be registry-based. Then it became policy extensions. Then there were preferences, then CSPs, and suddenly the same configuration could land in different places on Windows 7 versus Windows 10. That's the reality of Components Of Windows Operating System. It's not a clean design. It's accumulation.
Core architectural components
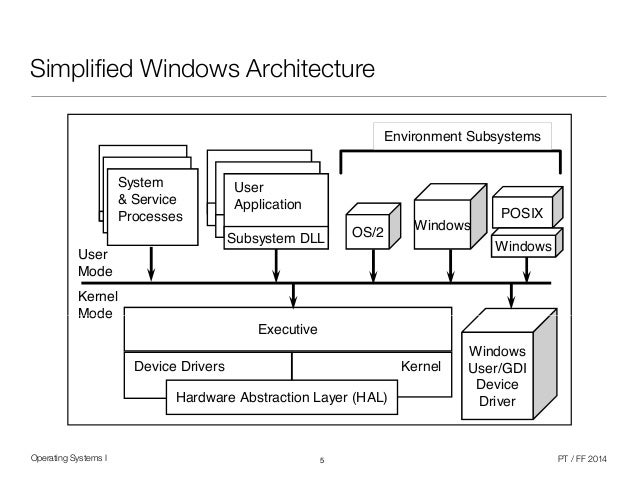
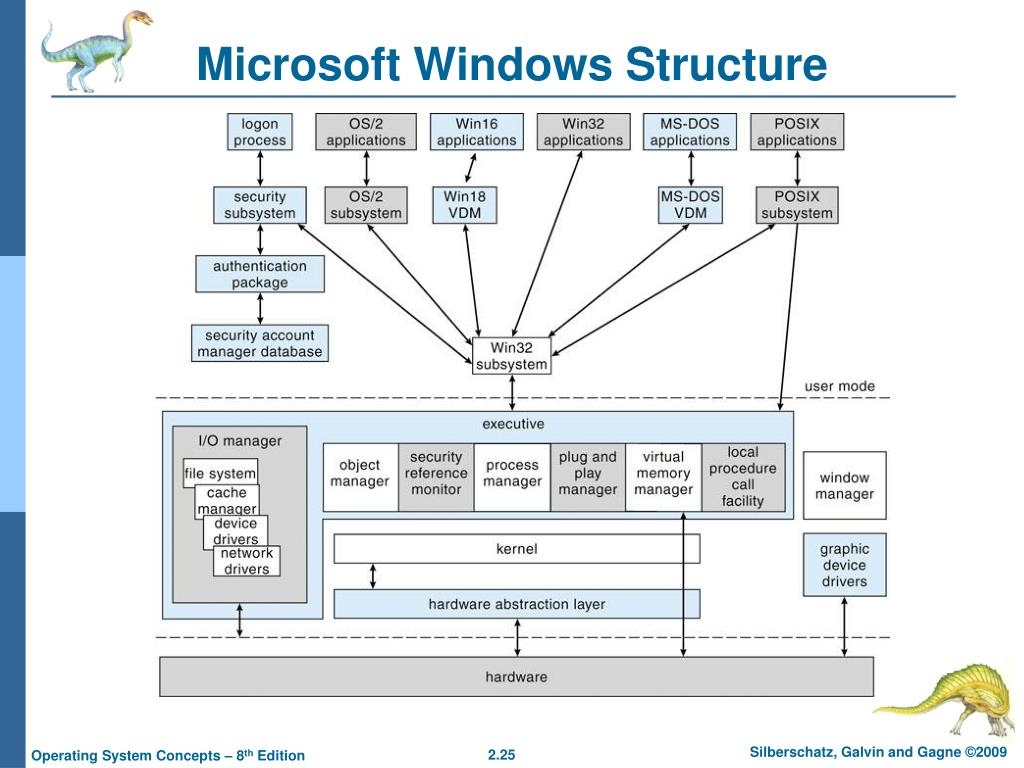
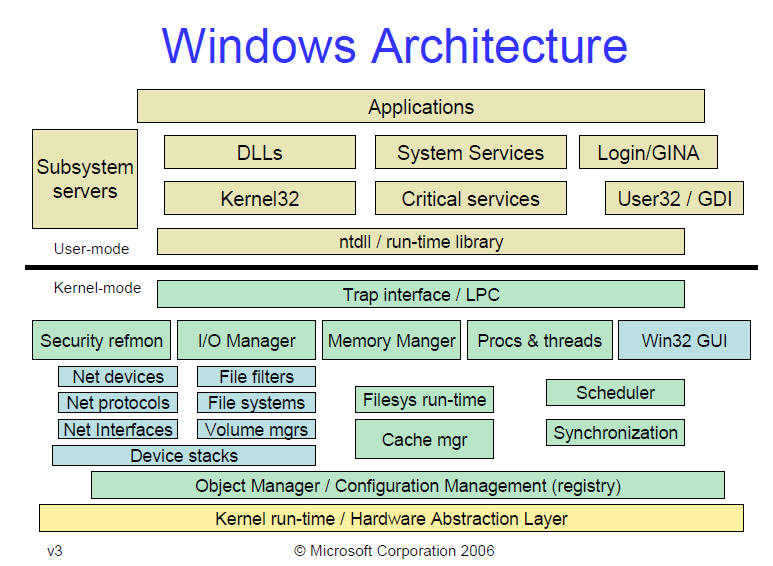
The kernel itself is the thinnest part of Windows and the most critical. It handles interrupt dispatching, thread scheduling, and memory management. The kernel mode driver model sits on top of it, and this is where most system instability comes from. A poorly written driver doesn't just crash your application. It takes the whole system down with a bug check. I once spent three days tracking a blue screen on a custom-built workstation. The GPU drivers were fine. The SSD firmware was fine. It turned out to be a network adapter driver from a cheap PCIe card that was corrupting memory during DMA operations. Had to remove the card entirely to stabilize the system. That's how deep these components go. Beneath the kernel is the hardware abstraction layer, or HAL. It's what separates the kernel from the actual physical hardware. Different HALs exist for different processor architectures and ACPI implementations. Most people never interact with it directly, but it matters when you're doing things like deploying Windows to mixed hardware environments or building custom boot images. Get the HAL wrong during imaging and you'll see random driver failures on boot. The executive layer is where things get interesting. This is the ring 0 environment that manages objects, processes, threads, virtual memory, and the I/O subsystem. The Object Manager within the executive is what gives Windows its unified resource model. Everything is an object. Files, registry keys, events, semaphores. They all share the same naming space and security framework. This design choice means that access control isn't bolted on. It's baked into the core. That's why you can apply the same DACL logic to a file as you would to a registry key.
User mode components you actually interact with
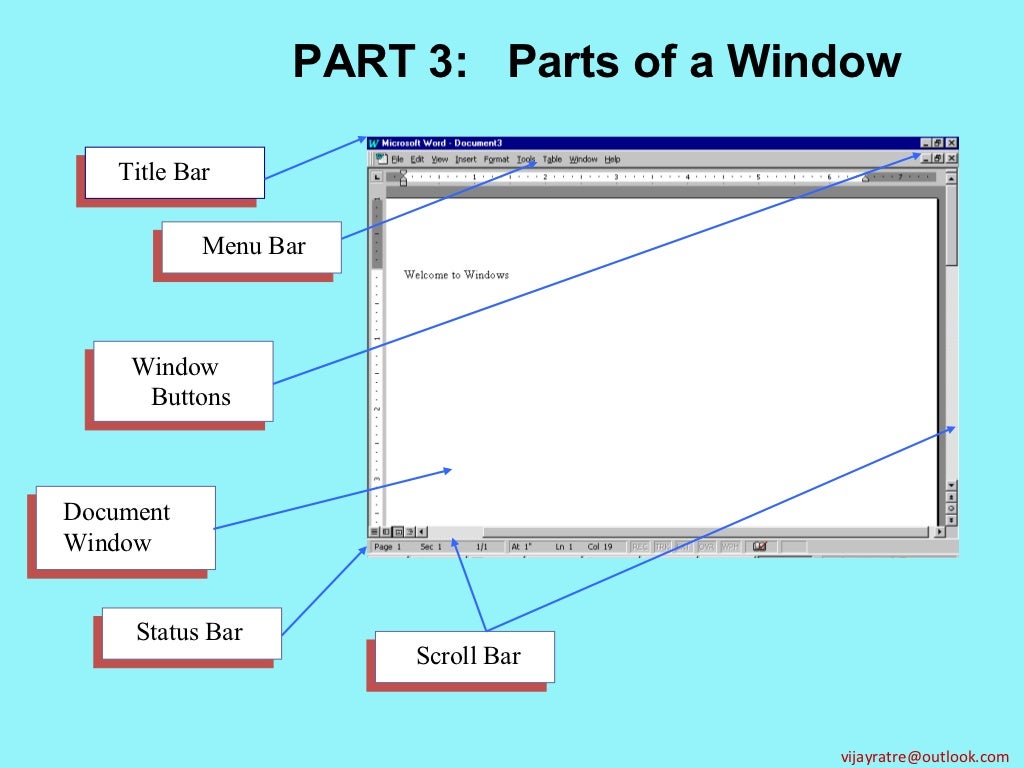
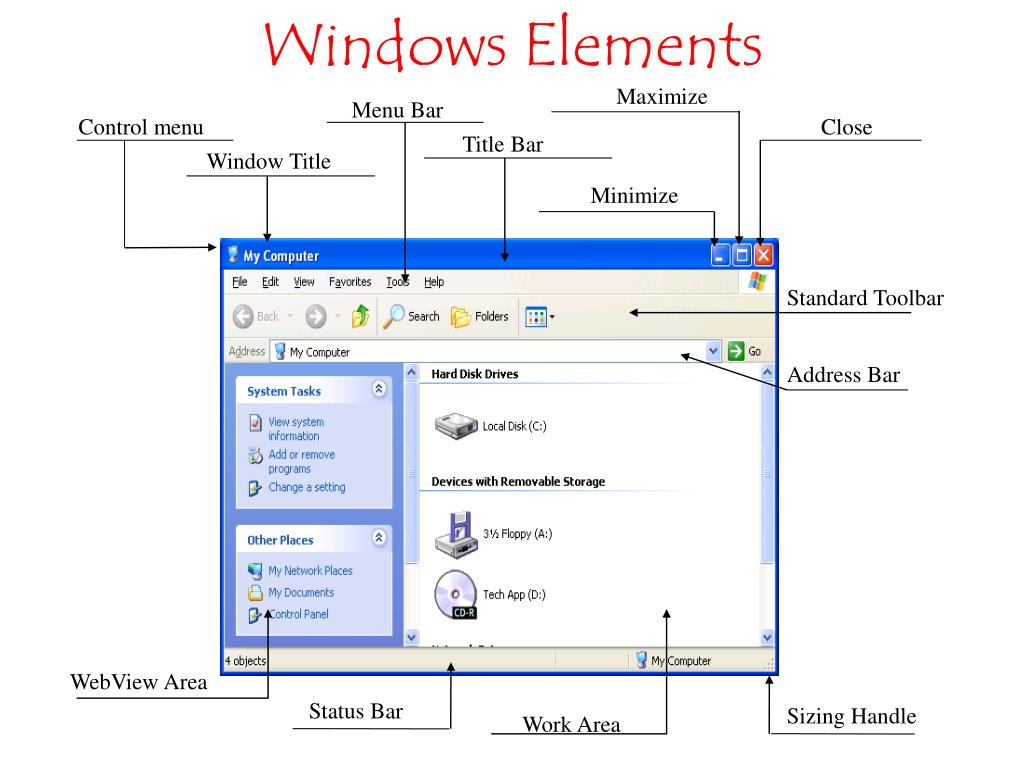
Win32 subsystem is the backbone of application compatibility. It provides the API surface that every Windows program since Windows 95 has called. The console subsystem handles command-line applications. The window manager and GDI handle graphics rendering. DirectX sits alongside them for GPU-intensive workloads. These aren't separate operating systems. They share the same kernel resources but are maintained by different teams with different release cycles. The Windows Registry is arguably the most misunderstood component. It's not a database. It's a hierarchical key-value store implemented as a set of hive files stored under System32\config. Each hive is a binary file loaded into memory at boot. When you use regedit, you're talking to the Registry service, which reads and writes these hives. The problem is that Windows has hundreds of entries scattered across multiple hives, and many of them serve no purpose on modern systems. I've cleaned up hives on machines where the registry had accumulated over 40,000 orphaned entries from old software installations. Registry bloat doesn't slow down the OS in any measurable way on modern hardware, but it does make troubleshooting a nightmare because you can't tell which entries are active and which are dead weight. Services are another area where the components model creates confusion. Every service runs inside svchost.exe or as a standalone process. The Service Control Manager decides when each one starts, stops, or recovers. Services have dependency chains, restart policies, and security contexts. I once had a server where a database service wouldn't start because a dependent print spooler service was configured to run under a domain account that had been deleted during an AD cleanup. The error message pointed at the database. The real problem was three dependencies deep. That's the kind of thing that eats hours.
Get the Full Details
System utilities and management tools
Device Manager, Disk Management, Event Viewer, Performance Monitor, Component Services, services.msc, msconfig. These are all management interfaces that talk to the same underlying components. They just expose different views. The reason they exist as separate tools is historical. Each one was built by a different team at different times. They don't always agree with each other. You'll see a device listed as working in Device Manager but show errors in the Event Log. Or you'll see a service running in services.msc but the underlying process isn't responding. That's not a bug. It's the result of different components reading from different data sources. Windows Update itself is a component. The Windows Update Agent, the Background Intelligent Transfer Service, the CUx containers. It's surprisingly complex under the hood. The update store lives in C:\Windows\SoftwareDistribution and the catalog files are cached locally. When an update fails, the problem is rarely the update itself. It's usually a corrupted catroot2 folder, a stuck BITS job, or a damaged Windows component store. The DISM tool fixes the component store. The Reset Windows Update Components script handles the rest. I run both in sequence when dealing with persistent update failures, and it resolves about 90 percent of cases without needing manual intervention.
Security components
Windows Security Center, SmartScreen, Controlled Folder Access, Windows Defender Antivirus, BitLocker, Credential Guard. These are all components that operate at different layers. Some run in kernel mode. Some run in user mode. They don't always coordinate well. I've seen cases where BitLocker and third-party encryption software conflicted at the driver level, causing boot failures. The workaround was disabling the third-party solution before enabling BitLocker, not after. Order matters with security components because they install kernel drivers that can conflict during initialization. User Account Control is another component that people complain about constantly. It's not a virus scanner. It's a privilege separation mechanism. It runs as a filtered token for standard users and a full token for administrators. The prompt you see is the admin consent flow. What most people don't realize is that UAC is tied to the Windows Filter Manager and the Token Manipulation APIs. When you click yes on a UAC prompt, you're not just approving an action. You're allowing a process to create a new access token with elevated privileges. Malware exploits this exact mechanism. That's why legitimate applications sometimes trigger false positives during elevation.
Networking stack components
The TCP/IP stack in Windows is implemented in ntoskrnl.exe and ixlite.sys. DNS resolution goes through dns.dll and the DNS Client service. Network Location Awareness handles profile switching between public, private, and domain networks. Winsock catalogs manage protocol providers. Each of these can fail independently. I once dealt with a machine that could reach IP addresses but not hostnames. nslookup worked fine from the command line, but browsers failed. The issue was that the Winsock catalog was corrupted at the LSP layer. Had to reset it with netsh winsock reset and reboot. The system recovered immediately after. These components are interconnected in ways that aren't documented clearly anywhere. Power management is handled by the kernel power manager, ACPI drivers, and the power shell APIs. Modern standby, hibernate, fast startup. They all use different mechanisms. Fast startup on Windows 10 and 11 hybridizes a normal shutdown with hibernation of the kernel session. This means that when you shut down, the kernel drivers are saved to disk and restored on boot. It's faster but it also means that driver updates sometimes don't take effect until you do a full restart. I've seen this cause issues with network driver updates where the new driver was installed but the old one was still running from the hibernation image.
What most guides leave out
The Windows Component Store, located at WinSxS, is where side-by-side assembly management happens. It's not bloat. It's by design. Multiple versions of the same DLL can coexist because different applications depend on different versions. The problem is that this folder grows over time and people treat it like junk. You shouldn't delete from it manually. DISM can clean it, but even that has limits. The component store is also where Windows stores backup copies of system files for repair operations. If you compromise it, you lose the ability to fix corrupted system files without a full reinstall. There's no single list of components that applies to every Windows installation. A Home edition, a Server Core install, and an IoT deployment have radically different component sets. The best approach is to understand what each layer does rather than memorizing component names. When something breaks, you need to know whether it's a kernel issue, a driver issue, a service issue, or a user-mode application issue. That distinction determines your entire troubleshooting path.