Understanding How Your Browsing Data Is Actually Treated Under Telecom Law
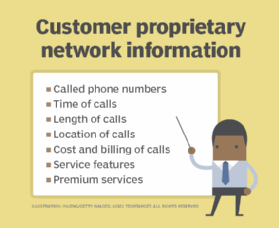
Most people think their internet search history is completely unprotected. It isn't. Not entirely. Under the framework established by the Telecommunications Act of 1996 and enforced through FCC regulations, customer browsing data can fall under CPNI — Customer Proprietary Network Information. This matters more than you'd think if you're dealing with carrier compliance, data governance, or legal disclosure issues. CPNI originated as a telecom concept. It covers the type of service a customer subscribes to, calling patterns, and routing information — the kind of stuff a telephone company naturally collects. But broadband ISPs do the same thing at a network level. They see what addresses you hit, how much data you move, and for how long. The FCC has treated that pattern data as analogous to traditional telephony CPNI in several advisory opinions and rulemakings. The 2016 FCC privacy order was the closest thing we got to a definitive ruling. It classified browsing history, app usage data, and billing information as CPNI-equivalent for broadband providers. That order required explicit opt-in consent before carriers could use or share that data. Then Congress passed a resolution of disapproval in 2017 under the Congressional Review Act, and the FCC under Ajit Pai formally repealed it in 2018. So the federal opt-in regime vanished. That doesn't mean the protection is gone though. It just means the legal basis shifted.
What remains is a patchwork. The FCC still recognizes CPNI protections for traditional voice and certain hybrid services. Several states have enacted their own broadband privacy laws that effectively recreate the 2016 rules at the state level — Vermont, California, Delaware, Colorado, and a few others. In those jurisdictions, your search history and browsing metadata are treated as protected customer information with real enforcement teeth. Even in states without specific statutes, carriers that classify themselves as telecommunications providers may voluntarily maintain CPNI-style safeguards because the legal risk of misclassification is high.
What Exactly Counts As CPNI For Internet Customers
This is where people get tripped up. CPNI doesn't cover the literal text of every search query you type into Google. It covers the metadata surrounding your connection — the domains you visit, the URLs, the timestamps, the data volumes, and the services you access. Think of it this way: if your ISP can see that you spent forty minutes on a streaming platform at 11 PM on a Tuesday, that pattern is CPNI. If they can see you visited a specific medical website, that URL and the associated traffic data is also CPNI. The actual content of what you read on those pages falls under a different legal umbrella — the Electronic Communications Privacy Act — which is separate and in some ways more restrictive. I've seen carriers and their legal teams struggle with this distinction constantly. The boundary between CPNI and ECPA-protected content isn't always clean. When an ISP logs that a customer accessed a particular endpoint using HTTPS, they technically don't see the page content, but they do see the domain. The FTC has taken the position that domain-level data collected by ISPs is CPNI-adjacent and should be treated with the same care. That's not a hard legal rule everywhere, but it's the direction enforcement has been moving. One thing that catches people off guard: your search history becomes CPNI the moment it passes through your ISP's infrastructure. It doesn't matter that you're using a search engine owned by a separate company. The ISP is the gateway. They're the ones collecting the network-level record. That's why privacy advocates have consistently pushed for ISPs to be regulated as common carriers — because that classification triggers the CPNI framework automatically.
Get the Full Details
How CPNI Protection Works In Practice
If you're a carrier or ISP handling customer data, the operational requirements are straightforward but easy to mess up. You need to classify what data you collect, implement access controls that limit who inside the organization can view CPNI, obtain customer consent before using or sharing it for marketing purposes, and provide customers a way to opt out. The 2016 order also required data security safeguards — encryption in transit and at rest, regular audits, breach notification procedures. None of that disappeared when the federal rule was repealed. It just stopped being uniformly mandated. From a technical standpoint, the biggest challenge is data mapping. You have to know exactly what qualifies as CPNI across every system that touches it. I worked on an audit once where a mid-size ISP had CPNI flowing into three different marketing analytics platforms because the data engineering team had set up automatic pipelines without legal reviewing them. The CPNI was leaking into third-party dashboards that the compliance team didn't even know existed. We spent about six weeks tracing every data path and shutting down the unauthorized flows. That's the kind of problem that shows up when you treat CPNI as a legal checkbox instead of an operational reality. For consumers, the practical takeaway is that you should check whether your state has broadband privacy legislation. If you live in California, for example, the California Privacy Rights Act gives you the right to know what browsing data an ISP collects and to restrict its use. In states without those laws, your protections depend almost entirely on your carrier's own privacy policy, which may or may not reflect CPNI standards. Reading that policy carefully matters more than most people realize.
Common Mistakes And Where The Framework Falls Short
The biggest misconception is that CPNI protection is binary — either your data is protected or it isn't. It's not. It depends on who collects it, how they collect it, where you live, and what they want to do with it. An ISP's CPNI obligations are different from a search engine's obligations, which are different from a router manufacturer's obligations. None of these entities are the same, and the legal frameworks that apply to each are layered on top of one another in ways that aren't intuitive. Another issue: CPNI rules apply primarily to carriers and ISPs. They don't reach the apps and services you actually interact with. Your search history on Google or Bing is governed by those companies' privacy policies, not by CPNI law. So even in a strong CPNI regime, you can still have your browsing data shared downstream through analytics scripts, ad trackers, and browser extensions that operate outside the carrier's control. That's a gap that state privacy laws are starting to address, but it's far from solved. The enforcement landscape is also uneven. The FCC can take action against carriers for CPNI violations, but the agency has been understaffed and politically directed away from aggressive privacy enforcement in recent years. State attorneys general fill some of that gap, but not consistently. And there's no private right of action for CPNI violations at the federal level — meaning you can't sue your ISP just because they mishandled your browsing data. You'd need to find a state law that allows it or wait for regulatory action. That's a structural weakness that isn't going away soon.
What To Do If You Need To Handle This Data Correctly
Start by determining your regulatory classification. Are you a telecommunications provider, an information service provider, or both? That distinction alone determines whether CPNI rules attach. Then map every category of customer data you collect and flag which ones qualify as CPNI or CPNI-adjacent. Don't rely on what your engineering team tells you — they'll miss things. Audit your data flows, especially any pipelines that feed third-party tools or analytics platforms. Implement consent management that meets the strictest standard you're subject to. If you operate in multiple states, comply with the highest requirement — which right now is usually California or Colorado. Build in opt-out mechanisms that are actually functional, not just buried in a settings menu. And maintain documentation. If you're ever audited, the burden shifts to you to prove you classified and protected the data correctly. Assumptions won't hold up. For individuals who want to protect their own browsing data, the most effective steps are using a reputable VPN, enabling DNS over HTTPS, and choosing an ISP that explicitly commits to CPNI-level privacy practices. Check your state'sAttorney General website for broadband privacy resources. The legal protections exist, but they only help you if you know they exist and know how to invoke them.