Understanding the Daf Opsec Awareness Training CBT
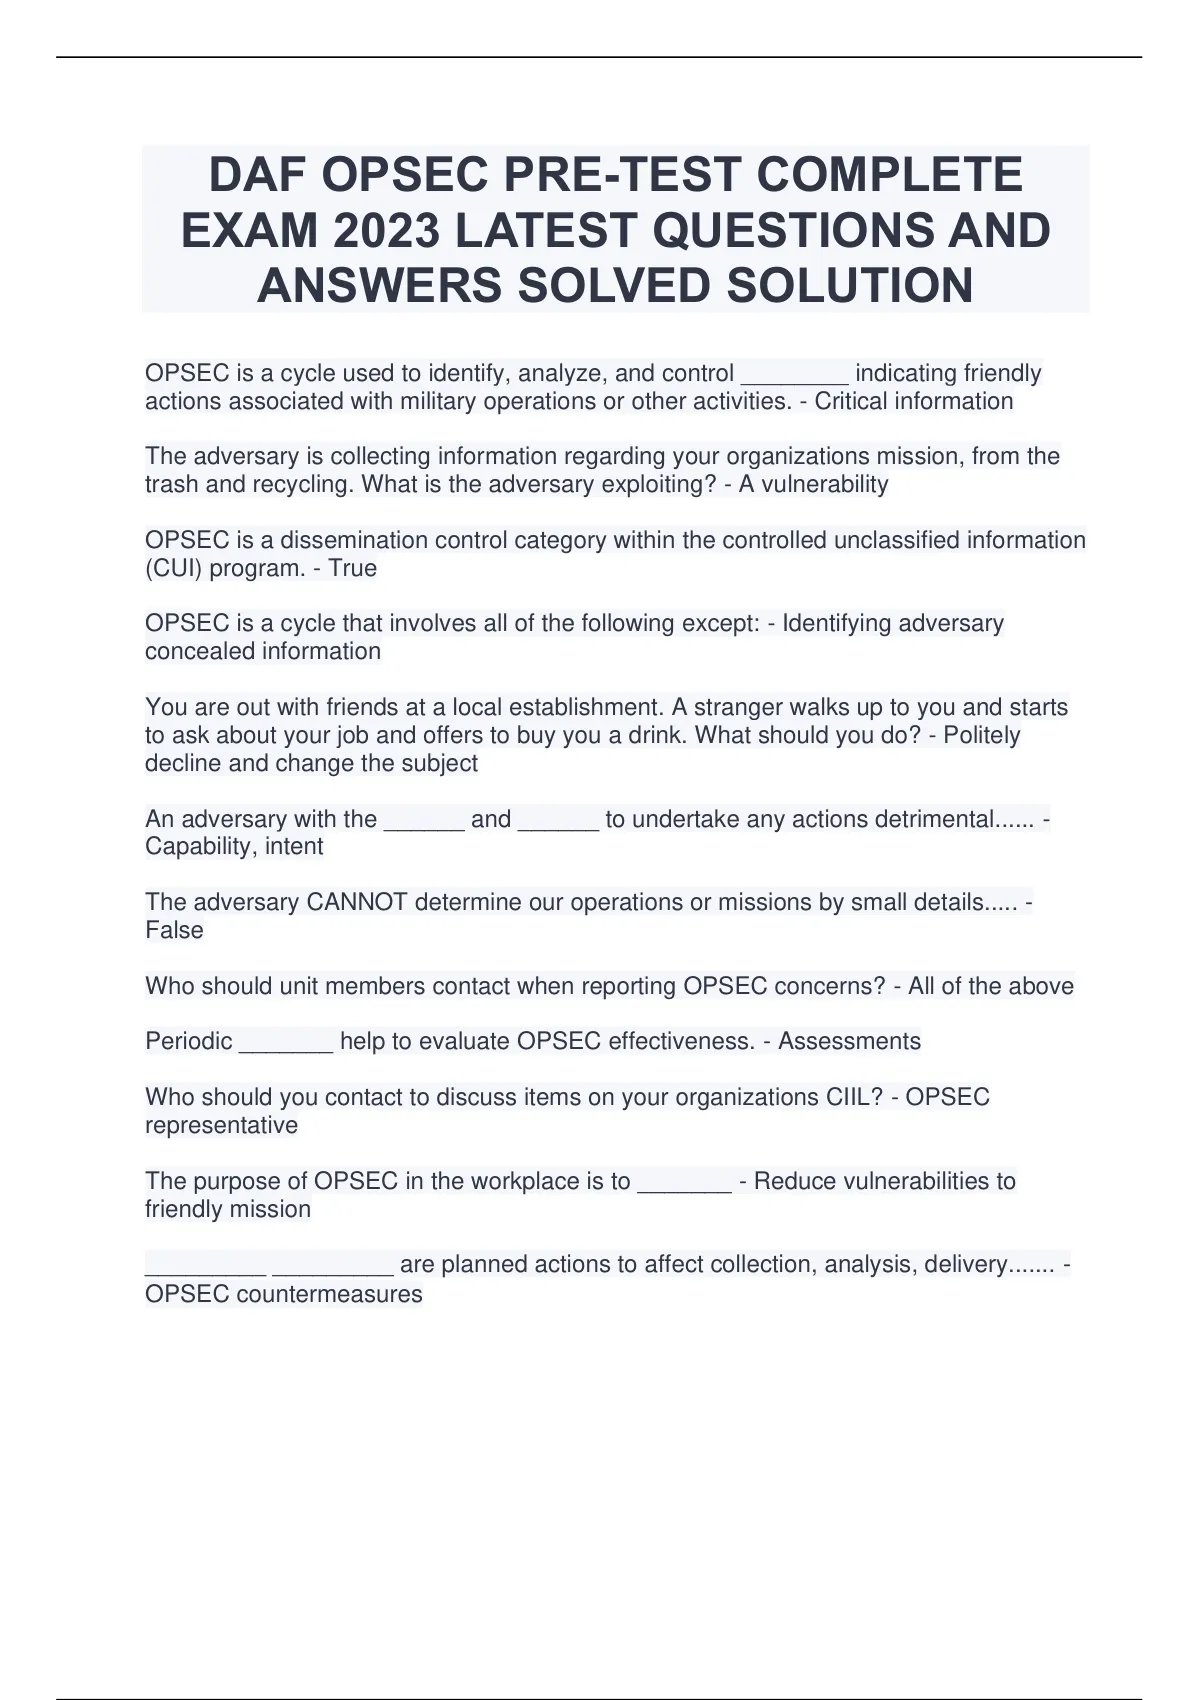
The Daf Opsec Awareness Training CBT Answers are sought by employees who need to complete their mandatory operational security awareness module for the Dutch Tax and Customs Administration. The training covers handling classified information, recognizing phishing attempts, using encrypted communication channels, and understanding data classification levels. It is not an optional course, and most staff members complete it through the internal learning management system. The CBT module is typically self-paced and takes between 45 and 90 minutes depending on your reading speed. You are presented with scenarios, short knowledge checks, and a final assessment. The assessment usually requires a passing score of around 70 percent or higher, though exact thresholds vary by department and year. The questions are scenario-based rather than purely definitional, which is one reason rote memorization does not always work well. I ran into this myself when a colleague tried to rush through it by skimming. They scored 58 percent on the first attempt. The issue was not that they did not know the material but that the questions were framed around specific cases — for example, "what do you do when you receive an email from an external party requesting document transfer via an unapproved channel." The wrong answers were designed to look plausible. The correct answer was always the most conservative, process-following option.
Approaching the CBT Effectively
Read every scenario carefully before selecting an answer. The training deliberately includes distractor answers that follow partially correct logic but miss a key step. If a question asks about reporting a suspected breach, the correct sequence usually starts with isolation or non-engagement, not investigation or forwarding the message to a colleague. Pay attention to the distinction between classification levels. Dutch government data uses the standard EU classification framework: EURATOM SECRET, CONFIDENTIEL UE, TRÈS SECRET, and RESTREINT. In the Daf context, you will also encounter internal categories like "vertrouwelijk" and "confidentieel." Knowing which category maps to which handling requirement is essential, and it is where most people lose points. One thing many miss is the section on shoulder surfing and clean desk policy. The questions here are straightforward but easy to overlook because the content feels obvious. I have seen people skip reviewing those sections and then get tripped up by questions about leaving a terminal unlocked in a shared workspace. The answer is always the most restrictive action available.
Common Pitfalls
The biggest mistake people make is assuming the training tests memory of policy documents. It does not. It tests whether you would act correctly in a realistic situation. This means you should think about what a cautious, compliance-focused employee would do, not what a practical one would do to get something done quickly. Another trap is the assumption that all external communication is prohibited. It is not. The training emphasizes approved channels and verified recipients. Sending sensitive data through an unauthorized service like a personal email account or a public file-sharing tool is the violation, not external communication itself. Time management matters too. The CBT does not usually have a strict timer, but rushing through increases error rates. Taking two minutes per question and flagging uncertain items for review improves accuracy noticeably. My own experience shows that returning to flagged questions with a clearer head yields better results than trying to force an answer on the first pass.
Get the Full Details
What to Do If You Do Not Pass
If you fail the assessment, you can usually retake it after a waiting period set by your department. Some versions allow immediate retakes with reordered questions, while others require a 24-hour cooldown. Check your LMS dashboard for the specific rule that applies to your cohort. There is no penalty for failing beyond the delay, and the material remains the same across attempts. Review the feedback sections provided after each wrong answer. The CBT typically explains why the selected option was incorrect, which is more useful than generic answer keys. Those explanations contain the exact wording the assessment expects.
Final Notes
The training is designed to build habits, not to filter people out. Treat it as a chance to understand what your organization considers acceptable behavior regarding data handling and operational security. The questions will feel repetitive if you have worked in a government-adjacent role before, and that repetition is intentional. Compliance training succeeds through reinforcement, not novelty.