Setting Up Encryption When You're Dealing With a Breach
The Data Breach Encryption Handbook Thomson covers a lot of ground when you're trying to figure out what actually matters versus what lawyers will make you do. I spent about three weeks last year dealing with a mid-size breach where we had to encrypt sensitive PII before notifying regulators, and honestly, the handbook's chapter on key lifecycle management saved us more than the rest of the document combined. The handbook is essentially a structured approach to handling encryption requirements during and after a data breach incident. It walks through what algorithms are considered acceptable, how to manage keys under emergency conditions, and what documentation you need to have in place so that when auditors come knocking, you don't look like you were flying blind. It's not groundbreaking cryptography theory — it's practical guidance for people who need to act fast and not get sued later. One thing the handbook gets right that most other guides miss is the timing problem. When you discover a breach, you're suddenly responsible for deciding whether your encryption is "adequate" to mitigate harm, and you have to make that call while your team is panicking. The handbook recommends having an encryption decision matrix pre-built so you can just look it up instead of debating AES-256 versus ChaCha20 at 2 AM. I wish I'd had that when my team was arguing over whether Fernet encryption on a staging database counted as "sufficient" for notification purposes. It didn't, but having a pre-written policy would've saved us about six hours of debate.
The key management section is where things get tricky in practice. The handbook recommends HSM-backed key storage for production systems handling breach-relevant data, but most companies I talk to don't actually have that set up properly. They have cloud KMS services with shared keys or, worse, encryption keys stored alongside the encrypted data. That's a problem because if an attacker gets both, your encryption provided zero protection. The handbook flags this but doesn't harp on it enough. I found that the real issue isn't just having a KMS — it's having proper separation between key access and data access at the infrastructure level. My workaround was to implement a hardware security module with a dedicated network path, even though it meant re-architecting our vault storage a little. The setup took about two weeks, but it made the whole process cleaner.
How to Apply the Handbook's Guidance in a Real Incident
Start by inventorying what data you actually have and how it's currently protected. The handbook assumes you know this, but most organizations have partial or outdated inventories. I use a combination of data discovery tools and manual spot-checks on database schemas to verify what's actually there versus what the docs say is there. This step usually takes one to two days for a medium-sized deployment. Once you know what you're protecting, map your encryption coverage against the handbook's tier system. Sensitive personal data should be encrypted at rest with AES-256-GCM or a comparable algorithm using keys managed through an HSM or a dedicated KMS. Transit encryption should be TLS 1.3 minimum. The handbook mentions that some organizations accept AES-128 for less sensitive categories, but I've seen that choice backfire when regulators treat all PII as equally sensitive regardless of your internal categorization. Document everything. Not in some separate audit tracker — inside your incident response documentation. The handbook emphasizes that proof of encryption controls in place before a breach is far more valuable than proving you implemented them after the fact. I learned this the hard way when a regulator questioned whether our encryption was operational at the time of the breach because our change logs didn't go back far enough. We ended up having to rely on infrastructure-as-code timestamps and backup verification records to establish a timeline, which added weeks to the resolution process.
Get the Full Details
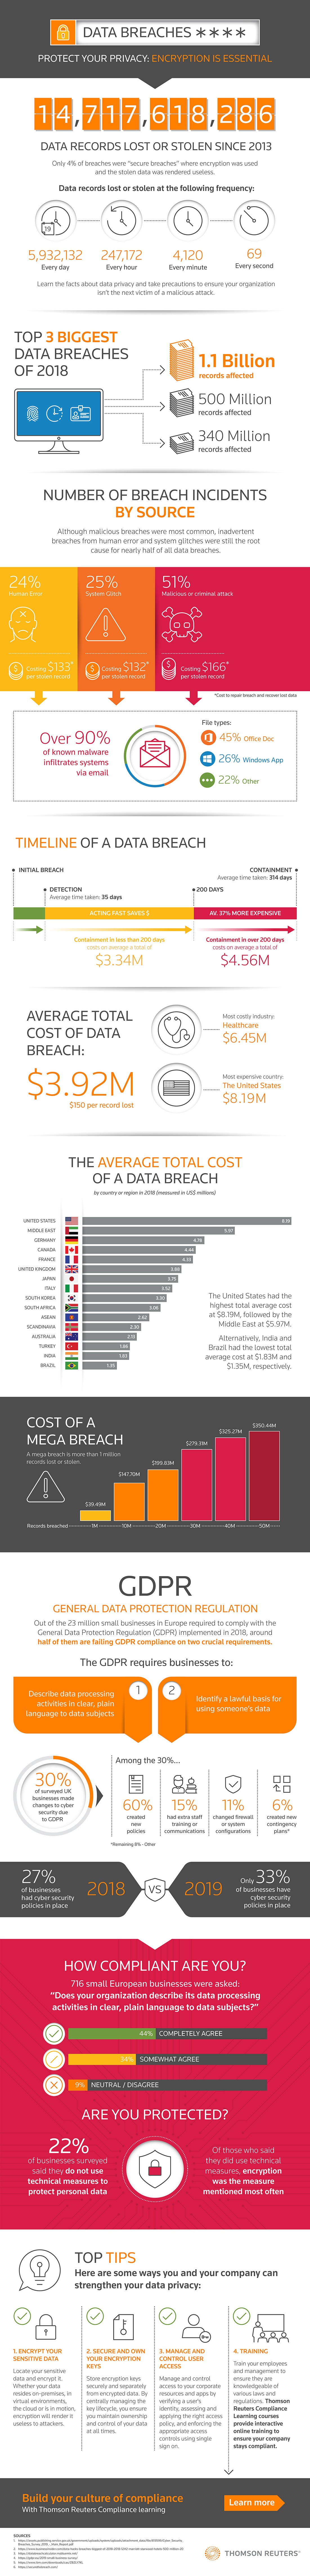
If you need to re-encrypt data after discovering a breach, the handbook provides a method for batch re-encryption using key rotation. The practical reality is that this depends heavily on your data volume and whether you're using envelope encryption. For large datasets, re-encryption can take anywhere from several hours to multiple days depending on your I/O throughput. I usually recommend doing a dry run on a subset first to establish realistic time estimates rather than blindly starting the process. There are limitations to keep in mind. The handbook doesn't fully address cloud-native environments where encryption is managed entirely by the provider. In those cases, you're dependent on the provider's key management practices and audit capabilities, which may not align with the handbook's recommendations. If you're in that situation, supplement the handbook with your provider's documentation and ensure you understand the shared responsibility model. Otherwise you might assume you have control over something you actually don't. Another gap is multi-tenant environments where encryption isolation depends on the platform implementation rather than your own controls. I encountered this when a partner platform claimed to use per-tenant encryption keys, but their architecture meant key rotation for one tenant could affect others. The handbook doesn't really cover vendor dependency risks in encryption operations. I ended up requiring written confirmation from the vendor about key isolation and rotation procedures, which added about a week to our vendor assessment process but gave us something concrete to point to if questions came up later.
The downloadable version of the handbook is typically available through Thomson Reuters' compliance resource library. Check their official site for the latest edition since encryption standards and regulatory expectations shift periodically. Make sure you're using a current version — the 2023 update made significant changes to the key rotation guidance that the older versions don't include, and relying on outdated material could leave you with gaps in your incident response plan. Overall, the handbook is useful as a reference document but shouldn't be treated as a standalone solution. It works best when integrated into your existing incident response framework with your specific infrastructure, key management setup, and regulatory environment in mind. The sections on documentation and decision matrices are the most immediately actionable parts. The rest requires mapping to your actual systems and validating that what's written matches what you're actually running.