Setting Up a Proper LAN for Small Office Deployment
Data Communication And Networking is one of those things everyone claims to understand until they actually have to cable an office and make sure eight people can print without the server melting down. I spent three weeks last year ripping through drywall in a converted warehouse because someone had terminated Cat6 without doing a proper T568B run on half the jacks. The network came up, obviously, because the switches do auto-MDI/MDIX now. But the packet error rate on two segments was sitting at 0.3 percent, which sounds negligible until you're running a VoIP system through it and everyone's calling each other through static. The biggest mistake I see people make is treating cabling as an afterthought. You can buy a $2,000 managed switch and connect it with $8 cables from a gas station, and your whole network is going to perform like that $8 cable is the bottleneck. It always is. I use Belden or CommScope certified bulk cable, Krone blocks for termination, and I verify every single run with a Fluke DSX-5000 before I ever think about throwing a device at the end of it. Certification takes about four minutes per drop. Doing it saves you approximately six hours of troubleshooting later when someone complains their workstation is slow. Don't skip the documentation step either. I keep a spreadsheet with every jack location, cable length, patch panel port, switch port, VLAN assignment, and MAC address. Yes, there are auto-discovery tools. They don't tell you which wall plate in room 204 connects to port 12 on switch B. I learned that the hard way when a tenant moved furniture and a cable got yanked out of a jumbled patch panel with zero labels. Took me two days to trace it manually with a toner probe.
VLANs and subnetting without overcomplicating it
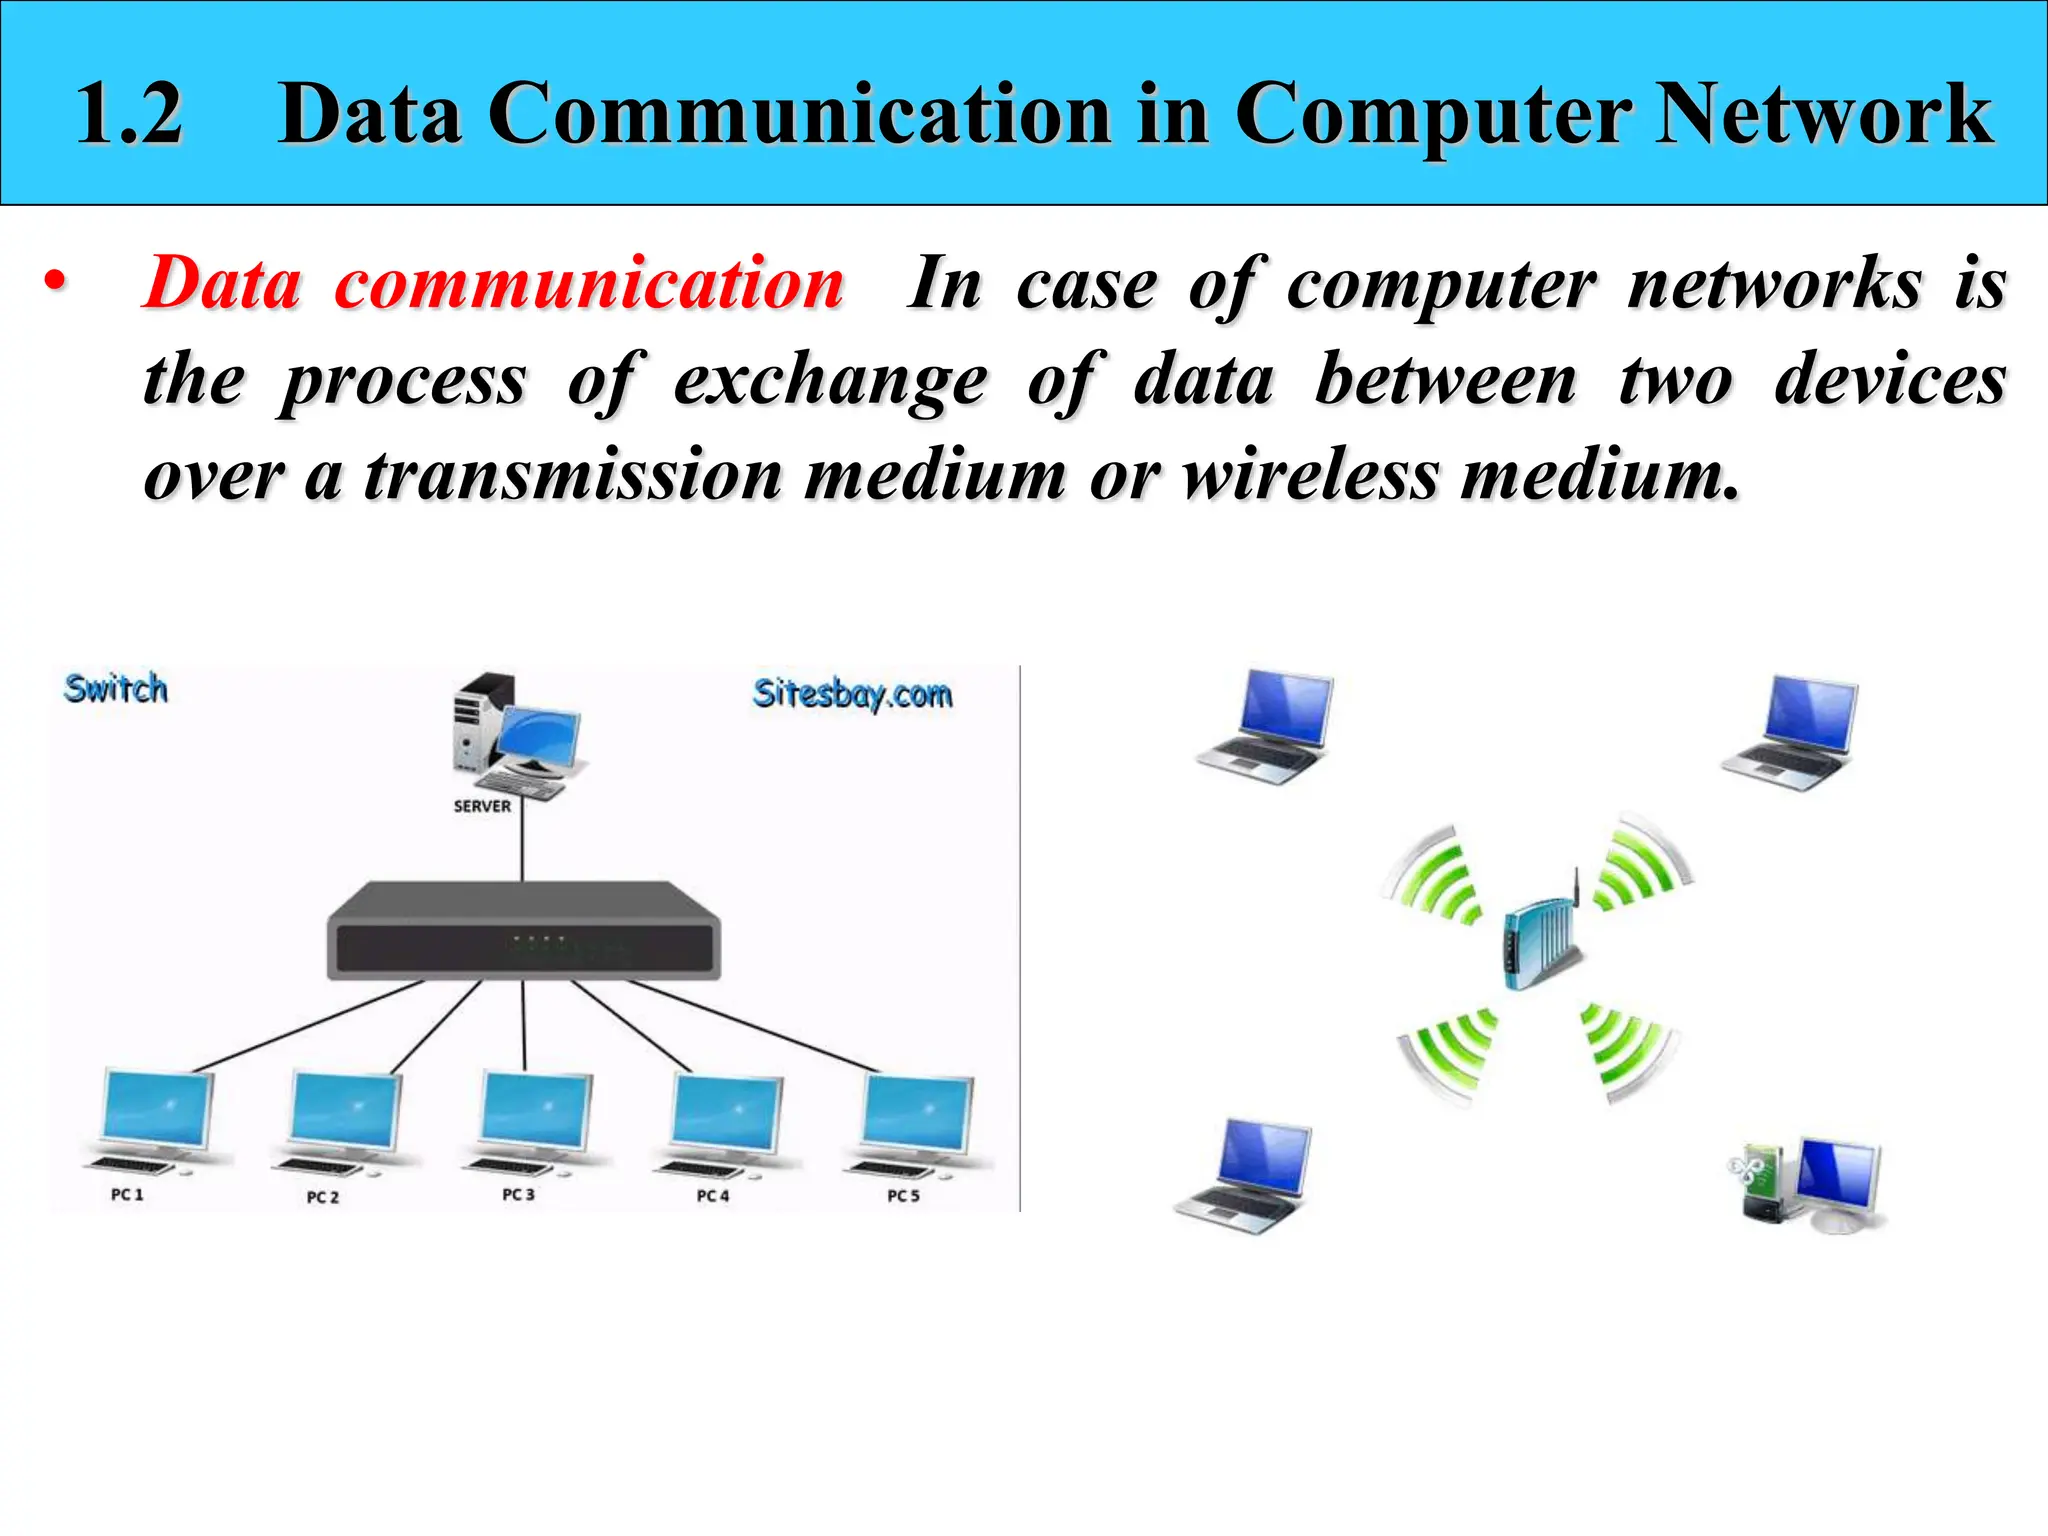
You don't need twenty VLANs for a twelve-person office. I've seen people do it though, and it makes troubleshooting infinitely worse for no real security gain. Start with three: one for user workstations, one for servers and storage, and one for IoT/smart devices. That's it. If you're dealing with guest Wi-Fi, give it its own VLAN with a firewall policy that blocks any traffic toward the internal subnets. Most people skip this and let guest devices see everything on the network, which is how you get printers broadcasting their administrative interfaces to visitors. For IP addressing, just use /24 subnets unless you have a genuine reason not to. A /24 gives you 254 usable hosts per segment, which covers most small deployments comfortably. I once worked with someone who used a /30 for every single point-to-point link between switches. That's 2 IP addresses per link. After twelve links, they'd burned through a /24 and had no idea where the addresses went. Just use /24s. It's boring and it works.
Switch configuration that won't come back to haunt you
Layer 2 switching is mostly set it and forget it at this scale, but there are a few settings that absolutely matter. Enable Spanning Tree Protocol immediately if you have more than one switch, and make sure you designate one switch as the root bridge. Without that, you're at the mercy of whatever switch happens to have the lowest MAC address, which is rarely the right choice for performance. BPDU guard should be enabled on all access ports so that someone can't accidentally plug a second switch into a wall jack and loop the entire network. I've done that myself. It took down a whole floor's connectivity for about forty seconds before Spanning Tree converged. Not fun when people are on active calls. Port security is another thing people ignore until it's too late. Set a maximum of two MAC addresses per access port and configure violation mode to shutdown. That stops someone from plugging in a rogue hub or switch and either accidentally creating a loop or intentionally intercepting traffic. I caught a guy doing ARP spoofing on an unsecured port because his laptop showed up on a printer's management port. The port shut down automatically and I had the MAC address to go find him.
Get the Full Details

Wi-Fi deployment: why most offices do it wrong
Wireless is where most small-network projects fall apart. People buy a consumer-grade router, set it to broadcast on 2.4 and 5 GHz, and call it done. Then they wonder why the conference room has dead zones and the video calls keep dropping. The issue is almost always channel overlap and transmit power set too high. When every access point blasts at maximum power on overlapping channels, you create co-channel interference that's worse than just having weaker signals in the first place. I use Ekahau Site Survey (the free version is sufficient for small offices) to map out coverage before mounting a single AP. It shows you exactly where the dead zones will be and which channels will overlap. For a typical office, I space access points about thirty to forty feet apart depending on wall materials, set transmit power to medium-low so each AP covers its intended area without bleeding into the next one's space, and assign non-overlapping channels: 1, 6, and 11 for 2.4 GHz, and a spread of 36, 149, and 153 for 5 GHz depending on how many APs I'm running. The one edge case that still catches me off guard is concrete floors with metal rebar. I deployed a setup in a mid-rise building where the 5 GHz signal would travel fine horizontally but died almost completely going vertically through floors. The metal in the concrete absorbed it. I ended up having to run Cat6 vertically between floors and place an AP on each level rather than relying on wireless uplinks, which restored full coverage. Wireless mesh between floors in that building would have been a joke at best.
Firewall and segmentation basics
You need a firewall between your internal network and the internet. Not a software firewall on a single machine, an actual perimeter device. A $200 Ubiquiti or MikroTik router handles this for a small office. Configure it with default-deny inbound rules, allow outbound traffic on standard ports, and set up a DMZ if you're running any publicly accessible services like a website or VPN server. Most small business owners don't run public services, so skip the DMZ and just make sure remote access goes through an encrypted VPN tunnel instead of opening ports on your firewall. I've seen too many office networks compromised because someone forwarded port 445 for "convenient file sharing" and then had ransomware moving through it in under six minutes. Set up basic monitoring from day one. PRTG or Zabbix will cost you nothing for small deployments and will alert you before a failure becomes a crisis. I configured a simple ICMP poll with threshold alerts on all switch ports and critical servers. When a link flaps more than three times in five minutes, you get a notification and can investigate before the whole segment goes down. I also set up SNMP traps on all managed switches for immediate fault reporting. The reality is that most network problems in small offices aren't caused by fancy attacks or complex configuration errors. They're caused by someone moving a desk and disconnecting a cable, a switch power supply failing, or a Wi-Fi channel getting interfered with by a new microwave or Bluetooth device. Good monitoring catches these faster than anyone noticing. Keep your cable documentation current, label everything, and don't skip the testing steps because they feel tedious. The alternative is spending your Saturday night tracing a cable through a ceiling that's three stories tall because you never marked which patch panel port went where.
Common pitfalls that waste time
Here's what I see consistently: people mix cable categories mid-run, using Cat5e on one segment and Cat6 on another without realizing the speed negotiation falls back to the lowest common denominator. It'll work at 1 Gbps across both, but if you ever upgrade to 2.5 or 5 Gbps, that Cat5e segment becomes a hard limit and you won't know why without testing. Always match cable categories within a single run. Another one is neglecting PoE budget calculations. If you're powering ten access points and five IP phones through a single switch, you need to verify the switch's total PoE budget covers the maximum draw of every connected device simultaneously. I once had four APs that all hit their peak power during a firmware update at the same time, which tripped the switch's overcurrent protection and dropped every PoE device on that VLAN. Moving the APs to a dedicated PoE+ switch solved it, but it took two hours of downtime to figure out what was happening. And finally, don't assume that just because something connects, it's configured correctly. I inherited a network where the guest Wi-Fi SSID existed but had no captive portal, no isolation policy, and no DHCP scope configured. It was broadcasting and accepting connections but handing out IPs from the main corporate subnet. Anyone walking by could connect and access internal resources. This is the kind of thing that doesn't show up on a basic connectivity test. It only shows up when someone actually connects to it, which is exactly when you want to catch it.