What a Gap Assessment Template Actually Is
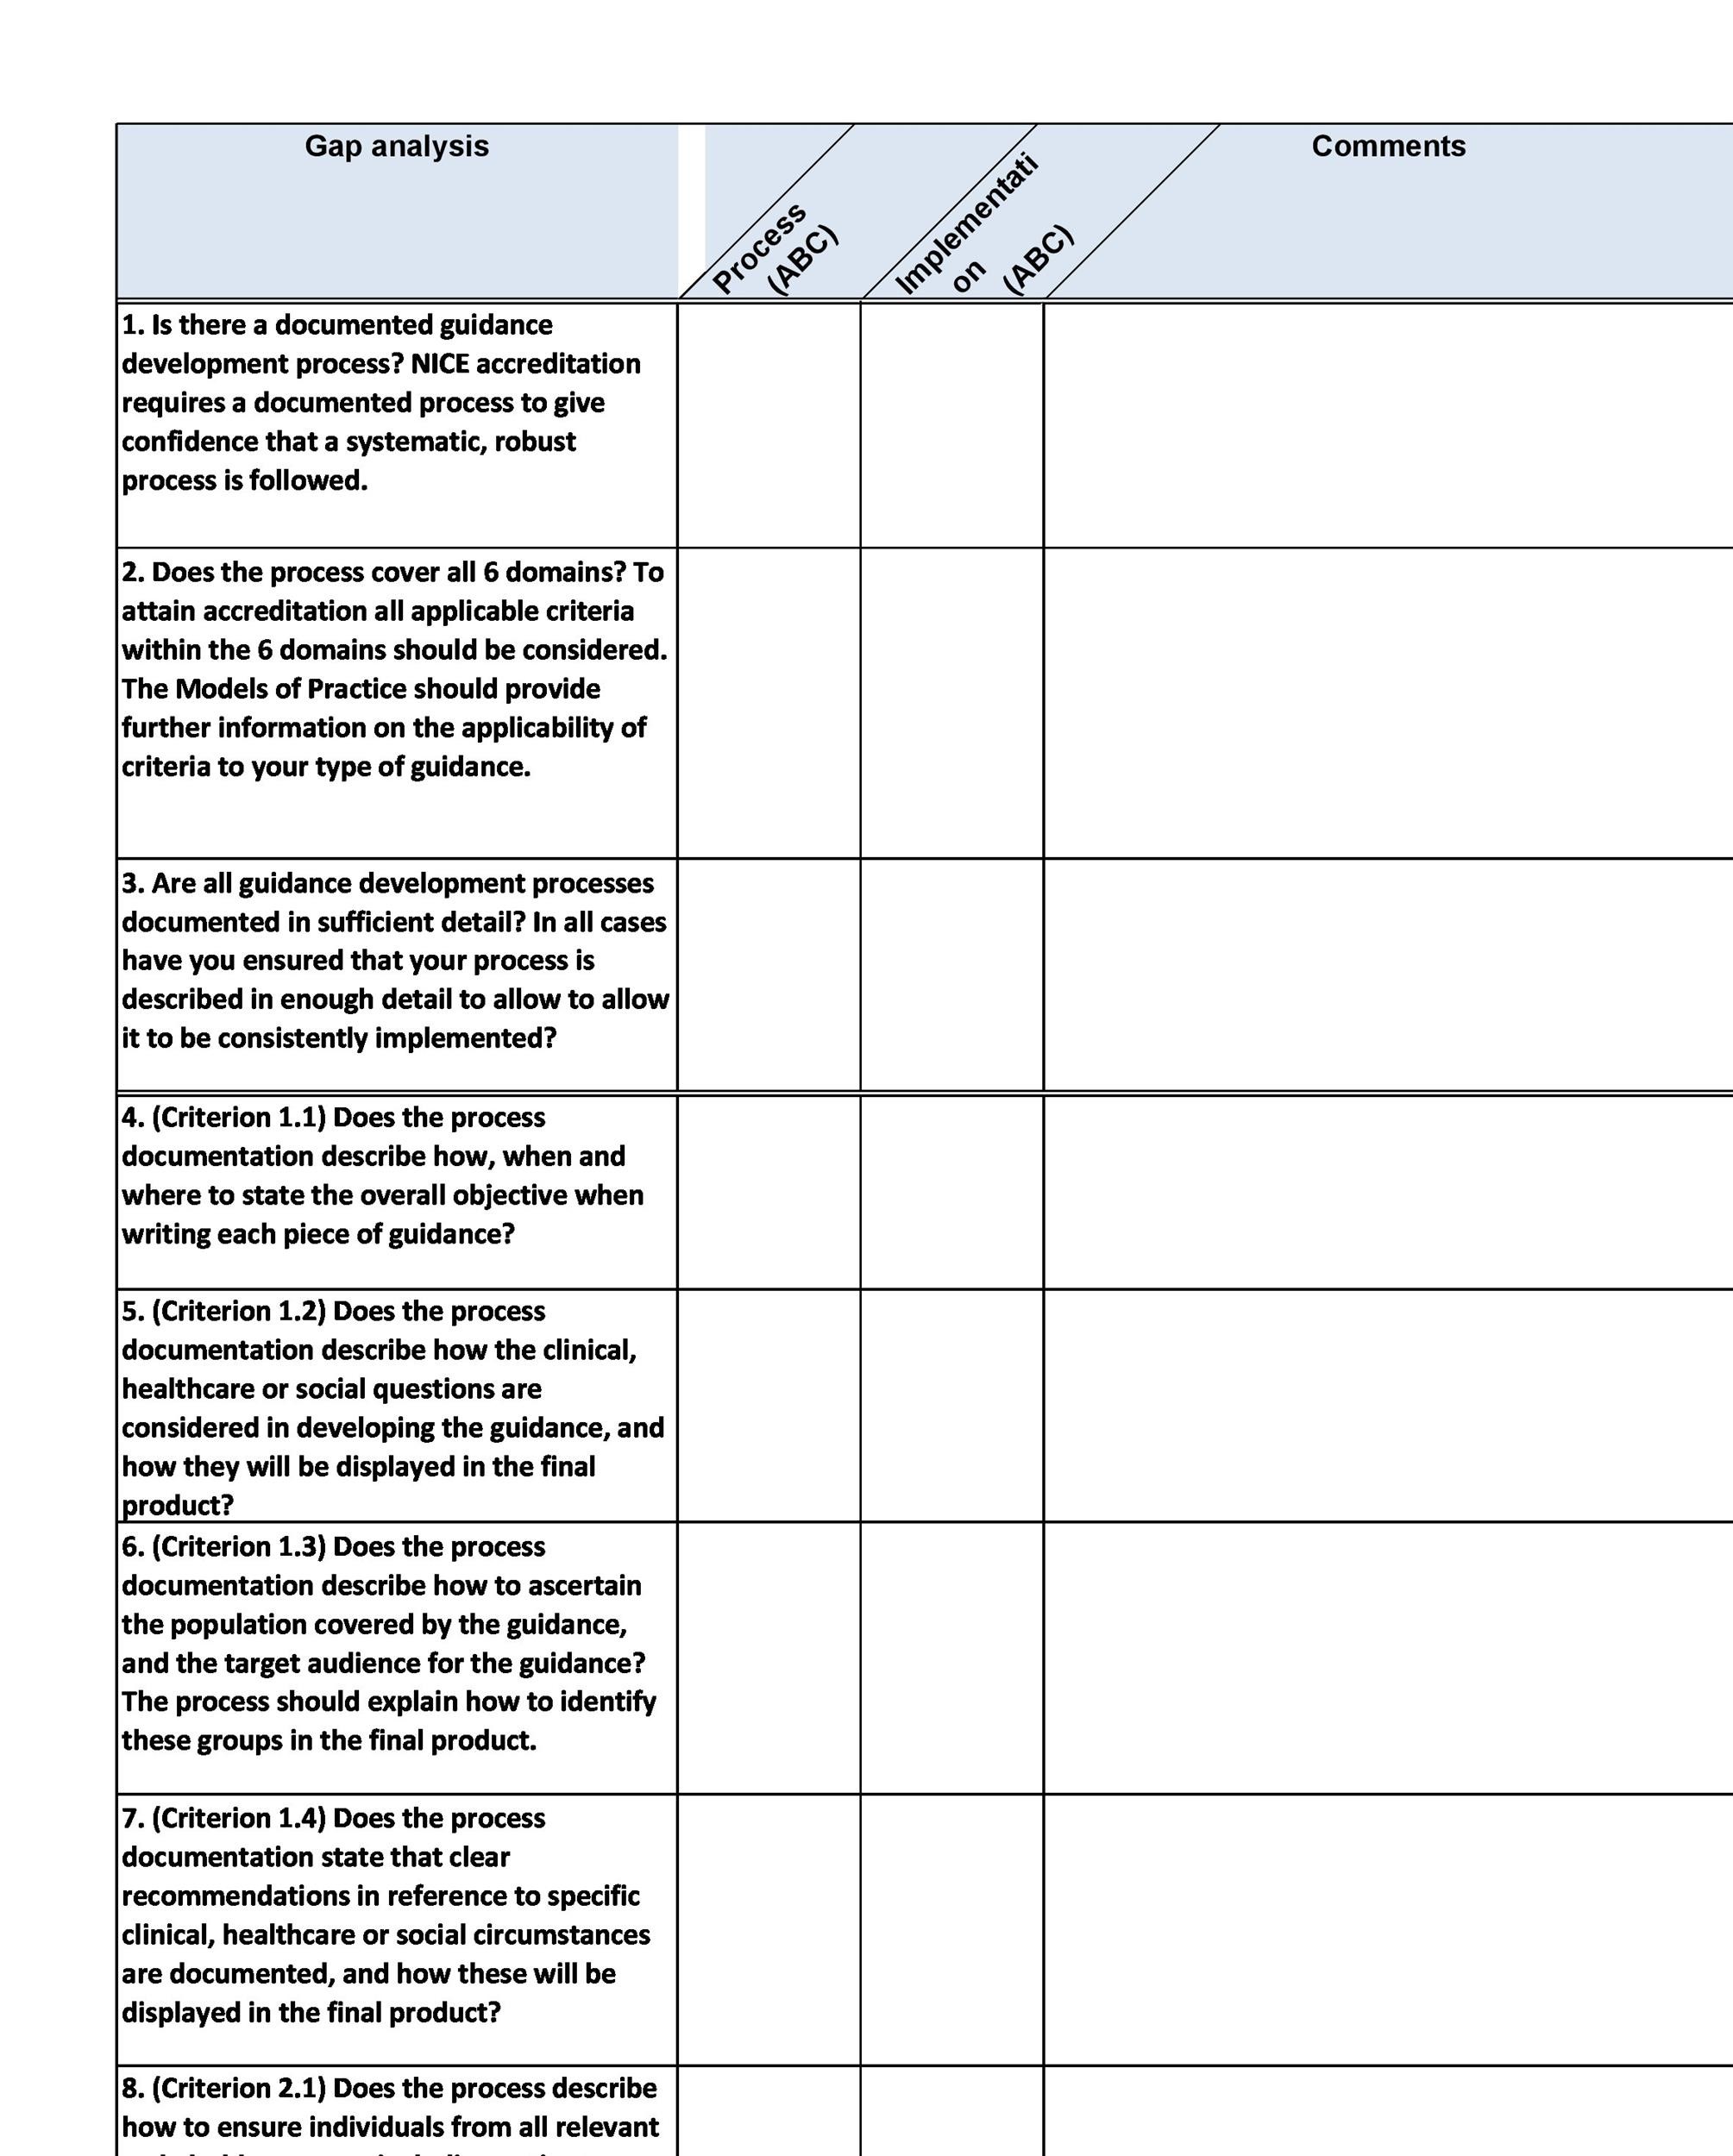
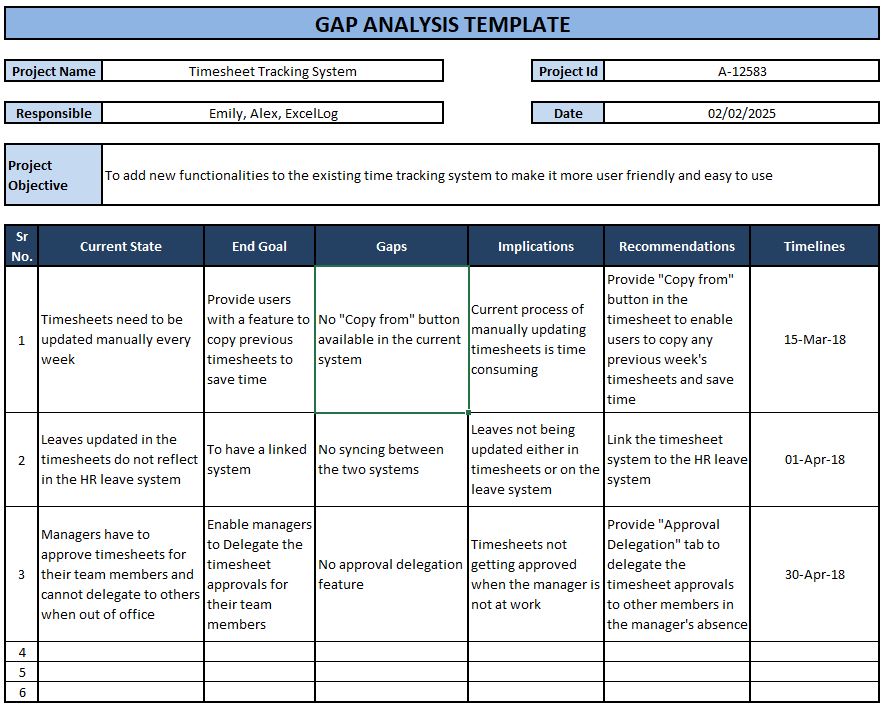
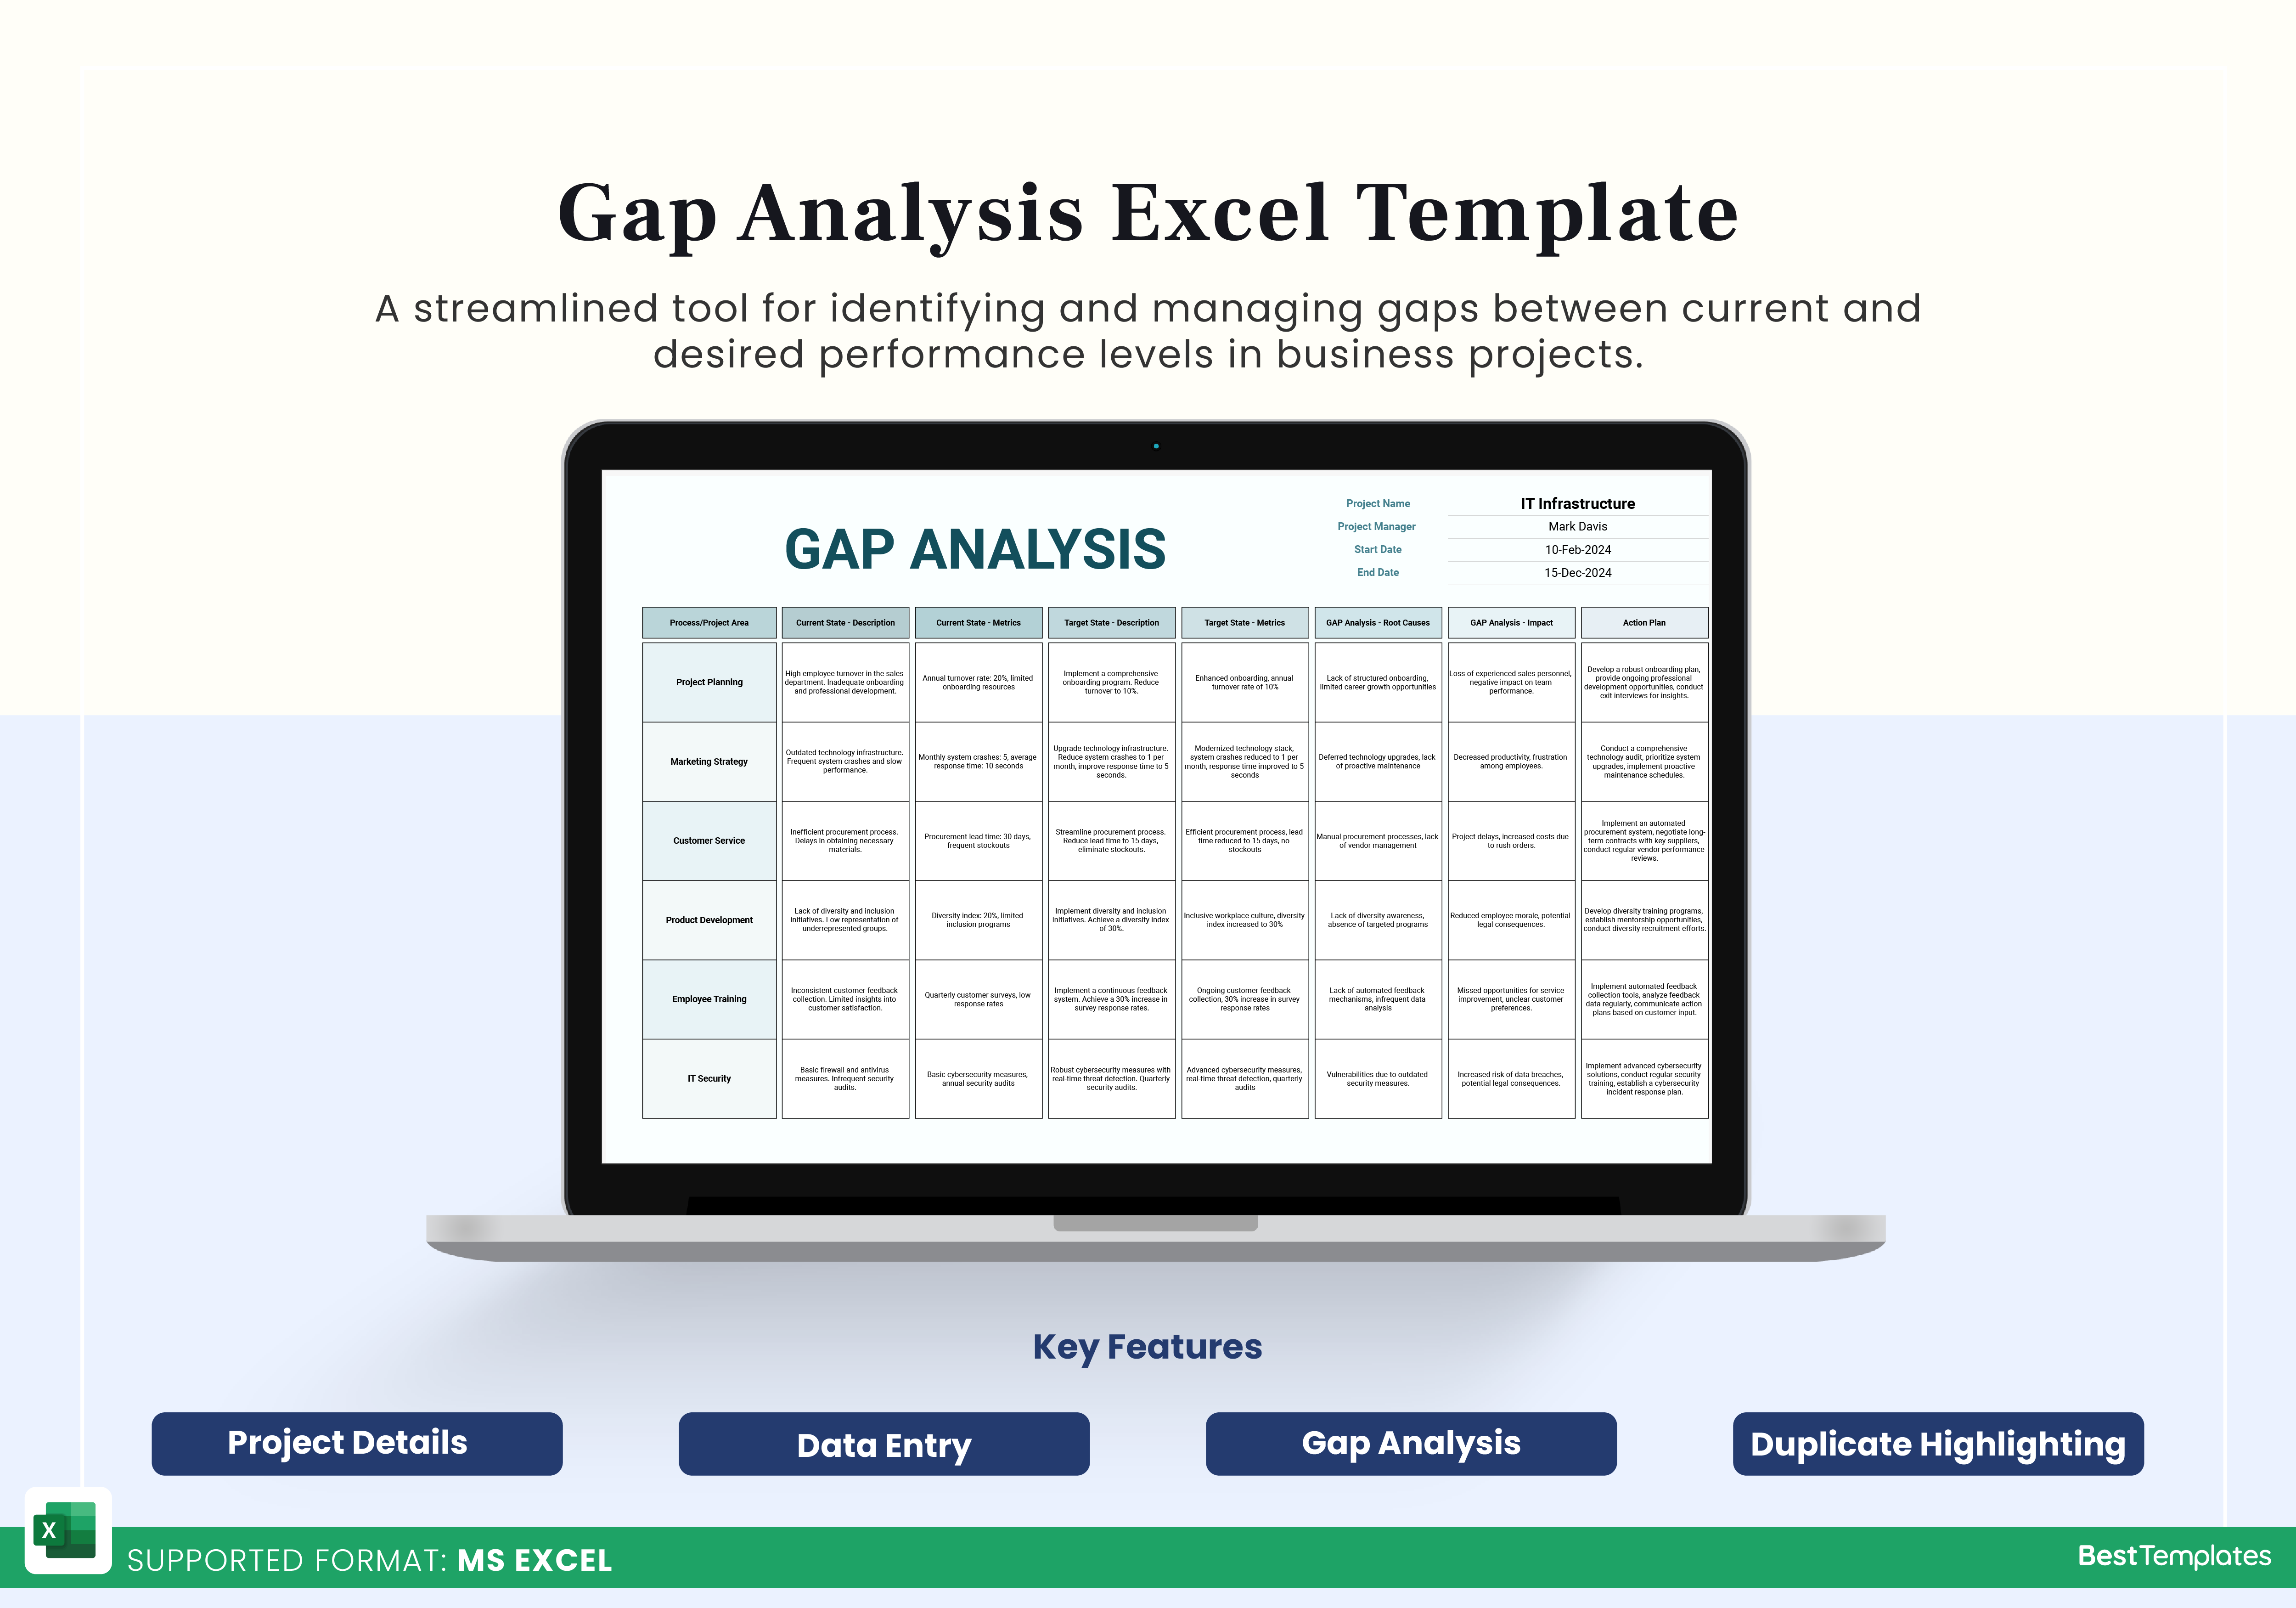
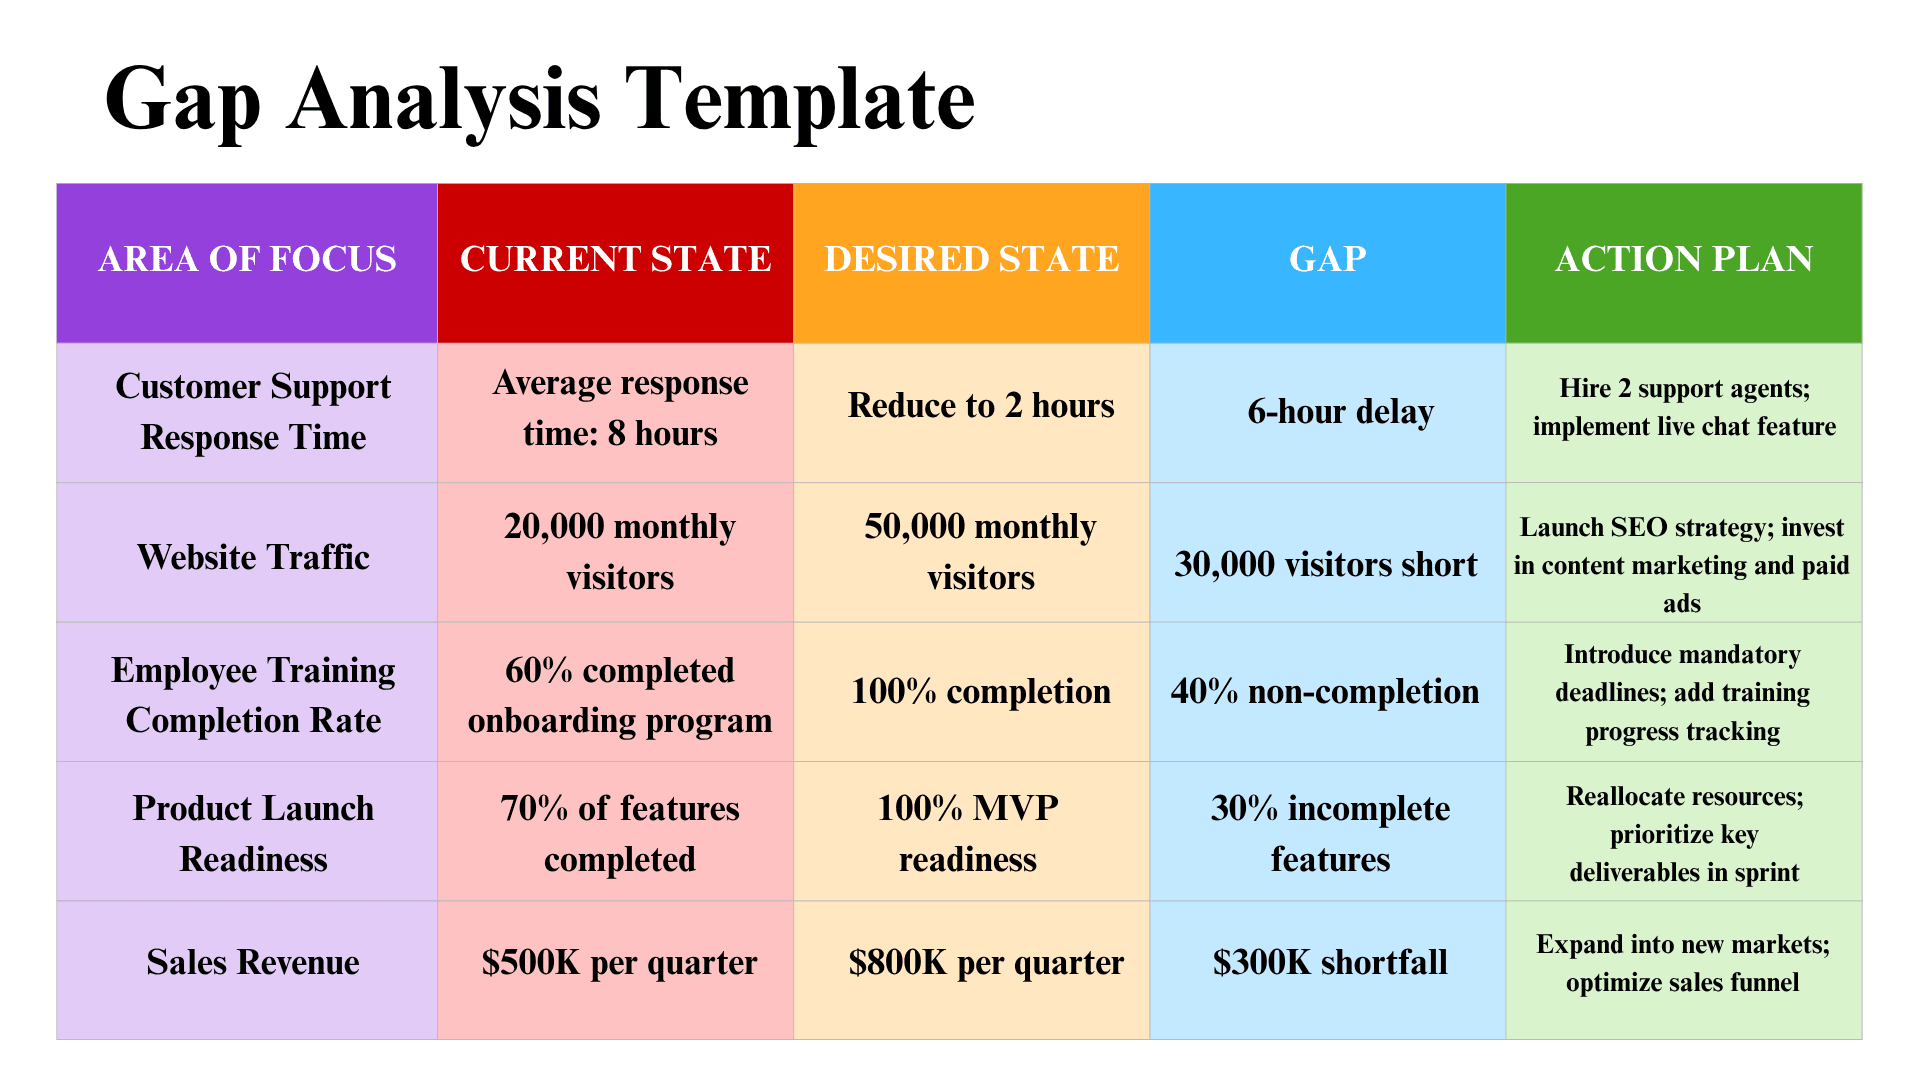
A gap assessment template is a structured document that maps your current state against a target state, then flags the differences you need to address. It is not a fancy tool. It is usually a table with columns for requirements, current status, gaps, remediation actions, and owners. People overcomplicate this because they think they need software, but most teams just need a clean spreadsheet or a well-organized shared doc. I have built these for everything from SOC 2 readiness to cloud migration planning. The structure is always roughly the same, and that is by design. The value is not in the template itself. It is in how consistently you fill it out.
How to Use a Gap Assessment Template
Here is the practical process I go through every time. First, define the scope. What framework, standard, or internal policy are you measuring against? Pick one. I see people try to assess against three frameworks at once and end up with a mess that satisfies nobody. SOC 2 and ISO 27001 overlap heavily, so if you are doing both, use one as your primary and map the other on top. Do not duplicate rows. Second, list every requirement verbatim from the source material. Do not paraphrase. I learned this the hard way during an audit where I summarized a control as "access reviews happen quarterly" when the actual text said "management shall review access rights on a quarterly basis and document any changes." The auditor flagged it because my version implied routine when the standard required documented evidence of change tracking. One sentence difference. Cost us two weeks of catch-up.
Third, for each requirement, fill in your current state with blunt honesty. If you do not have the thing, say you do not have the thing. "Partial" is the worst answer you can give. It means nothing to anyone reading the document. Use binary: present or absent. If something is partially implemented, break it into sub-requirements until you can say yes or no for each piece. Fourth, identify the gap. This is straightforward. Current state minus target state equals what is missing. Then assign a remediation action, an owner, and a target date. That is the core of the template. The columns I typically use are: requirement ID, requirement text, current state, gap description, risk rating (high medium low), remediation action, owner, target completion date, and evidence location. Evidence location is the column most people skip, and it is the one that saves you during an actual review. You do not want to be hunting for a policy document six months after you wrote the assessment.
Get the Full Details
Where These Templates Fall Apart
The biggest problem I run into is version drift. Someone updates the standard, adds a new control, or rewords an existing one, and the template sits there with outdated requirements. I maintain a change log at the bottom of my templates that records every update with dates and what changed. Takes thirty seconds per edit and prevents the "but we assessed against the 2023 version" conversation. Another failure mode is treating the gap assessment as a one-time deliverable. It is not. It is a living document that should be updated whenever the environment changes or new controls are implemented. I see teams build these, hand them to management, and never touch them again. Then they wonder why the assessment looks nothing like reality when the audit actually happens. There is also the risk of gap inflation. When you are under pressure to show progress, people start marking items as "in progress" even when nothing meaningful has happened. An "in progress" label without a target date and a clear definition of done is just a way to look busy. Every in-progress item needs a committed completion date and a description of what "done" actually looks like. Otherwise it is fiction.
If you need to share or download a ready-to-use version, search for "Gap Assessment Template" and you will find options in spreadsheet format from various compliance and IT governance resources. Most of the free ones are decent starting points. The ones from recognized bodies like NIST or ISACA tend to be more aligned with actual audit expectations, but they are often written for larger enterprises and may need trimming if you are a small team. The template does not fix a broken process. It only makes the gaps visible. If your organization does not have clear ownership for security controls, or if policies are not actually being followed, a gap assessment will show you those problems but it will not solve them. You still have to do the work after the assessment is complete.