How to Make and Use Geek Prank Full Screen
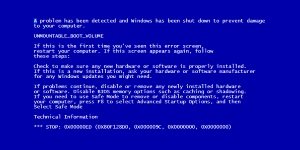
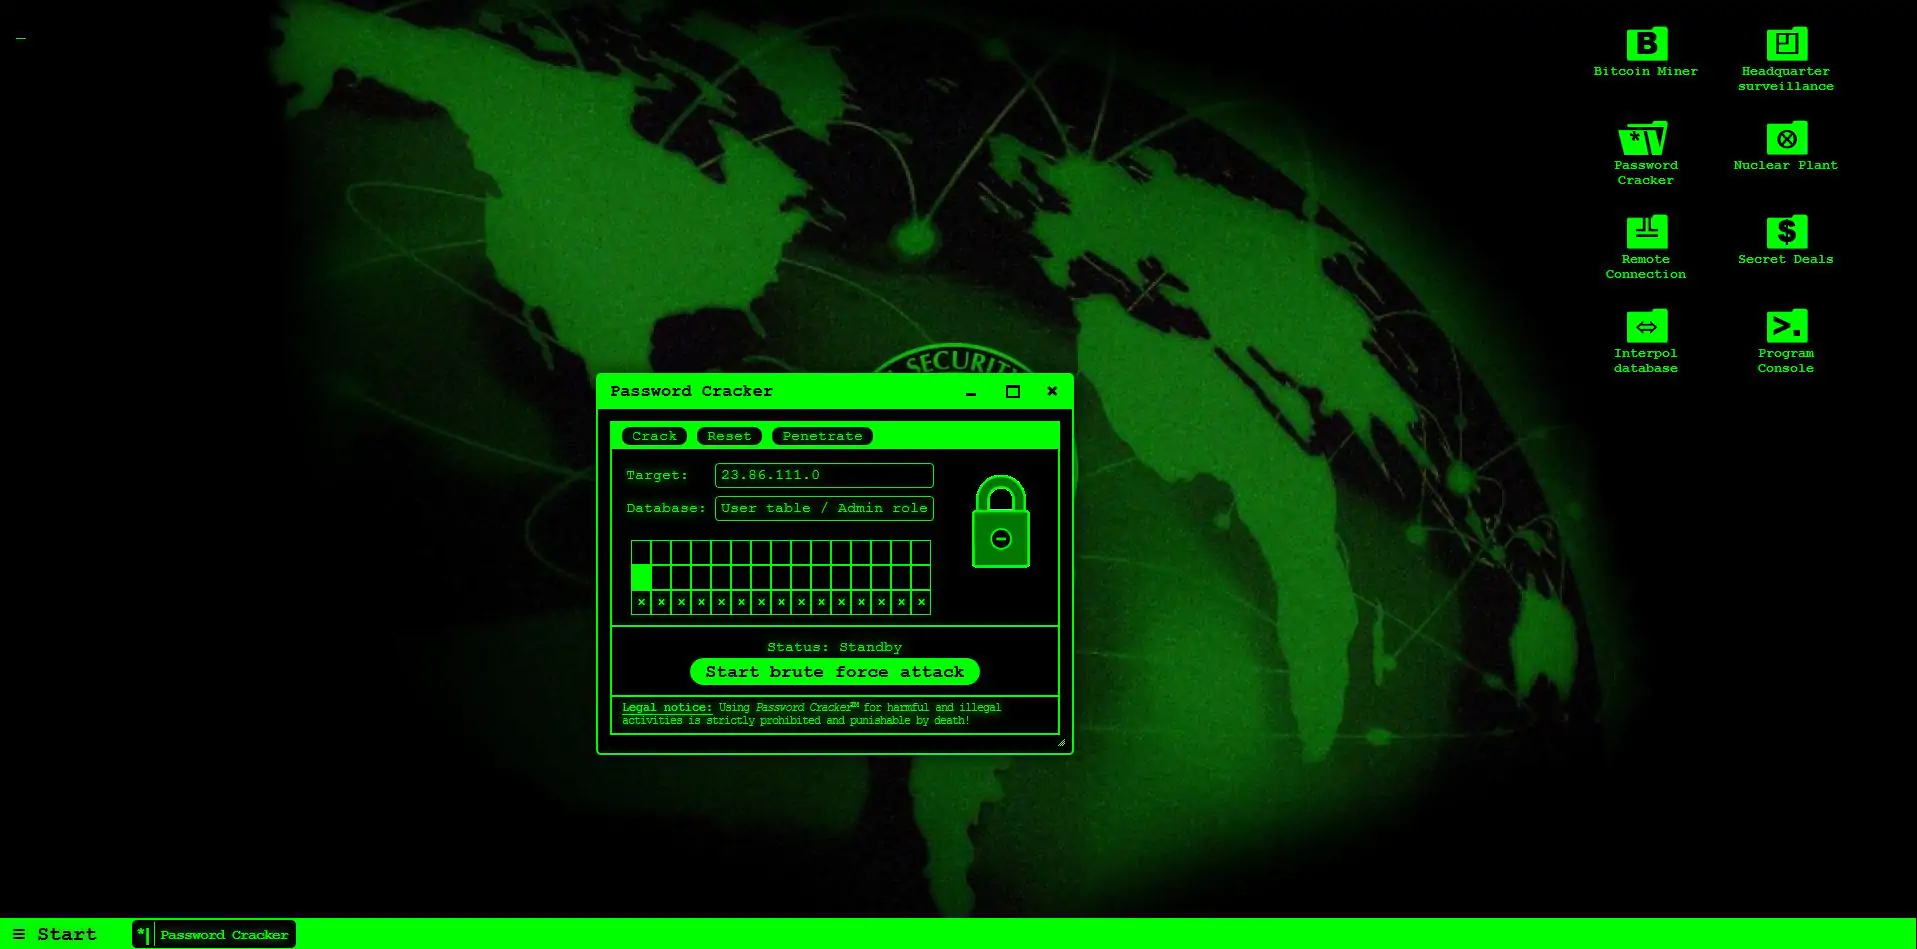
Geek Prank Full Screen is a browser-based script that locks a victim's display into fullscreen mode and replaces the content with a series of fake system errors, malware warnings, and crash screens. It's been around for years. The mechanic is straightforward enough that any decent HTML page can reproduce it. The page calls the requestFullscreen API on the document body or a wrapper div the moment it loads. From there, JavaScript swaps out the visible content on a timer. You see a fake blue screen, then a Windows error dialog, then a "virus detected" overlay, and so on. The exit button is usually a trap—it either opens another screen or does nothing. The real escape is closing the tab entirely. I learned the hard way that this doesn't always start automatically. Some browsers block requestFullscreen unless there's a real user interaction. That's why the best pranks include a fake "Click to download" or "Accept terms" banner right at the top. The victim thinks they're clicking to do something normal and accidentally triggers the fullscreen request. Without that prompt, the script sits there doing nothing and the whole thing falls apart.
Building Your Own Version
You don't need anything fancy. A single HTML file with an embedded script will do. I usually start with a blank page, add the fullscreen request at the top, and then layer in timed content changes using setInterval. The typical session runs anywhere from thirty seconds to two minutes depending on how many screens you string together. Here's a rough outline of the minimum code: Once that's in place, the rest is just designing the fake screens. I use absolutely positioned divs with system fonts like Segoe UI or Arial to mimic Windows error dialogs. A dark semi-transparent overlay behind the fake dialog simulates the dimmed desktop effect. Most people skip the audio, which is probably wise—I once included a Windows error sound effect and the victim immediately identified it as a prank within five seconds. Remove the audio and it becomes considerably more convincing.
Where It Breaks and How to Fix It
The biggest problem I've run into is Safari on macOS. The requestFullscreen call technically works, but the Escape key doesn't respond the way it does in Chrome or Firefox. The victim just hits Escape and bails out. If you're targeting someone on a Mac, don't bother with Safari. Stick to Chrome or Firefox, or find a workaround like injecting a keydown blocker that intercepts the Escape event. Mobile browsers are another dead end. Most phones don't support the fullscreen API, so sending a Geek Prank Full Screen link to an iPhone or Android device is a waste of time. The page will open, but nothing goes fullscreen and the prank fails completely. Another quirk: opening the HTML file directly from the filesystem using the file:// protocol can cause certain APIs to be blocked or behave unpredictably. I switched to hosting the file locally with a simple Python HTTP server and the success rate jumped from about eighty percent to near one hundred. The URL becomes http://192.168.x.x/something.html instead of a file path, and that small change avoids a lot of browser restrictions.
Get the Full Details
Common Pitfalls Most People Miss
The URL bar stays visible in fullscreen on most browsers. If the victim sees the actual page address in the top bar, they're going to realize it's a prank much faster than you'd like. A shortened link or a misleading domain name helps a lot. I've seen people use link shorteners that disguise the real destination, which buys you extra seconds of panic before anyone checks the URL. The Exit button trap is worth getting right. A lot of beginners put a clearly fake "Exit Prank" button that doesn't do anything. That's fine if the goal is to keep the victim trapped, but some people will eventually figure it out and just force-close the tab. If you want to give the impression that there's no way out, make the button visually appealing and styled like a system control. It doesn't need to actually work—the illusion is the point. Counter-intuitive note: looping the same fake screen repeatedly is less effective than varying the content. I initially reused the same blue screen three times and the victim started laughing after the second repetition. Swapping between different error types—a crash dialog, a malware warning, a corrupted system message—makes the sequence feel more like a real system failure. Human brains are pretty good at spotting patterns, and repetition kills the scare factor fast.
Downloader and Hosting Options
If you don't want to build this from scratch, there are open-source versions available on GitHub. Search for "geek prank full screen html" and you'll find several repos with pre-built templates. The ones I've looked at range from basic to fairly polished. You can host them on Google Drive's static hosting, GitHub Pages, or any free web host. Some people prefer to run it from a USB stick or a local server when they're in the same room as the target, which eliminates any network-based detection concerns. The exact download links change constantly as people take down old repositories or rebrand their projects, so I'd recommend searching GitHub directly rather than relying on third-party mirrors. That way you're getting something that hasn't been modified with unwanted tracking code or ads.
Limitations You Should Know About
This prank is browser-dependent and platform-dependent. It works reliably in Chrome and Firefox on Windows. Edge is Chromium-based so it generally works too. Safari is unreliable. Mobile browsers are effectively non-functional for this purpose. Kids who have used computers before will figure out Alt+F4 or Task Manager almost immediately. Tech-savvy adults may notice the URL or the lack of a real system process running and call it out within seconds. It's also worth noting that the prank relies entirely on the victim staying at the screen. If they step away and come back five minutes later, they'll just see a bunch of error windows they can close without any of the intended shock value. The effectiveness drops sharply the longer the gap between triggering the prank and the victim actually sitting down to deal with it. I've had mixed results with different victim profiles. Friends who don't take technology seriously are usually good candidates. IT departments or developers will laugh, but they'll also take apart the mechanism in under a minute and probably critique your code while they're at it. The sweet spot is someone who's mildly anxious about their computer but doesn't know enough to look under the hood.
Final Notes
The whole thing is harmless if kept short and ended with a clear "this was a prank" message. I've used versions that cycle endlessly without resolution and the reactions range from annoyed to genuinely shaken. A clear ending keeps the mood light and makes it more likely the person you pranked will actually find it funny instead of just resentful. A large text overlay that says something like "Gotcha" or "Just kidding" at the end does the trick and takes about ten seconds to implement.