
A Practical Look at the Hacker Prank Scripts
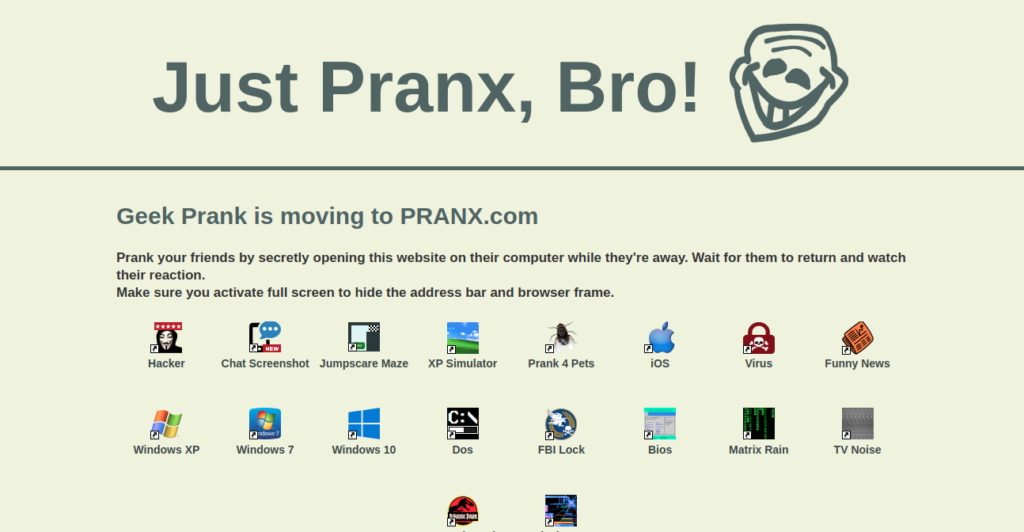
You've probably seen them before. Some script opens on your monitor, fills the screen with cascading green text, plays fake hacking sounds, maybe even throws in a "ACCESS DENIED" overlay that looks convincingly ominous. That's what people call a Geek Prank Hacker Troll, and it's been around long enough that most of the versions floating on the internet are recycled copies of each other. These are typically HTML-based pranks. Sometimes packaged as a simple browser page, sometimes wrapped in something like AutoIt or a batch file that launches the browser in fullscreen and disables the taskbar. The effect is cheap, sure, but it works because people react to the noise and the visuals before they think to look for the exit button.
How to Set Up a Basic Geek Prank Hacker Troll
The simplest version requires nothing more than a text editor and a browser. Open Notepad, paste the HTML prank code, save it as something innocent like system_update.html, and send it to whoever you're pranking. When they open it, the script launches fullscreen, runs a fake terminal animation, and loops until they force-close it. For something slightly more persistent, people wrap the HTML in a batch file that also hides the desktop icons and disables the taskbar. Here's what that looks like in practice: Create a file called update.bat with these contents:
start "" "C:\Program Files\Mozilla Firefox\firefox.exe" --kiosk "C:\path\to\prank.html" taskkill /f /im explorer.exe The first line launches Firefox in kiosk mode, which removes the address bar and tabs. The second line kills the Windows explorer process so the victim can't easily access the desktop. The only way out is through the task manager, and even then the prank script often detects and closes it.
Get the Full Details
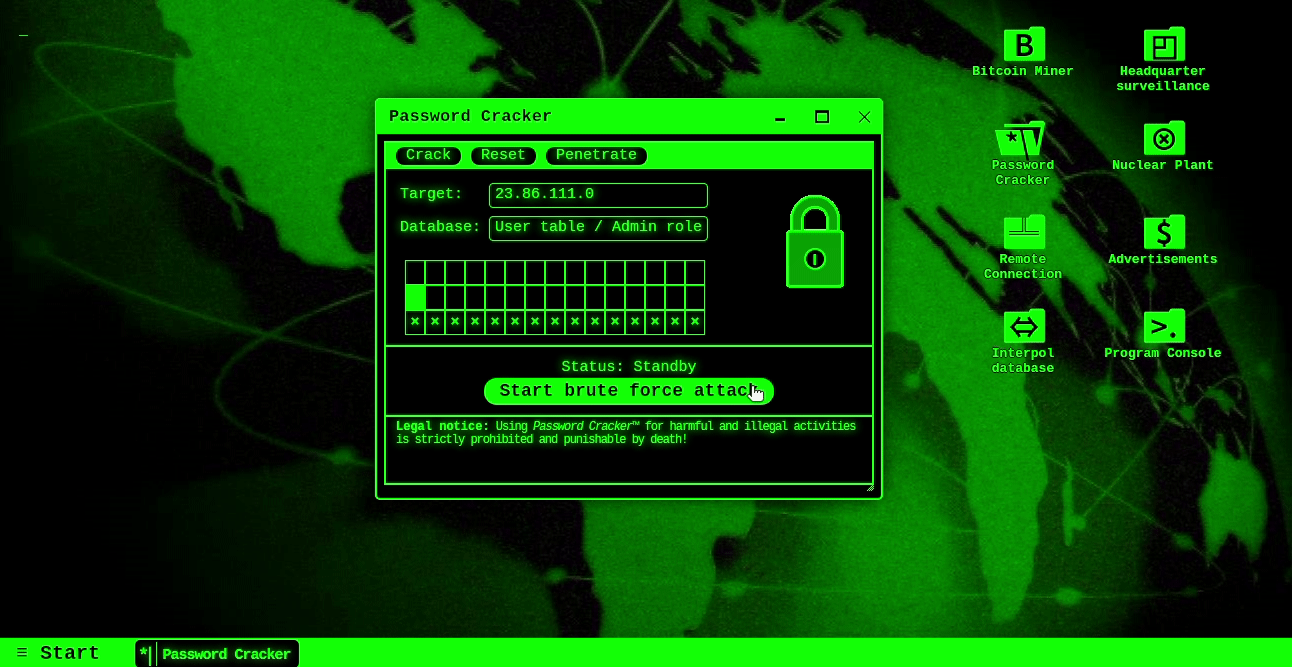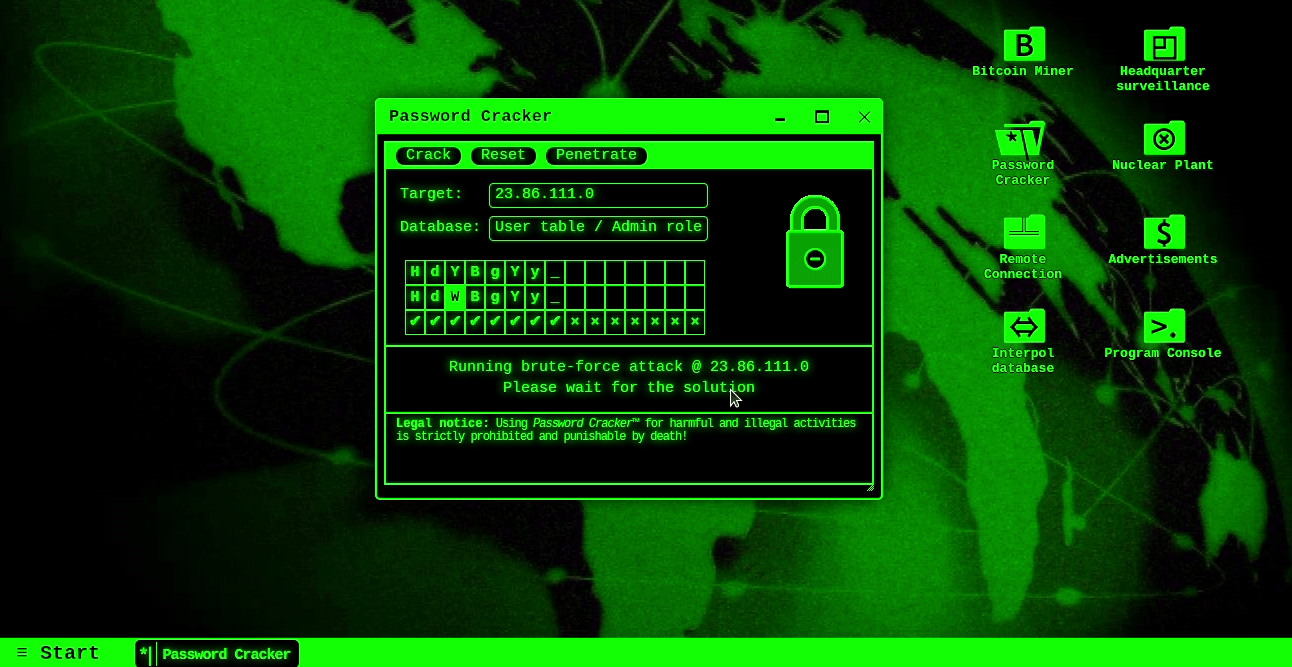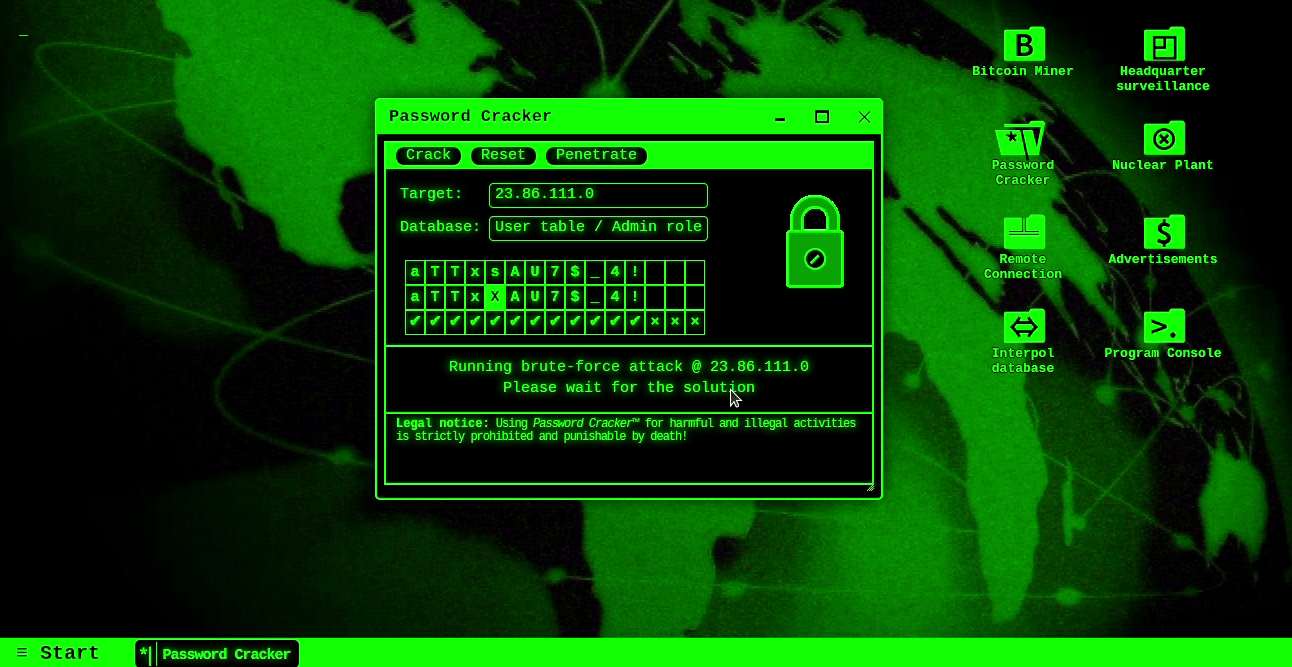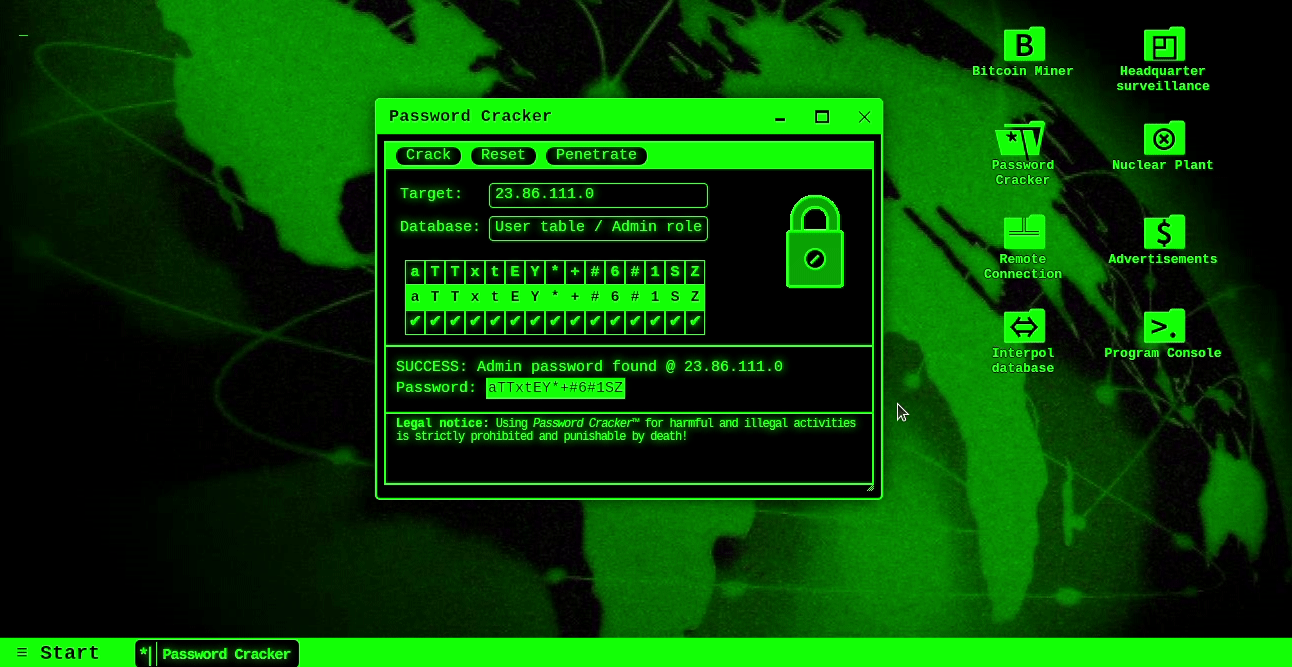
I spent way too much time troubleshooting a version where the kiosk flag didn't stick on Chrome instead of Firefox. The flag is --kiosk for Chrome but some corporate environments block it via policy. Switching to Firefox fixed it immediately, which was the actual solution rather than any of the troubleshooting guides I found online.
What These Pranks Actually Do
Beyond the visual noise, most of these scripts don't do anything actually harmful. They're designed to look intimidating without causing real damage. The fake terminal output is usually pre-written text that scrolls automatically. The sound effects are generic alarm or typing audio tracks embedded as base64 data within the HTML itself. Some versions include interactive elements. A fake command prompt that accepts "input" and responds with scripted reactions. A fake face-scanning animation that claims to be logging your identity. These work because the victim is still in the initial shock window where they haven't yet figured out whether to panic or close the browser. There's a significant difference between a harmless prank and something that causes actual problems. I once watched someone try to run one of these on a machine that had unsaved Excel files open. The kiosk mode and taskbar kill ended up interfering with their workflow monitoring tools, and it took twenty minutes of registry editing to restore normal function. Not catastrophic, but definitely not a clean get-out-of-jail-free situation.
Geek Prank Hacker Troll Installation and Usage
The download options for these scripts are scattered across Reddit threads, GitHub gists, and random file-sharing sites. The quality varies enormously. Some are clean single-file HTML pranks that work immediately. Others are bundled with adware installers or require you to disable your antivirus to run. Here's what I'd recommend if you want to set this up properly: Find a self-contained HTML version from a reputable source like a well-maintained GitHub repository. Avoid anything that asks you to download additional installers. Test it yourself first on a virtual machine or a spare laptop. Verify the fullscreen behavior works correctly and that there's an obvious escape mechanism, preferably a visible close button hidden behind one of the fake windows.
The most annoying edge case I hit was with the auto-hide taskbar feature. On Windows 11, the taskbar behaves differently than Windows 10, and the usual registry settings to hide it completely don't always apply cleanly. The workaround was using a PowerShell script that calls the native taskbar hiding API directly rather than relying on registry changes. It took about three extra lines of code but made the whole thing significantly more reliable.
Common Pitfalls
Most people skip the testing phase and assume the script will work exactly as intended. It rarely does. Browser updates change how kiosk mode behaves. Windows updates modify how the taskbar responds to process termination. Antivirus software increasingly flags these scripts as PUPs (Potentially Unwanted Programs) even when they contain no actual malware. Another issue is the escape problem. If your prank has no way to exit except closing the browser, modern operating systems make that difficult enough that the victim might spend thirty minutes trying to recover their system instead of just laughing it off. That's when a harmless prank turns into genuine frustration and potentially serious relationship damage. Sound is another variable that people underestimate. Some versions play loud alarm noises at maximum volume. This can trigger actual medical issues in people with certain conditions. It's worth considering whether the prank should include a mute option or keep the audio at a reasonable level. I learned this the hard way after a colleague had a panic attack from a prank I thought was mild.
Technical Details Worth Knowing
Most of these pranks rely on a combination of techniques. Fullscreen HTML with JavaScript animations. Base64-embedded audio. Keyboard interrupt hooks that prevent Escape from working. Some even use the Screen Capture API to grab your webcam feed and overlay fake text on it, making it look like the system is analyzing your face in real time. The webcam-overlay trick is technically the most impressive but also the most invasive. It requires explicit browser permission, which means the victim might dismiss the permission prompt before the prank even starts. That defeats the purpose entirely. I'd recommend skipping that feature and focusing on the visual and audio elements instead. One counter-intuitive thing about these pranks: they work better when they're slightly imperfect. A perfectly polished fake terminal looks obviously fake to anyone who has spent time around computers. Adding minor flaws, like occasional typing errors in the fake output or a slightly delayed response time, makes it feel more authentic. The uncanny valley effect works in your favor here.

When It Goes Wrong
There are scenarios where these pranks cause genuine harm. Devices with critical monitoring software, medical equipment interfaces, industrial control panels, anything where someone is actively using the computer for work at the moment the prank launches. I've seen these used in professional settings where the target was testing production code, and the resulting crash cost the company real money. The legal side is murky. In most jurisdictions, running unauthorized software on someone else's computer violates computer fraud statutes, even if the intent is purely humorous. Sending the prank file through a shared network drive or email could constitute unauthorized access depending on how you interpret the applicable laws. This isn't something to be casual about just because the output is silly. If you're determined to do this, the safest approach is using it on your own devices or with explicit consent from the target. The whole concept of a prank collapses when the person being pranked has no ability to opt out beforehand. There's no difference between a joke and harassment once someone has reported it seriously.
The underlying technology here is straightforward enough that learning it genuinely won't take more than an afternoon. HTML, basic JavaScript, and a bit of knowledge about how browsers handle fullscreen mode. After that, it's mostly about testing, refining the timing, and understanding the limitations of your target environment before deploying anything.


