On actually using Hacking Exposed Malware And Rootkits
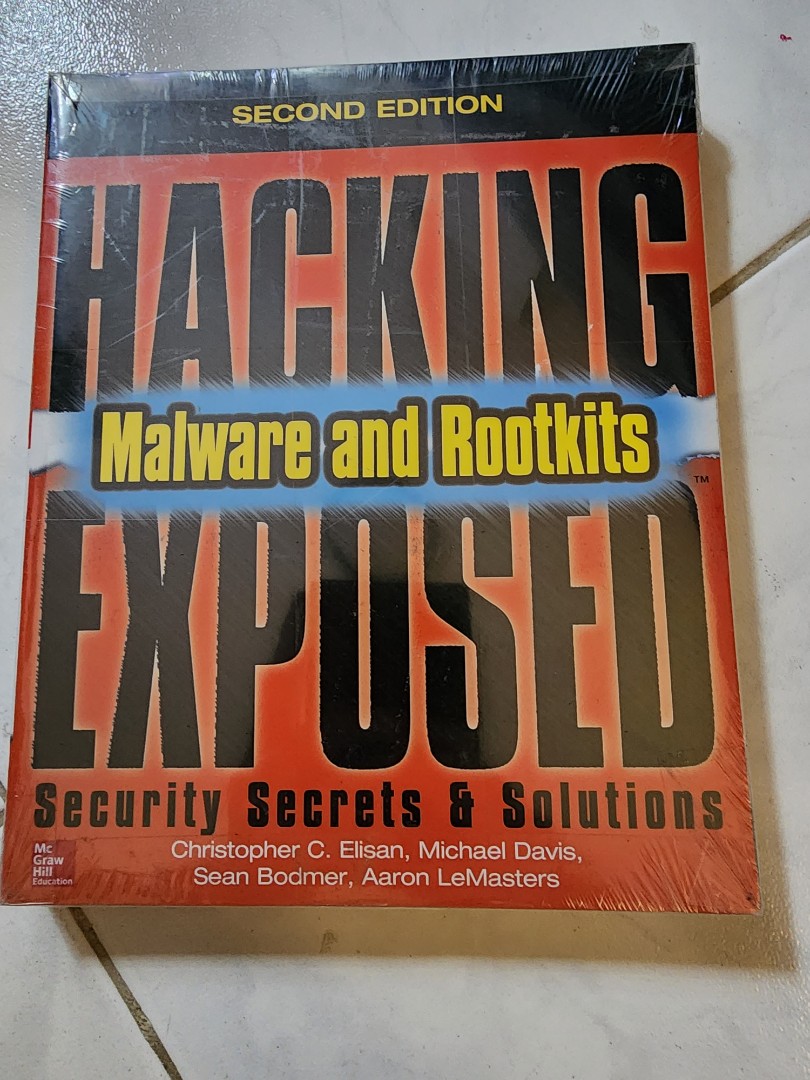
I picked up Hacking Exposed Malware And Rootkits a few years back after my team spent three solid weeks trying to figure out why our endpoint detections kept missing what looked like a coordinated implant campaign. The book didn't give us a silver bullet, but it did give us the right vocabulary and methodology, which is honestly more than most books in this space do. It's part of the long-running Hacking Exposed series, and this volume covers the practical sides of malware analysis, rootkit behavior, and the tradecraft used by both attackers and defenders. Not everything in it is current — some of the payload obfuscation techniques were already being phased out by the time it hit shelves — but the foundational concepts hold up better than most.
What the book actually covers
The content is divided into roughly four buckets. The first section walks through static and dynamic malware analysis methodology. This includes PE structure dissection, unpacking strategies, sandbox evasion patterns, and how to set up a proper analysis environment that doesn't leak your real infrastructure. The authors spend a reasonable amount of time on this because most people in incident response skip straight to dynamic analysis without having a clean baseline, and that's how you get contaminated evidence. The rootkit section is where a lot of readers probably come in. It covers kernel-mode rootkits, user-mode hooking, inline hook detection, and the various persistence mechanisms that get missed by standard AV tooling. The discussion on VxD and Bootkit-era techniques leans a bit outdated for modern Windows 10 and 11 environments, but the Linux and Unix portions remain relevant, especially around hidden module detection and auditd bypass methods. There's also a chapter on network-level threat detection and another on mobile malware, which is thinner than I'd like but functional. The anti-analysis and anti-debugging techniques section is genuinely useful — it describes how real malware detects VMs, checks for debuggers, and reads timing-based counters, all with code examples you can compile and test yourself.
What most people miss about this material
One thing that doesn't get enough emphasis in the book but should: the separation between what malware does and what rootkits do. Malware wants to execute payloads, exfiltrate data, and maintain access. Rootkits specifically exist to hide that activity from the operating system itself. They're not the same problem. Treat them the same and you'll spend your investigation time in the wrong subsystems. Another counter-intuitive point — the book hints at it but I want to underline it — is that most detection for advanced rootkits doesn't come from signature matching. It comes from behavioral anomaly detection at the kernel level. Signature-based tools will never catch a kernel driver that hooks SSDT or IDT directly. What catches those are tools that compare kernel module lists against the active process tree, check for unexported symbol references, and monitor for unexpected kernel callbacks. This matters when you're picking which tools to pair with the book's methodology.
Get the Full Details
A specific case where the book's approach fell short for me
Last year I was dealing with a targeted intrusion that involved a custom rootkit leveraging a compromised hardware security module for key generation. The attack chain included a bootkit, a kernel driver that replaced itself after every reboot via a firmware update hook, and a payload that communicated over DNS TXT records with polyglot encoding. The book gave me the analytical framework — reverse engineering methodology, hook detection patterns, persistence analysis — but nothing in the text prepared me for hardware-layer persistence. The workaround was to combine the book's rootkit detection techniques with a hardware assurance scan using a known-good firmware hash and UEFI Secure Boot verification before trusting the OS at all. I also shifted to memory forensics with Volatility, pulling a full memory image at power-off using a hardware-assisted capture tool rather than relying on live response. This added about forty-five minutes to the initial triage but eliminated the false confidence you get when your detection is running inside the same compromised kernel. If you're working in a resource-constrained environment where you can't do hardware verification, the next best move is a cold boot memory acquisition followed by offline analysis. Don't trust live tools on a suspected rootkitted system.
Hacking Exposed Malware And Rootkits practical usage notes
Here's how I actually use the book in a working environment. I don't read it cover to cover. I keep it open on a second monitor while I'm doing static analysis and flip to specific chapters as needed. The PE analysis and anti-debugging chapters are ones I reference most often. The rootkit detection methodology gets a second look when I'm building detection rules rather than doing live analysis. One practical tip: the code samples in the book use a mix of C, C++, and Python. If you're not comfortable compiling C on Linux or setting up a VM-based analysis environment, you'll slow down significantly. I'd recommend getting comfortable with x64dbg, IDA Free, and a Windows 10 analysis VM before diving in. It saves maybe two to three weeks of frustration. Another thing worth noting — the book doesn't cover modern supply-chain compromise scenarios very well. That's a gap shared by almost every malware analysis text published before 2022. If your concern is package repository poisoning or CI/CD pipeline attacks, you'll need supplemental material. The core rootkit and malware analysis sections are still solid, but the ecosystem has moved faster than the publication cycle.
The download situation depends on where you're getting it from. The official O'Reilly listing has the PDF and ebook formats. If you're looking for the physical copy, it's available through standard technical book retailers. I wouldn't bother with any of the pirated versions floating around — the print quality on some of the hex dump figures is poor in those editions and it actually makes the analysis harder when you're trying to match byte offsets. If you're new to this space and want a single starting point, this book sits at a solid intermediate level. It's not beginner-friendly, but it's not written for people who've already done hundreds of reversals either. The sweet spot is someone who has basic reverse engineering experience and needs to understand the specific mechanics of rootkit persistence and evasion. That was exactly my situation when I started reading it, and it turned out to be the right fit.